

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
414 results
RawHive preview

RawHive

GitHubnmht3t/rawhive

Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…
digital-forensicsdisk-forensicsexploitation+4
112
12 days ago
CVE-2010-2075 preview

CVE-2010-2075

GitHubrushikesh-a-bhujbal/cve-2010-2075

UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.

educationexploitationlabs-practice+7
28 days ago
Volumiser preview

Volumiser

GitHubccob/volumiser

CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
command-and-controldata-exfiltrationdigital-forensics+3
4372 years ago
ntfsDump preview

ntfsDump

GitHub3gstudent/ntfsdump

Use to copy a file from an NTFS partitioned volume by reading the raw volume and parsing the NTFS structures.
data-exfiltrationdata-recoverydigital-forensics+3
1175 years ago
SharpZipRunner preview

SharpZipRunner

GitHubjfmaes/sharpziprunner

Executes position independent shellcode from an encrypted zip
exploitationpayload-developmentpayload-generation+3
3035 years ago
PPLBlade preview

PPLBlade

GitHubtastypepperoni/pplblade

Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
data-exfiltrationexploitationmemory-forensics+2
6043 years ago
SliverKeylogger preview

SliverKeylogger

GitHubtrustedsec/sliverkeylogger

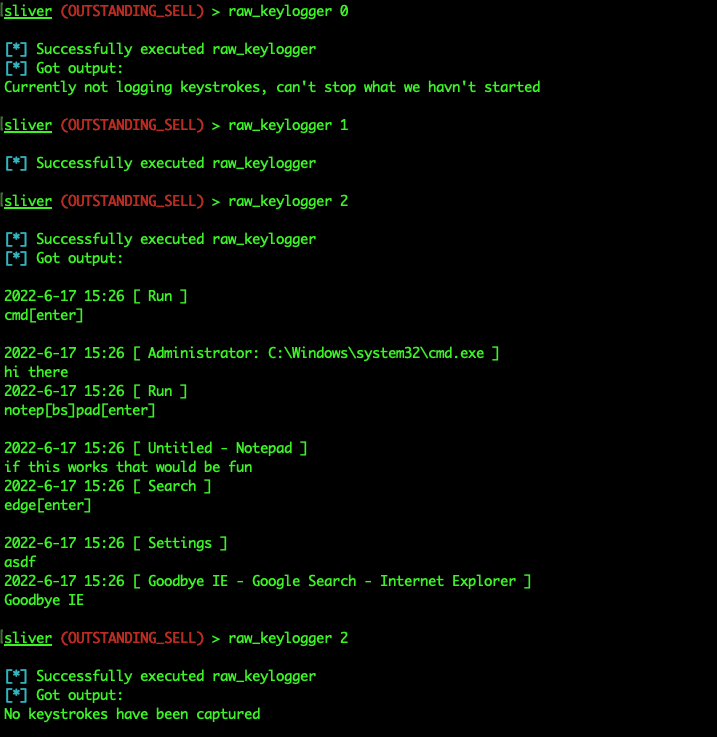
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
command-and-controldata-exfiltrationpayload-development+2
1734 years ago
Chrome-App-Bound-Encryption-Decryption preview

Chrome-App-Bound-Encryption-Decryption

GitHubxaitax/chrome-app-bound-encryption-decryption

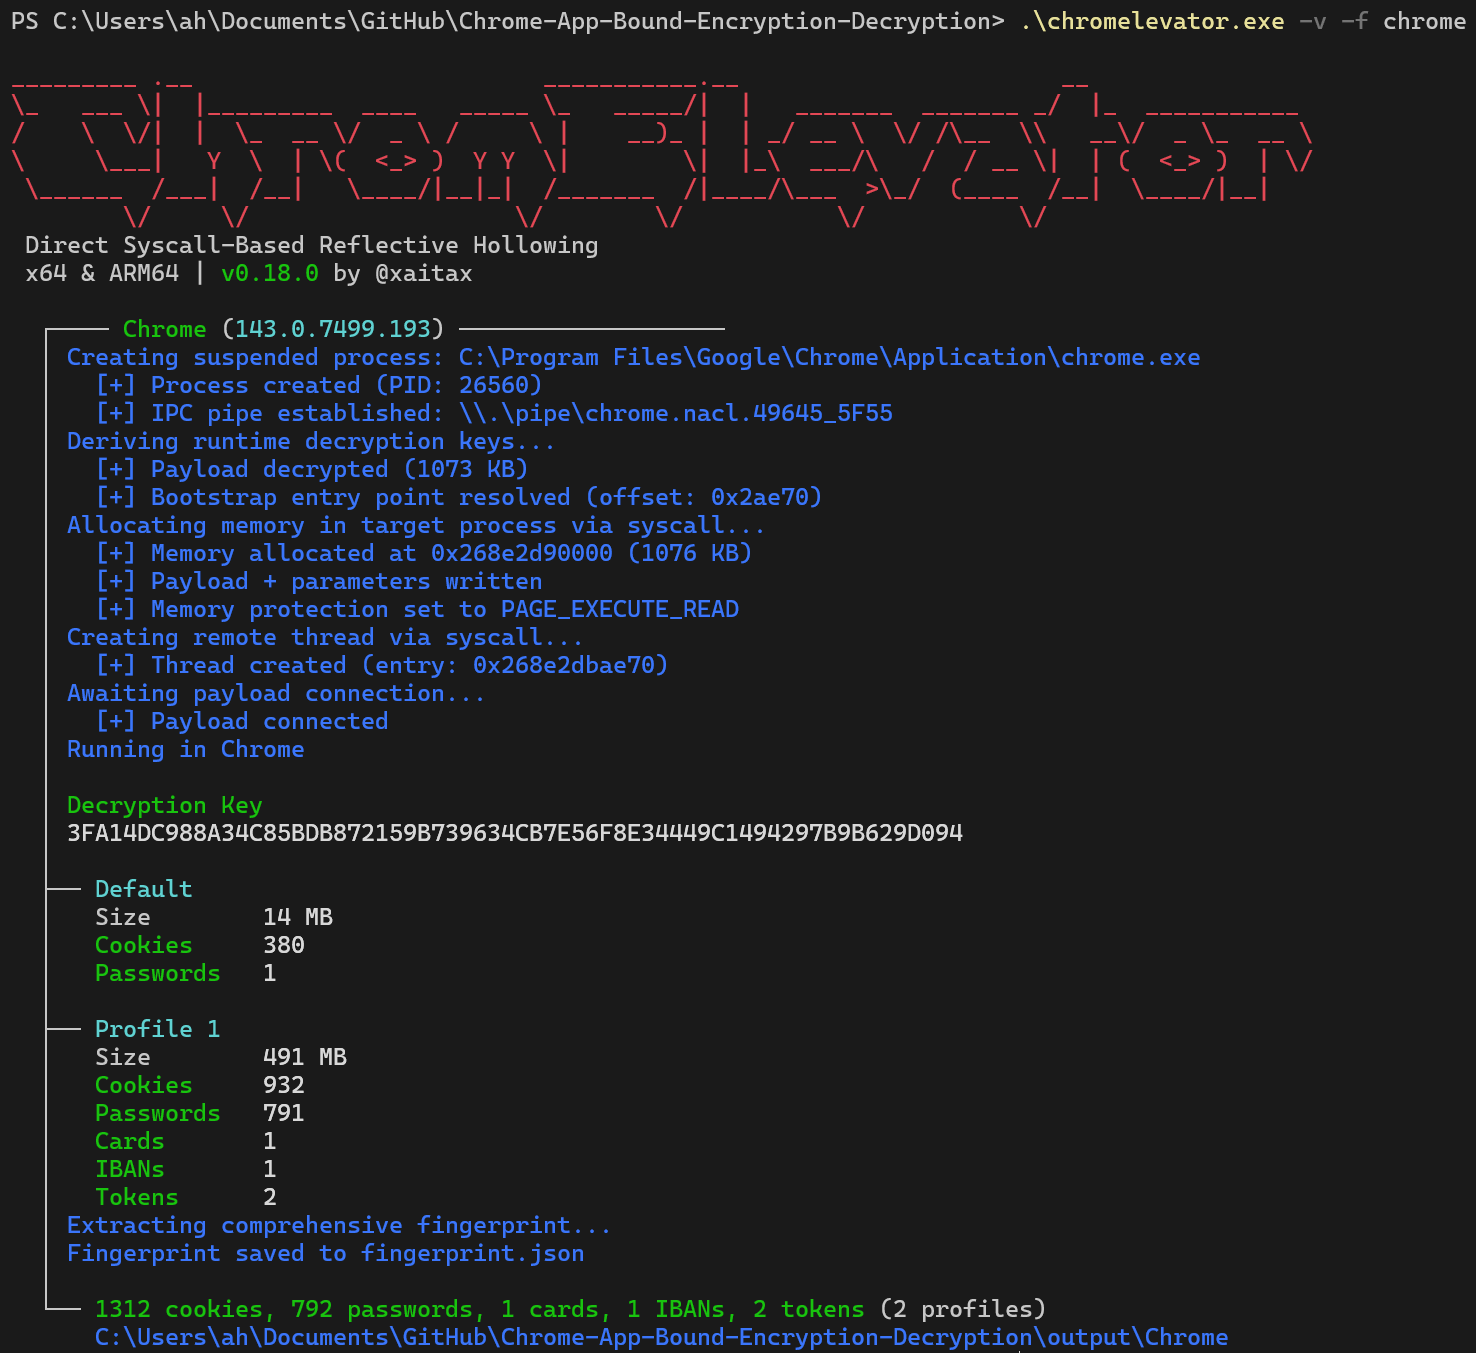
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…

cryptographydata-exfiltrationencryption-decryption-tools+5
1.8k8 months ago
ChromeKatz preview

ChromeKatz

GitHubmeckazin/chromekatz

Dump cookies and credentials directly from Chrome/Edge process memory
data-exfiltrationdebuggersmemory-forensics+3
1.5k6 months ago
cookie-monster preview

cookie-monster

GitHubkingofthenops/cookie-monster

BOF-based tool to extract browser cookies and credentials from Chrome, Edge, and Firefox via handle duplication and fileless download, with offline…

data-exfiltrationpenetration-testingpost-exploitation+1
5823 months ago
DumpBrowserSecrets preview

DumpBrowserSecrets

GitHubmaldev-academy/dumpbrowsersecrets

Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
data-exfiltrationdigital-forensicseducation+8
8284 months ago
EvilSelenium preview

EvilSelenium

GitHubmrd0x/evilselenium

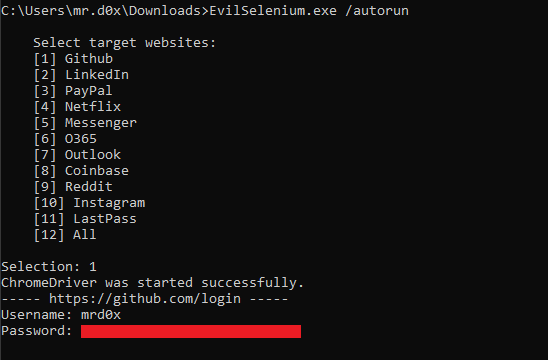
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
data-exfiltrationinformation-gatheringphishing-tools+3
6104 years ago
SharpGmailC2 preview

SharpGmailC2

GitHubreveng007/sharpgmailc2

Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol
command-and-controldata-exfiltrationpost-exploitation+2
2651 year ago
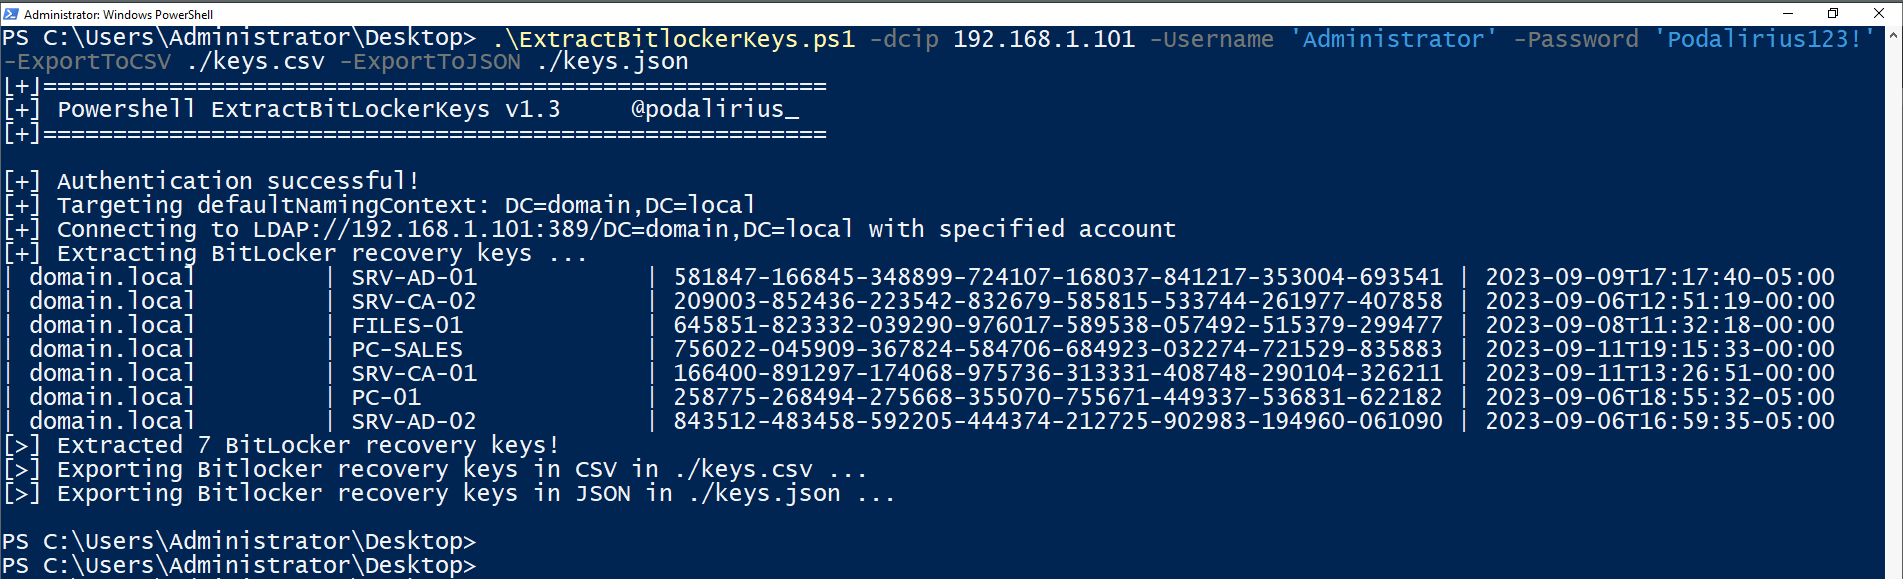
ExtractBitlockerKeys preview

ExtractBitlockerKeys

GitHubp0dalirius/extractbitlockerkeys

A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
data-exfiltrationencryption-decryption-toolsinformation-gathering+1
4069 months ago
secretsdump.py preview

secretsdump.py

GitHubfin3ss3g0d/secretsdump.py

Enhanced version of secretsdump.py from Impacket. Adds multi-threading and accepts an input file with a list of target hosts for simultaneous secrets…
data-exfiltrationpassword-attackspenetration-testing+2
2623 years ago
TotalRecall preview

TotalRecall

GitHubxaitax/totalrecall

This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…

data-exfiltrationexploitationinformation-gathering+5
1716 months ago
SrHollow preview

SrHollow

GitHubivancabrera02/srhollow

Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
cryptographydata-exfiltrationdefensive-tools+5
871 month ago
SilentNimvest preview

SilentNimvest

GitHubfrkngksl/silentnimvest

Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)

data-exfiltrationlateral-movementpassword-cracking+3
1086 months ago
Previous12…23Next