
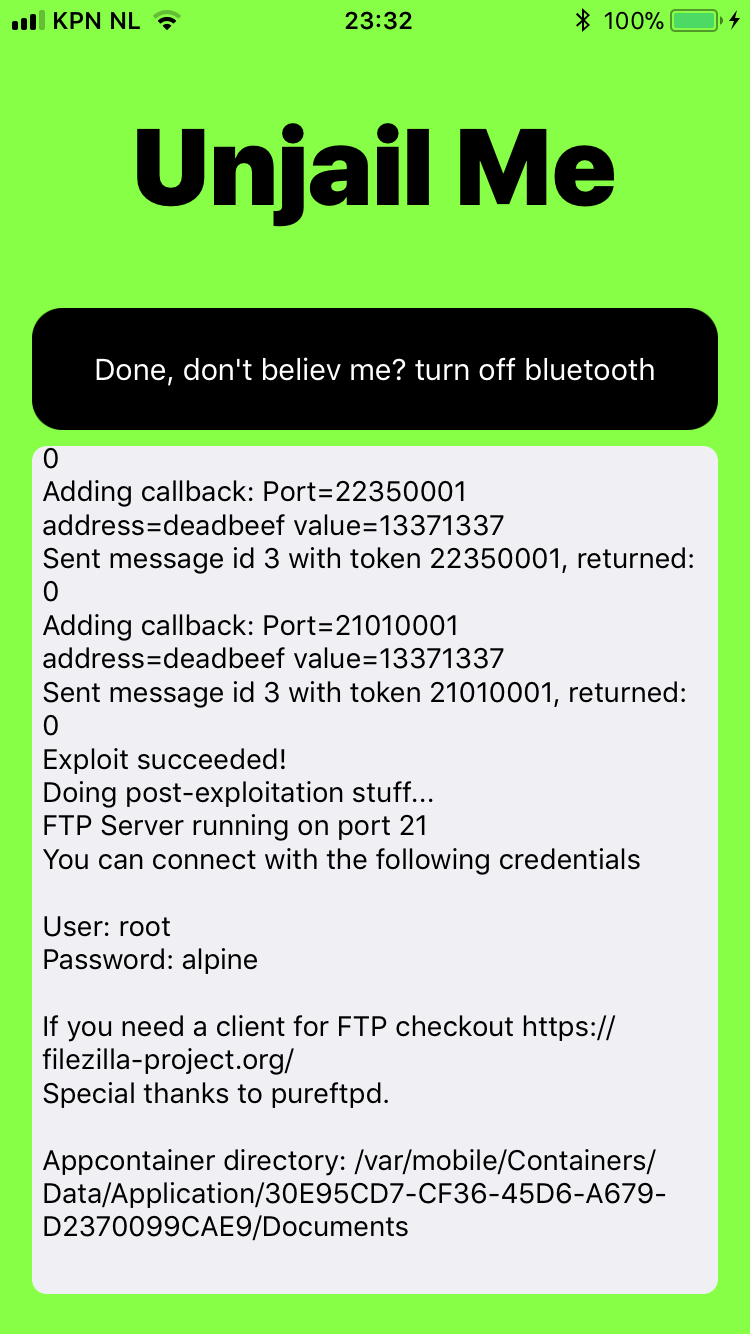
UnjailMe
 mtjailed/unjailme
A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
binary-exploitationexploitationexploit-frameworks+7
828 years ago
mtjailed/unjailmeA sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
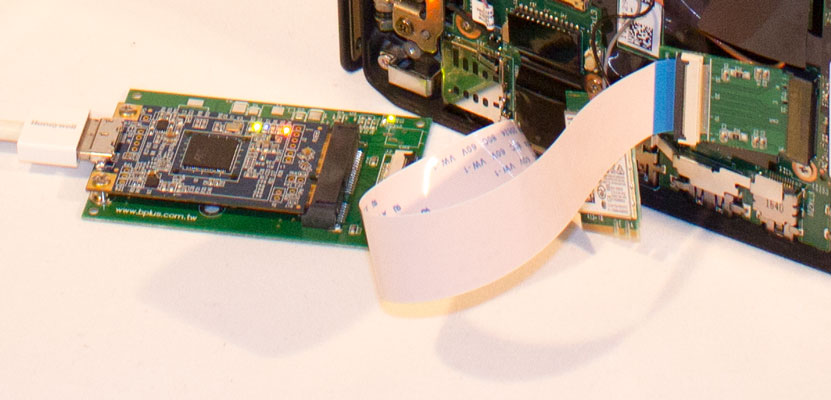 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
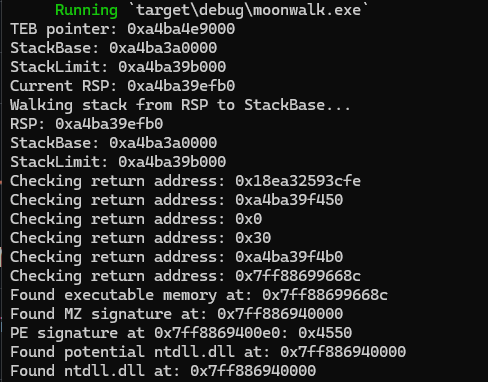 teach2breach/moonwalk
find dll base addresses without PEB WALK
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 nccgroup/diskwalker
Python script to efficiently find files on UNIX like file systems with specific properties (quicker than find)
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 randomrobbiebf/loot-me
Collects files and commands post-exploitation, formats them into Markdown reports, and helps find sensitive information for red team reporting.
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 rasta-mouse/sherlock
PowerShell script to quickly find missing software patches for local privilege escalation vulnerabilities.
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.