
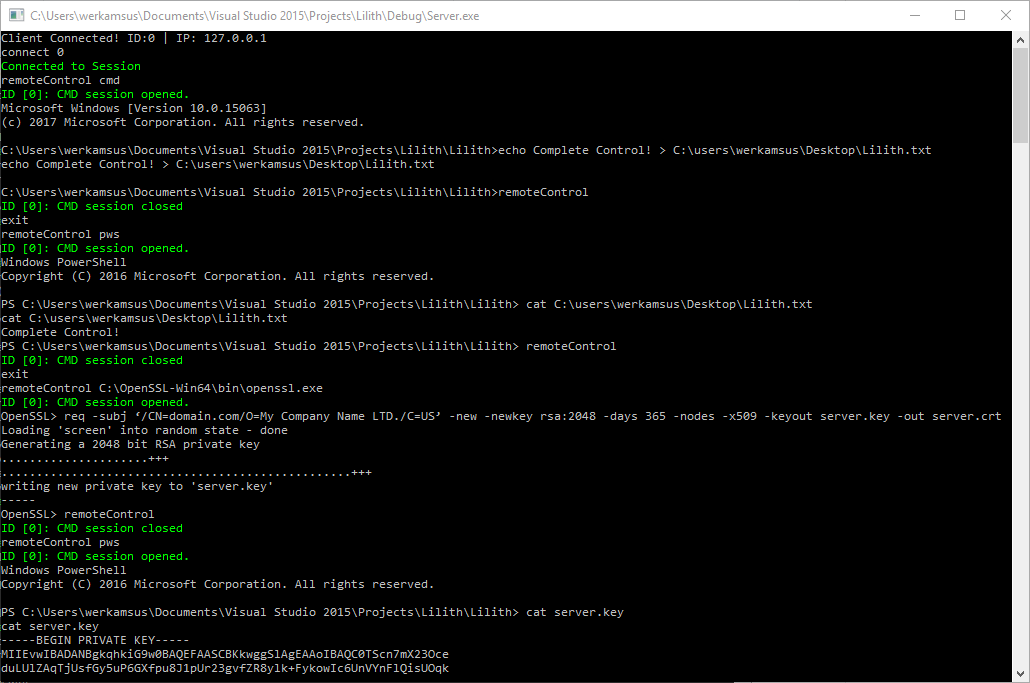
Lilith
 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
command-and-controlpayload-generationpenetration-testing+4
747
werkamsus/lilithLilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 cryptogenic/ps5-ipv6-kernel-exploit
An experimental webkit-based kernel exploit (Arb. R/W) for the PS5 on <= 4.51FW
 tiagorlampert/chaos
🔥 CHAOS is a free and open-source Remote Administration Tool that allow generate binaries to control remote operating systems.
 saadahla/githubc2
Github as C2 Demonstration , free API = free C2 Infrastructure
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 darthton/blackbone
Windows memory hacking library
 ashemery/exploitation-course
Offensive Software Exploitation Course
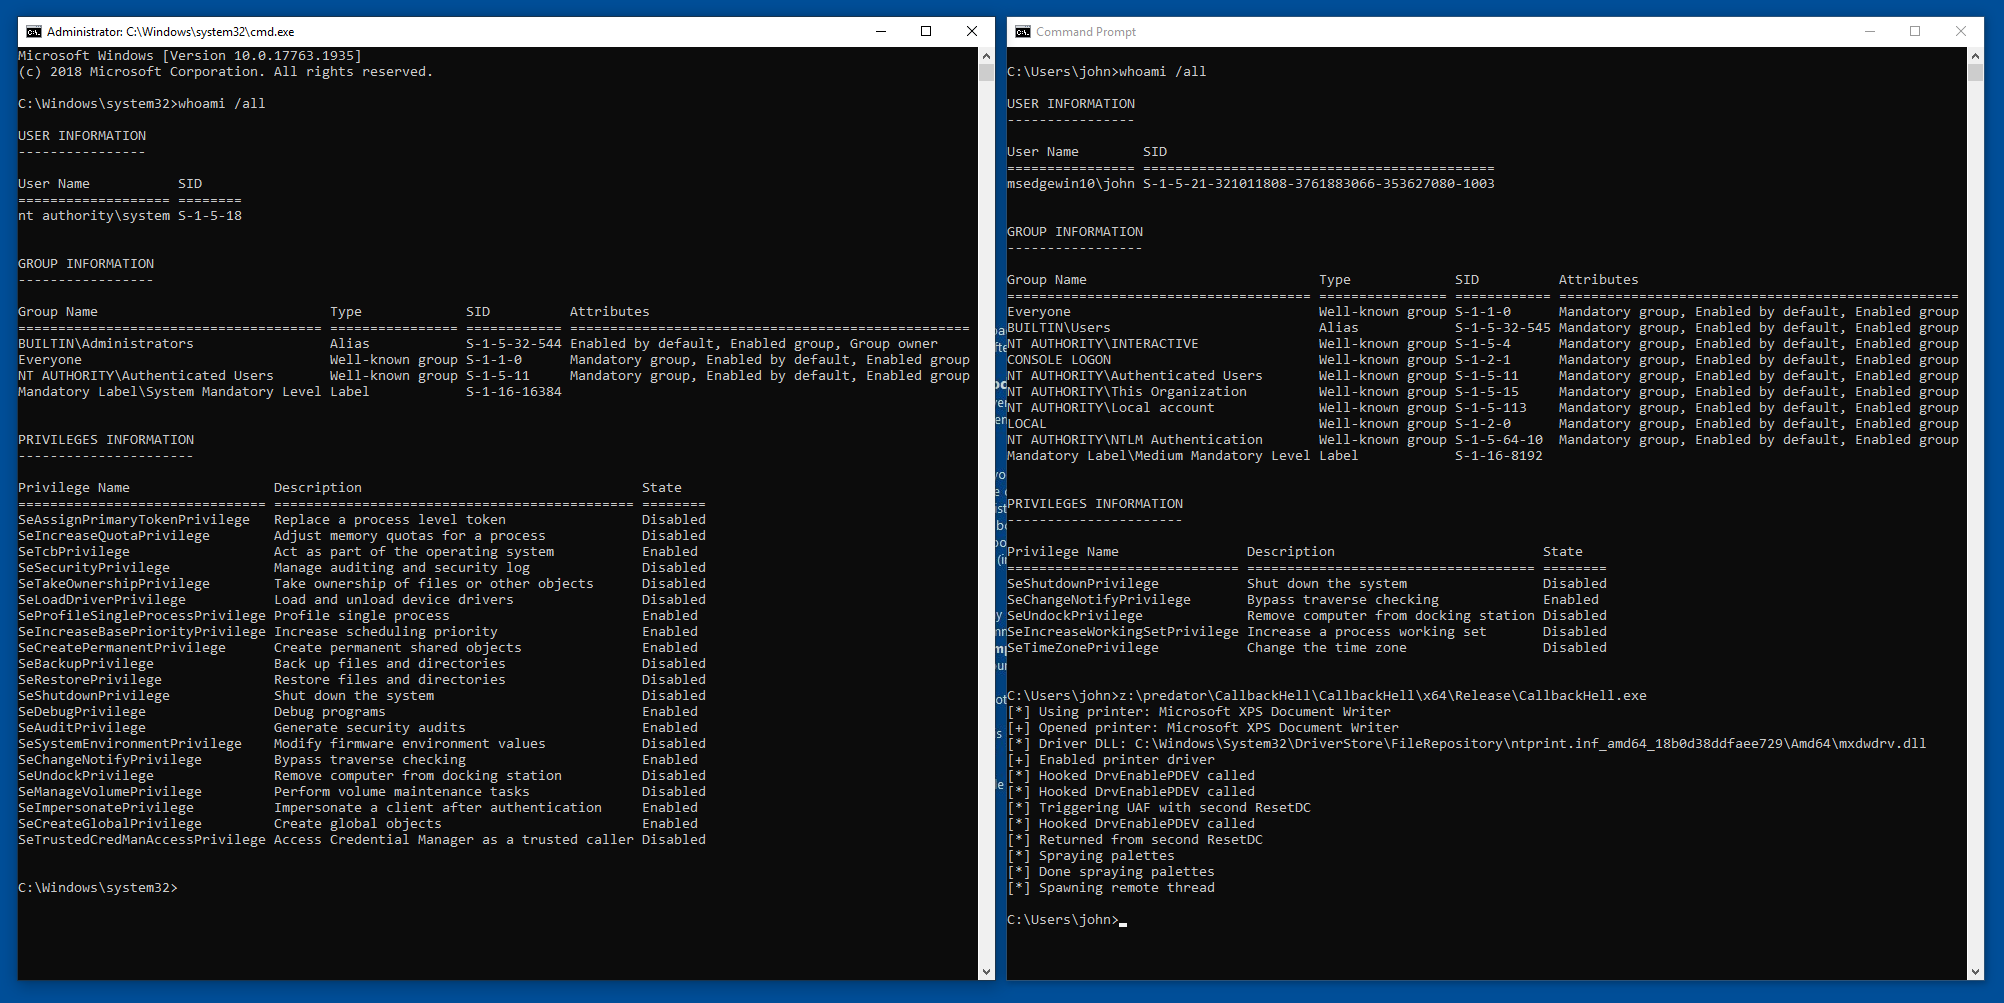 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
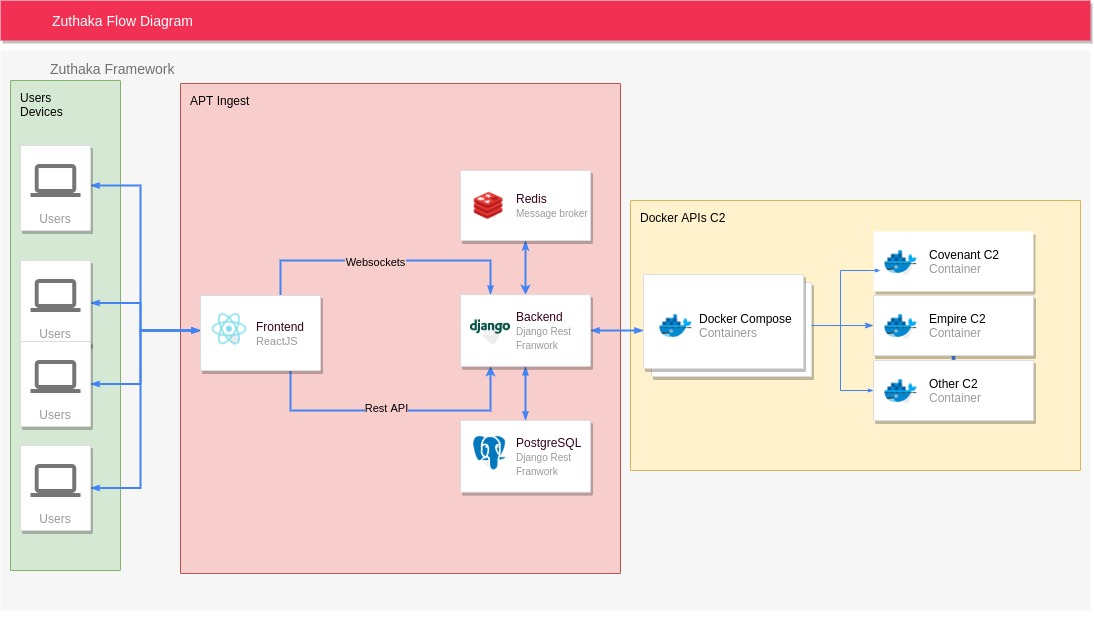 pucarasec/zuthaka
Open-source C2 integration framework providing a unified web interface for managing multiple command-and-control instances, listeners, agents, and…
 s4ntiagop/freebokuloader
A simple BOF that frees UDRLs
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 d4vinci/wormy
some python3 functions to add spreading features to any python backdoor
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
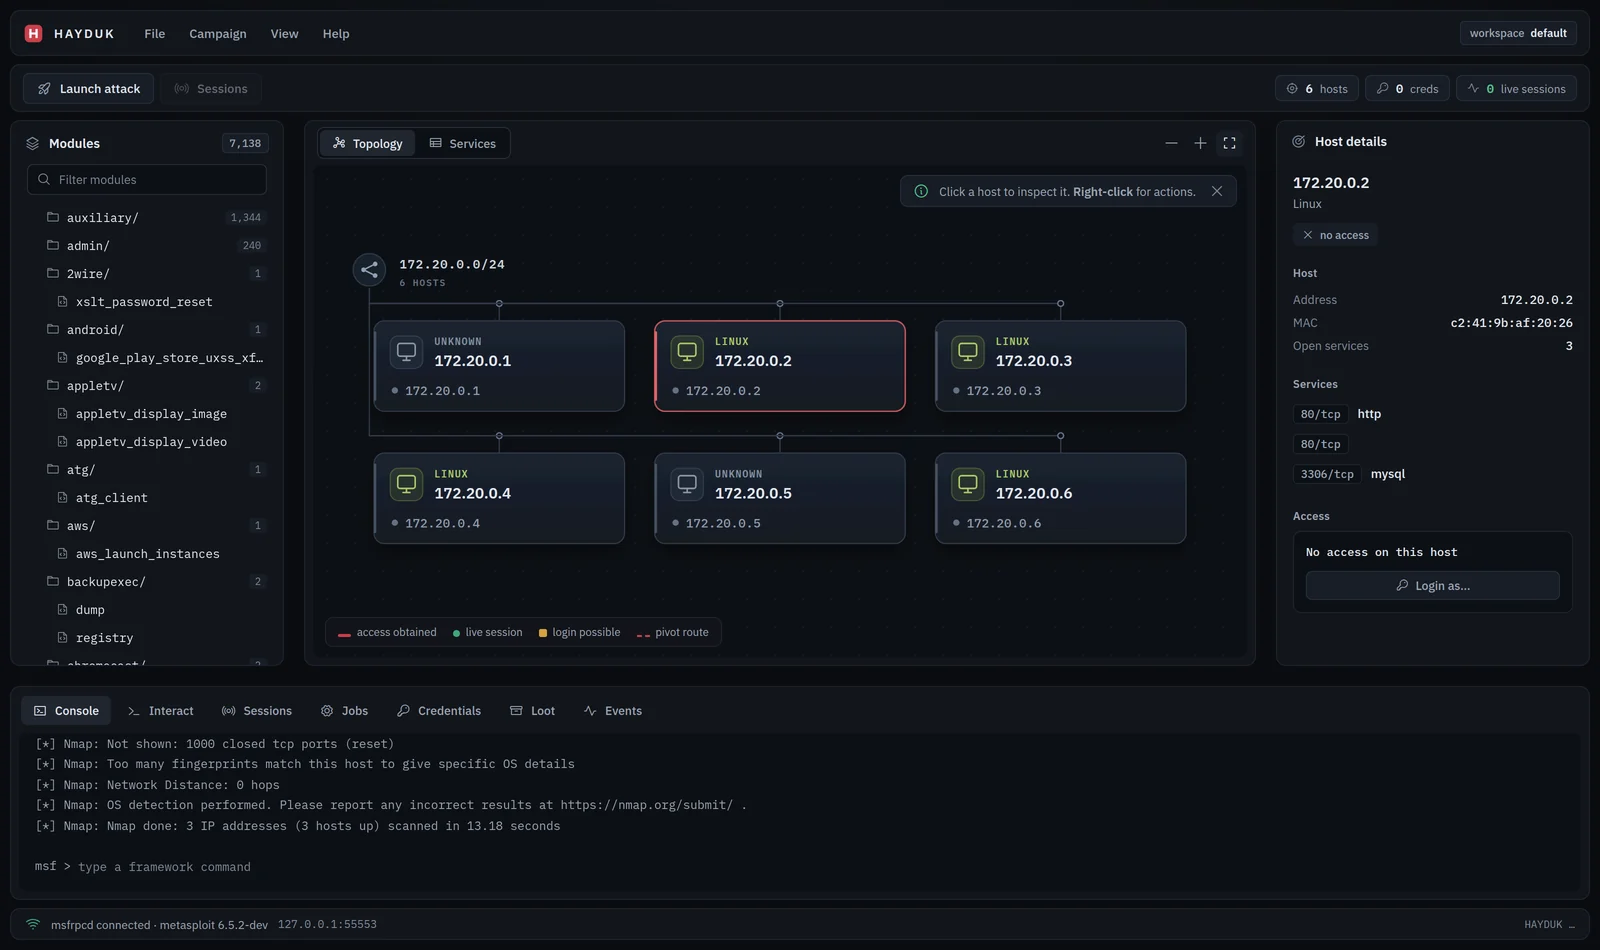 jolovicdev/hayduk
Graphical attack management console for Metasploit: the lineage of Armitage as a single Go binary with a browser UI. Live network topology, campaign…
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 yijiacloud/ghostlock-oppo-pckm00
CVE-2026-43499 GhostLock futex UAF LPE PoC for OPPO PCKM00 (SM6150) / Linux 4.14.180