
Archived
WEASEL
 facebookarchive/weasel
DNS covert channel implant for Red Teams.
command-and-controldns-analysisencryption-decryption-tools+5
731
 bishopfox/sliver
Adversary Emulation Framework
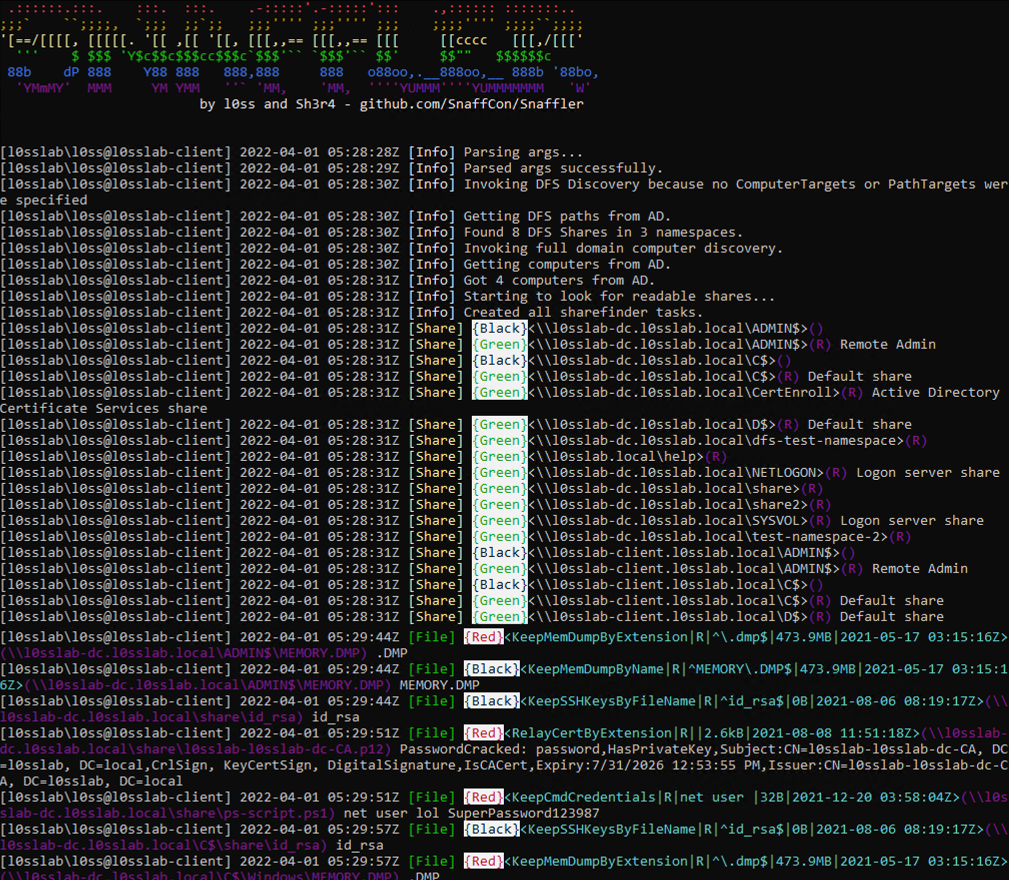 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
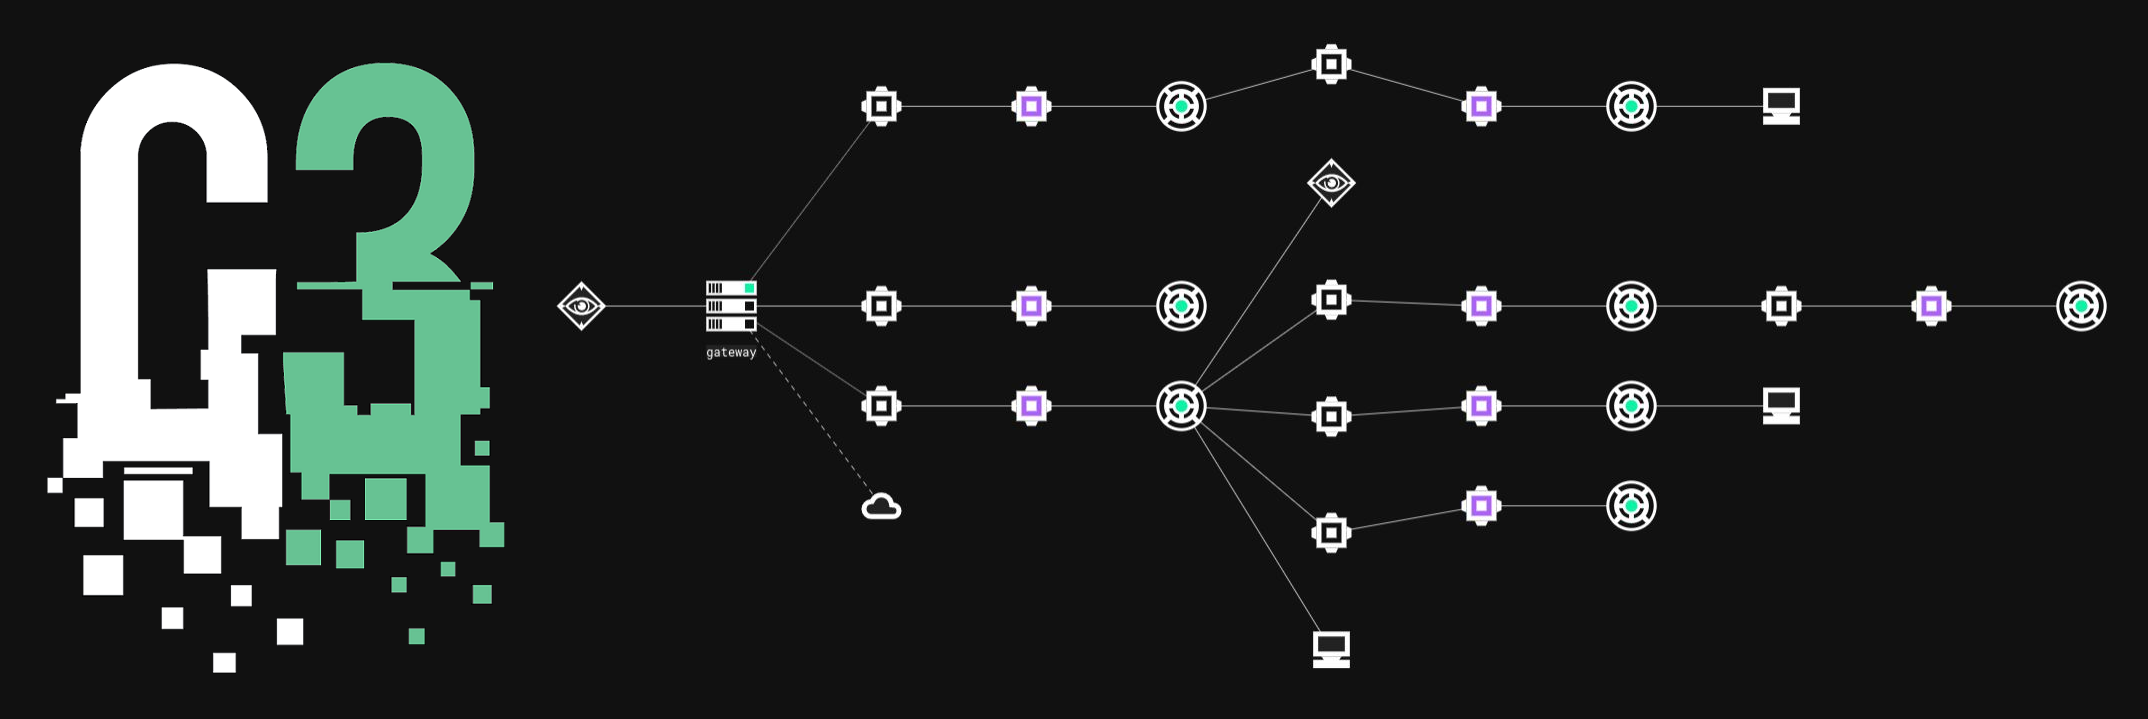 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
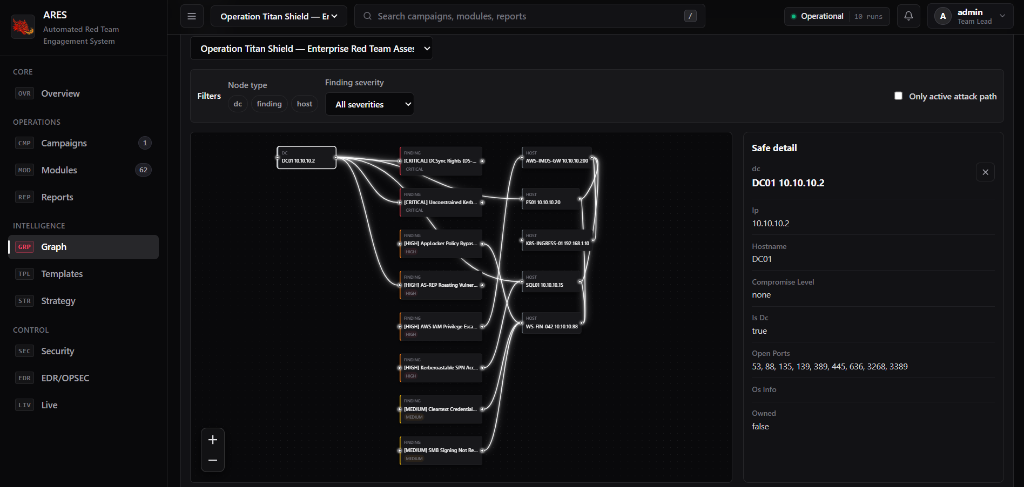 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 dragoqcc/cruciblec2
A C# Command & Control framework
 redteamoperations/pivotsuite
Network Pivoting Toolkit
 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 nettitude/poshc2_old
Powershell C2 Server and Implants
 justicerage/ffm
Freedom Fighting Mode: open source hacking harness
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
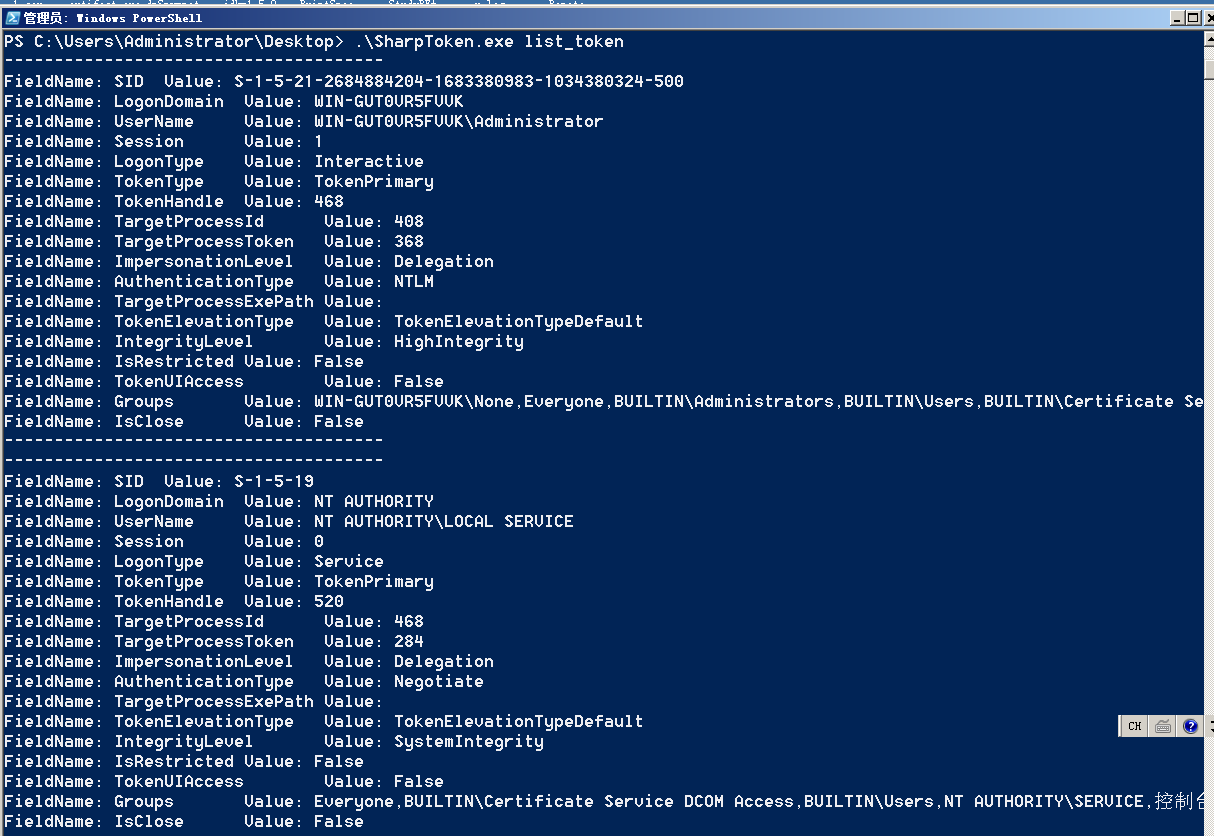 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
 hackerhouse-opensource/offensivelua
Offensive Lua.