
BRC4-BOF-Artillery
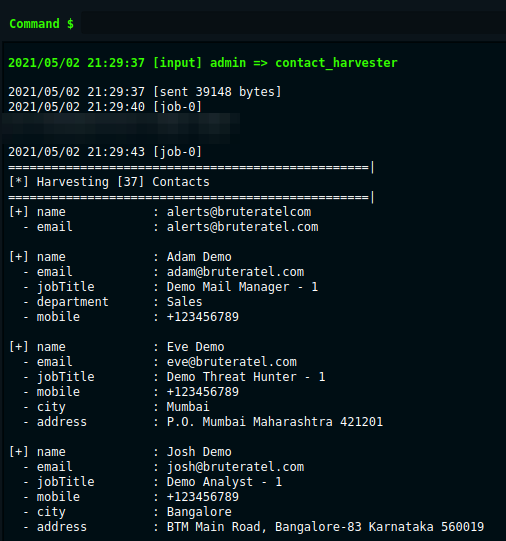
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

Decrypt GlobalProtect configuration and cookie files.

SCOMDecrypt is a tool to decrypt stored RunAs credentials from SCOM servers

pinky - The PHP mini RAT (Remote Administration Tool)


Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

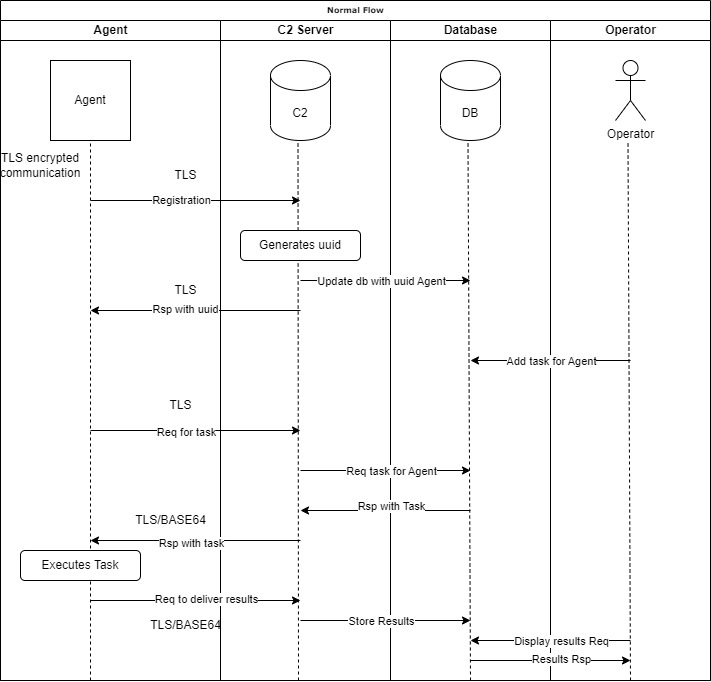
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.

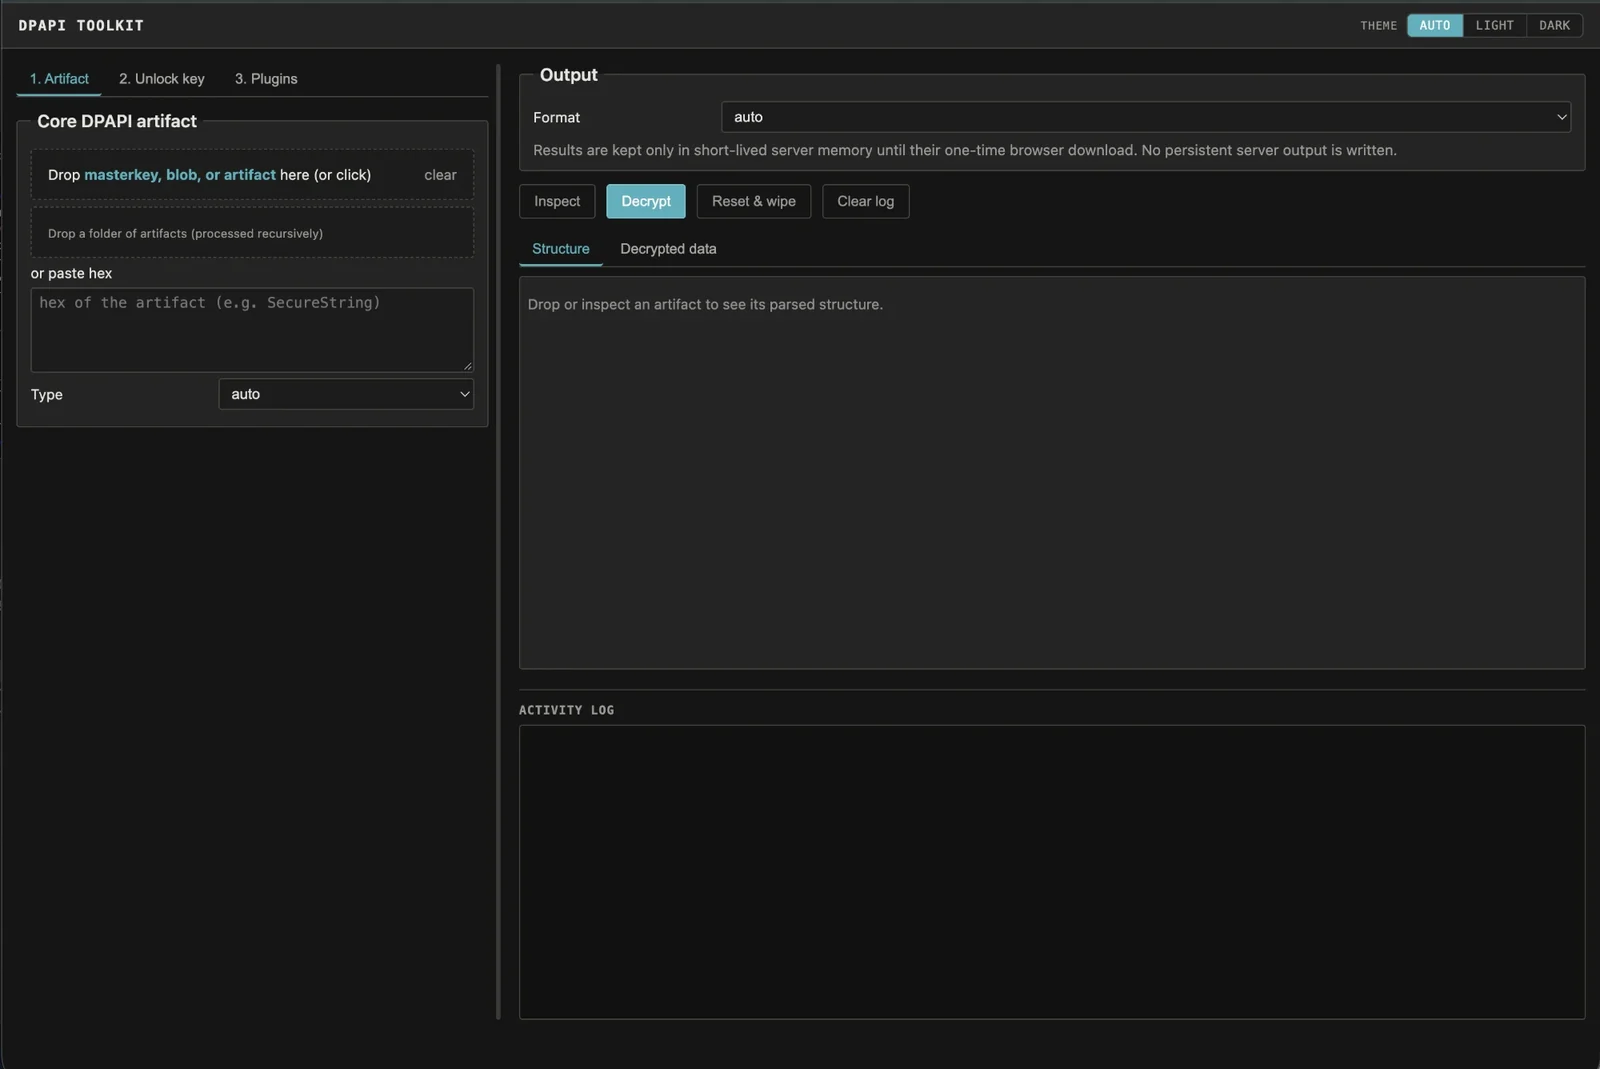
Drop any Windows DPAPI artifact and it identifies the format and the exact master key it needs, then decrypts once you supply the key. Offline, CLI +…

A small utility to translate NTDS.dit files to SQLite format.

DDoor - cross platform backdoor using dns txt records

:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)

A simple Toolkit to BF and decrypt Windows EntraId CacheData

Exploitation and Post-Exploitation Multitool for Palo Alto PAN-OS Systems affected by vulnerabilities CVE-2024-0012 and CVE-2024-9474

encrypted-linux-kernel-modules

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…