GodPotato-Aggressor-Script

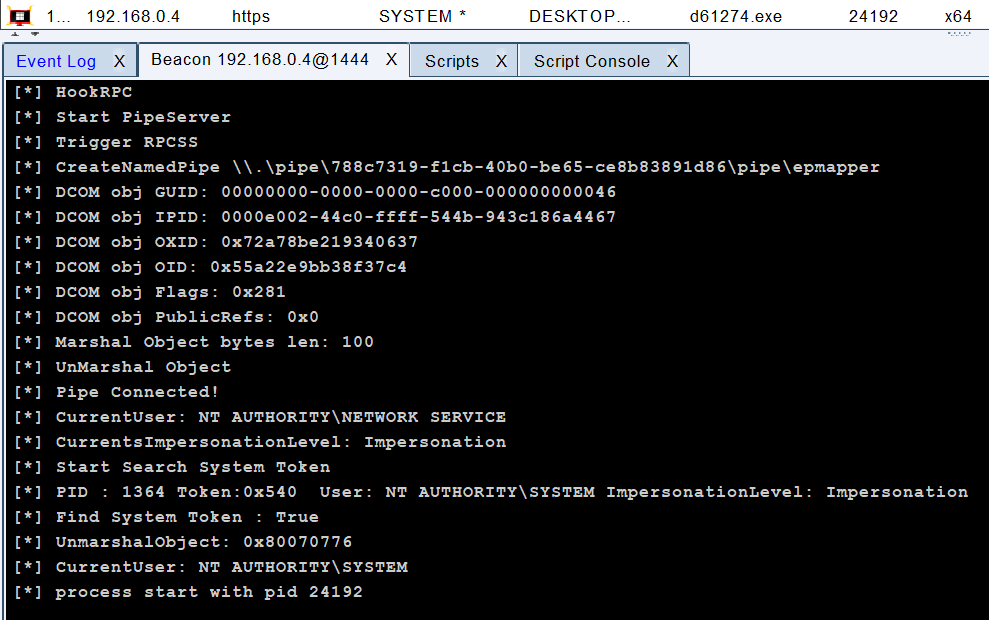
Cobalt Strike Aggressor script that automates Windows service-account-to-SYSTEM privilege escalation via GodPotato during red team operations.

Cobalt Strike Aggressor script that automates Windows service-account-to-SYSTEM privilege escalation via GodPotato during red team operations.

A care package of useful bofs for red team engagments

PoC that triggers Windows WebClient startup through EFS RPC call chains and WNF messages, enabling red teams to explore unprivileged service-start…

Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…

Windows Auto Post Exploitation - For ReD Team

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…

Single-file HTML cheat sheet for red teamers and pentesters with auto-injecting attacker/target variables, OS-aware reverse shell generator, and…

BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…

Comprehensive offensive security toolkit covering penetration testing, exploitation, and red teaming operations with modular attack workflows.

Host-based exploitation utility for penetration testing and red team operations, enabling payload delivery and post-exploitation actions on target…

Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…

SMB Red Team Lab— NTLM Relay via LLMNR Poisoning, CVE-2007-2447, NTLMv2 Hash Cracking & NT AUTHORITY\SYSTEM on Windows 10

Step-by-step penetration testing lab exploiting Samba CVE-2007-2447 on Metasploitable 2 using Metasploit, demonstrating root compromise, credential…

Collects files and commands post-exploitation, formats them into Markdown reports, and helps find sensitive information for red team reporting.

PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…

Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…

Browser-based C2 tunnel that exfiltrates payloads through Firefox's cookie.sqlite and auto-submitting HTML/JS, enabling stealthy firewall bypass for…