
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
156 results
MrKaplan preview

MrKaplan

GitHubidov31/mrkaplan

PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
defensive-toolsforensicsids-ips-evasion+3
276
3 years ago
SharpSploitConsole preview

SharpSploitConsole

GitHubanthemtotheego/sharpsploitconsole

C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
command-and-controlexploitationinformation-gathering+9
1814 years ago
Atomic-Red-Team-C2 preview

Atomic-Red-Team-C2

GitHubdarmado/atomic-red-team-c2

ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
command-and-controlexploit-frameworkspayload-generation+3
1782 years ago
EDR-Redir preview

EDR-Redir

GitHubtwosevenonet/edr-redir

Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
anti-botdefensive-toolsids-ips-evasion+5
2434 months ago
DSCourier preview

DSCourier

GitHubdylandavis1/dscourier

Proof-of-concept tool leveraging WinGet Configuration COM API to apply DSC configurations through Microsoft-signed binaries, enabling EDR bypass for…
configuration-auditingdefensive-toolspenetration-testing+3
2103 months ago
RedTeamScripts preview

RedTeamScripts

GitHubmr-un1k0d3r/redteamscripts

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
email-securityexploitationpassword-attacks+4
1485 years ago
PoisonApple preview

PoisonApple

GitHubcyborgsecurity/poisonapple

CLI tool for applying and removing macOS persistence mechanisms, designed for threat emulation and red team operations. Supports 17 techniques…
persistence-mechanismspost-exploitationred-teaming
2294 years ago
redteamguides.github.io preview

redteamguides.github.io

GitHubredteamguides/redteamguides.github.io

Red Team Guides
curated-resourceseducationexploitation+6
1452 years ago
Cohab_Processes preview

Cohab_Processes

GitHuboctoberfest7/cohab_processes

A small Aggressor script to help Red Teams identify foreign processes on a host machine

information-gatheringpenetration-testingpost-exploitation+2
893 years ago
aad-bofs preview

aad-bofs

GitHubkozmer/aad-bofs

Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
adversarial-attackcloud-infrastructure-securitycloud-security+5
14110 months ago
Azur3Alph4 preview

Azur3Alph4

GitHubhyd3sec/azur3alph4

PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
cloud-securityinformation-gatheringpenetration-testing+3
635 years ago
PickleC2 preview

PickleC2

GitHubxret2pwn/picklec2

Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.

command-and-controllateral-movementpenetration-testing-frameworks+2
985 years ago
DynastyPersist preview

DynastyPersist

GitHubtrevohack/dynastypersist

Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
ctfpenetration-testingpersistence-mechanisms+3
1611 year ago
Commander preview

Commander

GitHubvoukatas/commander

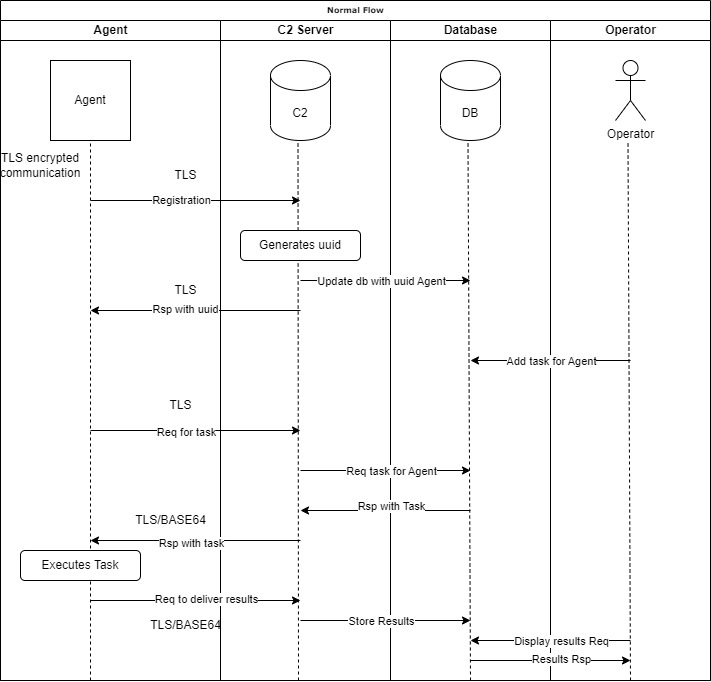
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…

command-and-controlencryption-decryption-toolspayload-development+3
632 years ago
scour preview

scour

GitHubgrines/scour

Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…

cloud-securityexploitationlateral-movement+4
1272 years ago
process-enumeration-stealth preview

process-enumeration-stealth

GitHublloydlabs/process-enumeration-stealth

Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…

ids-ips-evasioninformation-gatheringpost-exploitation+2
842 years ago
PT-ToolKit preview

PT-ToolKit

GitHubblacksnufkin/pt-toolkit

Exploits Scripts and other tools that are useful during Penetration-Testing or Red Team engagement
exploitationpayload-developmentpenetration-testing+5
744 years ago
Shell3er preview

Shell3er

GitHubyehia-mamdouh/shell3er

PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…

command-and-controlpayload-generationpersistence-mechanisms+3
803 years ago
Previous1…345…9Next