
red-kube
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
adversarial-attackcloud-securitycommand-and-control+6
8275 years ago
lightspin-tech/red-kubeRed Team K8S Adversary Emulation Based on kubectl
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
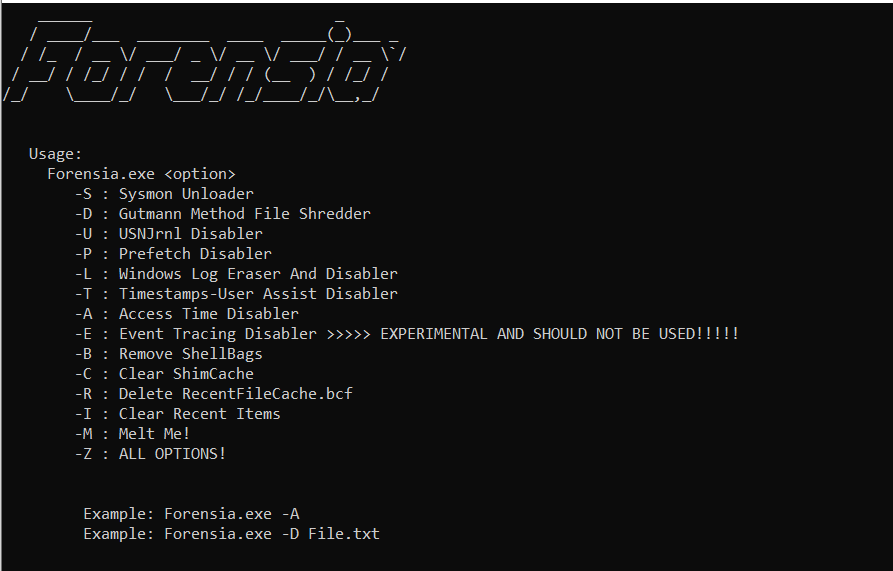 paulnorman01/forensia
Anti Forensics Tool For Red Teamers, Used For Erasing Footprints In The Post Exploitation Phase.
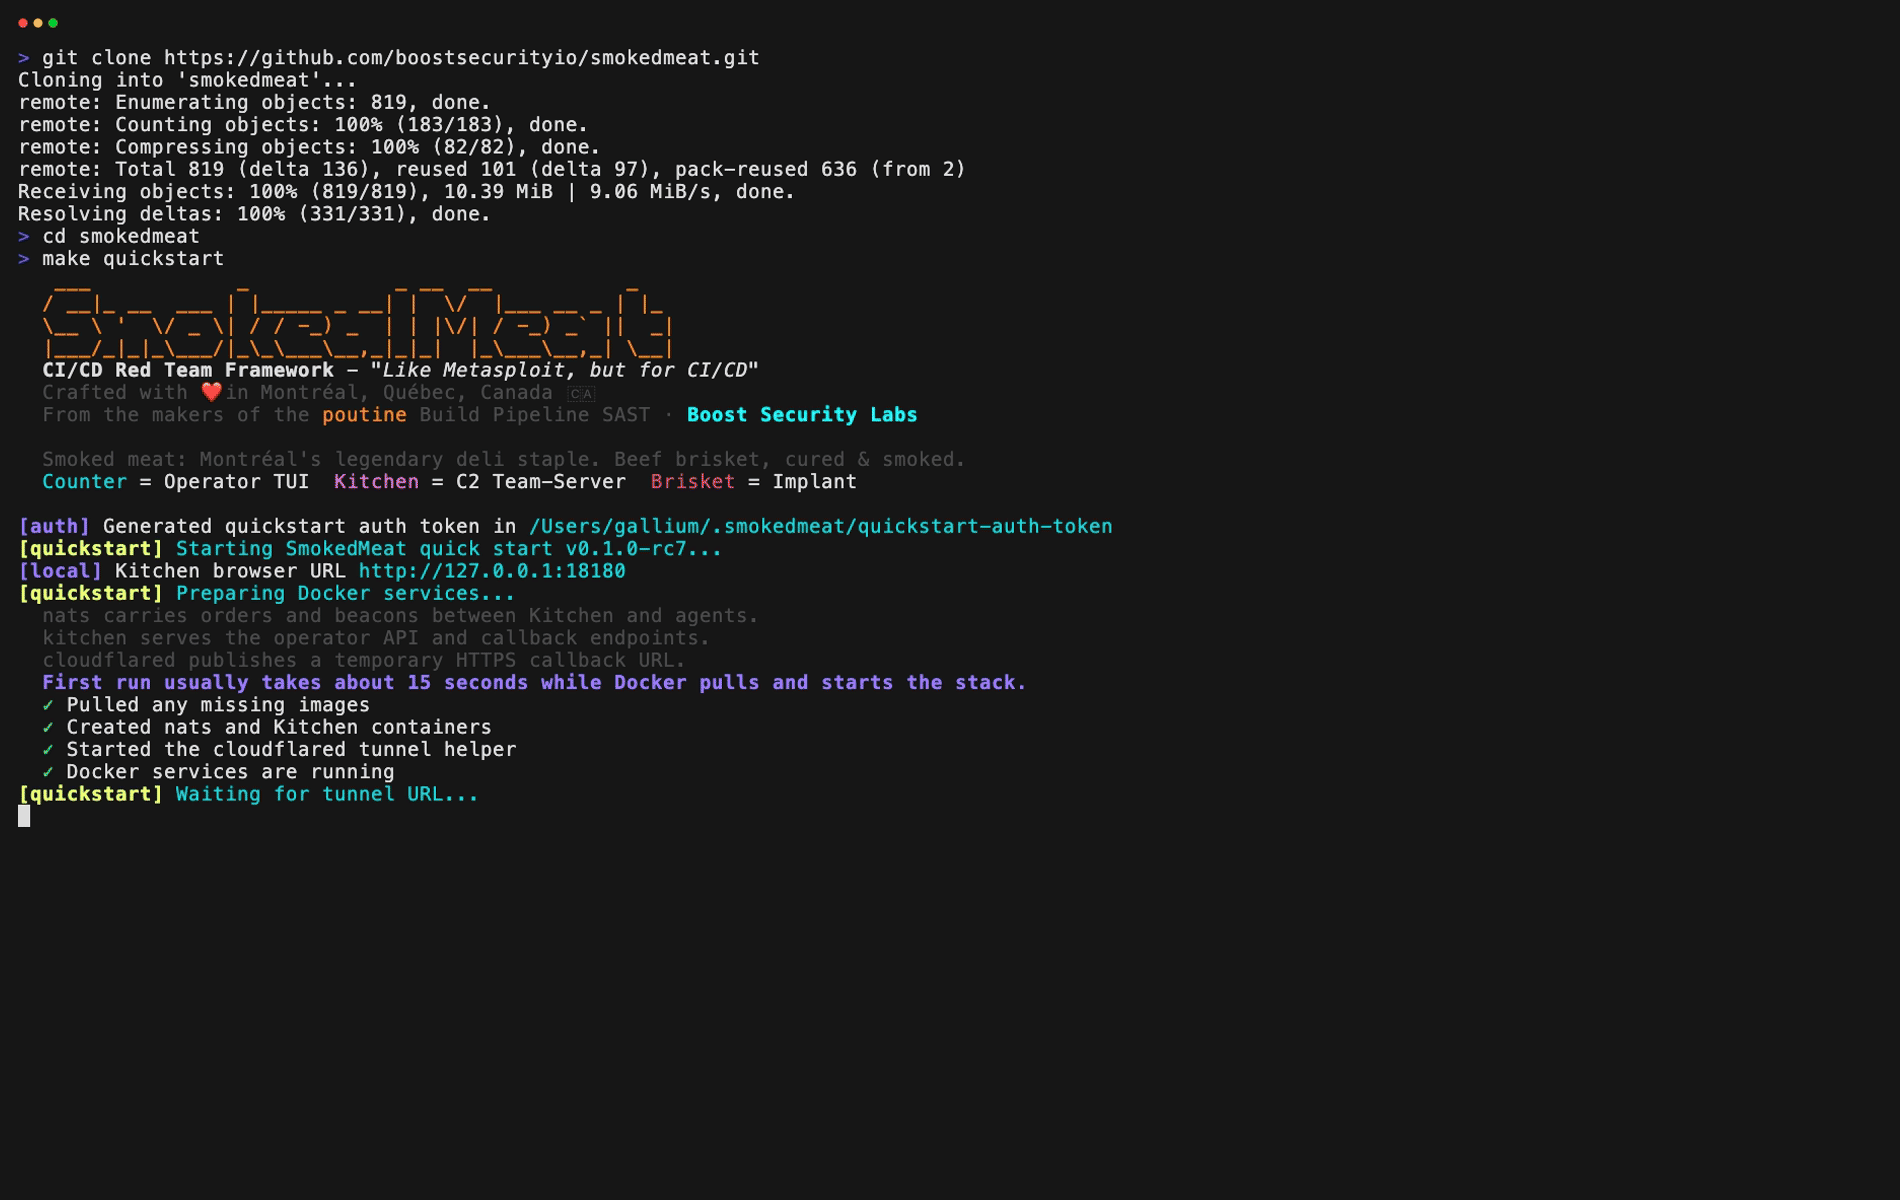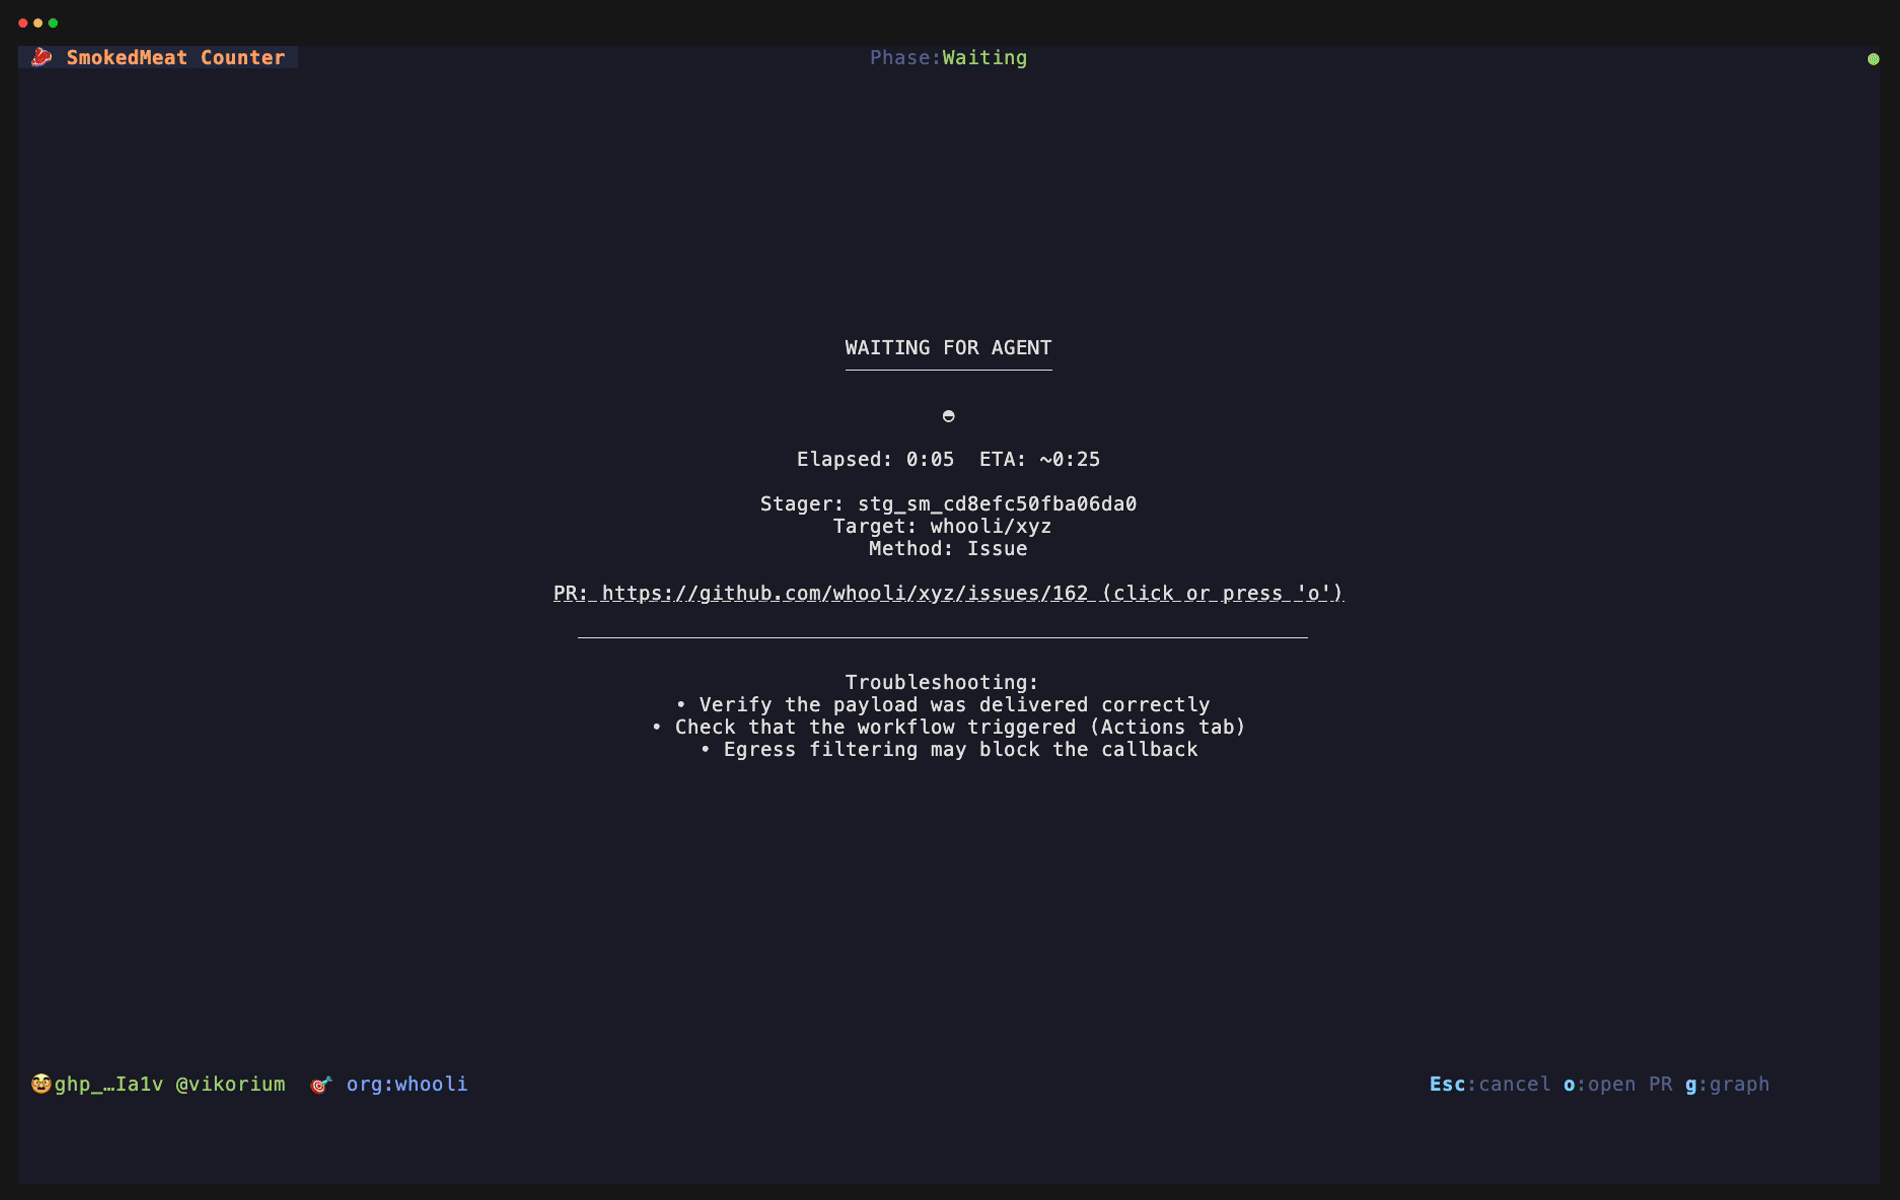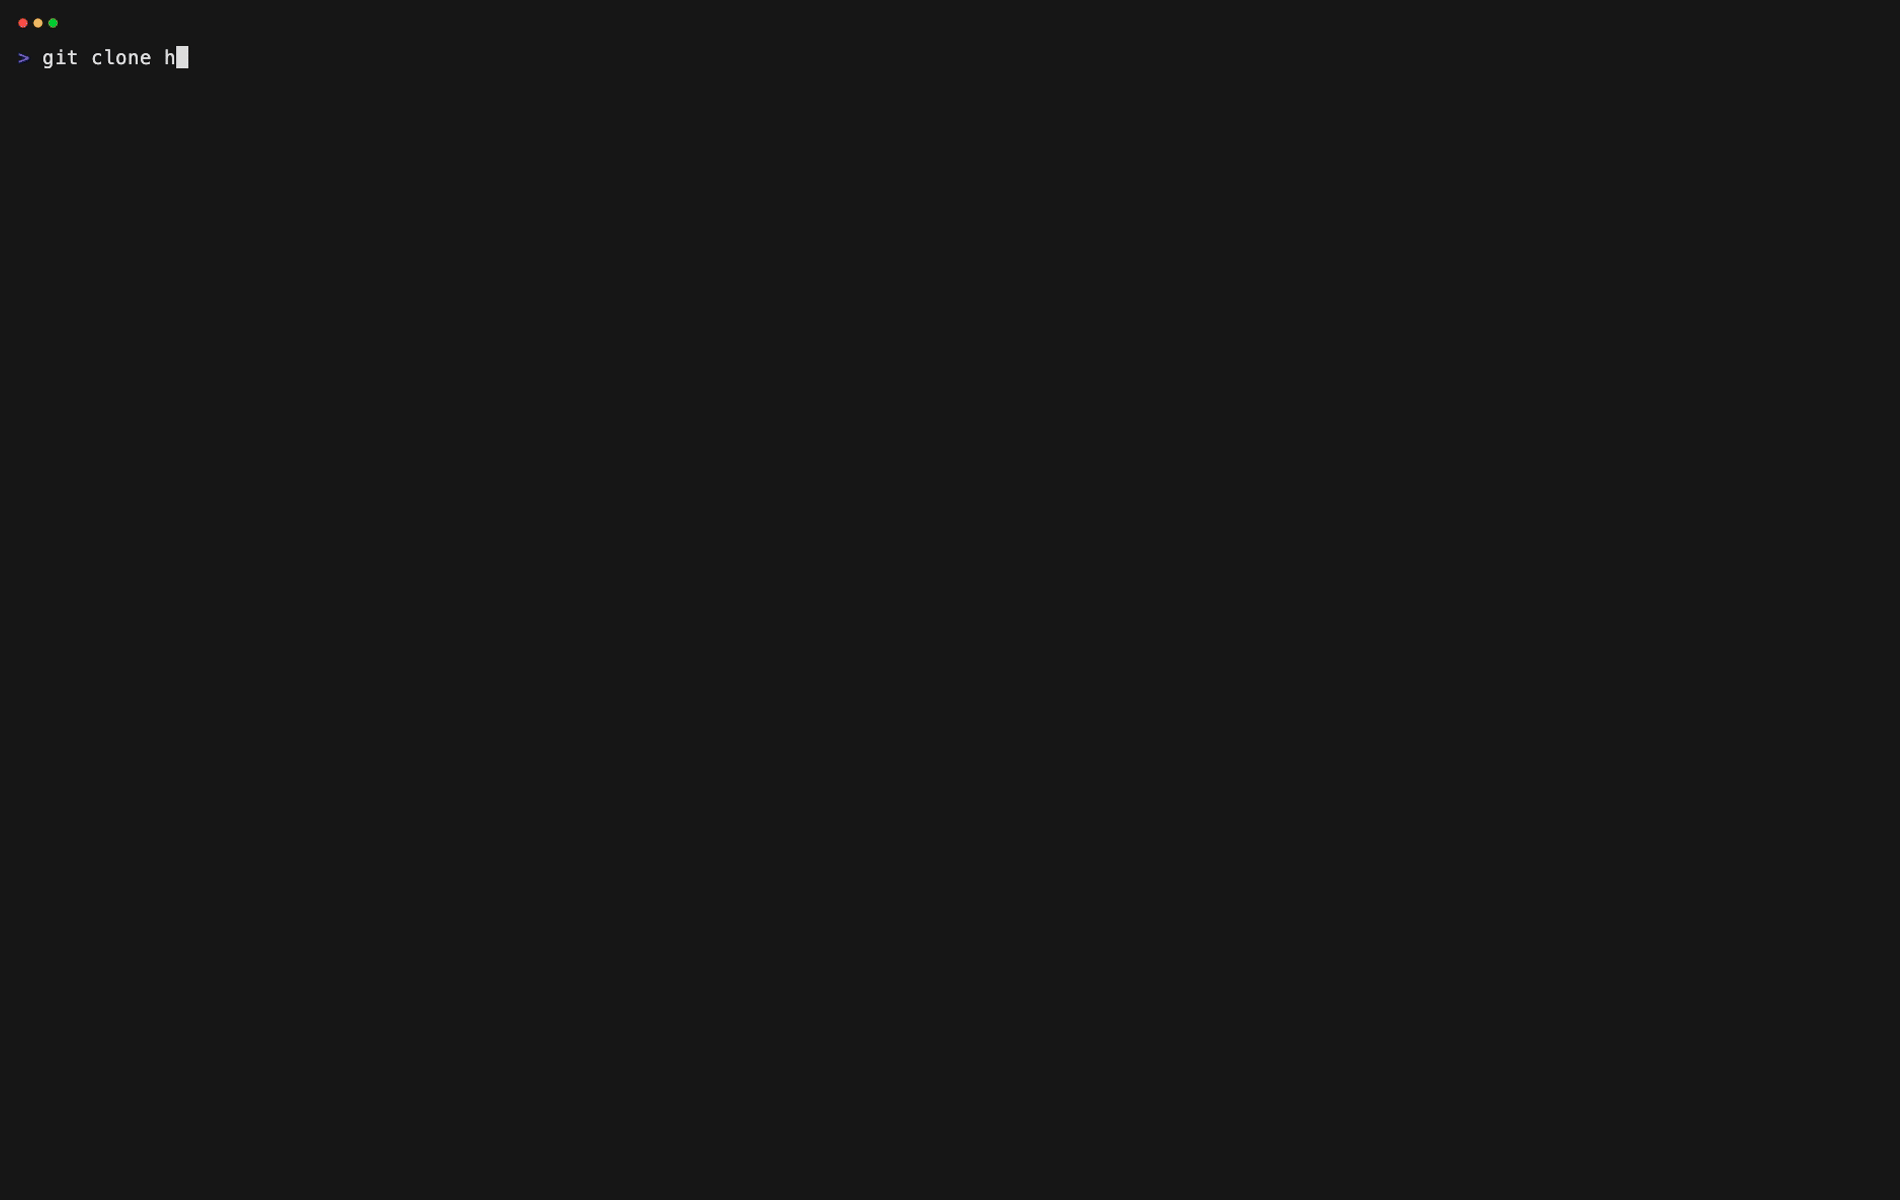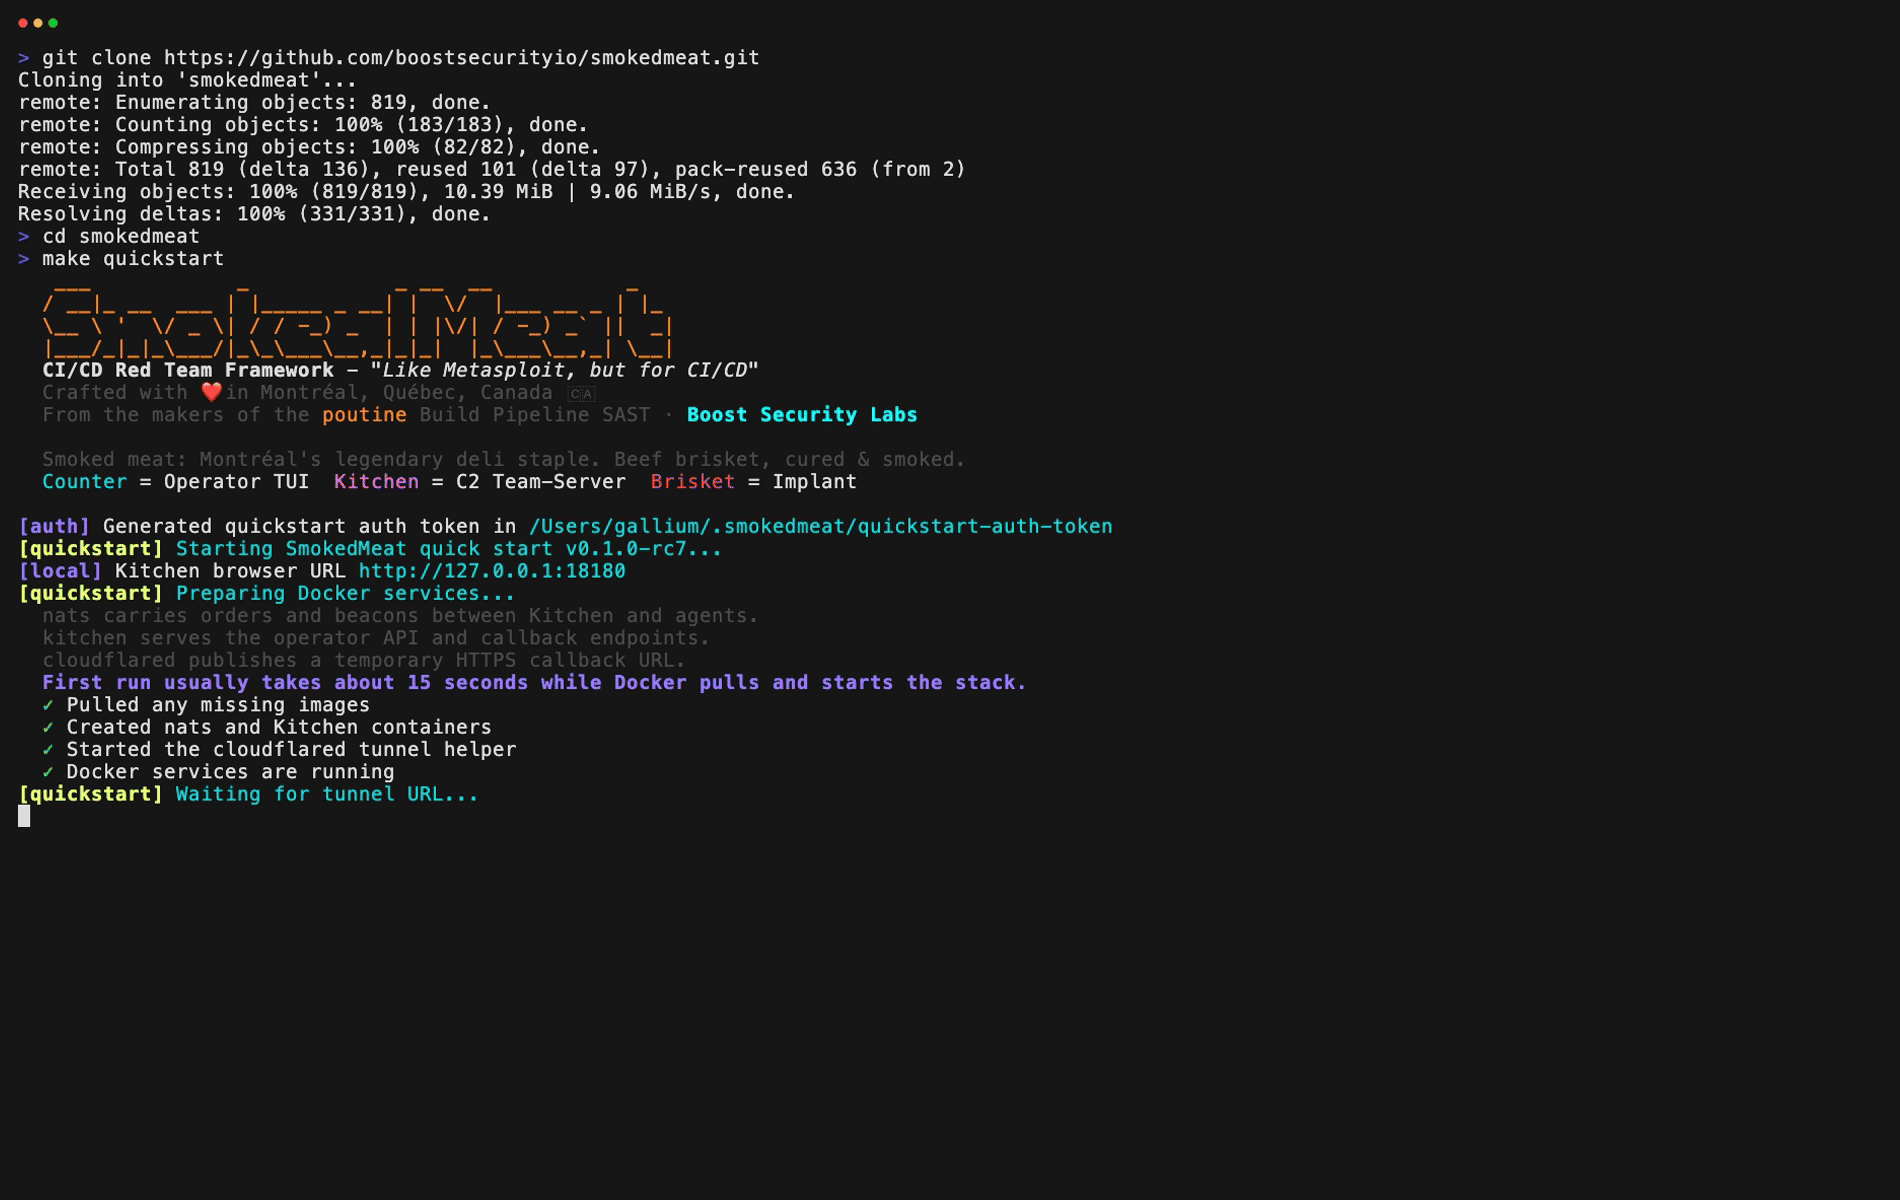 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 darkoperator/mimikatz-missing-manual
Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…
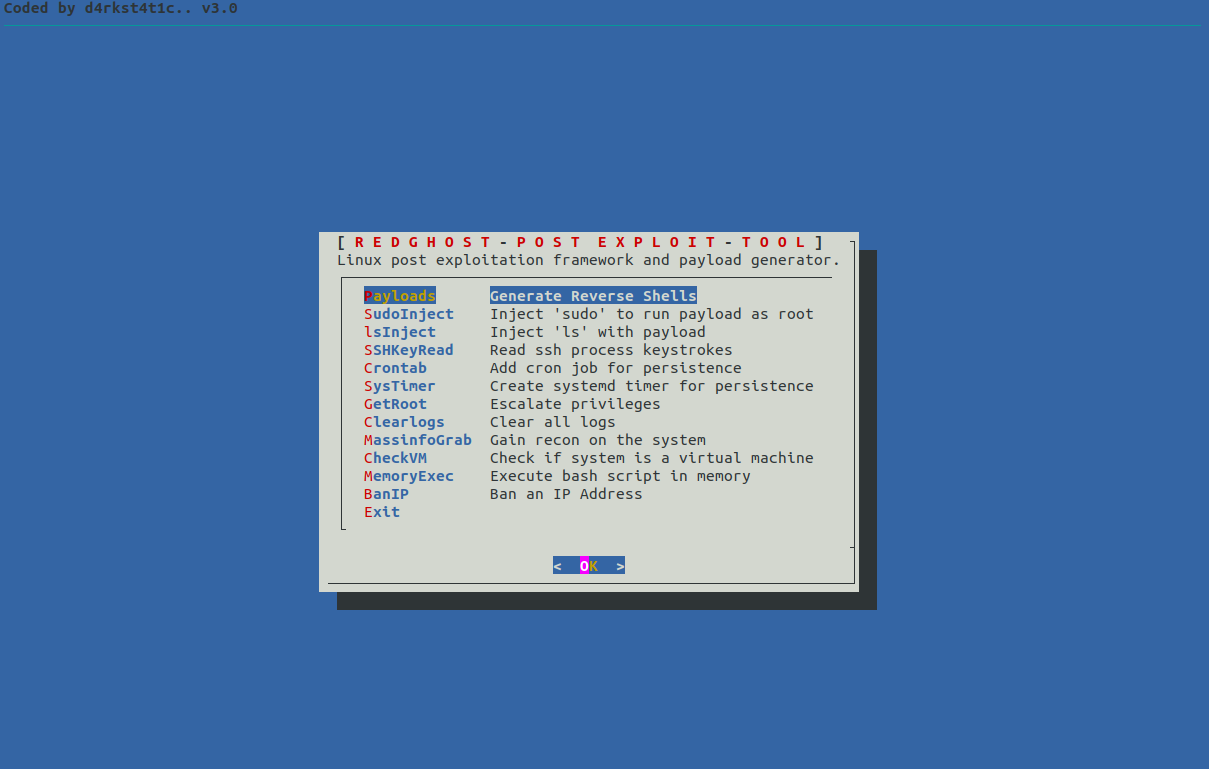 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
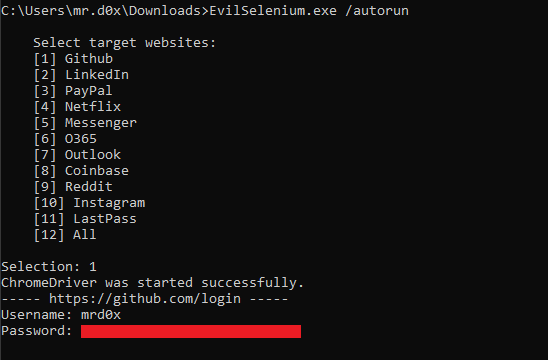 mrd0x/evilselenium
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 0xdea/blindsight
Red teaming tool to dump LSASS memory, bypassing basic countermeasures.
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
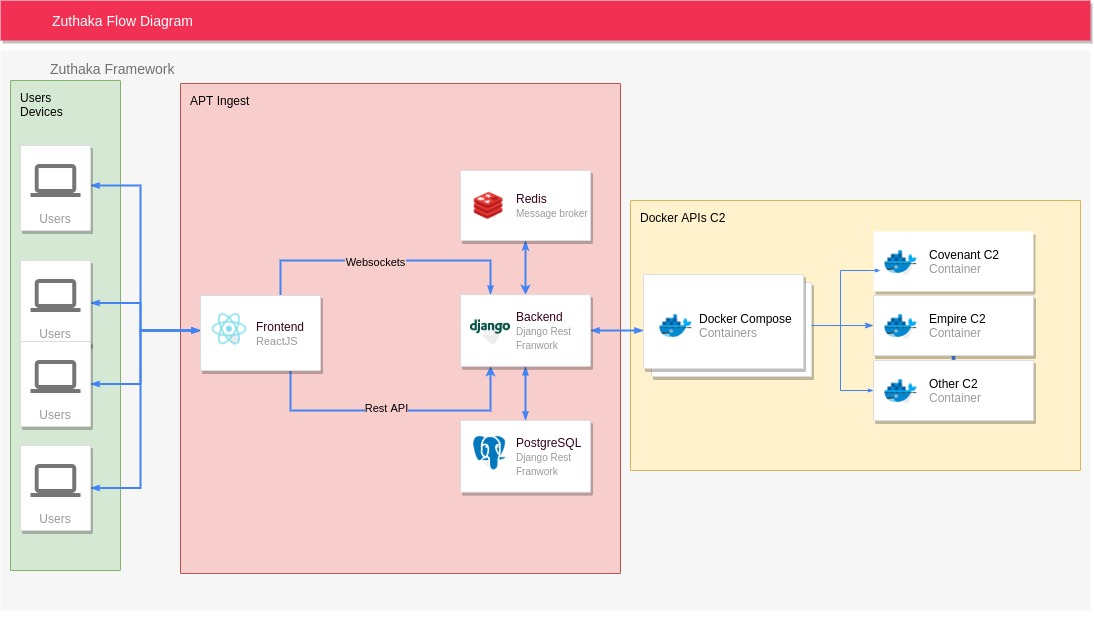 pucarasec/zuthaka
Open-source C2 integration framework providing a unified web interface for managing multiple command-and-control instances, listeners, agents, and…
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
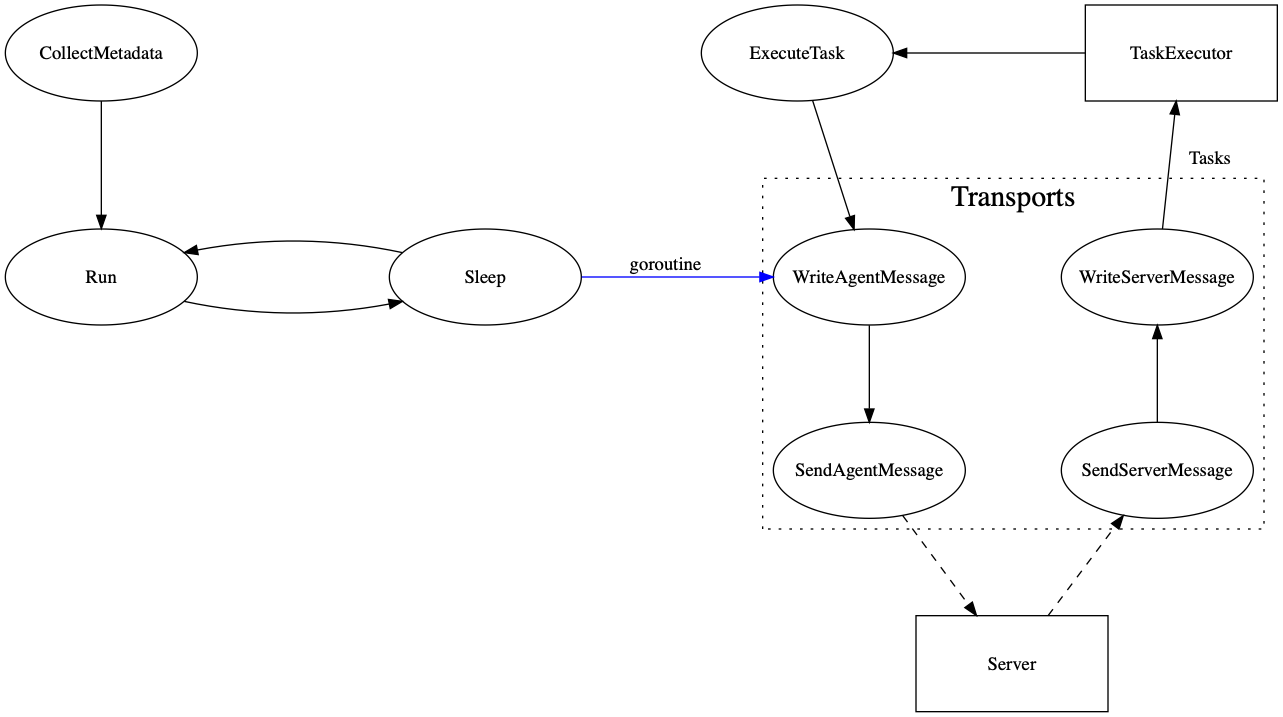 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
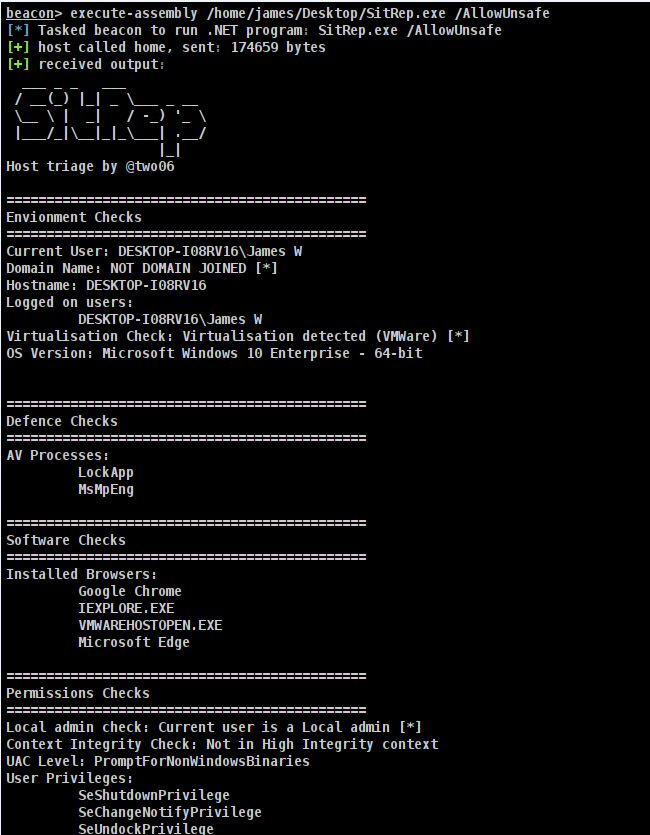 mdsecactivebreach/sitrep
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
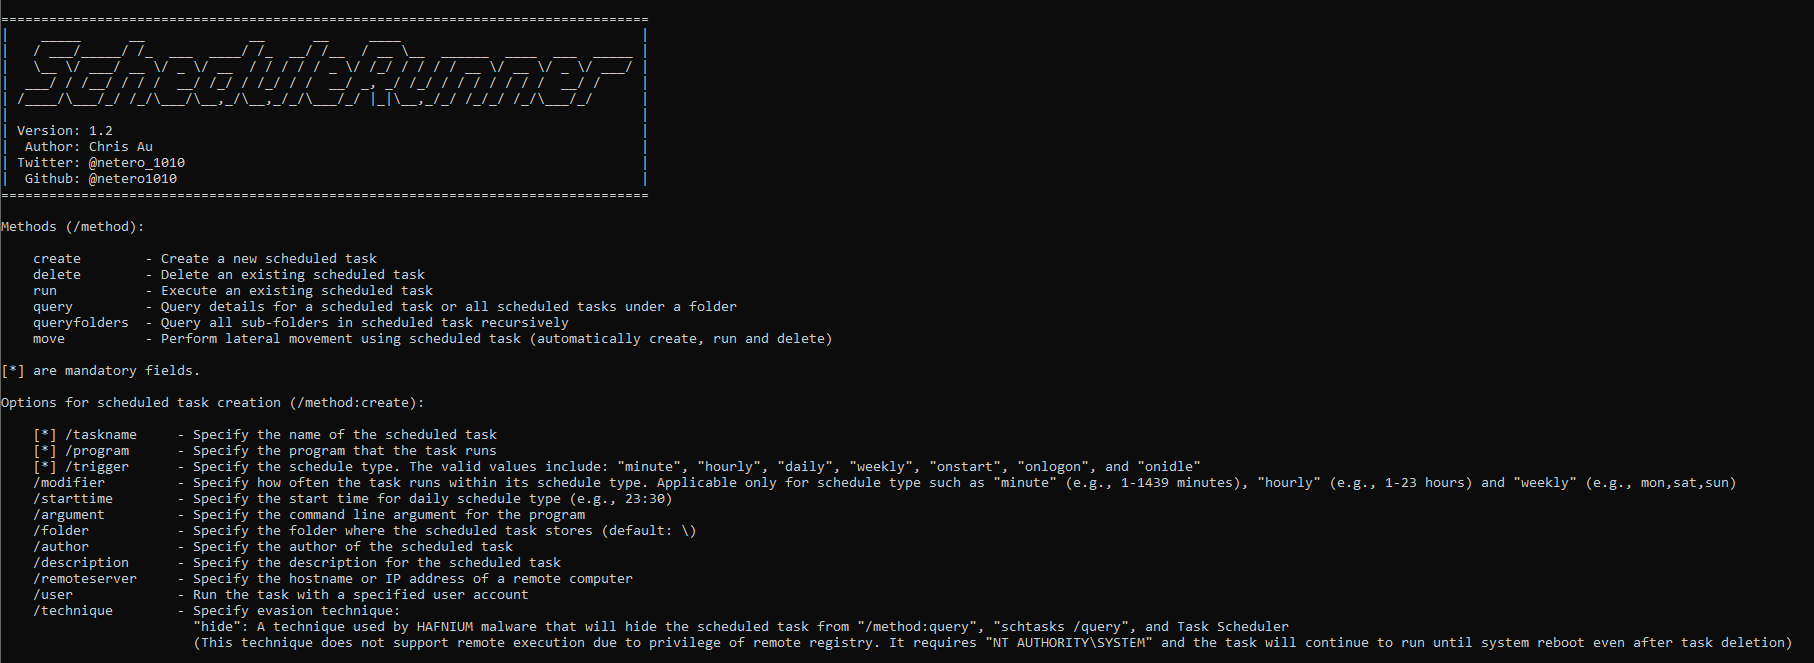 netero1010/schedulerunner
A C# tool with more flexibility to customize scheduled task for both persistence and lateral movement in red team operation