
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
71 results
CVE-2025-56383 preview

CVE-2025-56383

GitHubnewcomrade12211/cve-2025-56383

DLL hijacking to rev shell

binary-exploitationexploitationpayload-development+2
10 years ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.5k4 years ago
CompMgmtLauncher_DLL_UACBypass preview

CompMgmtLauncher_DLL_UACBypass

GitHubhackerhouse-opensource/compmgmtlauncher_dll_uacbypass

CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive
exploitationpersistence-mechanismspost-exploitation+2
1099 months ago
iscsicpl_bypassUAC preview

iscsicpl_bypassUAC

GitHubhackerhouse-opensource/iscsicpl_bypassuac

UAC bypass for x64 Windows 7 - 11
exploitationpayload-developmentpost-exploitation+2
8489 months ago
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

Dumping LSASS with a duplicated handle from custom LSA plugin
post-exploitationprivilege-escalationred-teaming
2074 years ago
RunAsWinTcb preview

RunAsWinTcb

GitHubtastypepperoni/runaswintcb

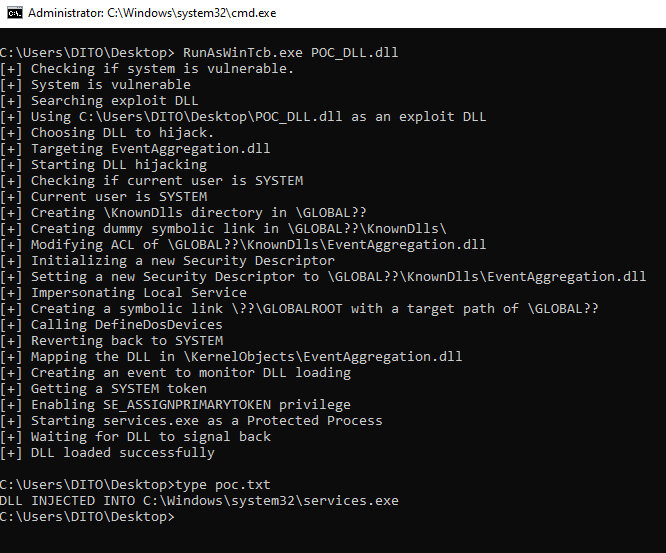
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
exploitationids-ips-evasionpost-exploitation+2
1384 years ago
azbelt preview

azbelt

GitHubdaddycocoaman/azbelt

AAD related enumeration in Nim

authenticationcloud-securityidentity-access-management+5
1323 years ago
QuickAssist_UAC_Bypass preview

QuickAssist_UAC_Bypass

GitHubr41n3rzuf477/quickassist_uac_bypass

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
defensive-toolsexploitationpayload-development+4
2443 months ago
DropSpawn_BOF preview

DropSpawn_BOF

GitHuboctoberfest7/dropspawn_bof

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
binary-exploitationexploitationpayload-development+4
2873 years ago
IDiagnosticProfileUAC preview

IDiagnosticProfileUAC

GitHubwh04m1001/idiagnosticprofileuac

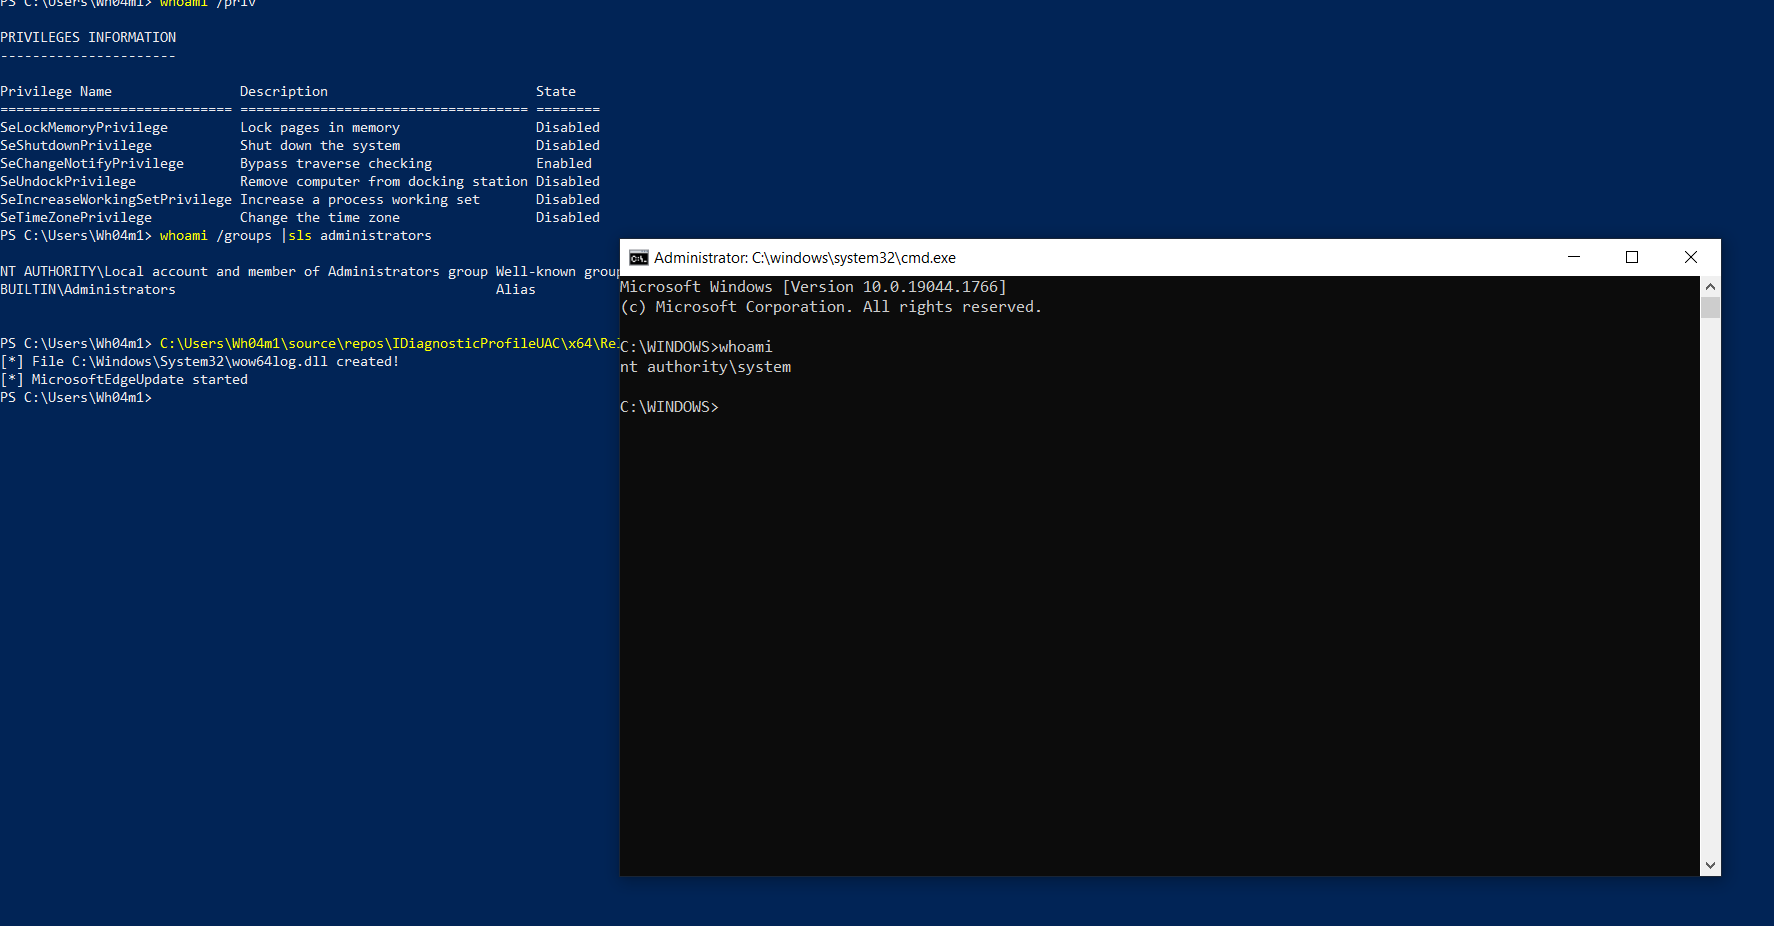
Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…
exploitationpenetration-testingpost-exploitation+2
1844 years ago
CS-DropSpawn_BOF preview

CS-DropSpawn_BOF

GitHubgmh5225/cs-dropspawn_bof

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
exploitationpayload-developmentpenetration-testing+2
33 years ago
KeeFarceReborn preview

KeeFarceReborn

GitHubd3lb3/keefarcereborn

A standalone DLL that exports databases in cleartext once injected in the KeePass process.
data-exfiltrationpassword-attackspayload-generation+3
2993 years ago
NimDllSideload preview
Archived

NimDllSideload

GitHubbyt3bl33d3r/nimdllsideload

DLL sideloading/proxying with Nim!

binary-analysispayload-developmentpayload-generation+2
1753 years ago
ReflectiveDLLRefresher preview

ReflectiveDLLRefresher

GitHubcylancevulnresearch/reflectivedllrefresher

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
ids-ips-evasionmalware-analysispayload-development+6
3248 years ago
ExecIT preview

ExecIT

GitHubflorylsk/execit

Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2242 years ago
TeamViewer_Permissions_Hook_V1 preview

TeamViewer_Permissions_Hook_V1

GitHubgellin/teamviewer_permissions_hook_v1

A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.

educationexploitationlateral-movement+5
3108 years ago
TeamsImplant preview

TeamsImplant

GitHuballevon412/teamsimplant

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…

command-and-controlexploit-frameworkspayload-development+5
2084 years ago
WHFB-PinCapture preview

WHFB-PinCapture

GitHubivancabrera02/whfb-pincapture

Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…

debuggersinformation-gatheringmemory-forensics+5
615 days ago
Previous1234Next
