
EggShell
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
command-and-controlexploitationinformation-gathering+7
lucasjacks0n/eggshelliOS/macOS/Linux Remote Administration Tool
 secgroundzero/warberry
WarBerryPi - Tactical Exploitation
 sense-of-security/adrecon
ADRecon is a tool which gathers information about the Active Directory and generates a report which can provide a holistic picture of the current…
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 login-securite/lsassy
Extract credentials from lsass remotely
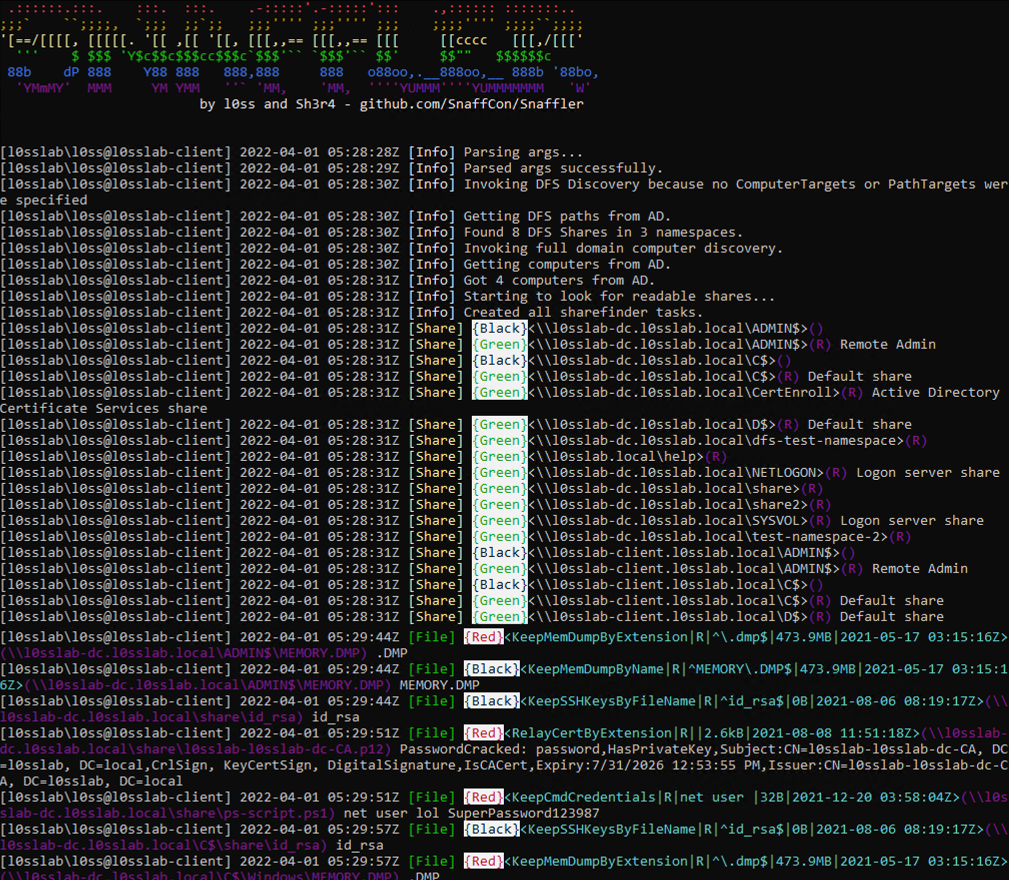 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 specterops/nemesis
Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…