

Awesome-Red-Teaming
 yeyintminthuhtut/awesome-red-teaming
List of Awesome Red Teaming Resources
curated-resourceseducationexploitation+4
8.1k
yeyintminthuhtut/awesome-red-teamingList of Awesome Red Teaming Resources
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
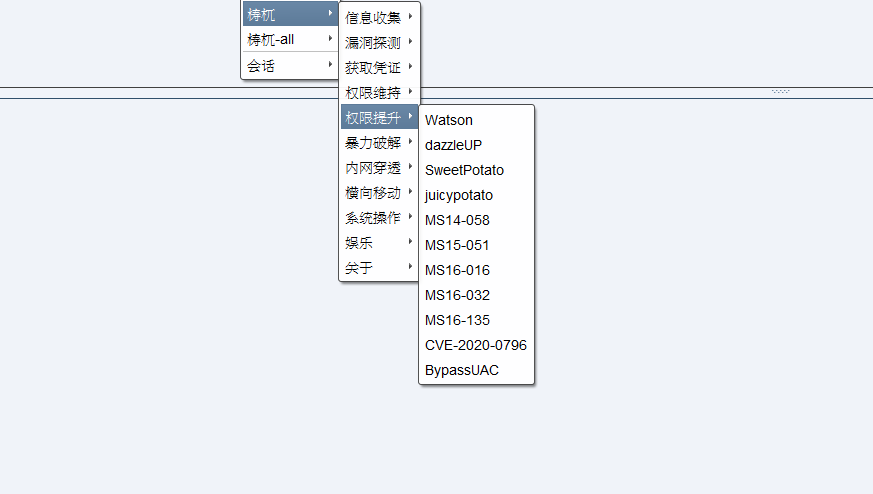 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
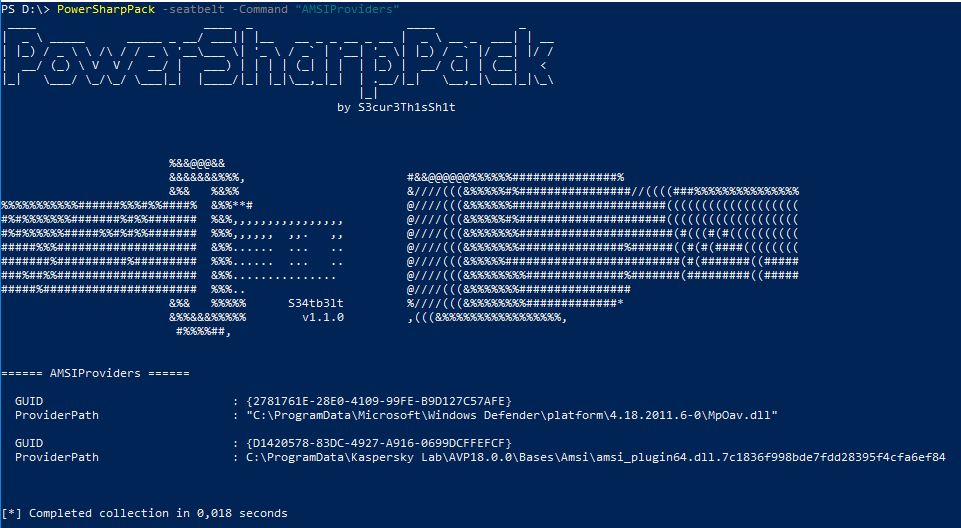 s3cur3th1ssh1t/powersharppack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
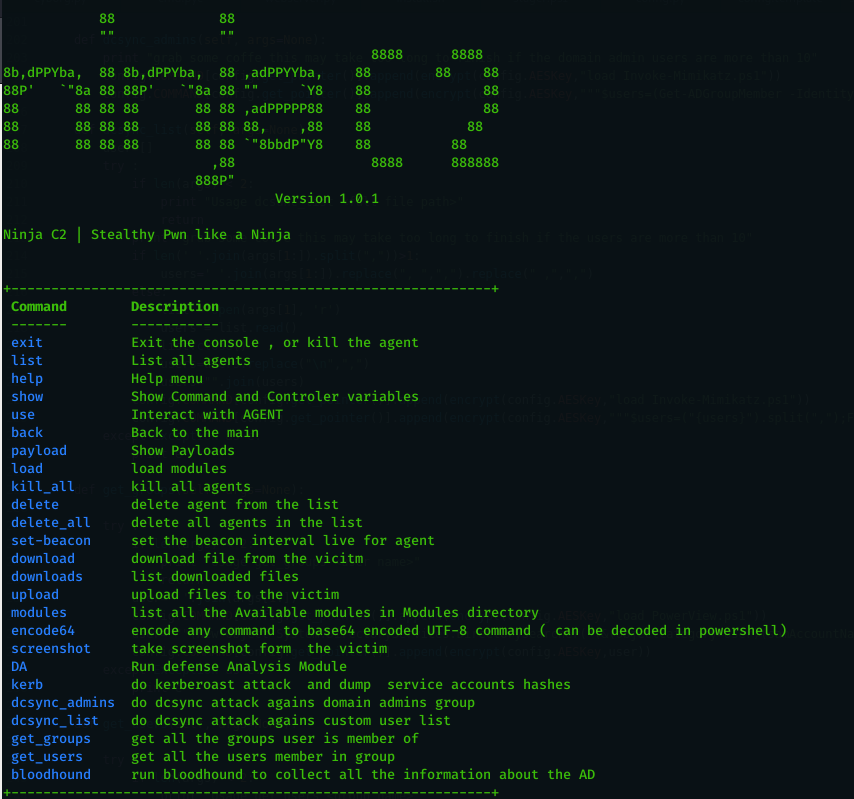 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
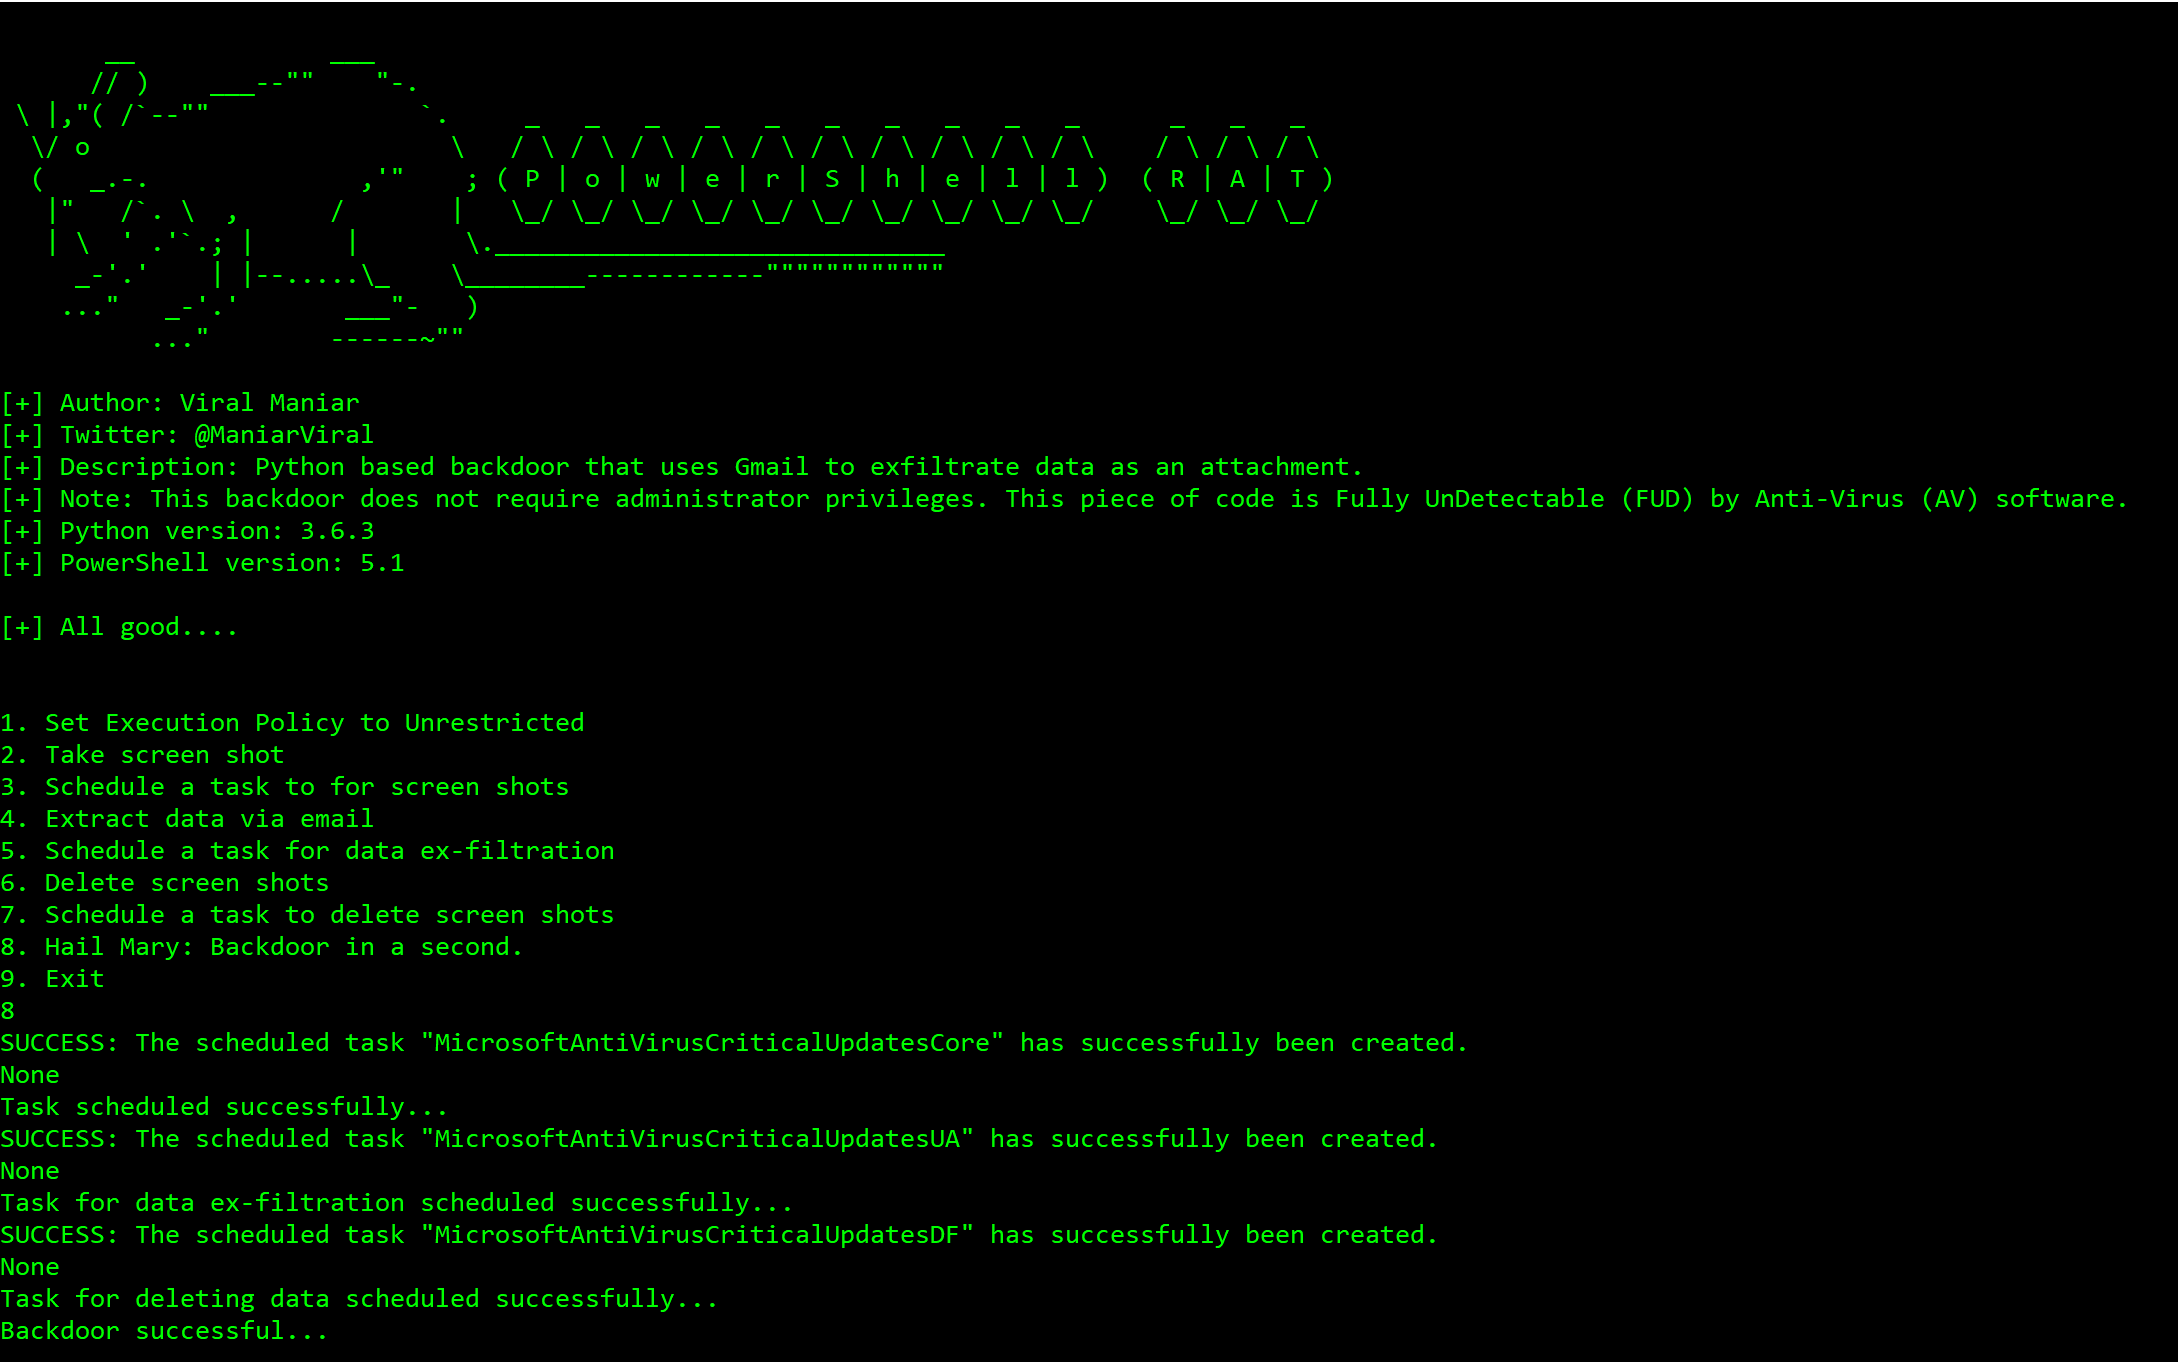 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
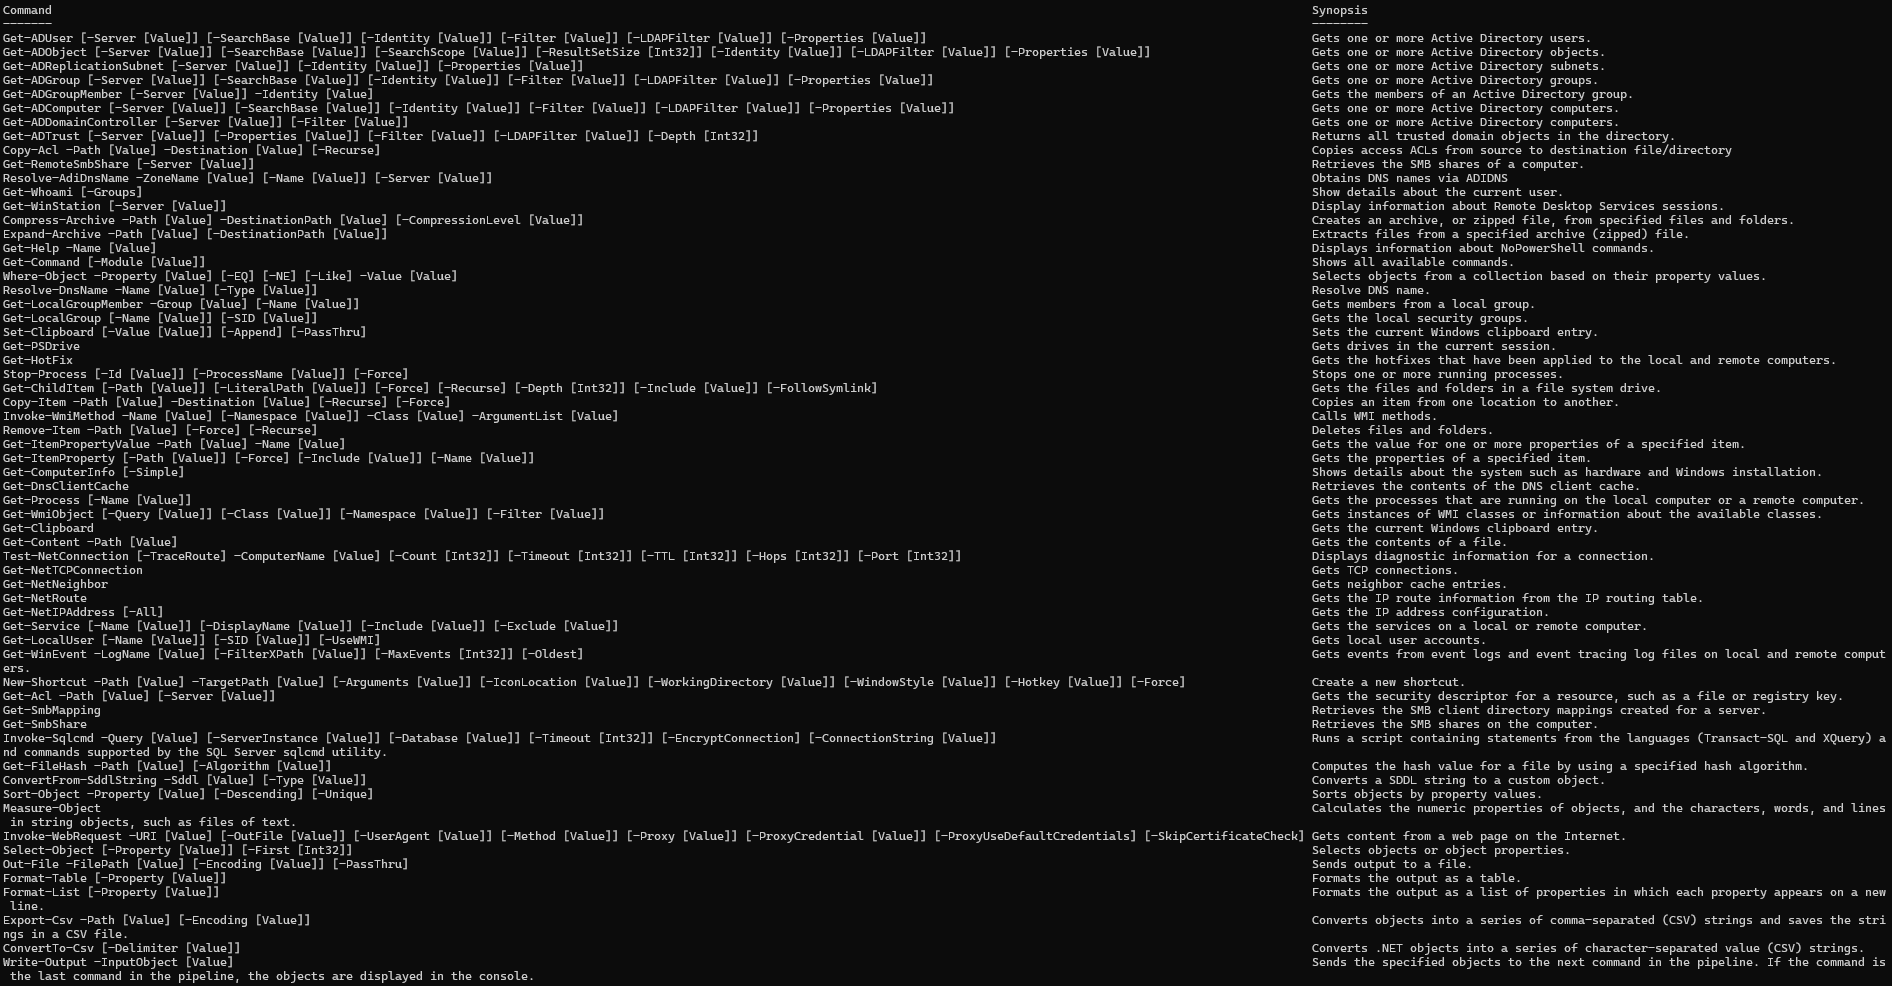 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 securethelogs/redrabbit
Red Team PowerShell Script
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
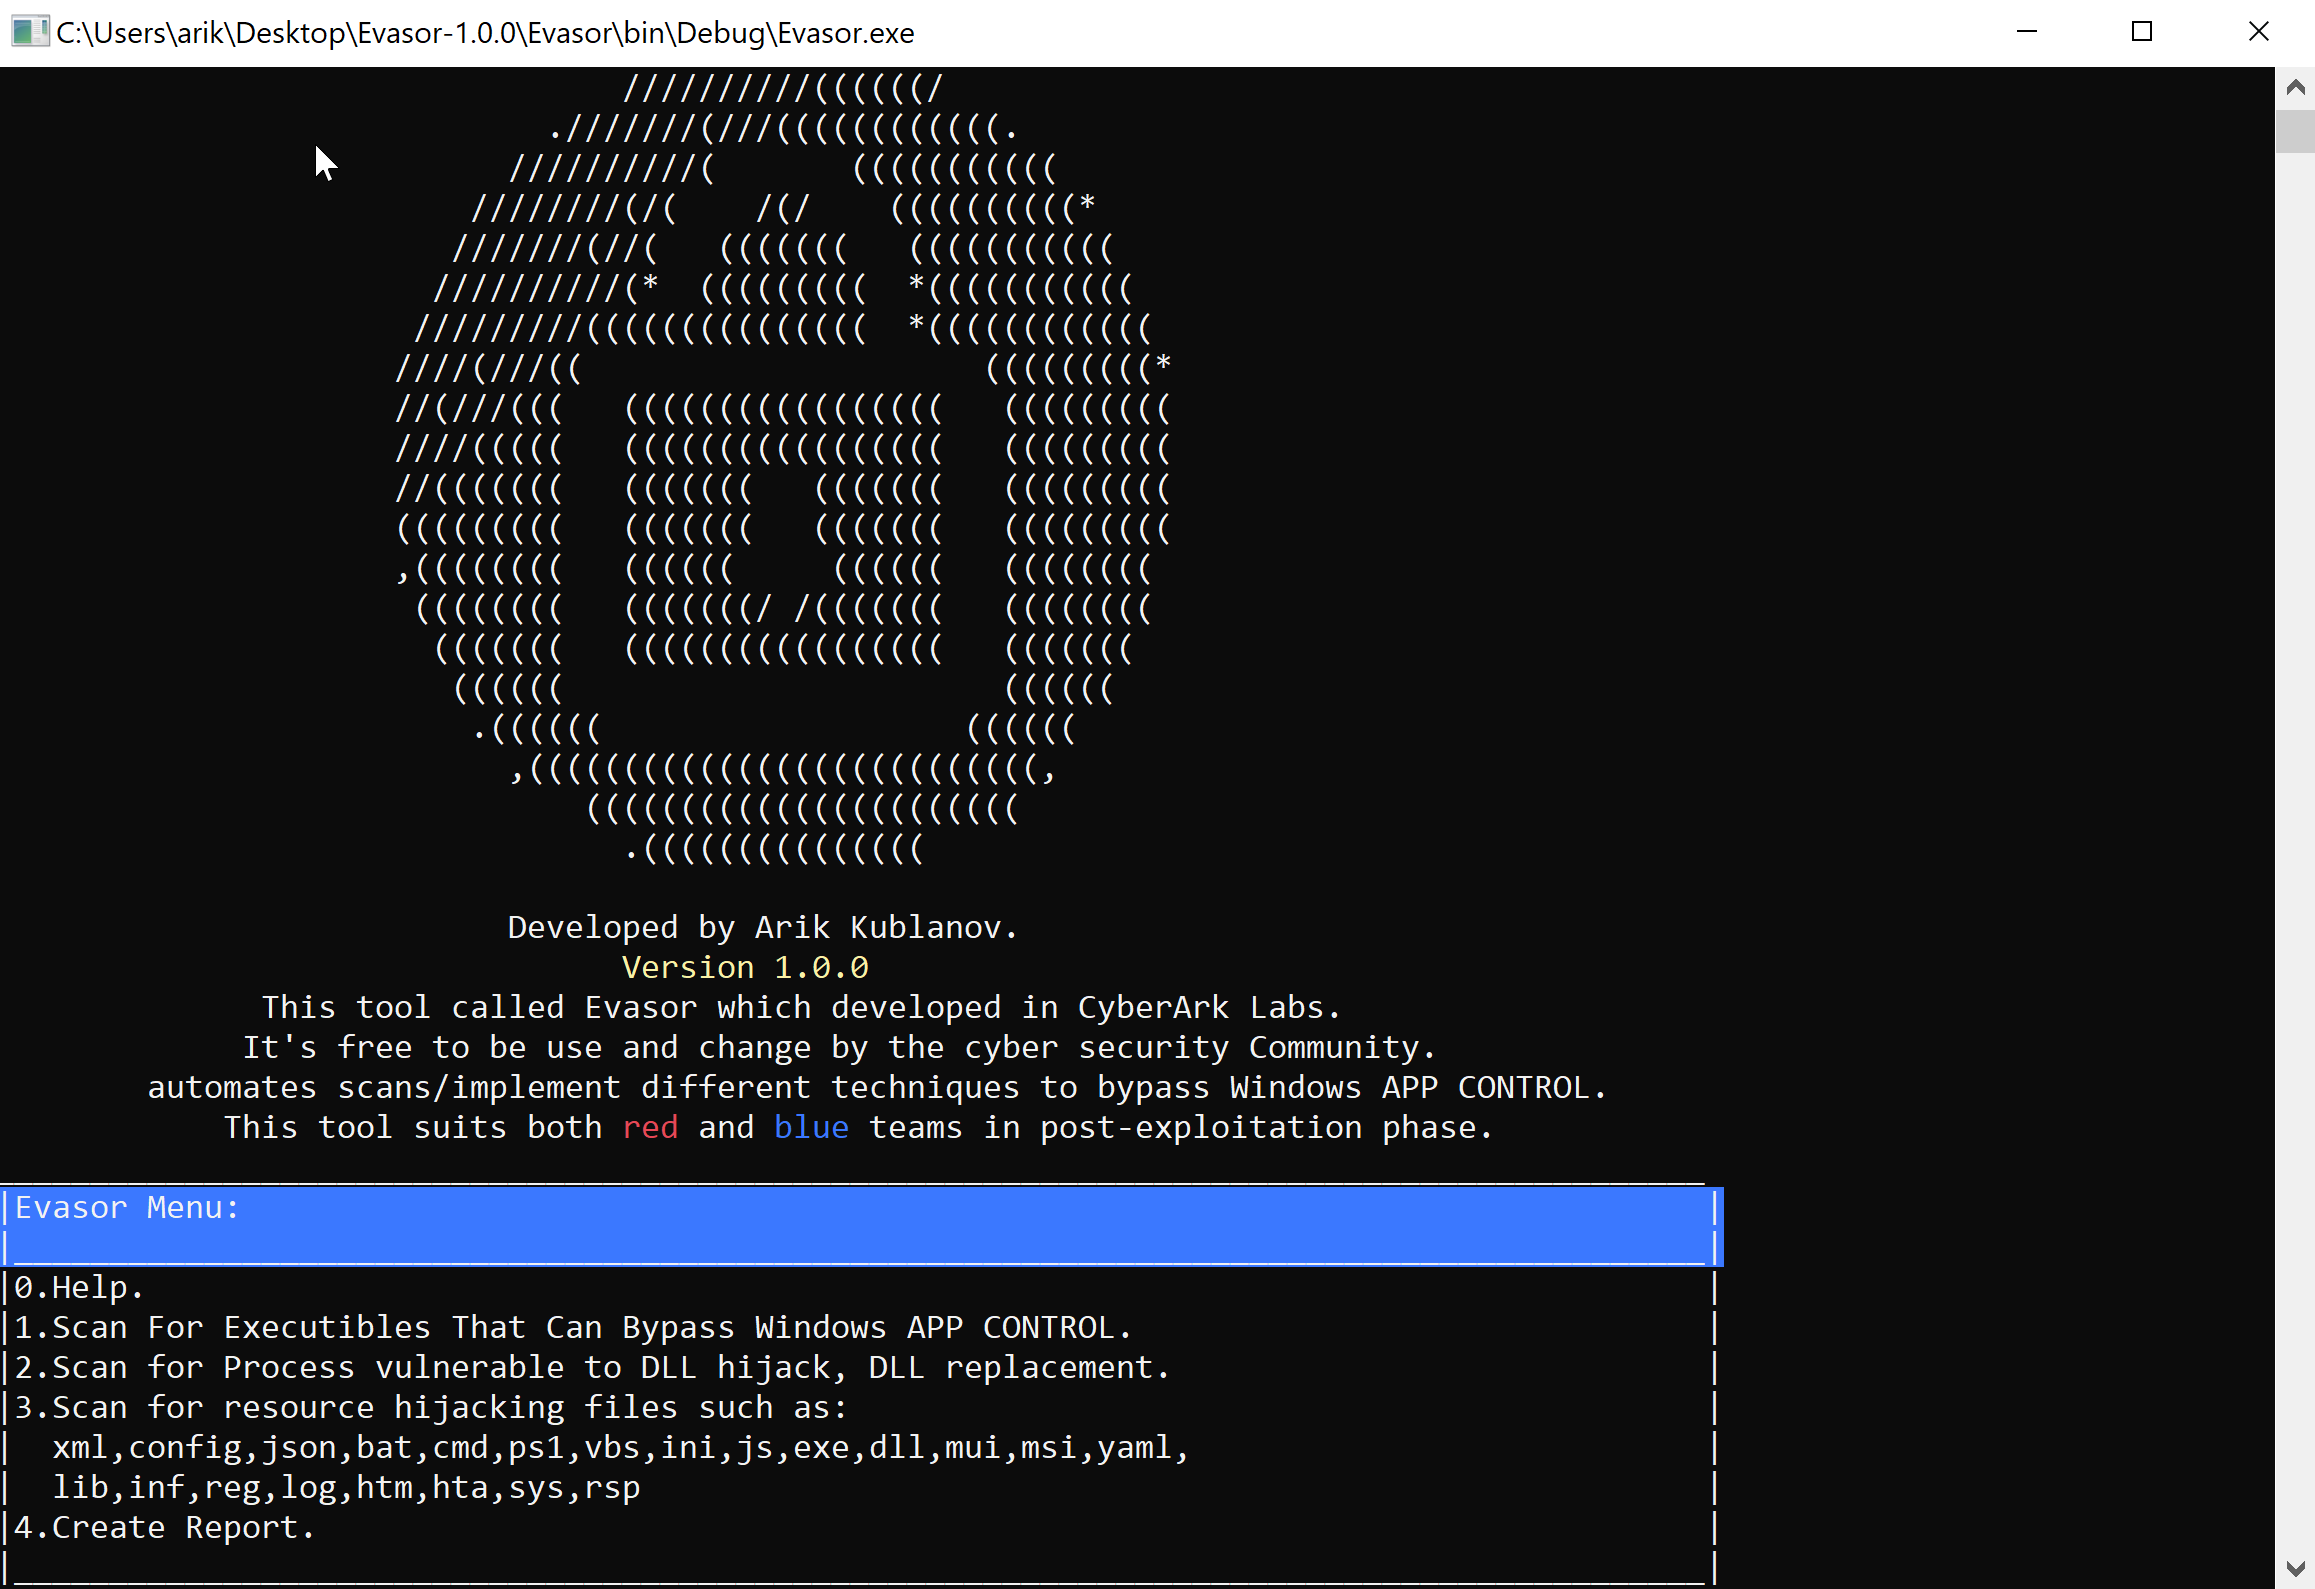 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies