
cve-2023-41993-test
 hrtowii/cve-2023-41993-test
Proof-of-concept exploit for CVE-2023-41993, demonstrating a WebKit vulnerability with post-exploitation techniques and binary exploitation…
binary-exploitationeducationexploitation+3
16
hrtowii/cve-2023-41993-testProof-of-concept exploit for CVE-2023-41993, demonstrating a WebKit vulnerability with post-exploitation techniques and binary exploitation…
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
 gbuyssens/cve-2026-39987
Marimo exploit prior to 0.23.0. Pre-Auth RCE vulnerability via websocket endpoint : /terminal/ws.
 graypixel2121/cve-2025-57489
Technical analysis and proof-of-concept exploit for CVE-2025-57489, a privilege escalation vulnerability in SuperDuper! v3.10 via improper setuid…
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 ant1sec-ops/cve-2023-39593
Database authenticated code execution
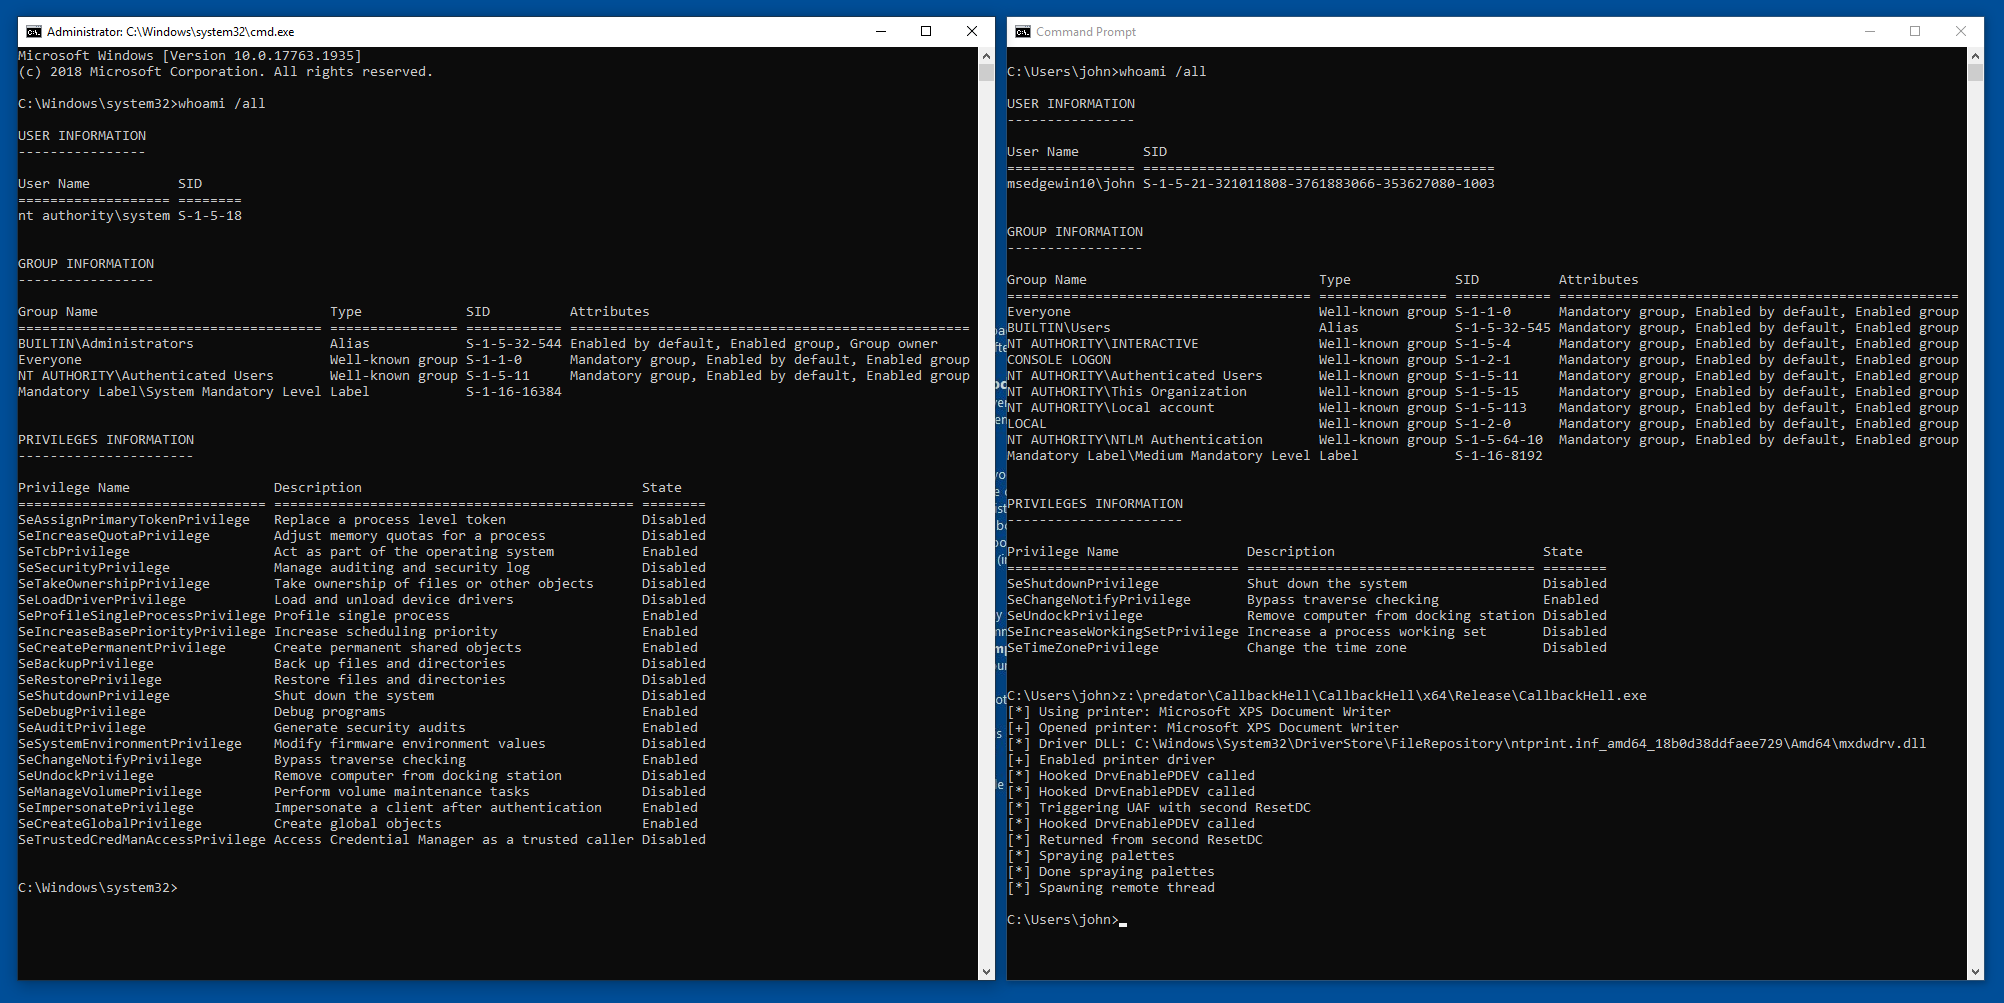 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 janod313/-cve-2019-14287-sudo-bypass-vulnerability
Exploit for CVE-2019-14287, a sudo privilege escalation vulnerability allowing command execution as root via crafted RunAs user specifications.
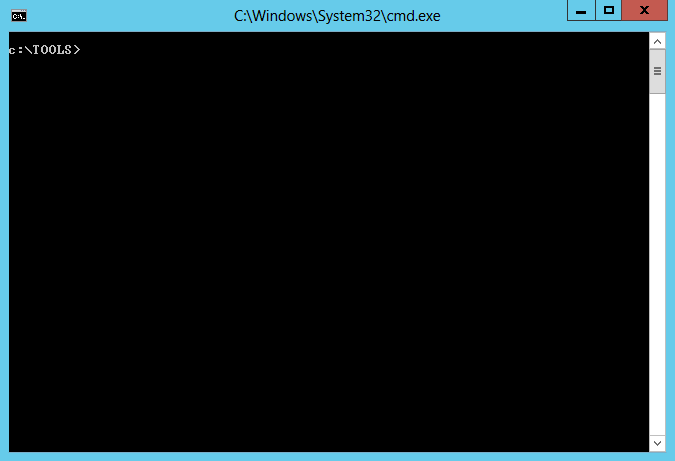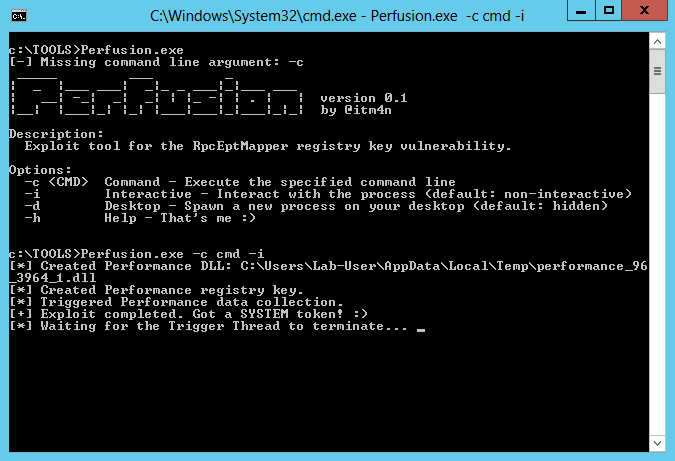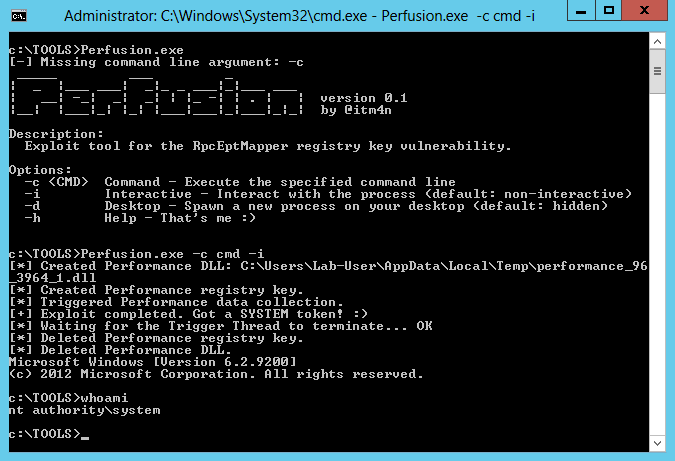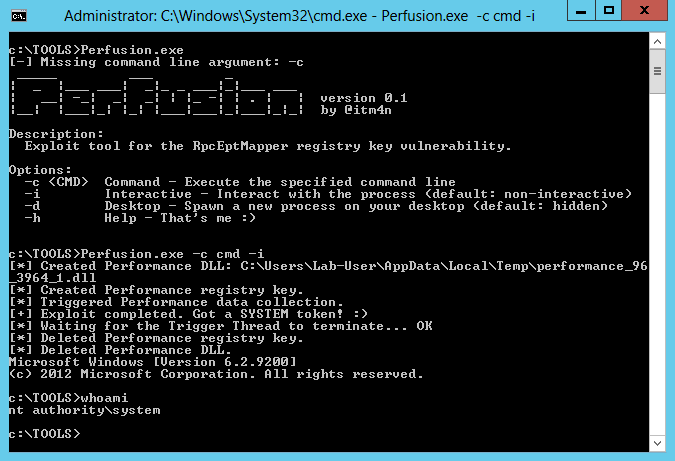 itm4n/perfusion
Exploit for the RpcEptMapper registry key permissions vulnerability (Windows 7 / 2088R2 / 8 / 2012)
 clarissss/osticketfilereadintorce
Full-chain exploit combining PHP filter chain injection with CVE-2024-2961 (CNEXT) for unauthenticated Remote Code Execution on vulnerable osTicket…
 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…
 danil-koltsov/below-log-race-poc
PoC for CVE-2025-27591 – Local privilege escalation in the below monitoring tool. By symlinking its log file to /etc/passwd, an attacker can inject a…
 malwarekid/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel AF_ALG memory corruption vulnerability. Uses splice to patch /usr/bin/su in page cache,…
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 0x0d1n/cve-2021-36934
Exploit PoC for CVE-2021-36934, a Windows local privilege escalation vulnerability, demonstrating access to SAM/SECURITY/SYSTEM hives and local…
 tc4dy/cve-2026-41940-poc-exploit
PoC exploit for CVE-2026-41940 targeting cPanel/WHM authentication bypass via CRLF injection. Supports session hijacking, RCE, reverse shell, mass…
 j4ck3lsyn-gen2/cve-2026-39047
Epson Printer RAW Protocol Exploit Framework
 dollarboysushil/linux-privilege-escalation-cve-2025-27591
CVE-2025-27591 is a known privilege escalation vulnerability in the Below service (version < v0.9.0)