
PiX-C2
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
command-and-controlnetwork-securitypacket-sniffing-analysis+3
robertdavis1/pix-c2Ping Exfiltration Command and Control (PiX-C2)
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
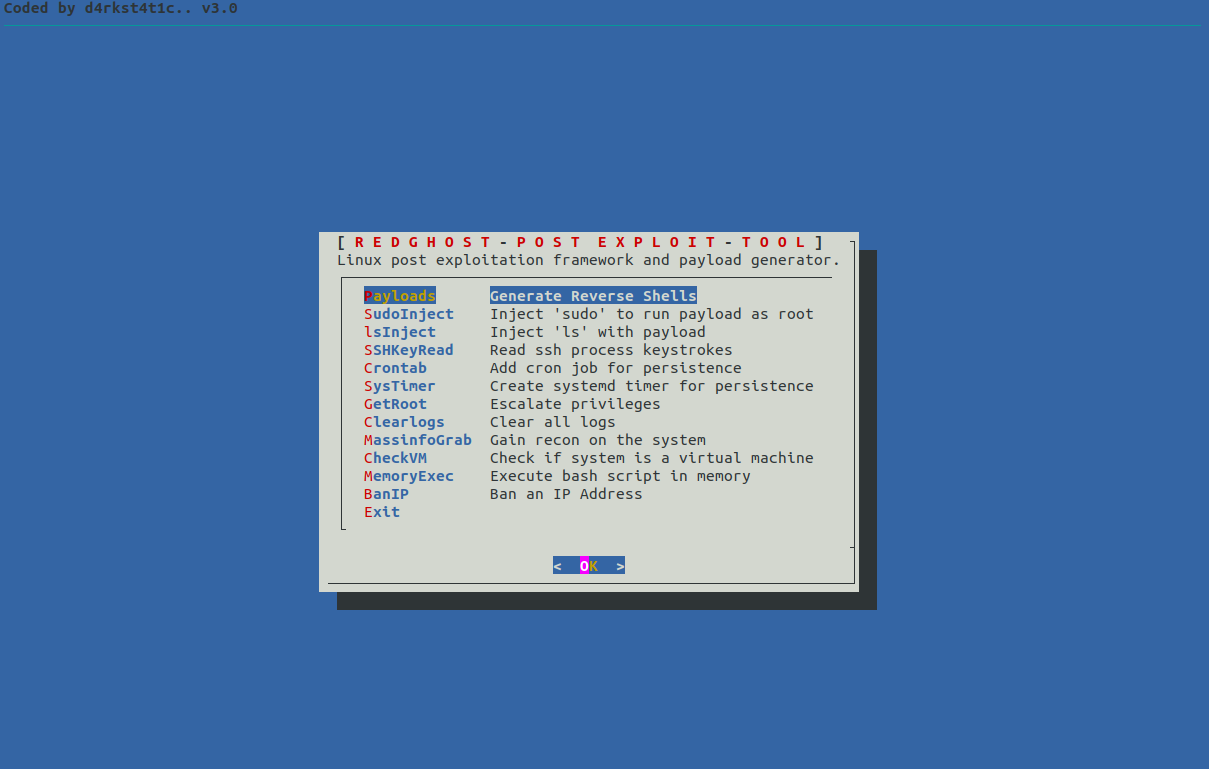 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 nccgroup/keimpx
Check for valid credentials across a network over SMB
 sensepost/impersonate
A windows token impersonation tool
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
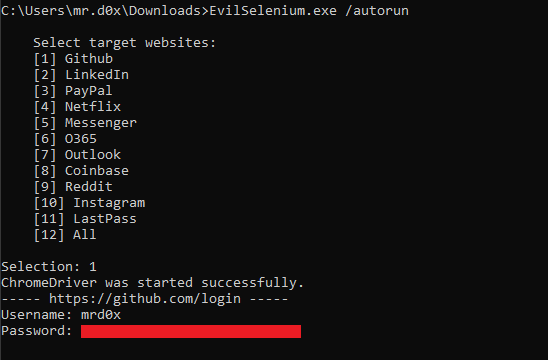 mrd0x/evilselenium
Weaponizes Selenium to automate credential theft, cookie dumping, email exfiltration, and file extraction from Chromium browsers for red team…
 ly1g3/cisco-cve-2023-20075
Cisco Email Security Appliance: Local Privilege Escalation and Shell Escape
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
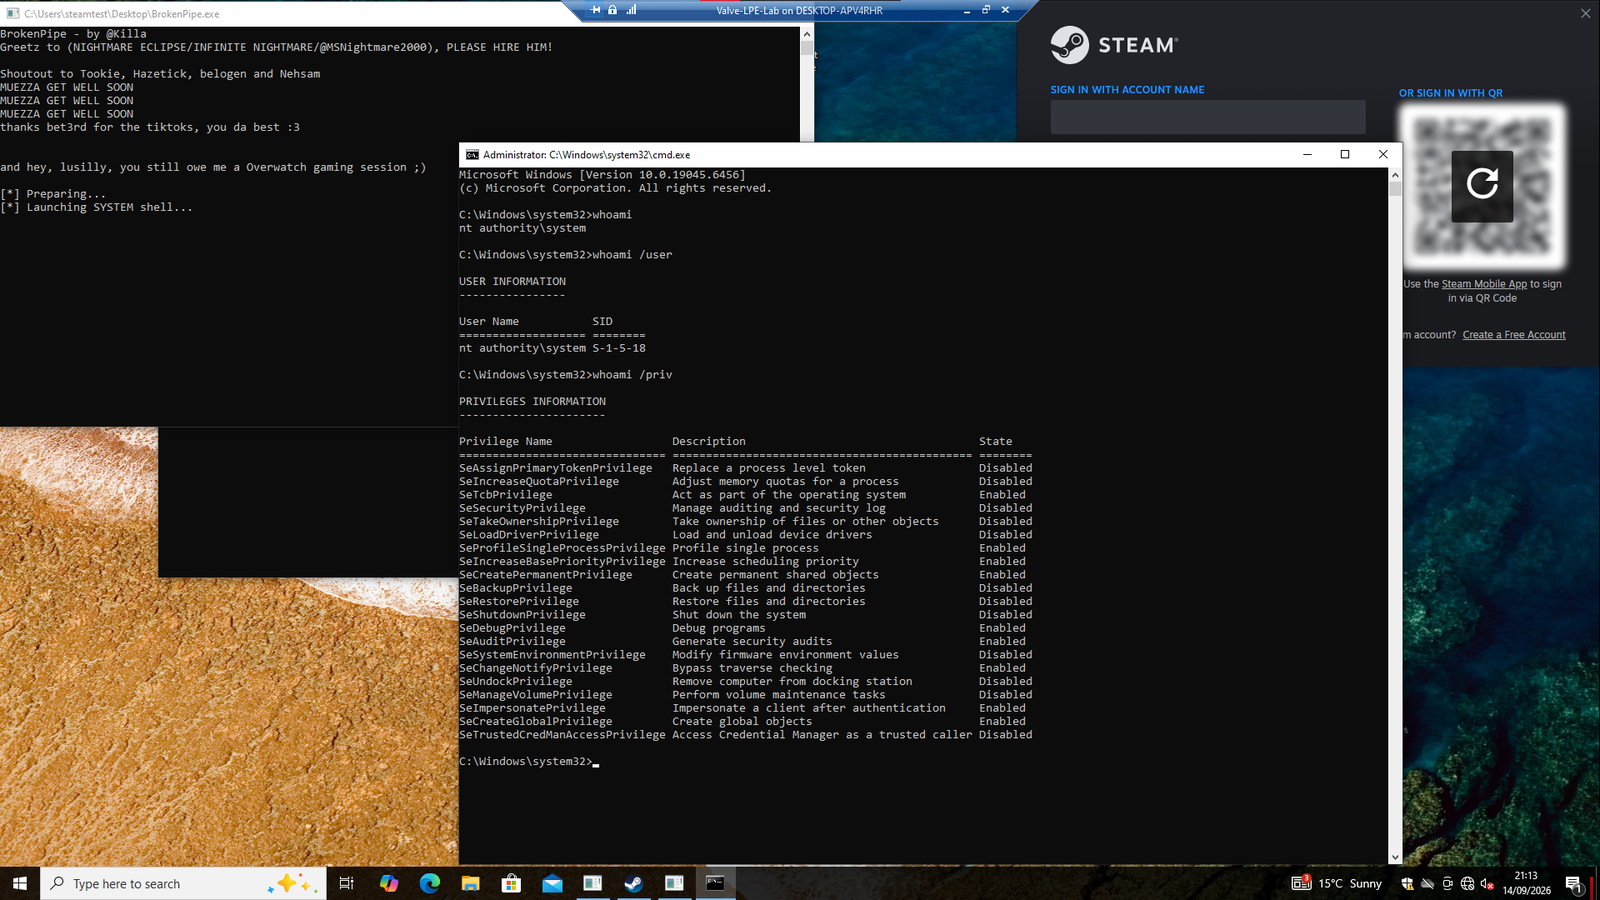 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 ghostpack/rubeus
Trying to tame the three-headed dog.