
D-RAT_VB.NET_MySQL_PHP
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
command-and-controlpayload-developmentpenetration-testing+3
14
mr-wolf-gb/d-rat_vb.net_mysql_phpD-RAT [VB.NET]+[MySQL]+[PHP]
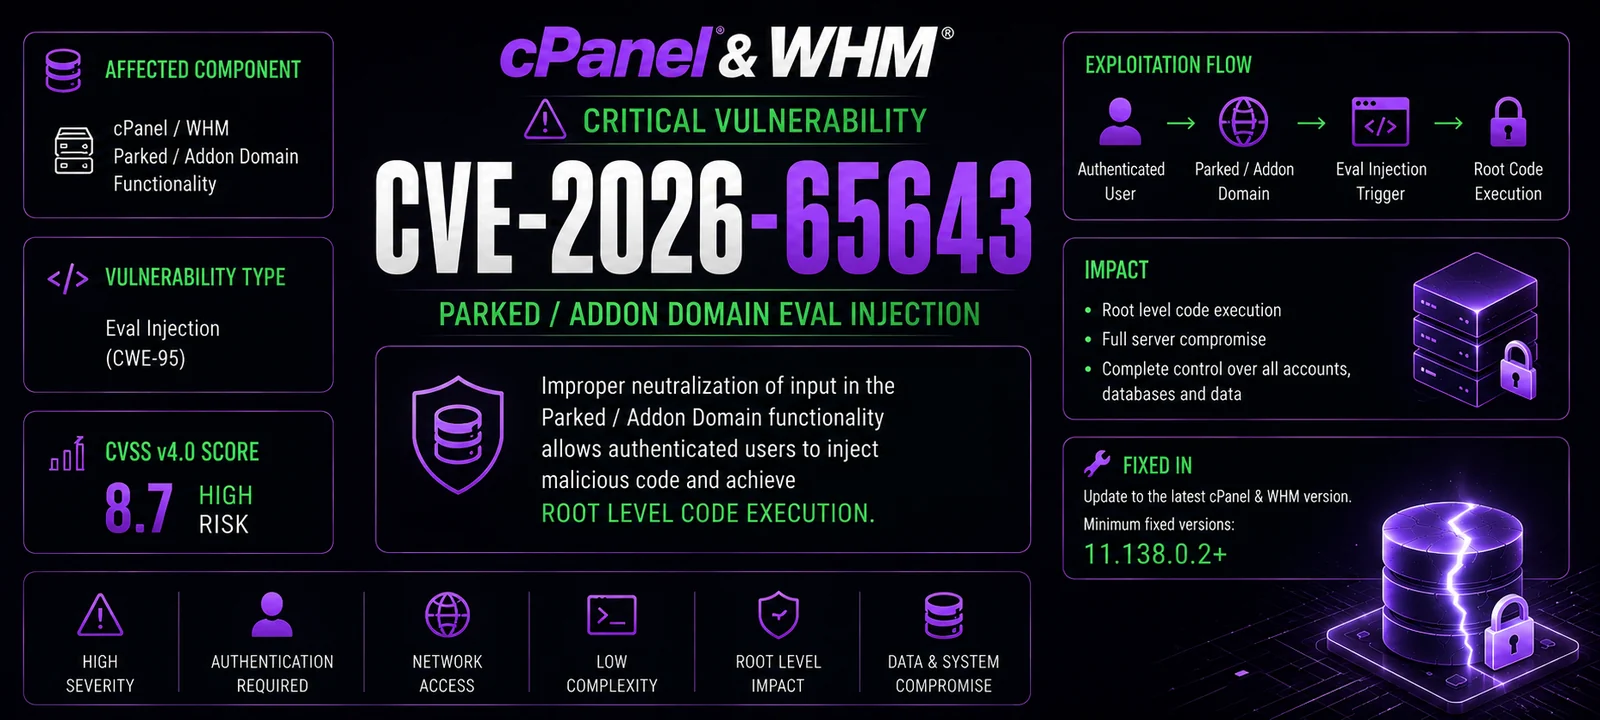 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 paradoxis/cve-2026-57239
Proof of concept exploit for CVE-2026-3775/CVE-2026-3780 and CVE-2026-57239 which lets you obtain NT AUTHORITY\SYSTEM rights via the Foxit PDF Reader…
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
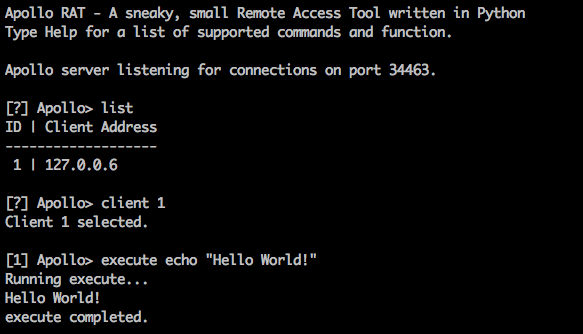 obsida-uk/apollo
A simple, lightweight Remote Access Tool written in Python
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 ycdxsb/cve-2020-0668
Make CVE-2020-0668 exploit work for version < win10 v1903 and version >= win10 v1903
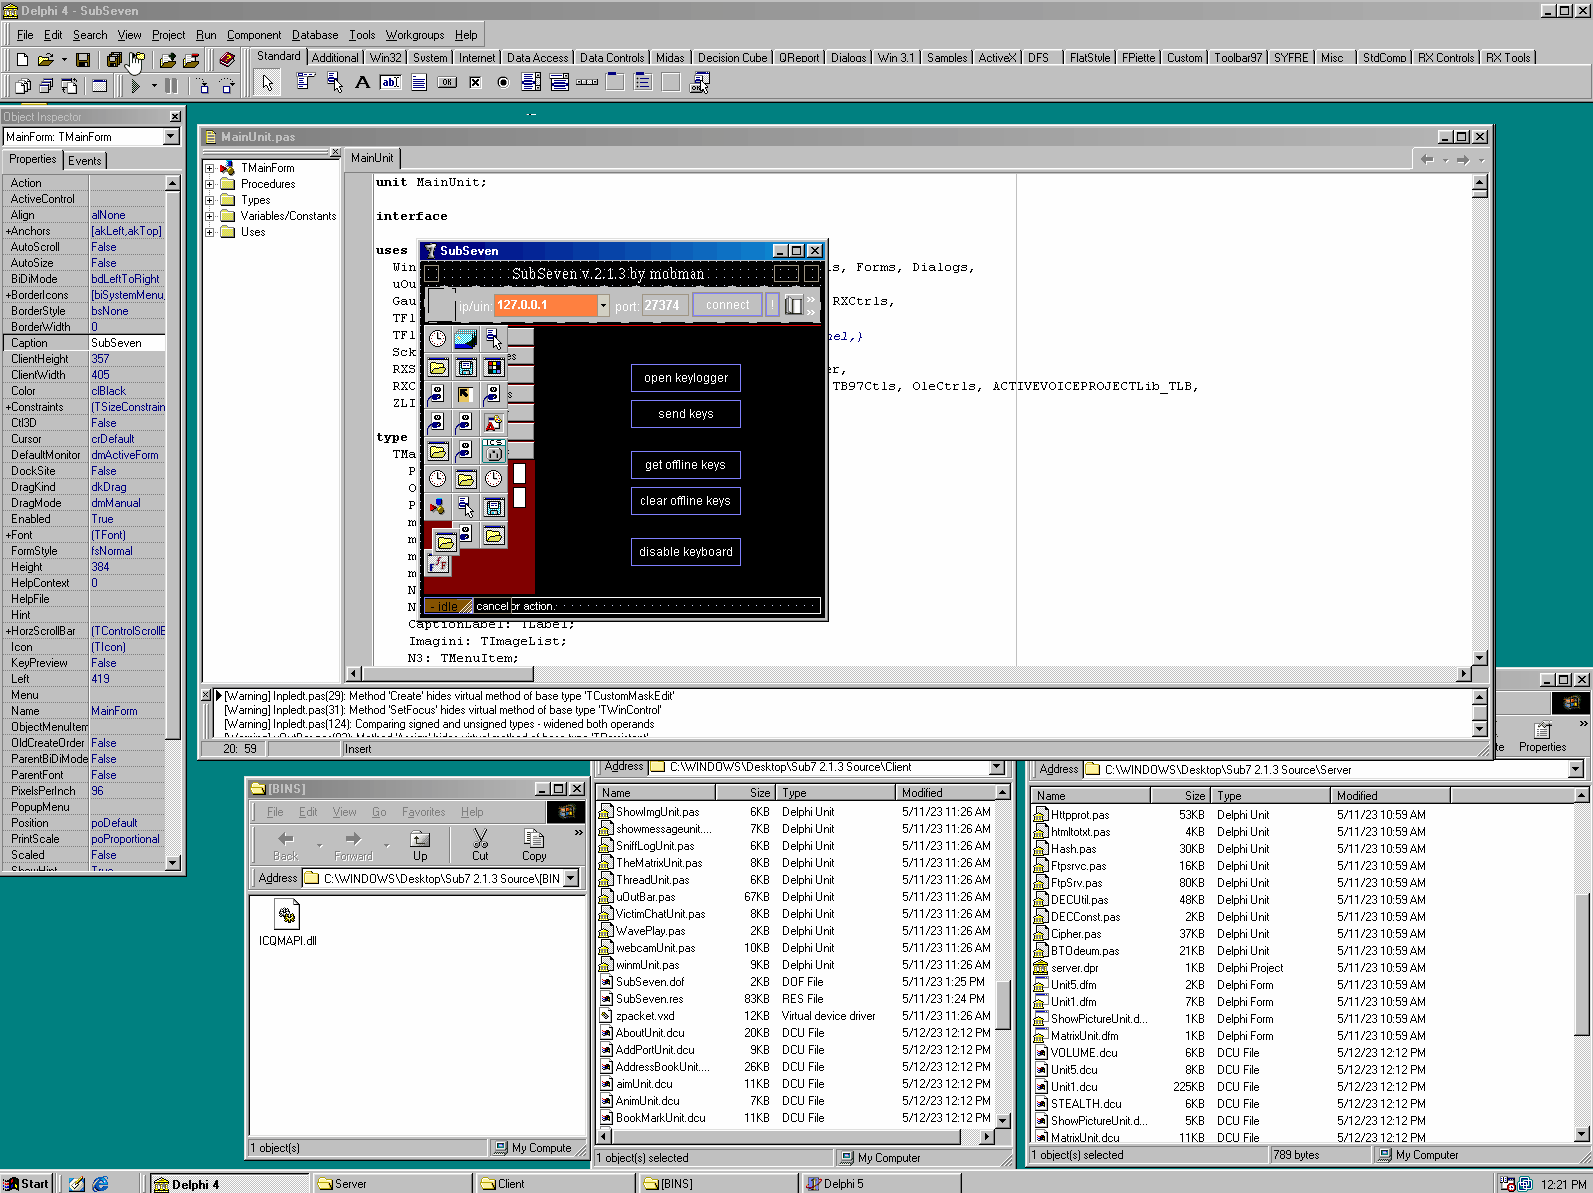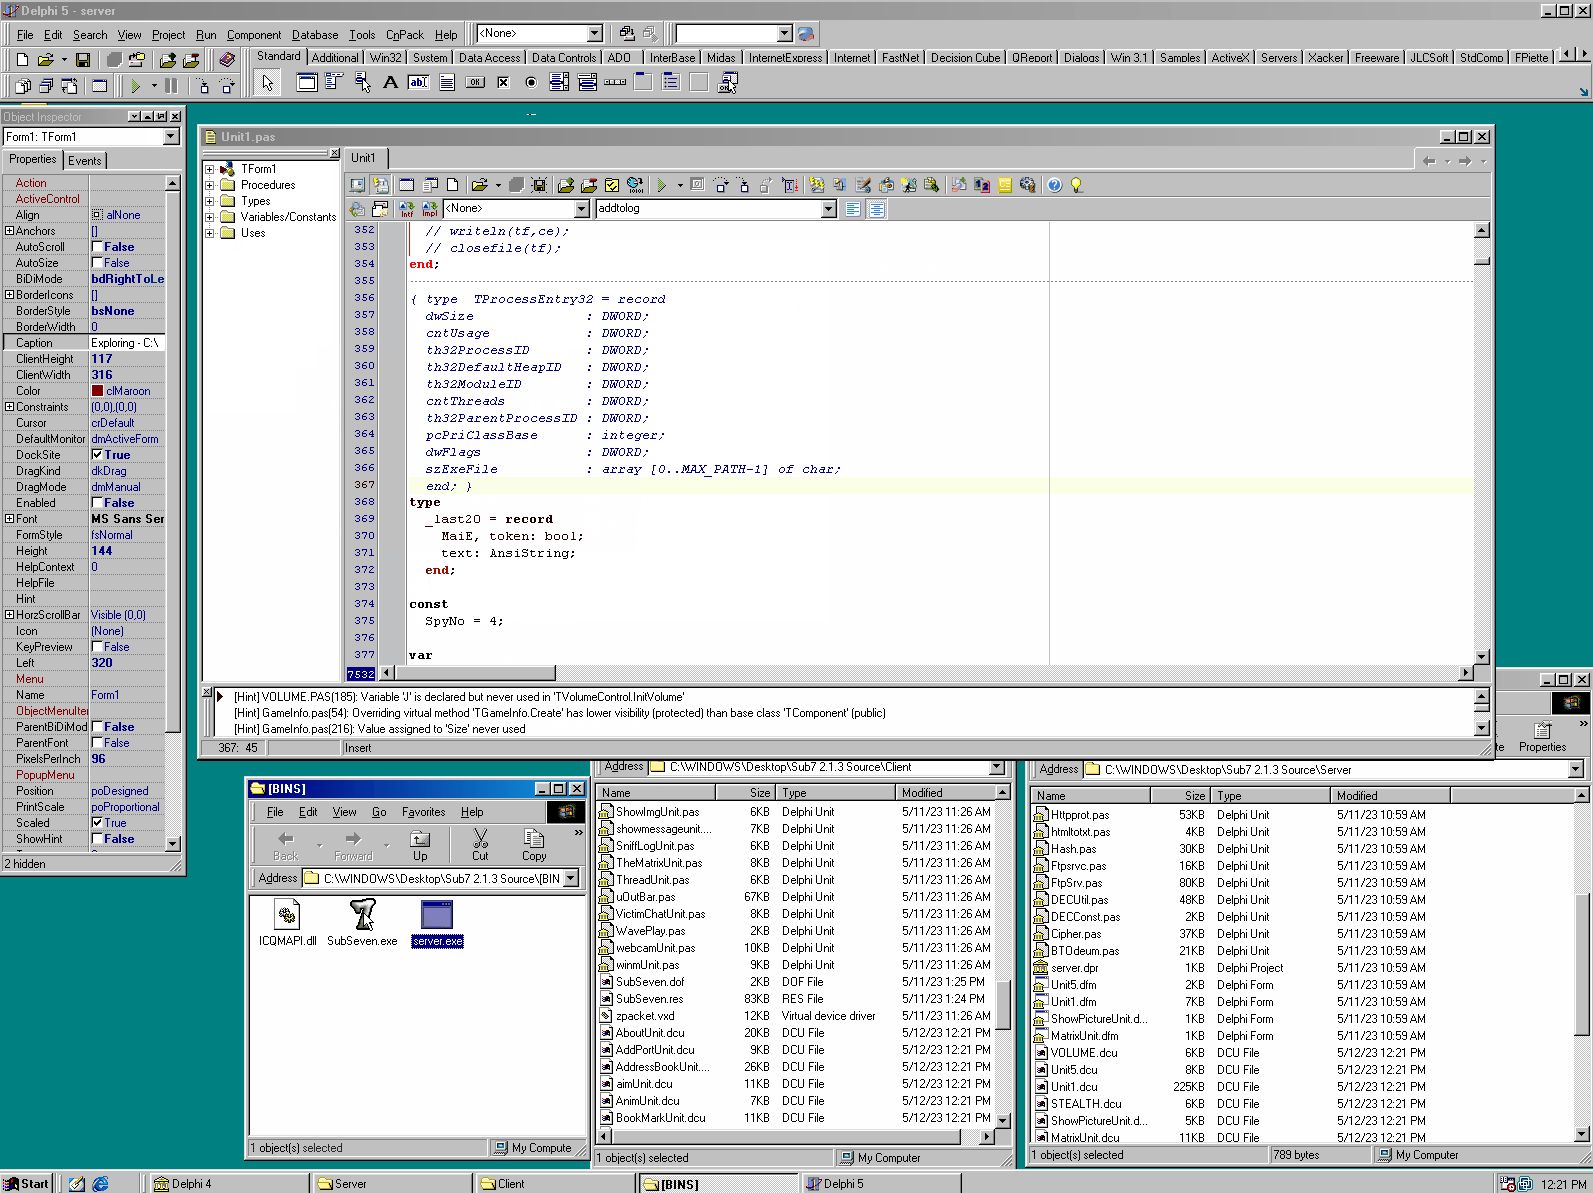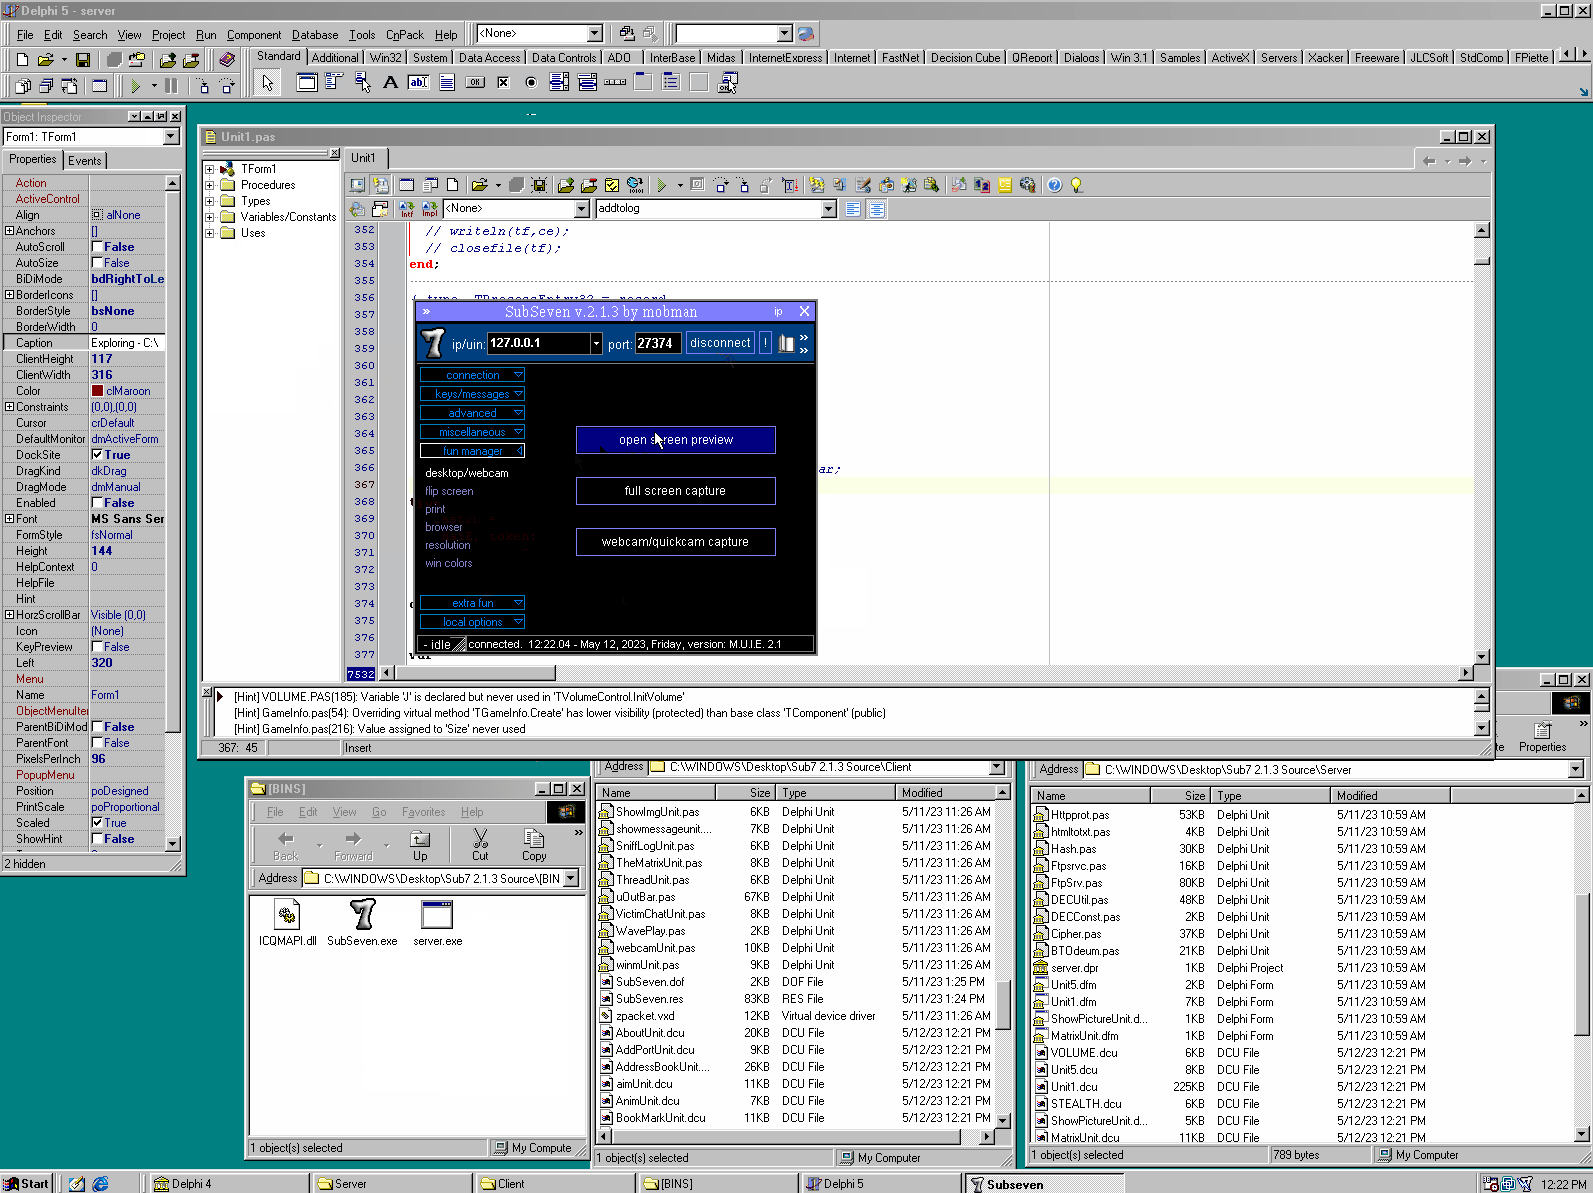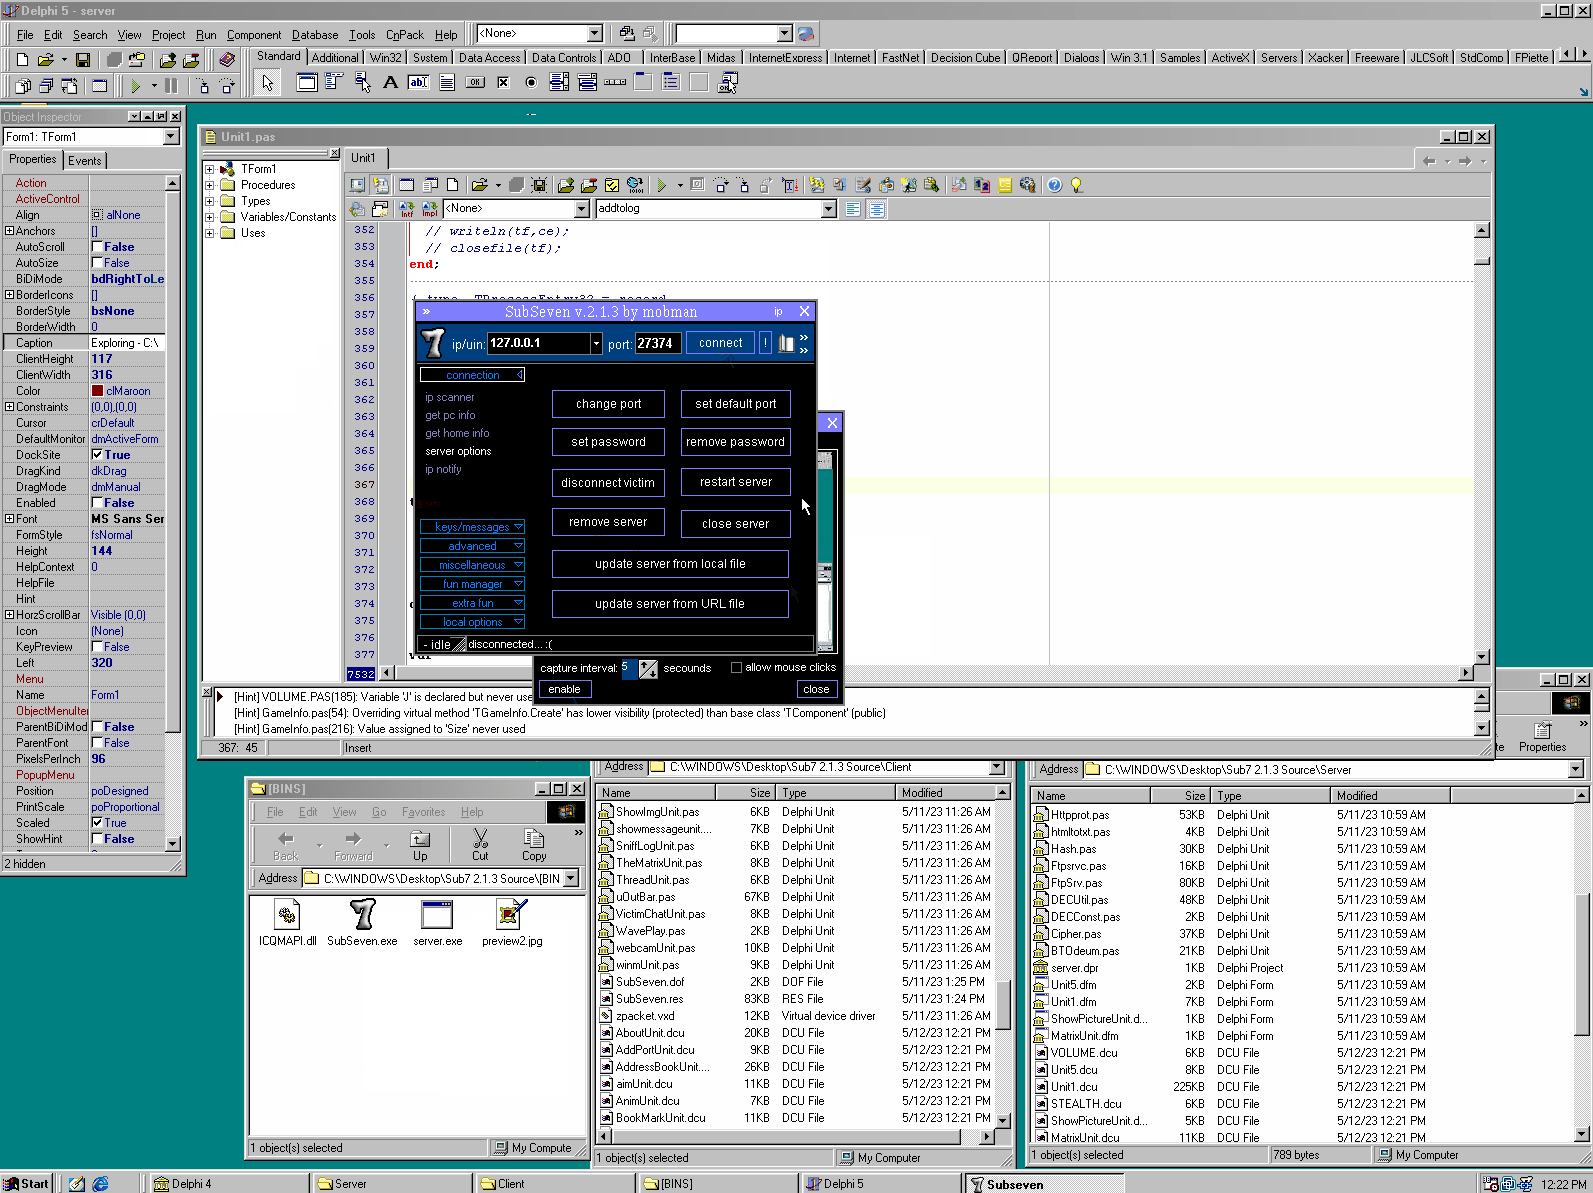
 illwill/sub7
Source code for SubSeven 2.1.3
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 777erp/cve-2026-49176_bof
CVE-2026-49176 WalletService LPE — standalone PoC + Cobalt Strike BOF (SYSTEM command on interactive session)
 richard-tang/sscms-pluginshell
CVE-2022-28118
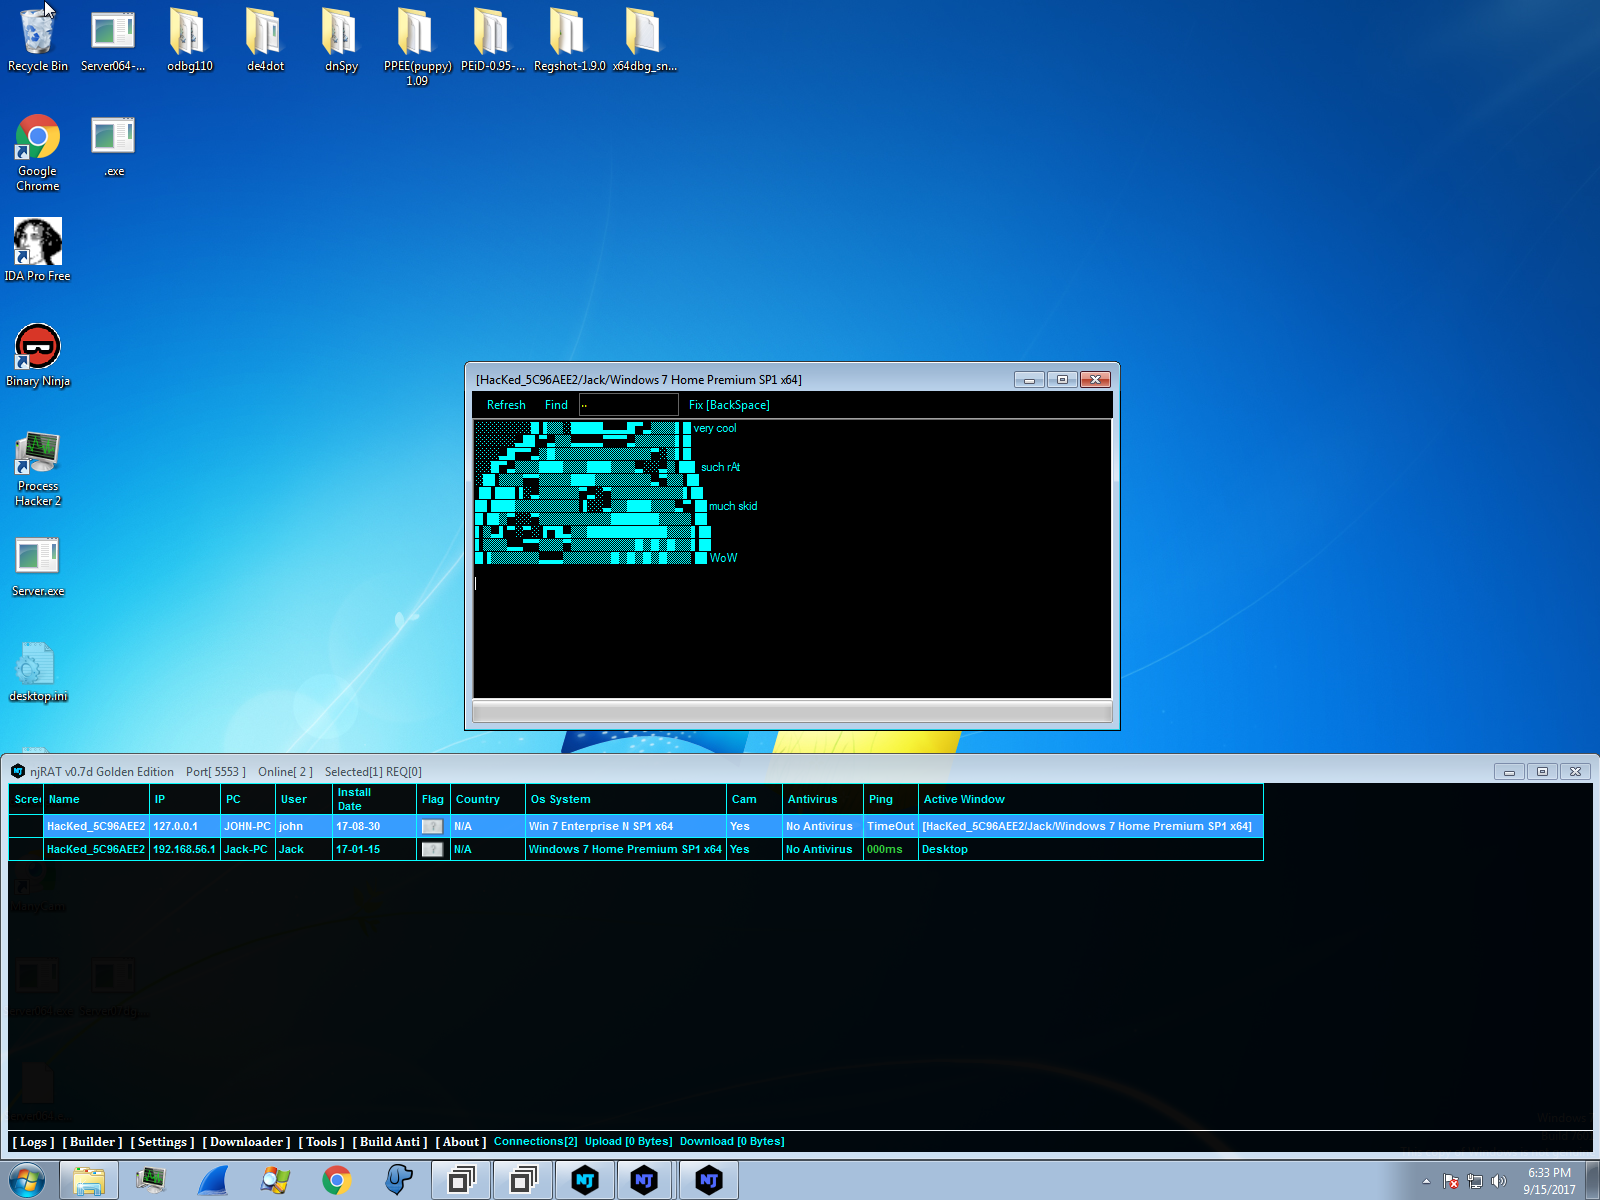 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 al1ex/remotedllinjector
RemoteDLLInjector