
SharpCollection
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
curated-resourcesexploitationlateral-movement+6
2.9k
flangvik/sharpcollectionNightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
 007bsd/ml-kem-key-recovery
Full ML-KEM-1024 key recovery from a partial Fujisaki-Okamoto comparison in wolfSSL (CVE-2026-6330 NEON, CVE-2026-10097 AVX2)
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
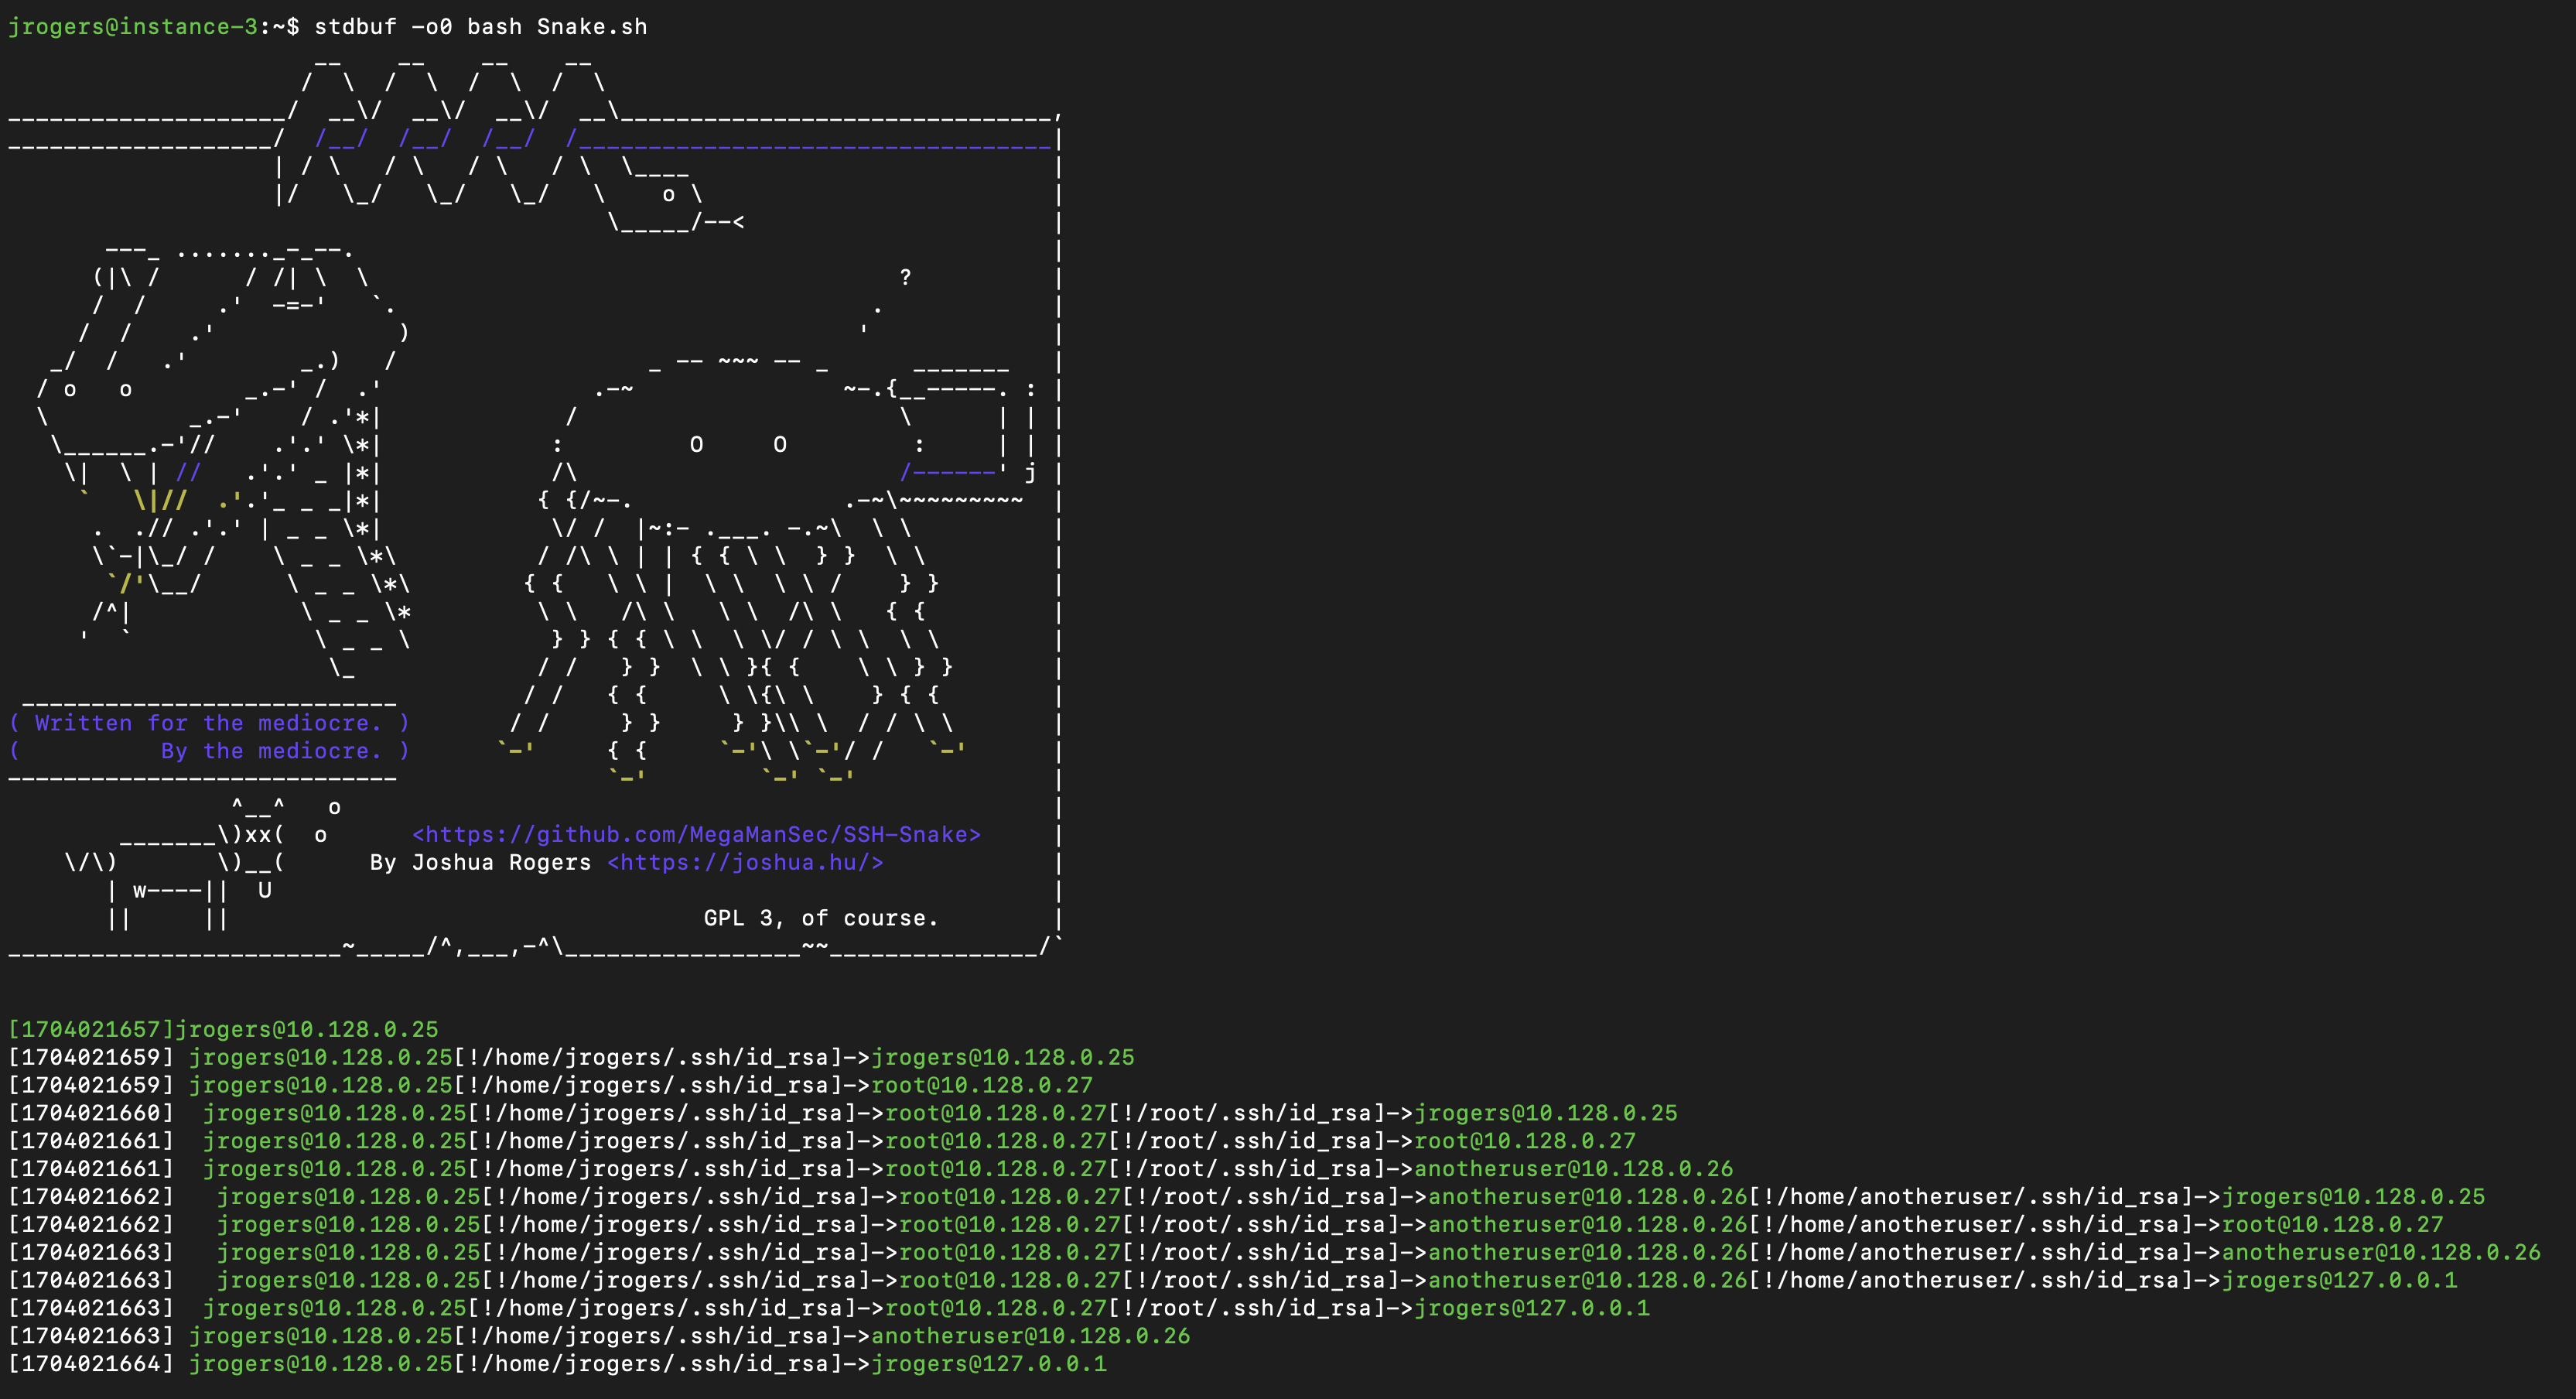 megamansec/ssh-snake
SSH-Snake is a self-propagating, self-replicating, file-less script that automates the post-exploitation task of SSH private key and host discovery.
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 zblurx/dploot
Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
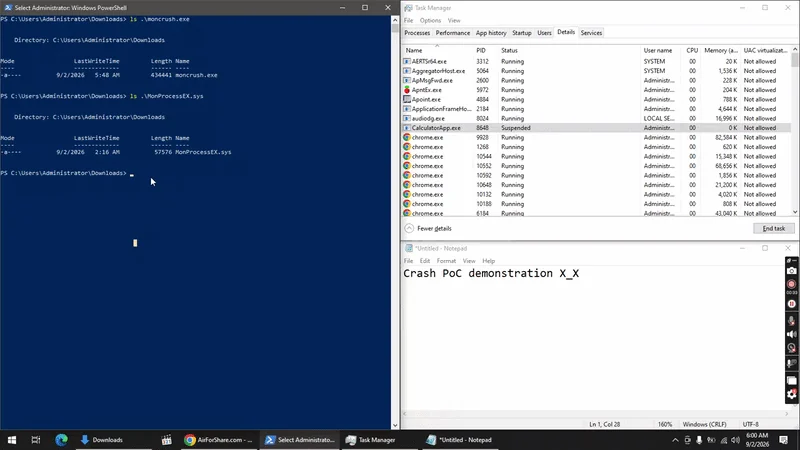 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 deathshotxd/cve-2025-52691-apt-poc
An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…
 bishopfox/sliver
Adversary Emulation Framework
 r0rt1z2/ghostlock
Kernel root exploit (CVE-2026-43499) for some Amazon devices
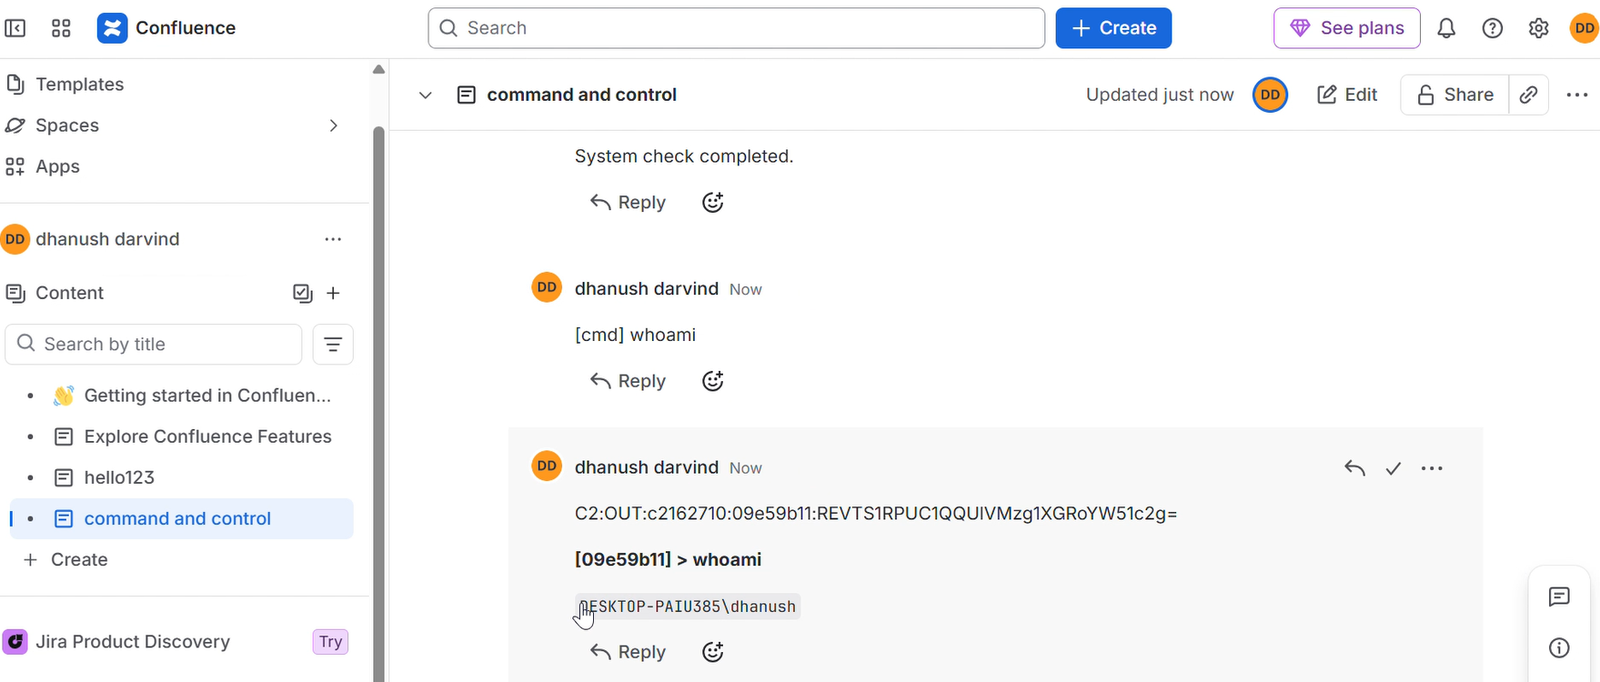 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.