
pentestcode
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
ai-securitycloud-securityctf+9
709
s0ld13rr/pentestcodeAutonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 portbuster1337/lpe-toolkit
Multi-architecture Linux privilege escalation toolkit with 24 pre-built and runtime-compilable exploits. Auto-detects kernel version, filters patched…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
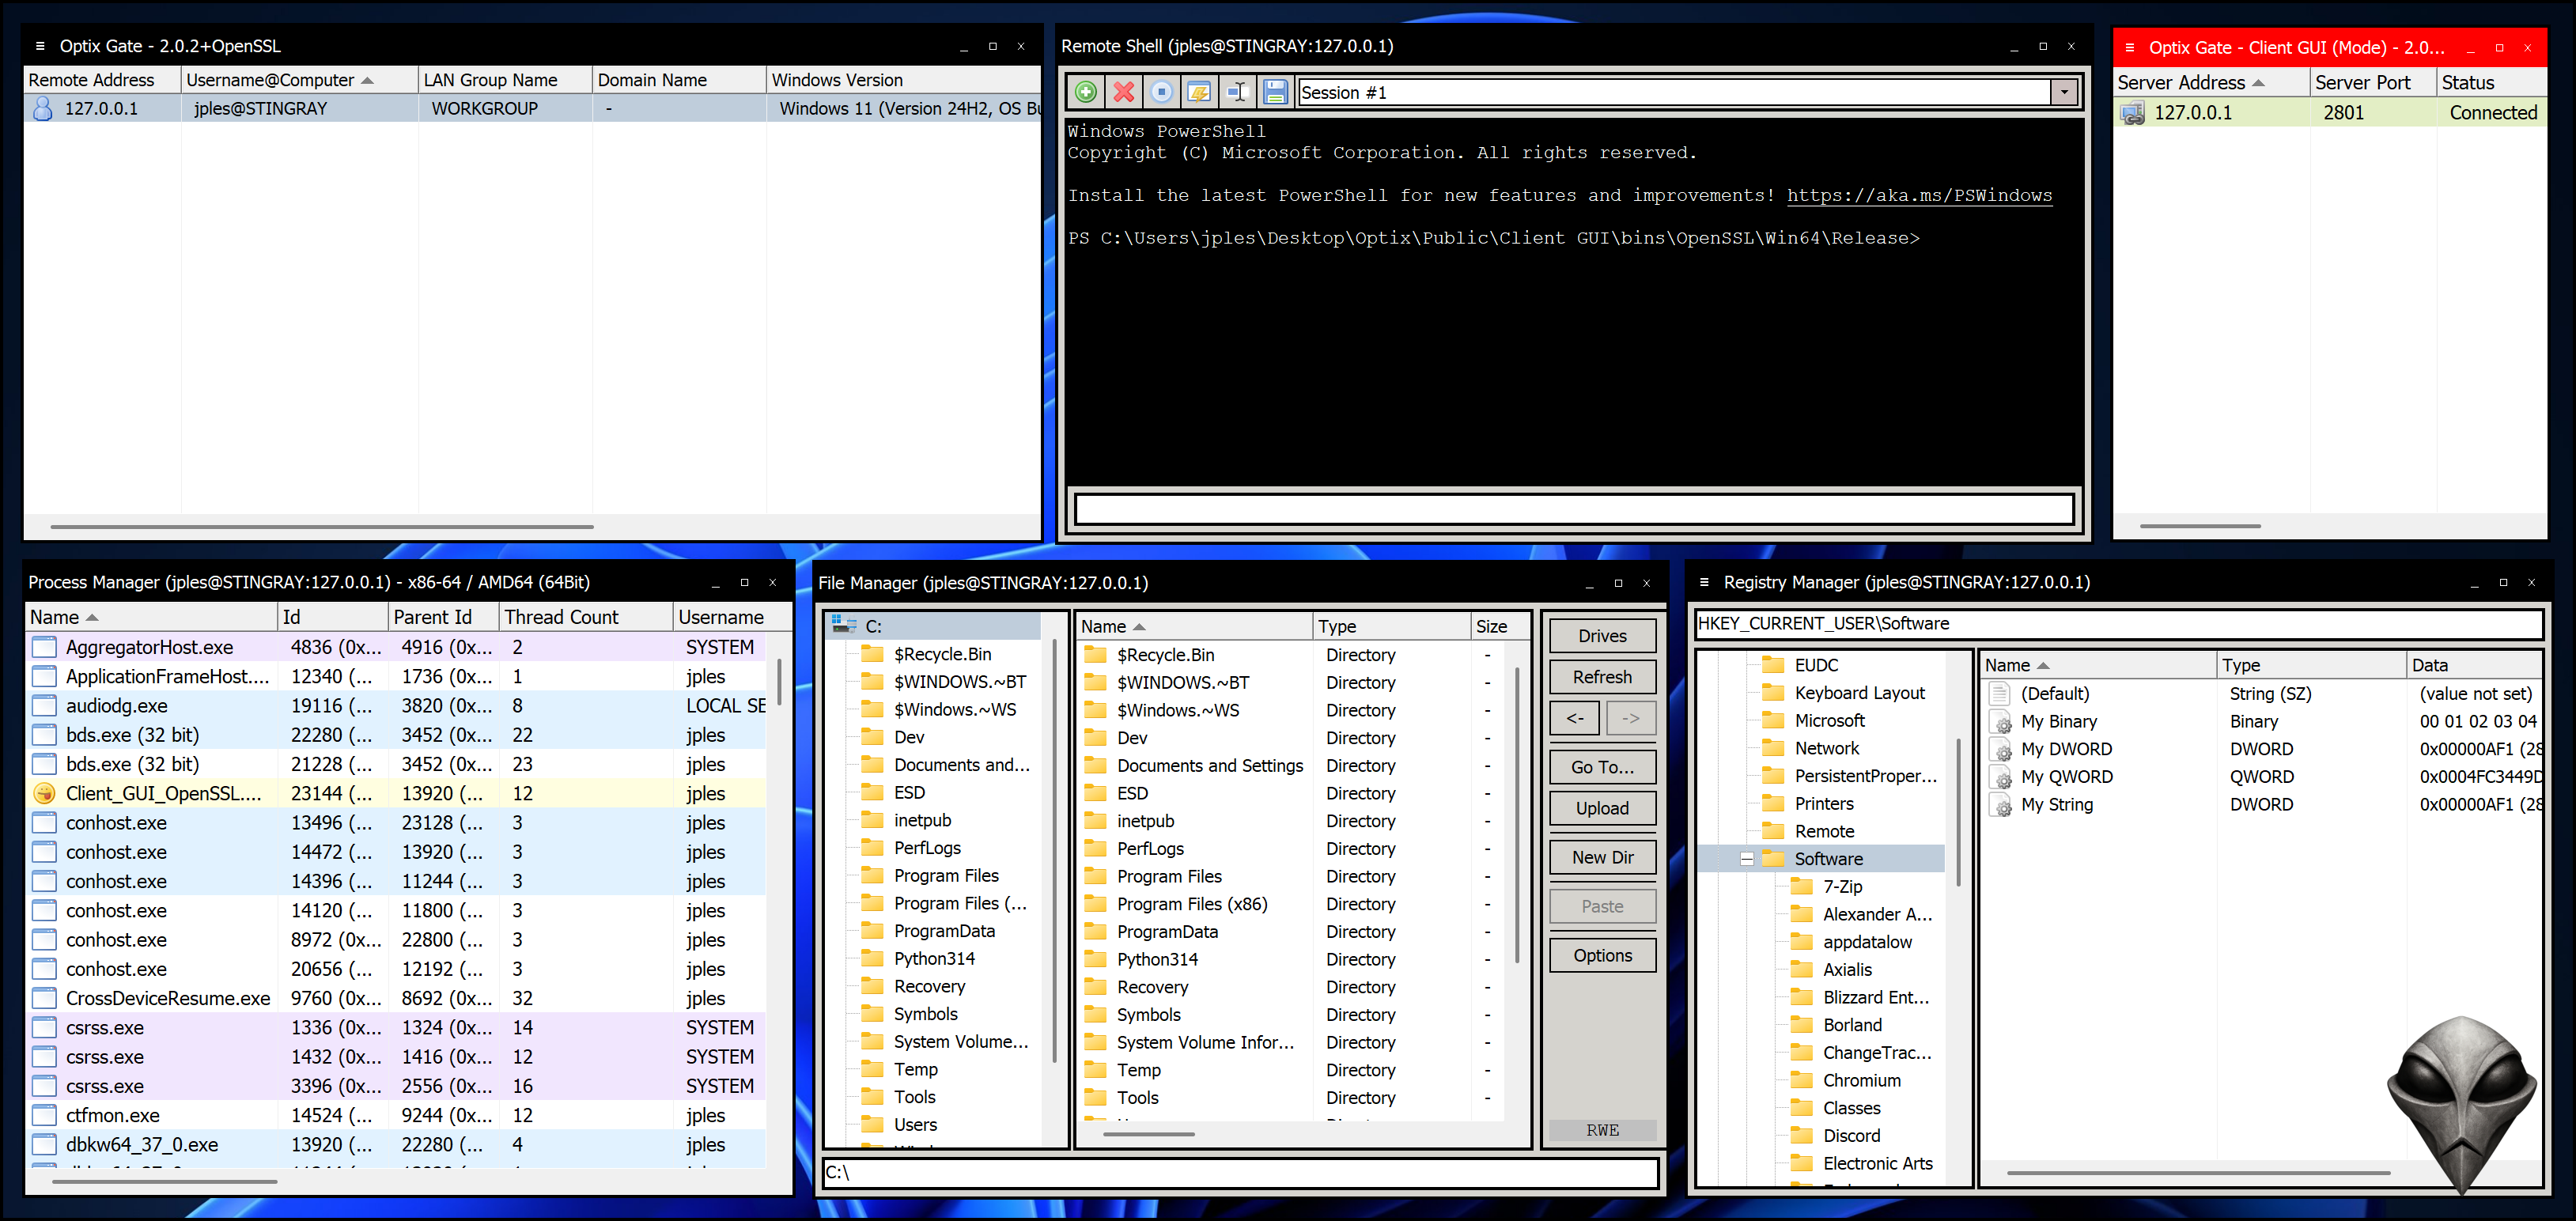 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows
 3nailsinfosec/dcvc2
Discord voice channel C2 framework for covert command and control operations. Transmits all data via RTP packets over voice channels, leaving no…
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
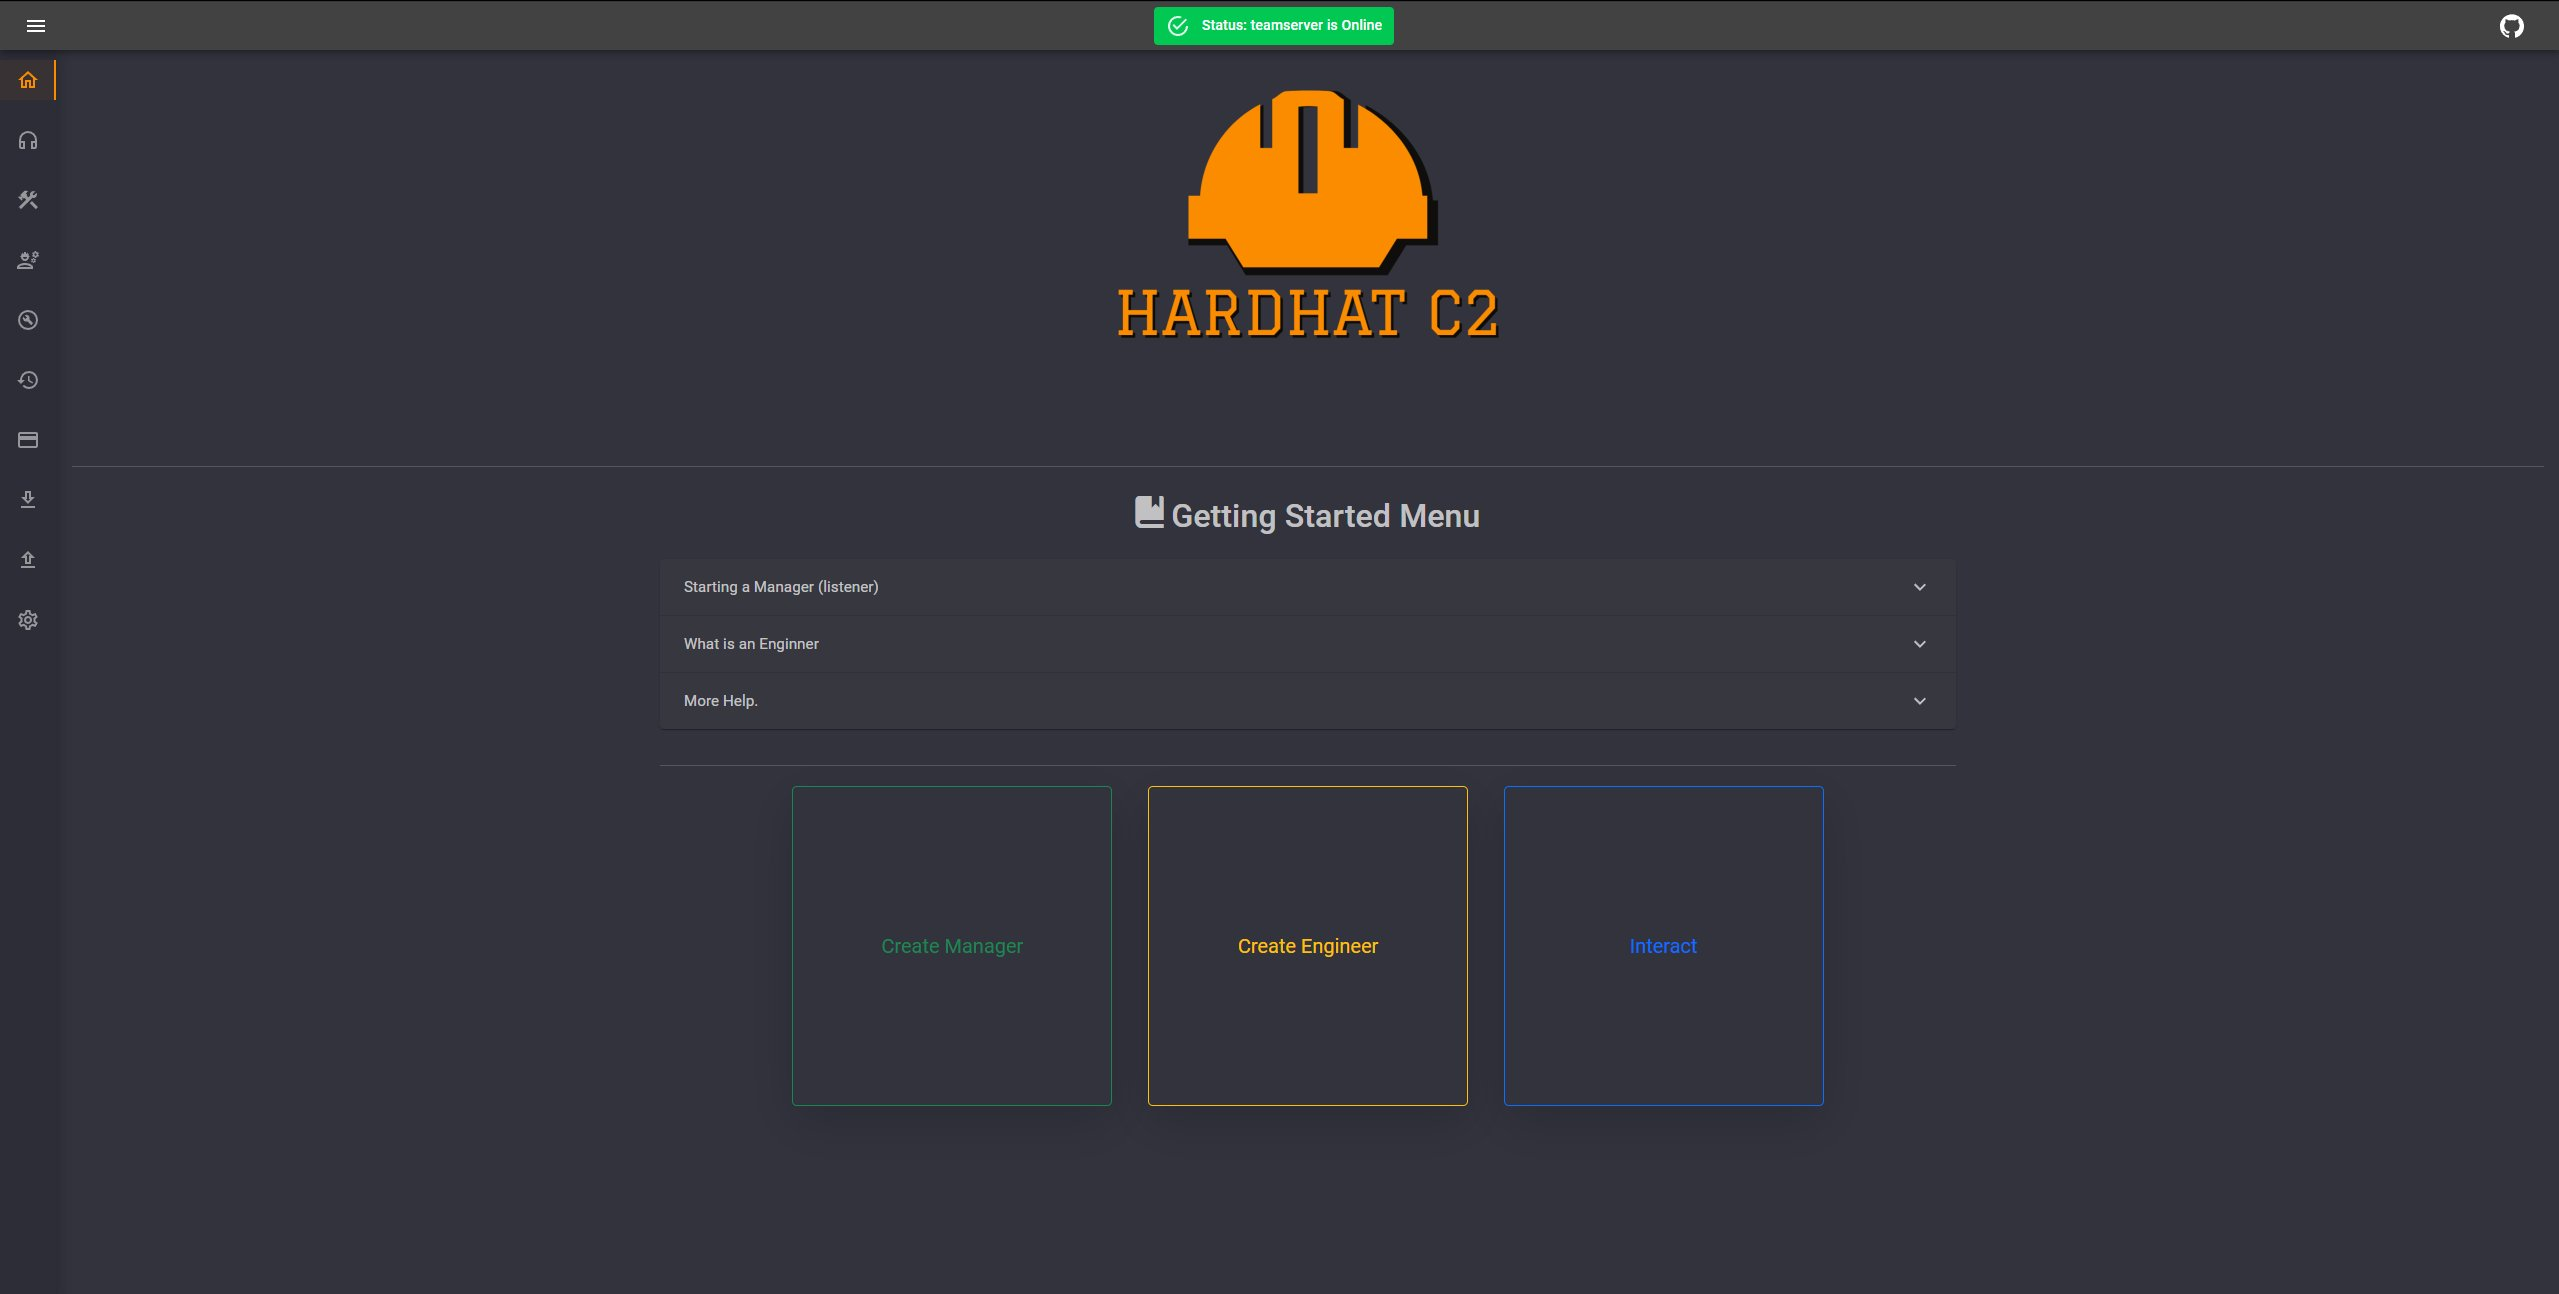 dragoqcc/cruciblec2
A C# Command & Control framework
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 gellin/bantam
A PHP backdoor management and generation tool/C2 featuring end to end encrypted payload streaming designed to bypass WAF, IDS, SIEM systems.
 d4rk007/sak1to-shell
Multi-threaded, multi-os/platform (Linux/Windows) c2 server and Windows reverse TCP shell client both written in C.
 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
 spiderlabs/scavenger
scavenger : is a multi-threaded post-exploitation scanning tool for scavenging systems, finding most frequently used files and folders as well as…
 alessandroz/pupy
Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…