

CVE-2026-114509
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
authenticationexploitationinformation-gathering+6
nxploited/cve-2026-114509Laravel TokenGuard authentication bypass through non-string API credentials
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 horizon3ai/cve-2026-102489
Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…
 fulxey/cve-2022-0543
Redis RCE through Lua Sandbox Escape vulnerability
 0xtatsuki/cve-2026-31857
Craft CMS RCE via relational conditionals in the control panel
 mrdebora/cups-2.4.16-lpe
CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 super-meuw/cve-2026-86218
Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
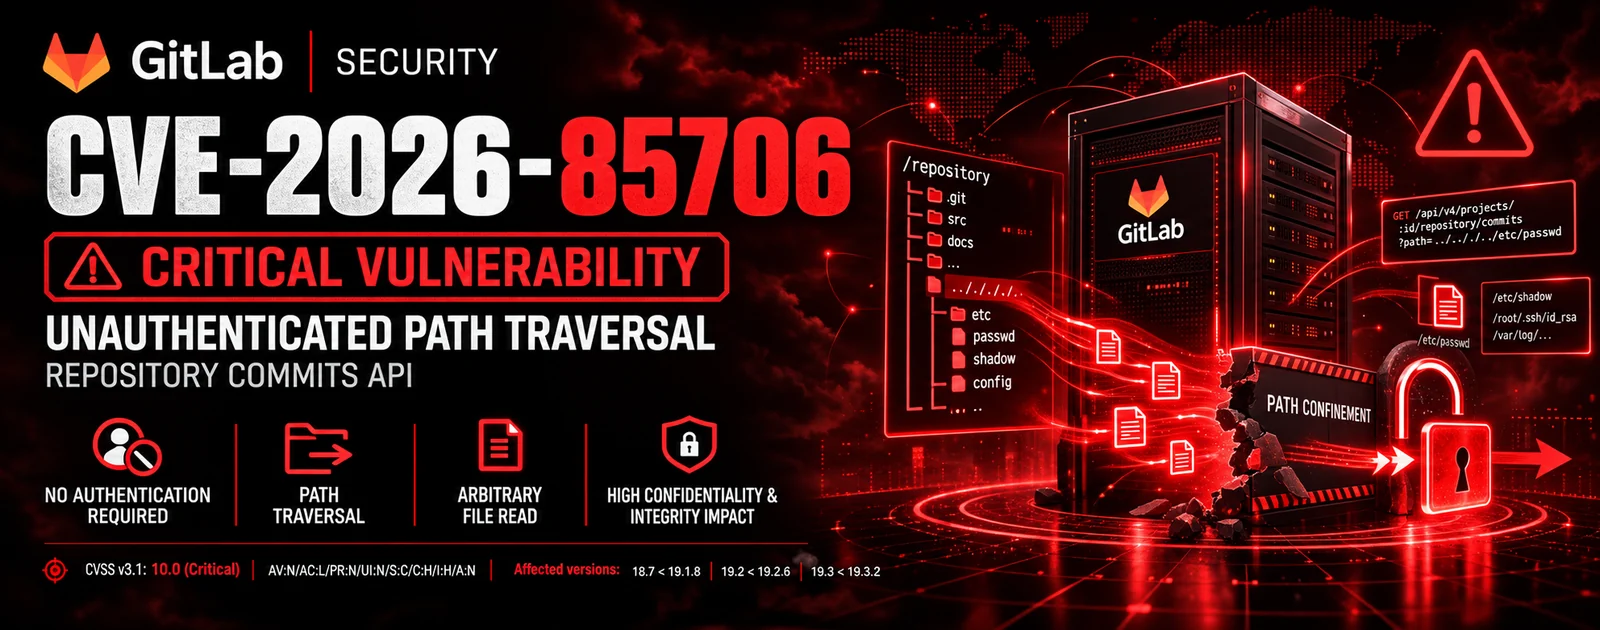 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
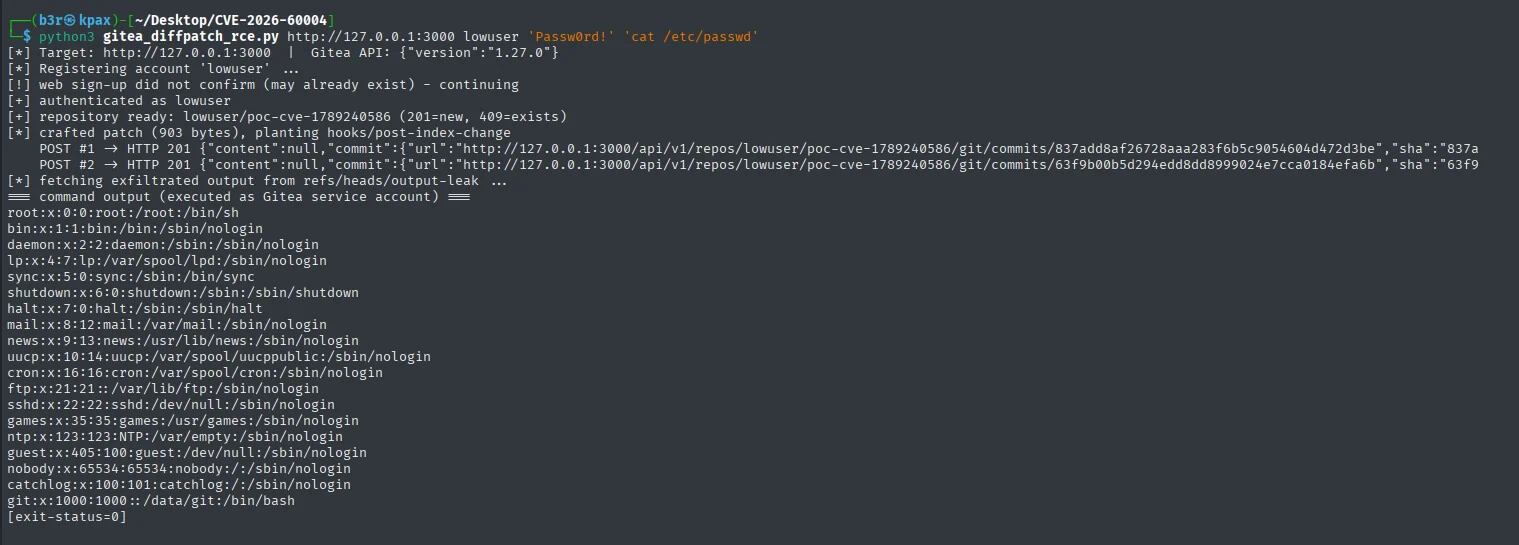 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution