
CVE-2026-90847
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
embedded-systems-securityexploitationiot-security+5
shlln/cve-2026-90847Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
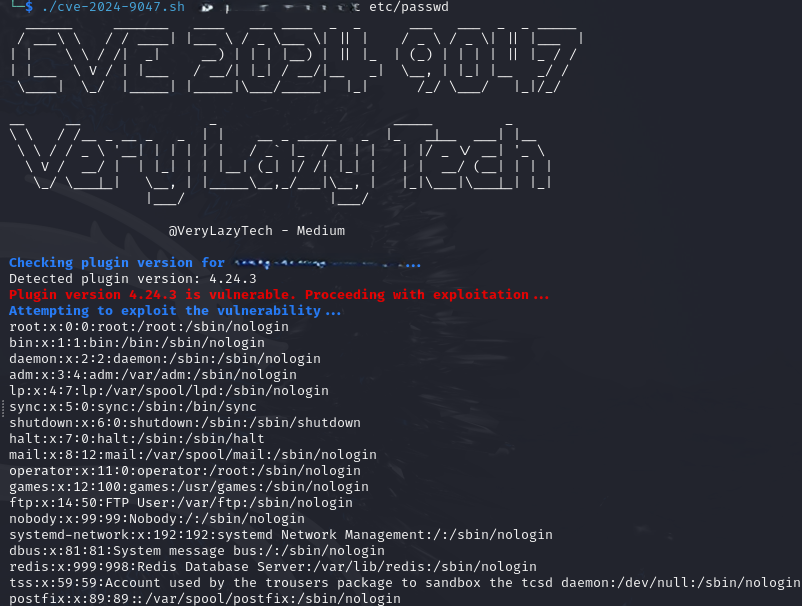 verylazytech/cve-2024-9047
POC - WordPress File Upload plugin, in the wfu_file_downloader.php file before version <= 4.24.11
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 deathshotxd/cve-2025-52691-apt-poc
An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.