
Silverseal
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
166
idov31/silversealLinux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 withsecurelabs/ppid-spoofing
Scripts for performing and detecting parent PID spoofing
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
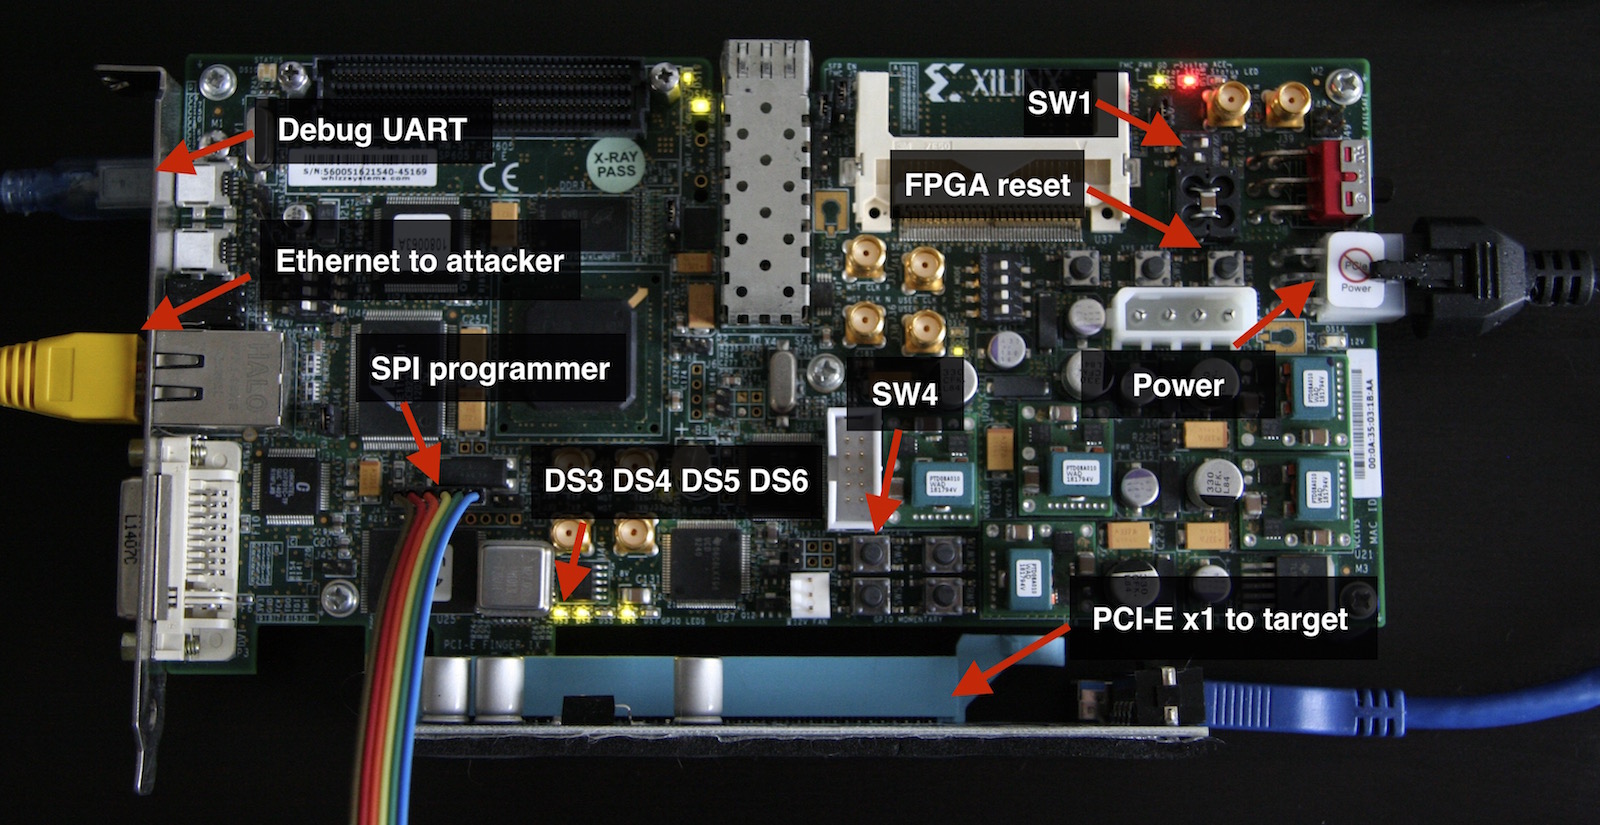 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.
 zeromemoryex/terminator
Reproducing Spyboy technique to terminate all EDR/XDR/AVs processes
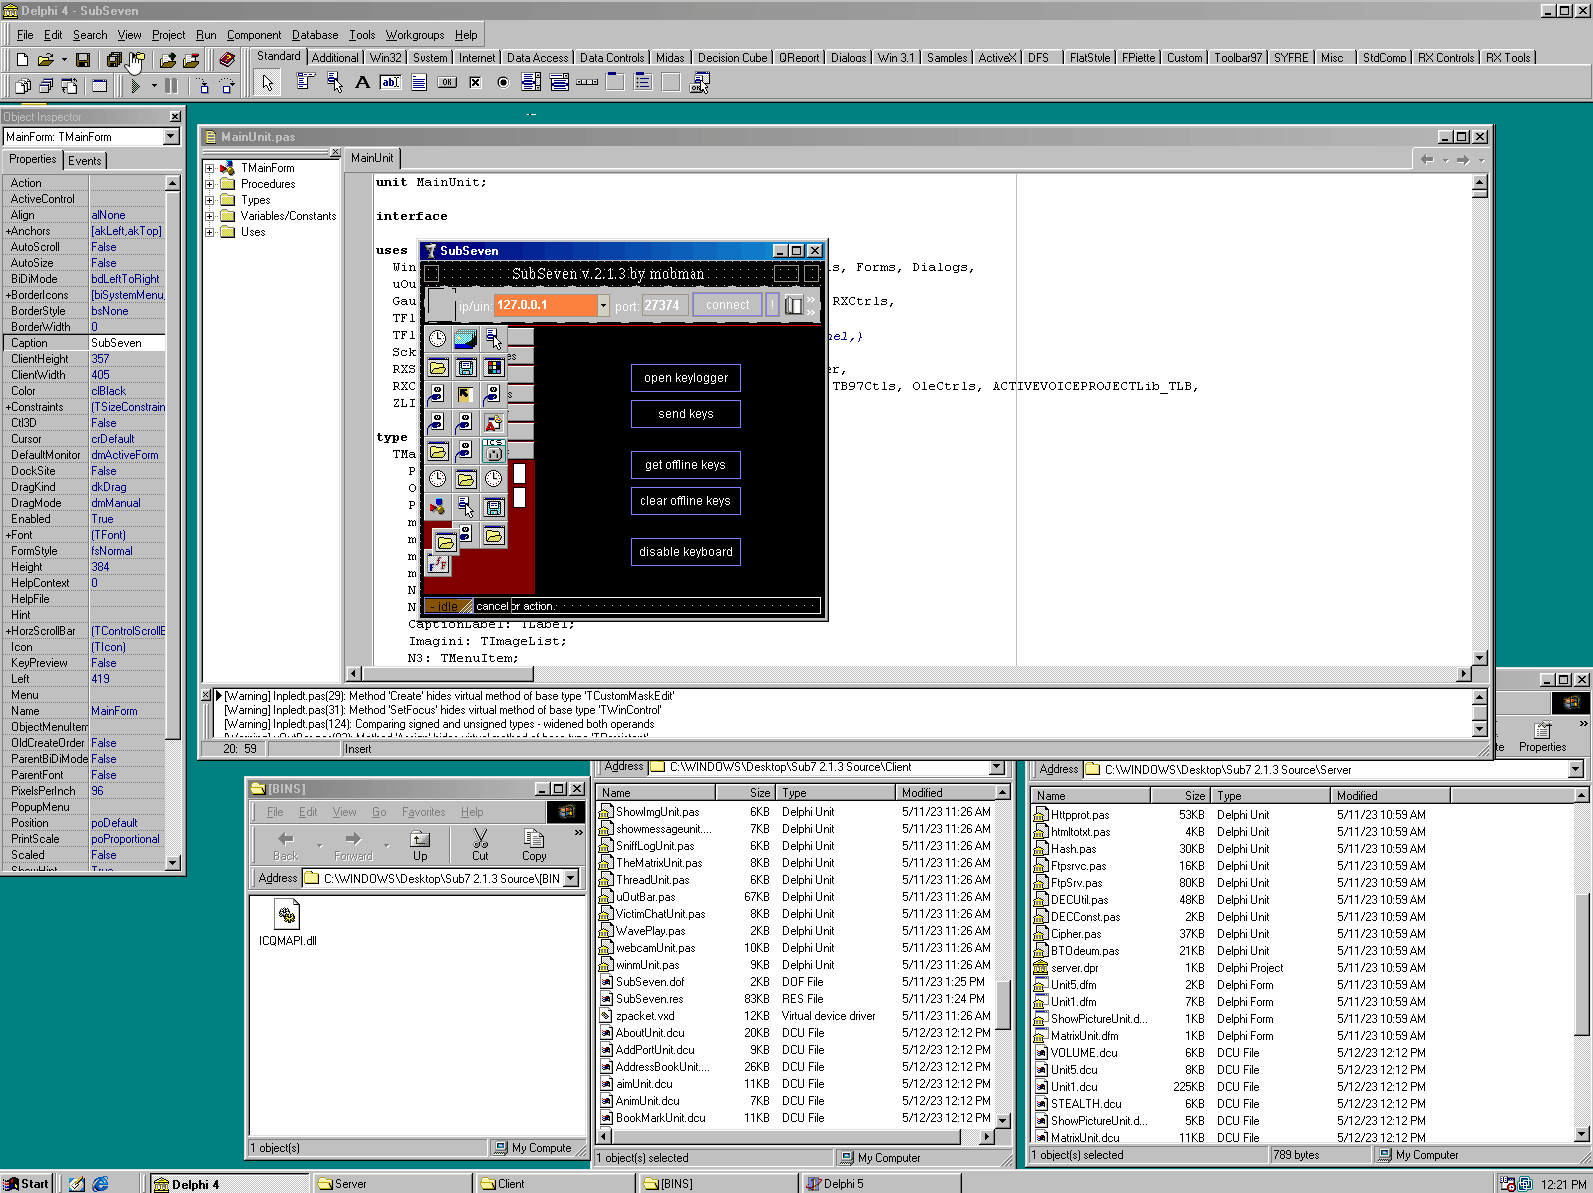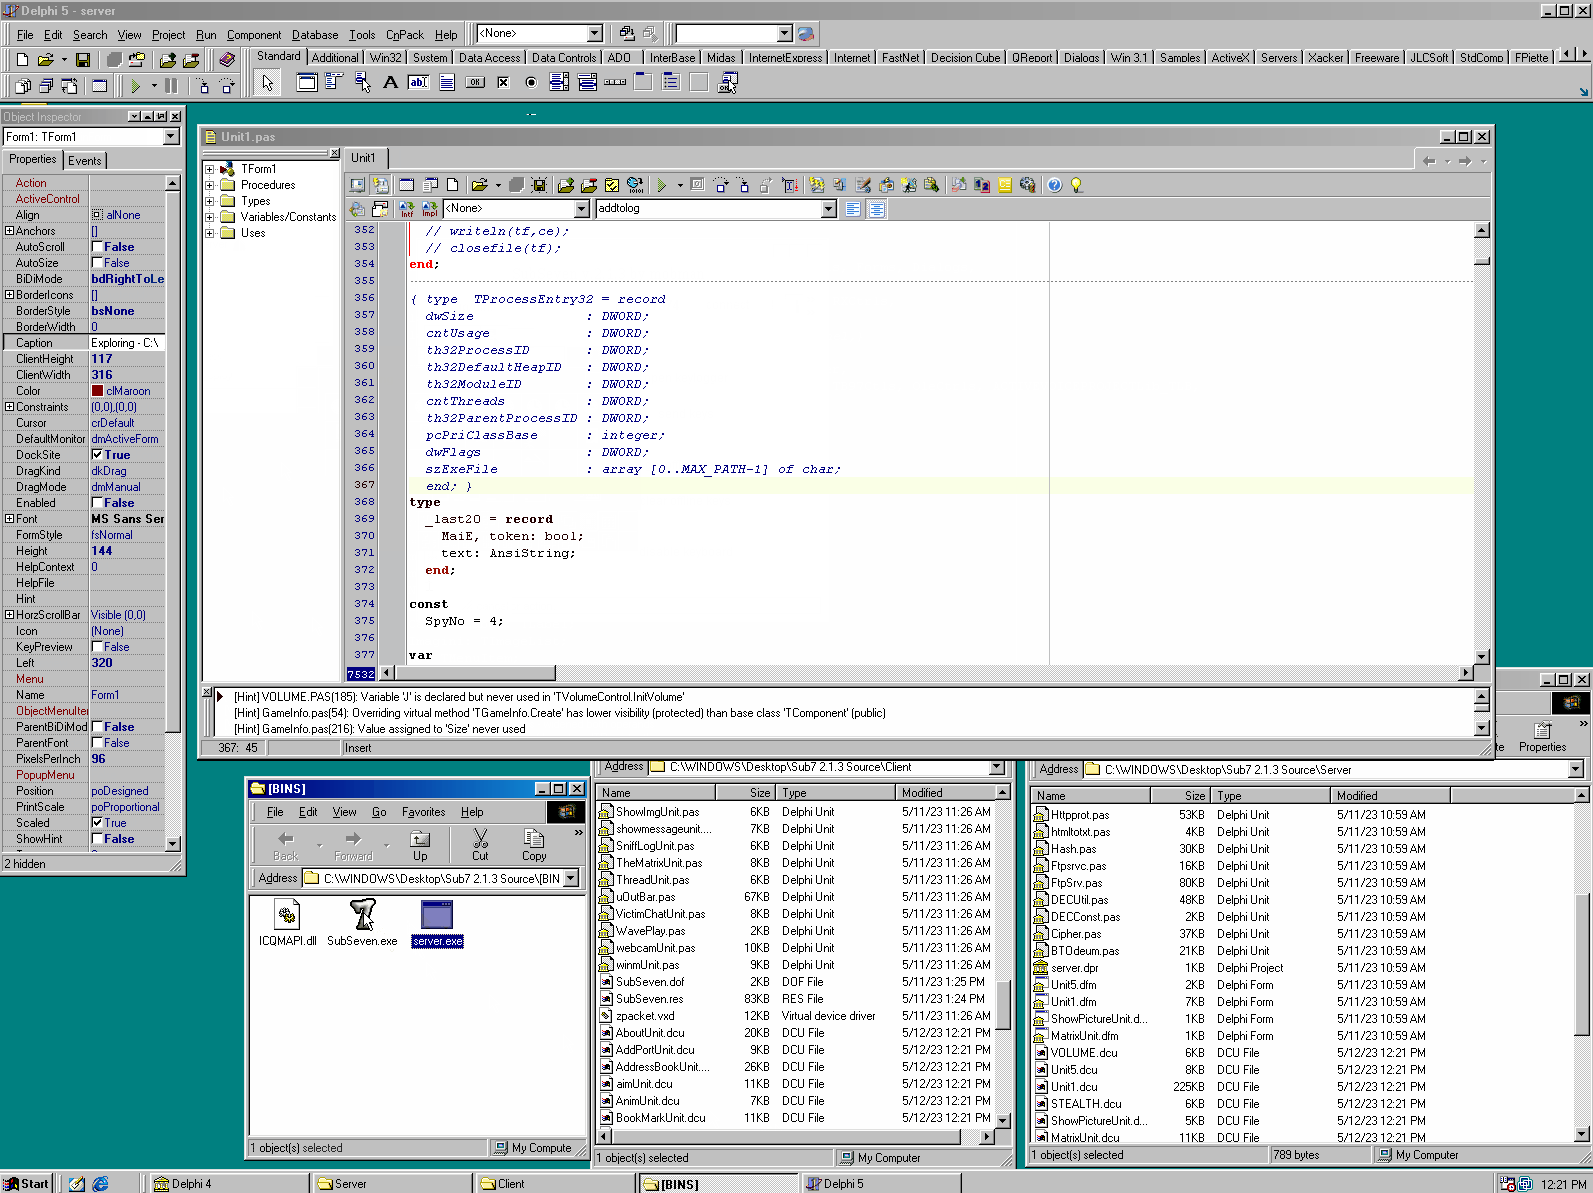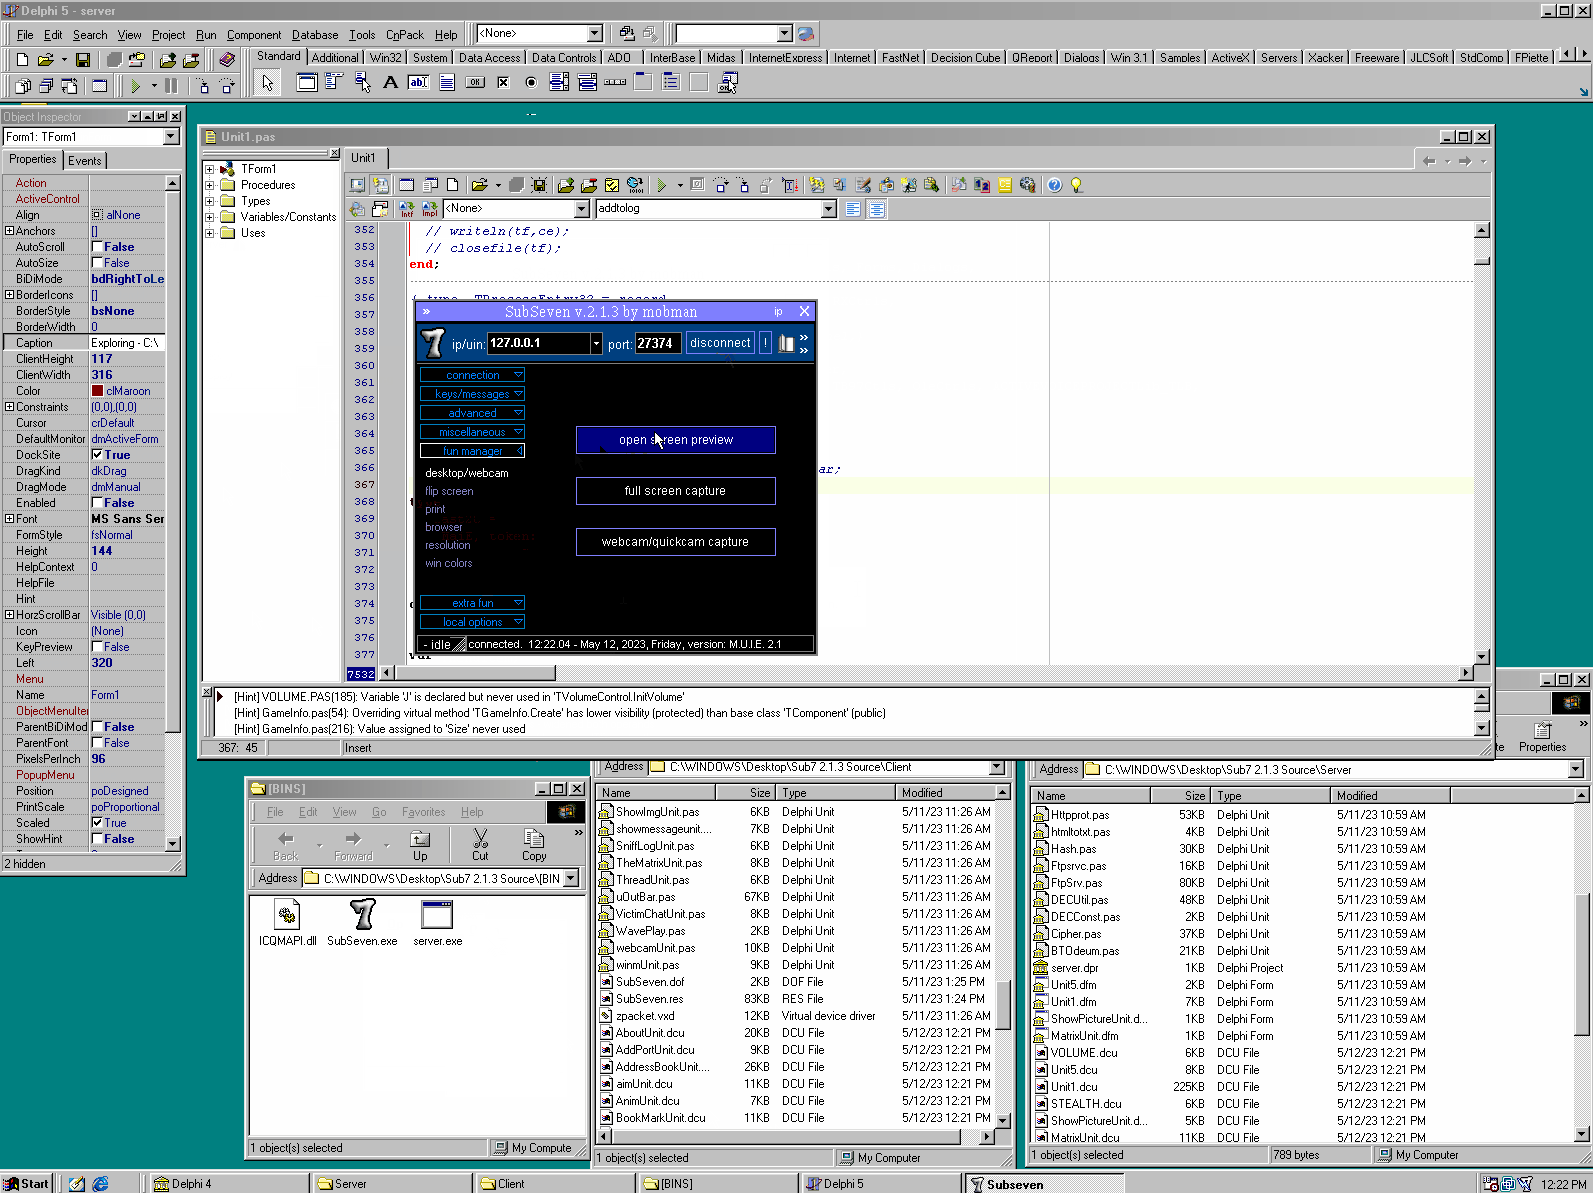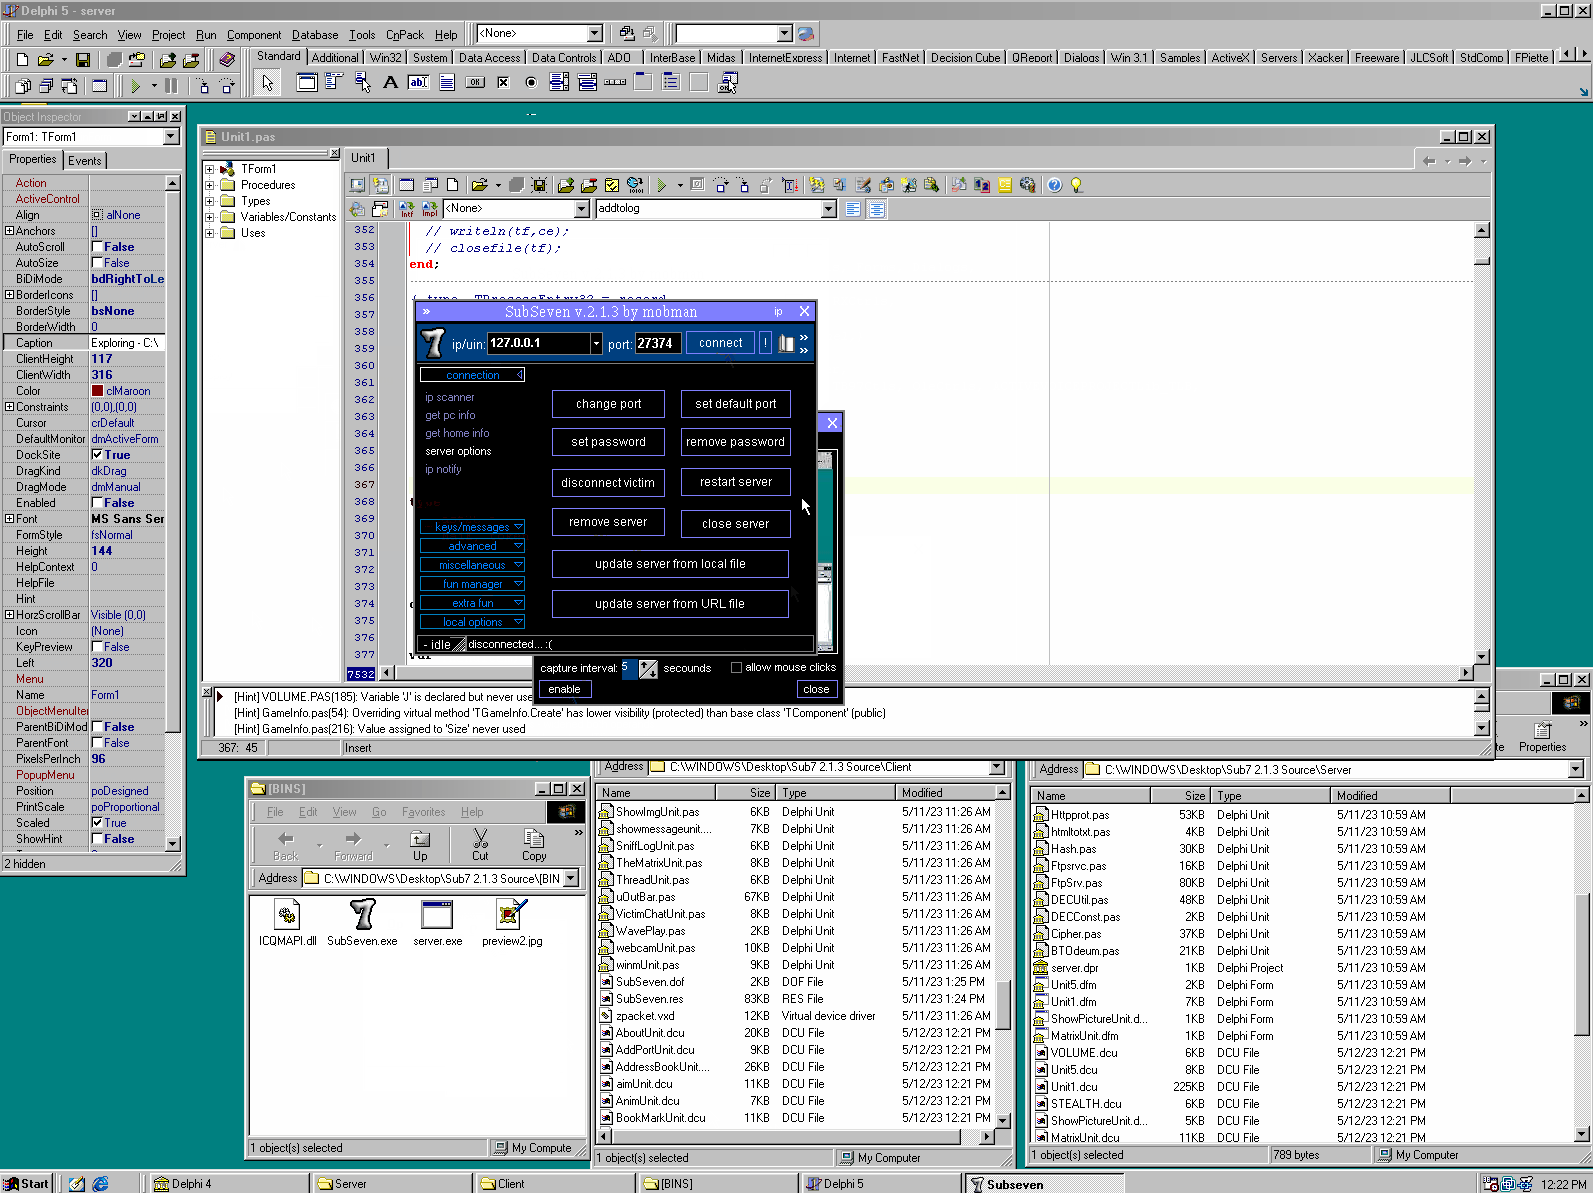
 illwill/sub7
Source code for SubSeven 2.1.3
 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 mbadanoiu/mal-002
MAL-002: Force System Restart via Installed Windows MSIs
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed