

Overthrone
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
command-and-controlexploit-frameworksinformation-gathering+8
31
karmanya03/overthroneAll-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 onescripter/wmiexec
Execute Windows commands remotely and capture output using only WMI and PowerShell (not remoting).
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 mythicagents/xenon
A Mythic agent for Windows written in C
 4xura/cve-2026-44011-craftcms-auth-rce
The PoC of CVE-2026-44011: Craft CMS RCE with an authenticated user.
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 iterat0r/cnaemulator
Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
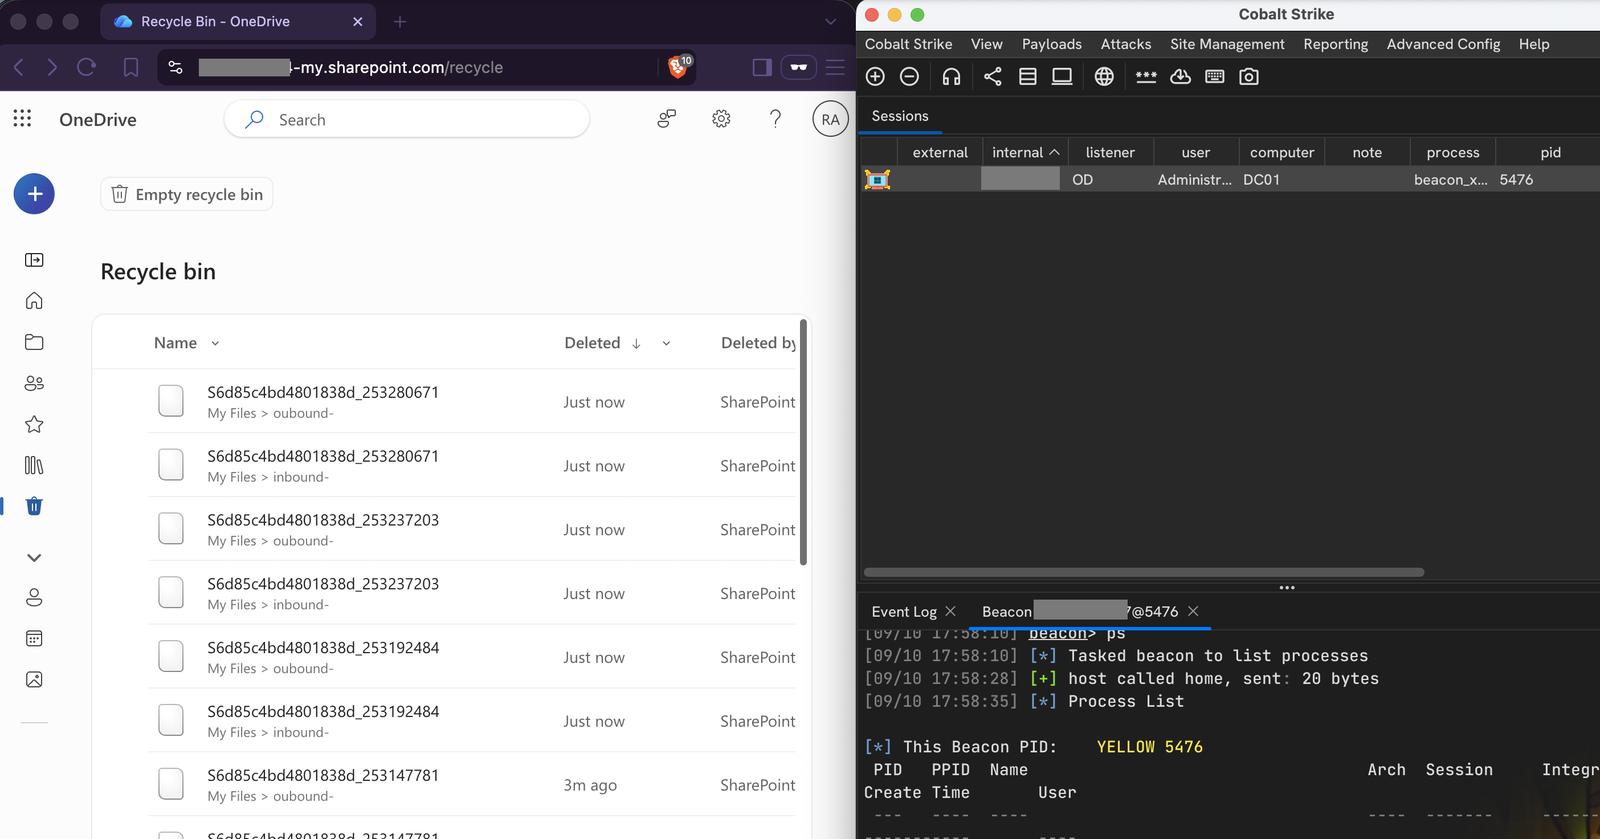 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 zildanz/cve-2026-64638
Node.js exploit for CVE-2026-64638 that runs an ngrok tunnel to a malicious endpoint, enabling remote access and post-exploitation control.