external-c2-experiments

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…

Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…

A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…

Exploit chain for local privilege escalation on SUSE Linux, chaining PAM environment injection and a udisks2 race condition to obtain a root shell.

Smart keylogging capability to steal SSH Credentials including password & Private Key

A WiFi Pineapple infecting worm.

The SSH Multiplex Backdoor Tool

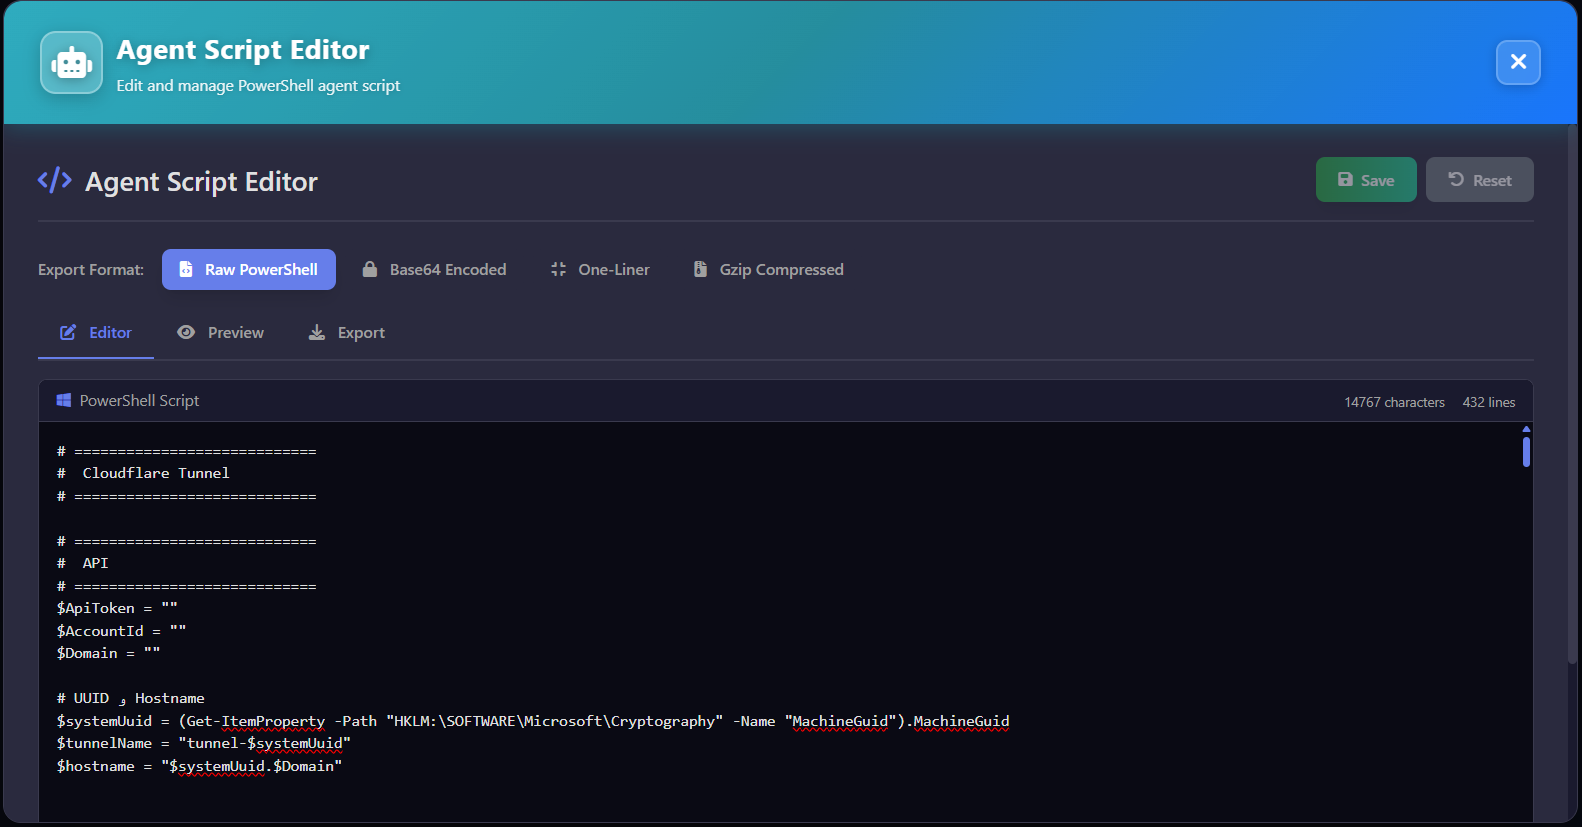
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…

Exploit for Ubuntu 20.04 using CVE-2021-3156 enhanced with post-exploitation scripts

Golang tool designed to exfiltrate passwords found via the sshd and su services

Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…

Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…

HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…

Chisel new generation, written in rust. SSH under WSS with some customization.

Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…

Modified dropbear server which acts as a client and allows authless login