
CouchPotato
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
exploitationpayload-developmentpost-exploitation+2
112
aaron-kidwell/couchpotatoWindows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 m3f157o/combine_harvester
Rust in-memory dumper
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
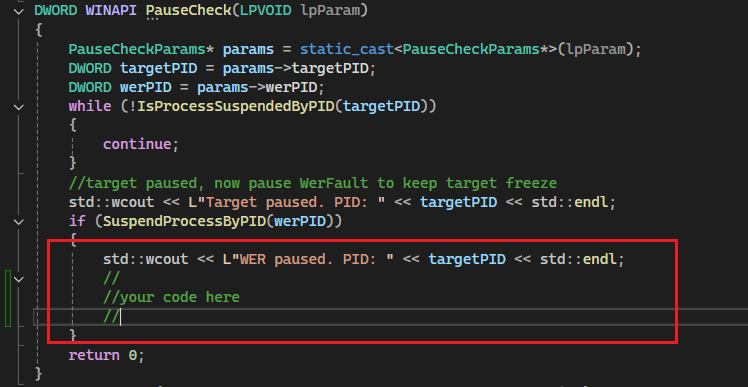 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
 nccgroup/diskwalker
Python script to efficiently find files on UNIX like file systems with specific properties (quicker than find)
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
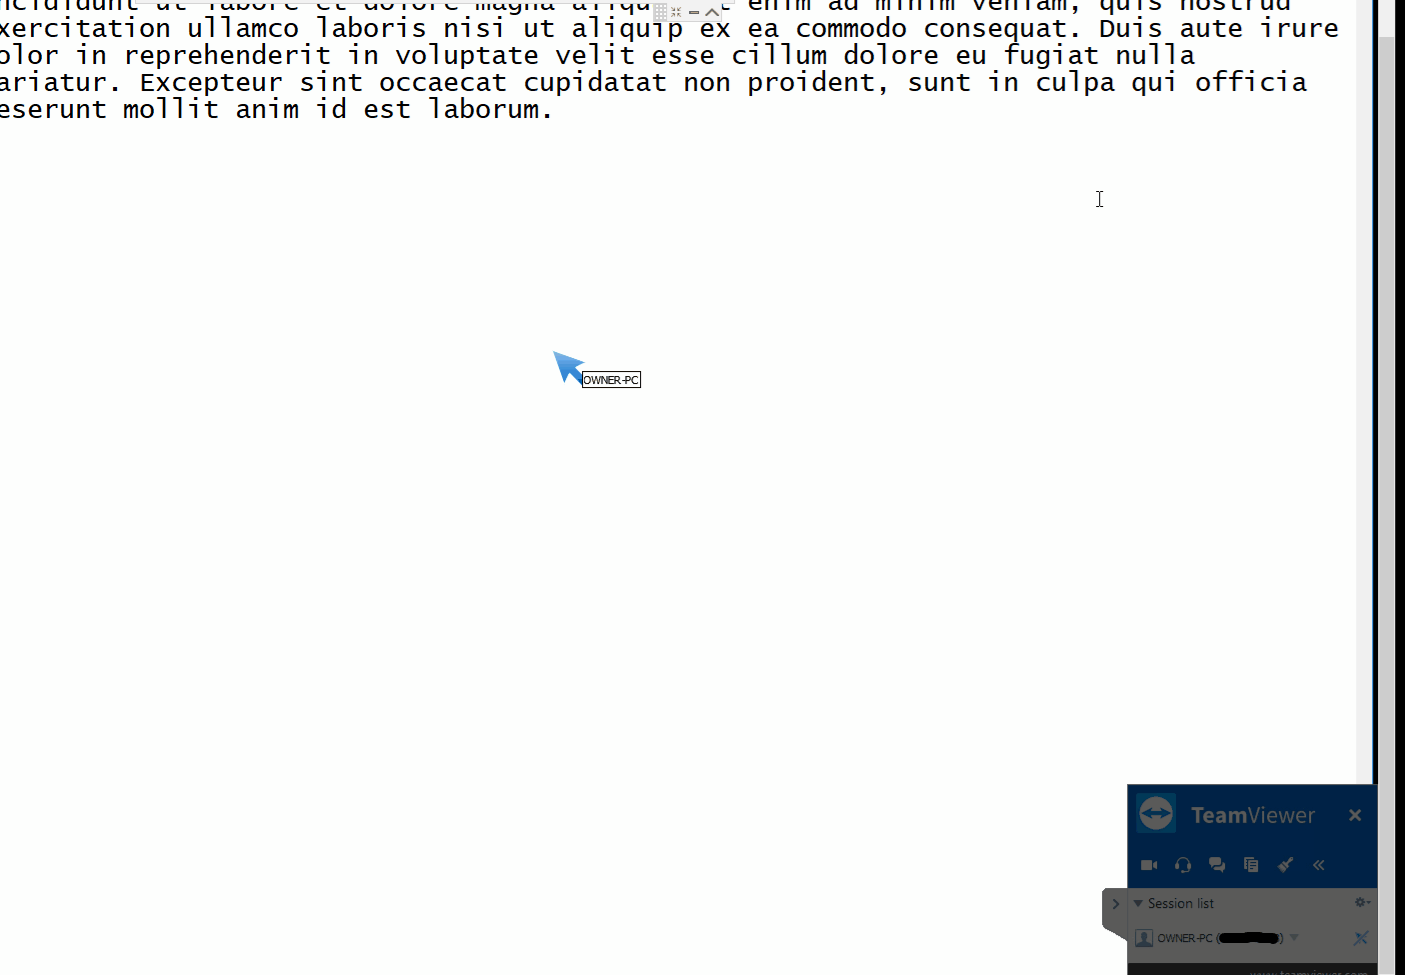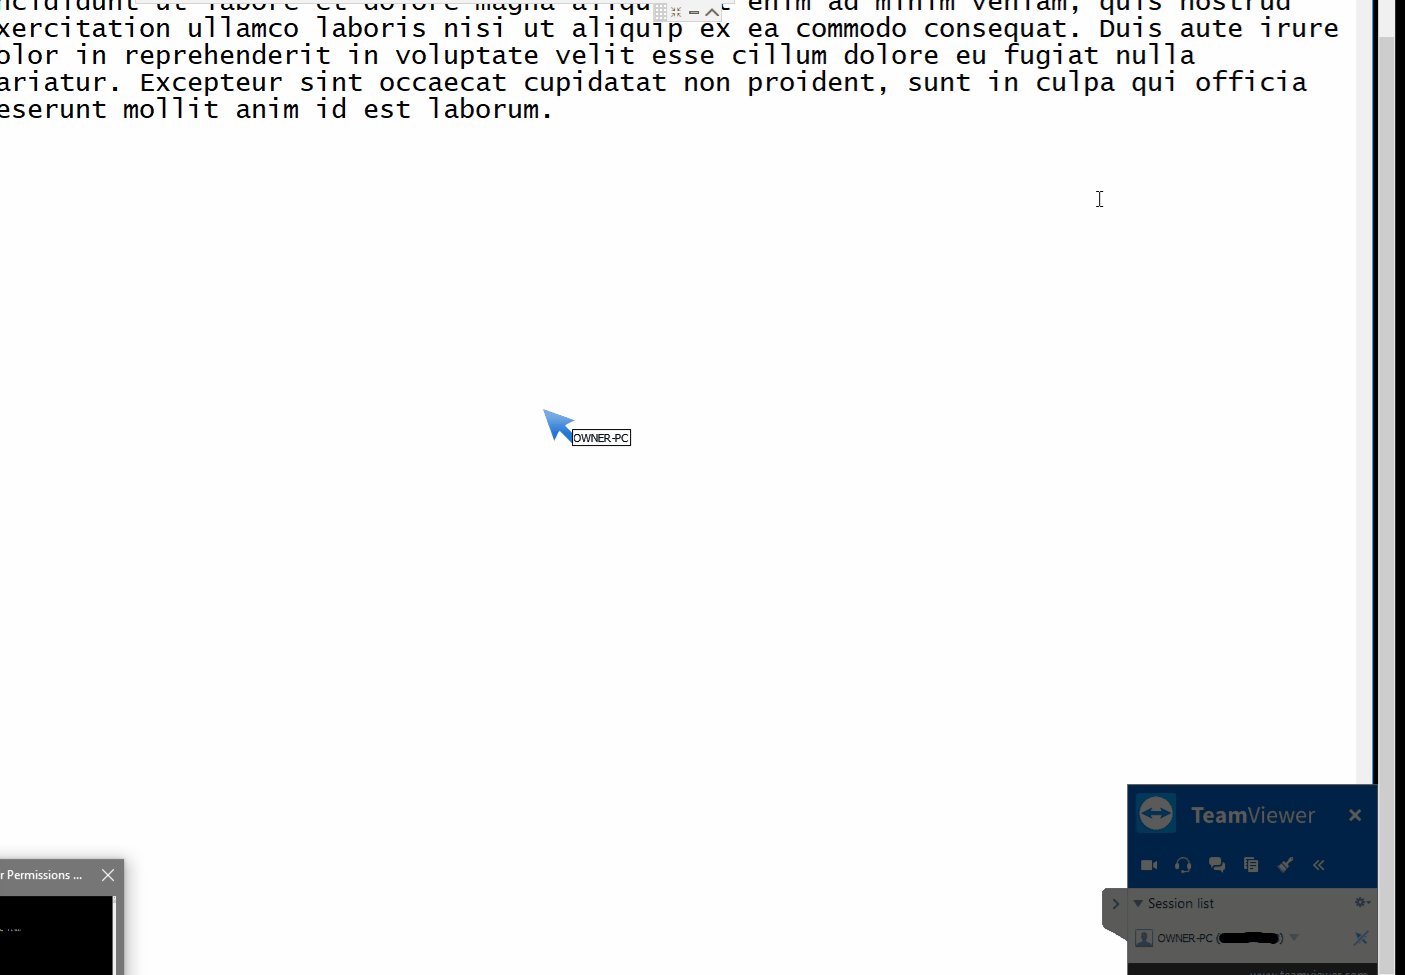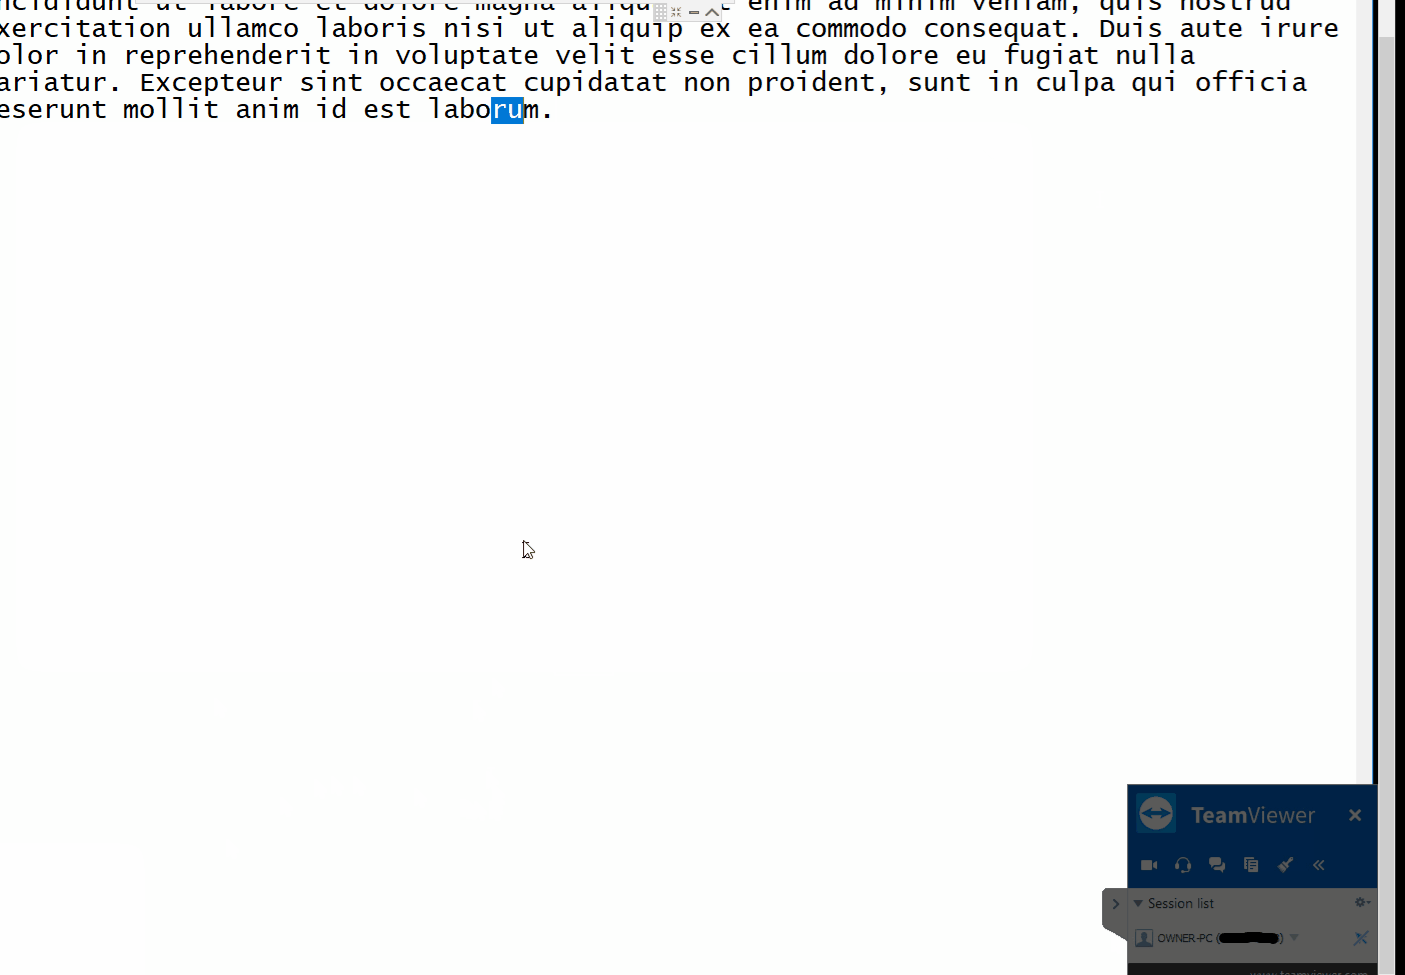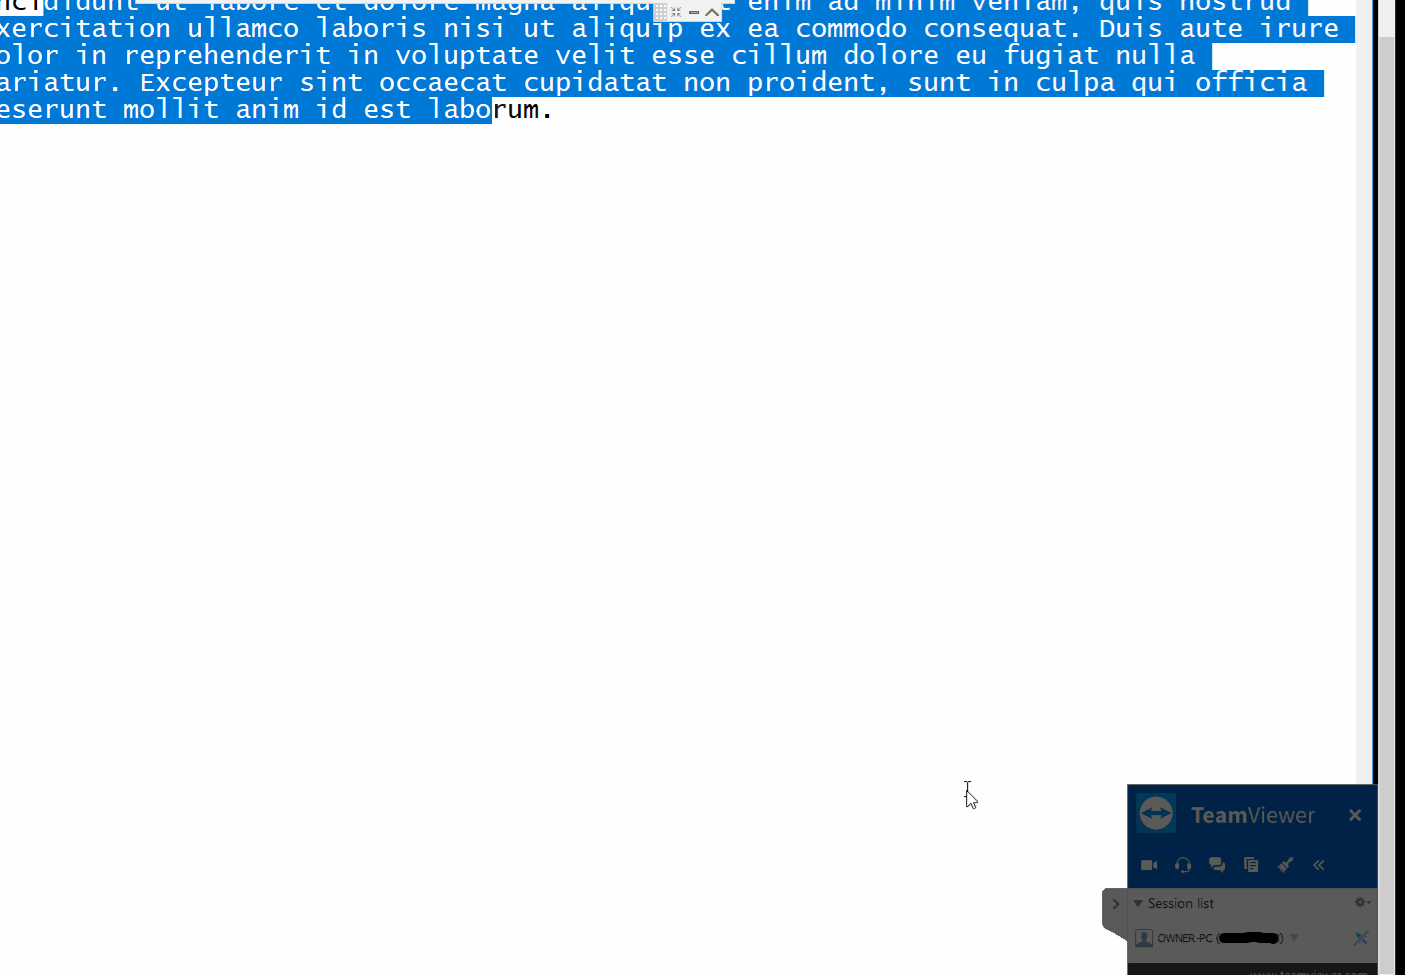 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
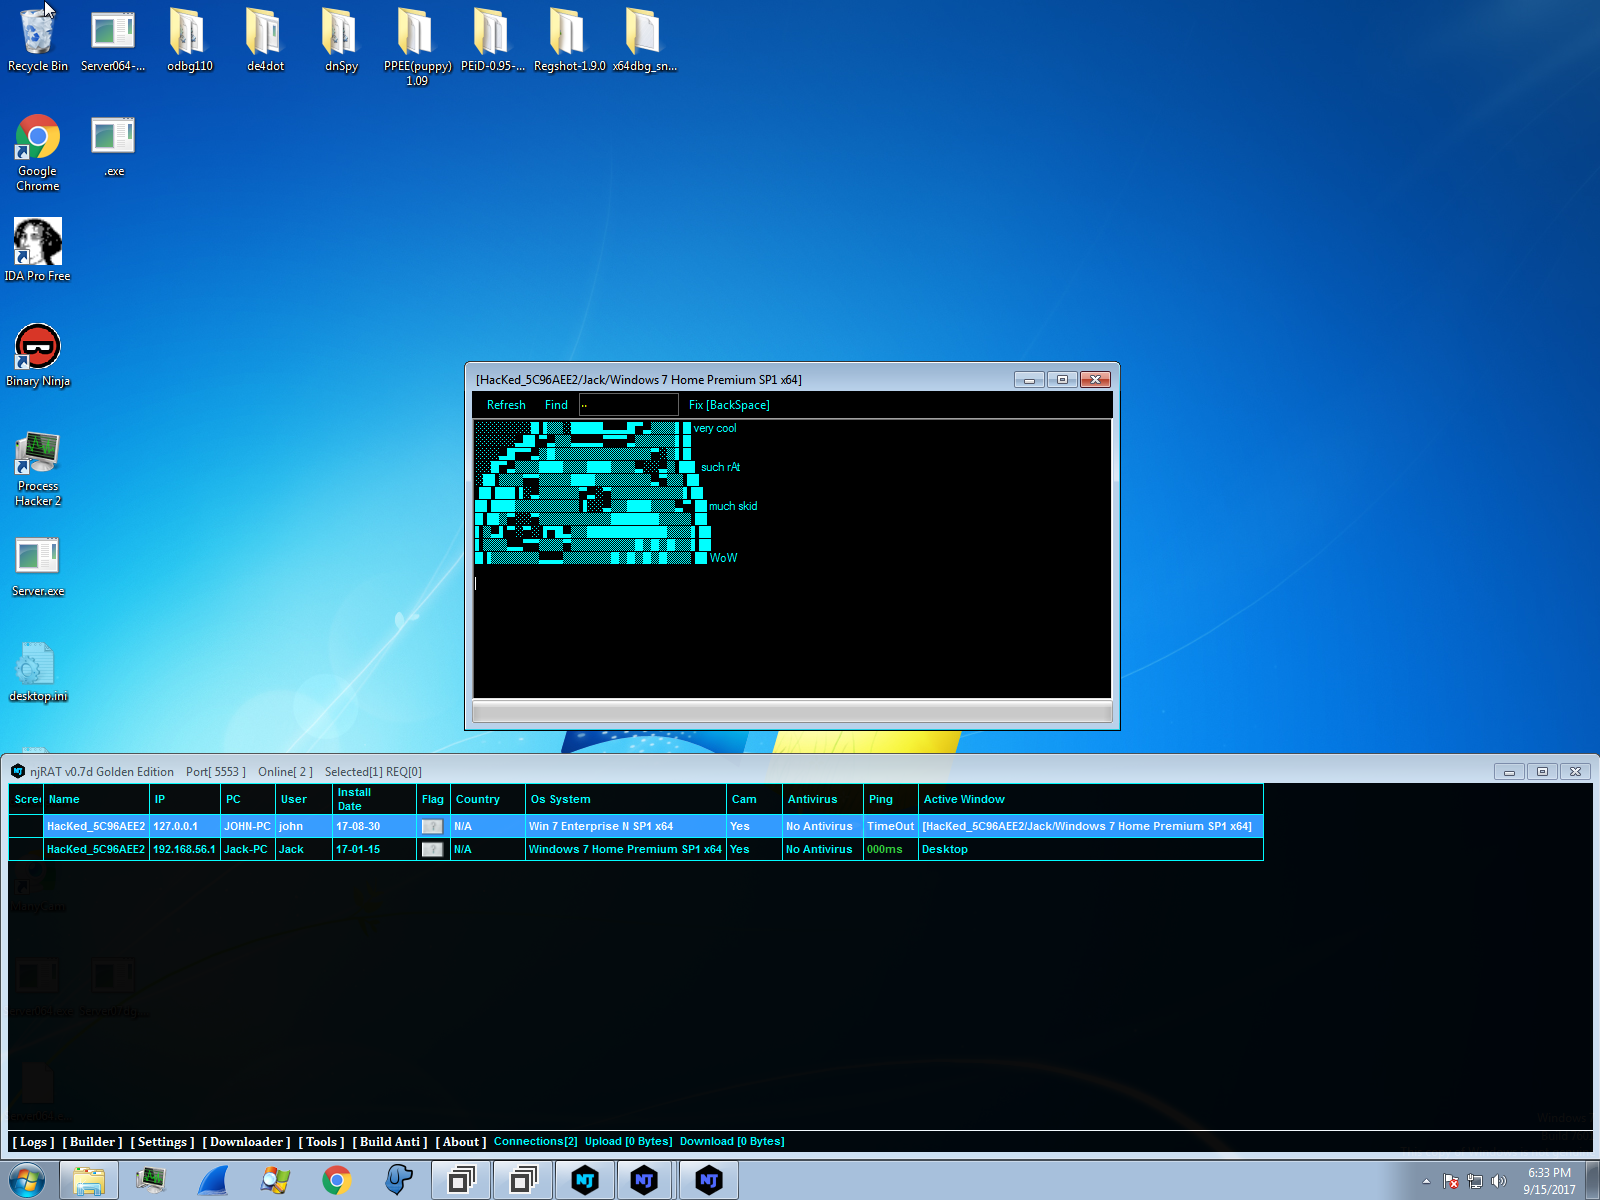 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 woj-ciech/social-media-c2
Script is a proof of concept how to control your machine by using social media sites.
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…