
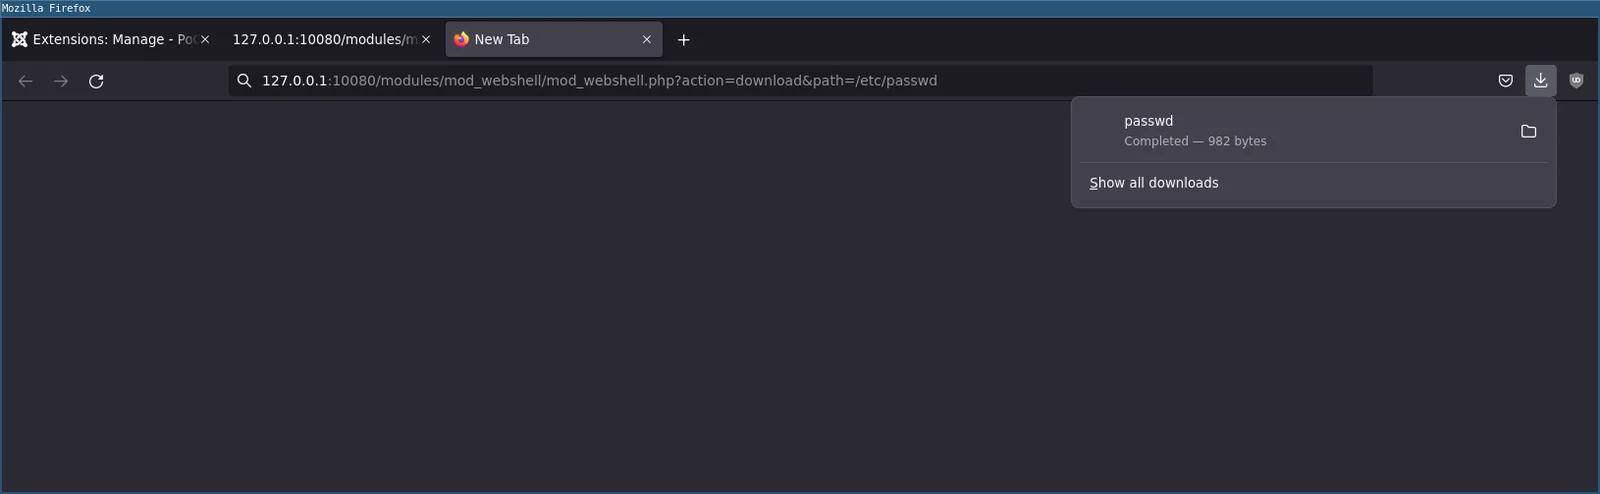
Joomla-webshell-plugin
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
command-and-controlexploitationpayload-development+6
62
p0dalirius/joomla-webshell-pluginA webshell plugin and interactive shell for pentesting a Joomla website.
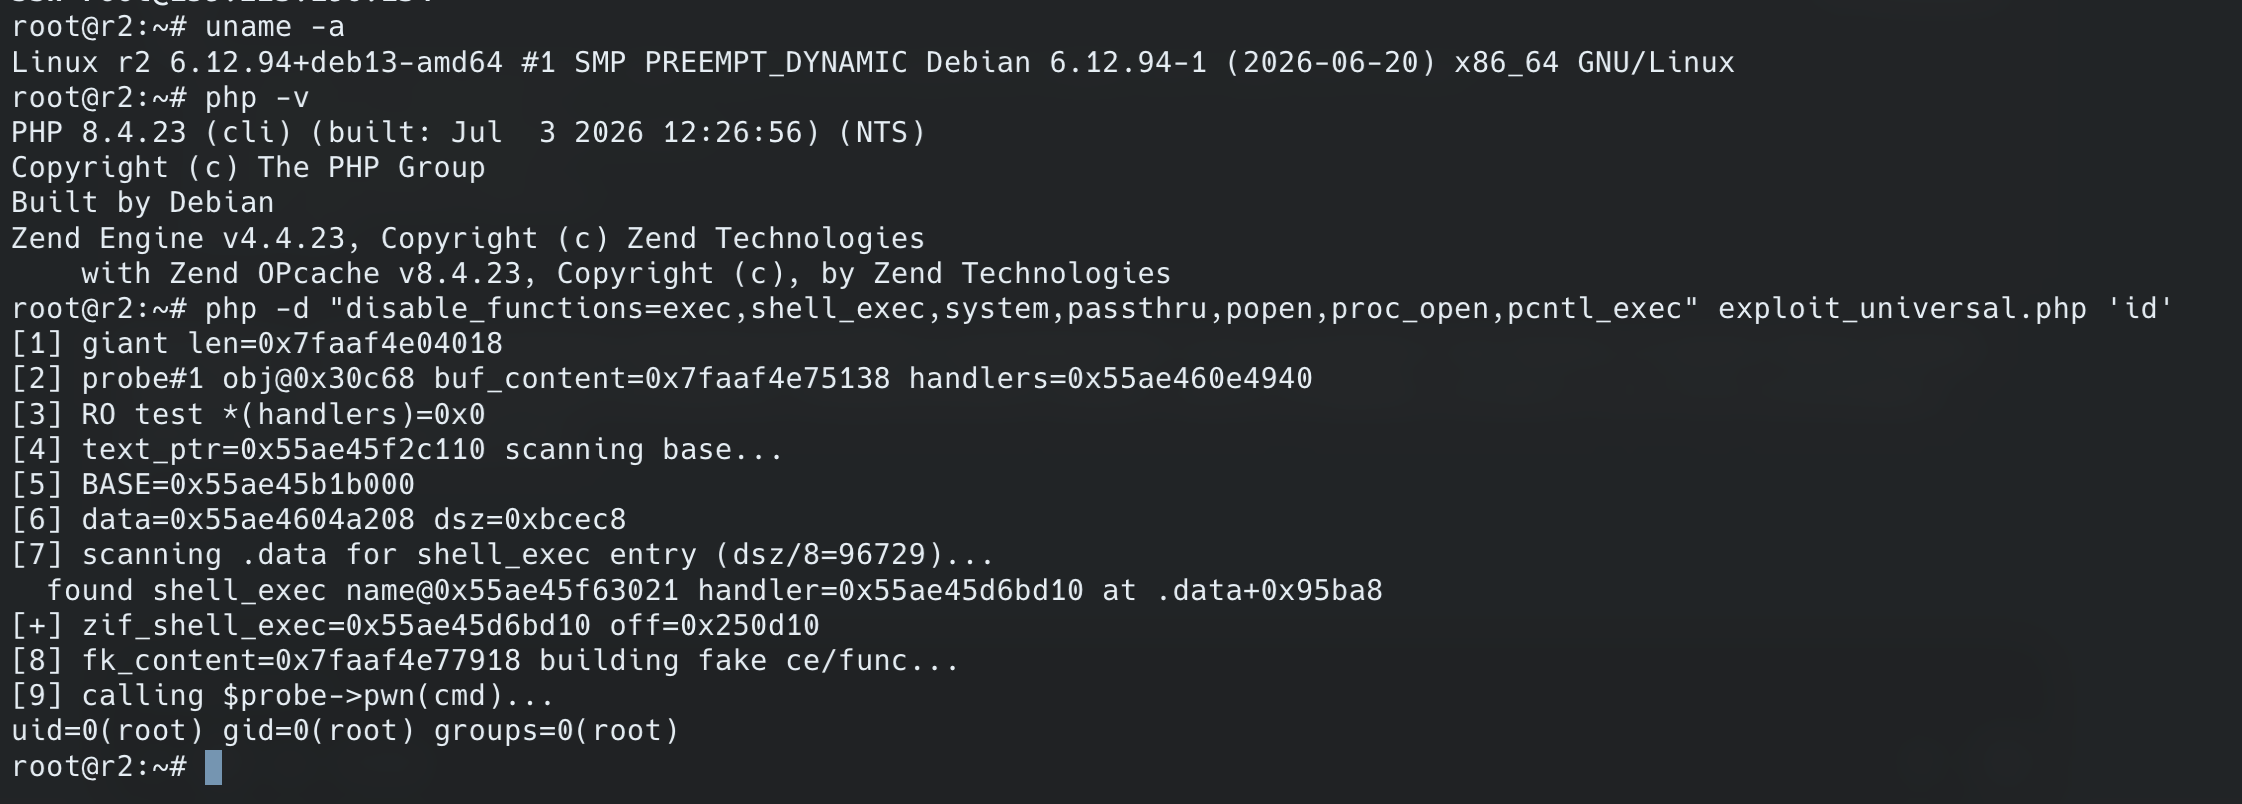 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 synacktiv/extloader
A chromium extension exploitation toolkit
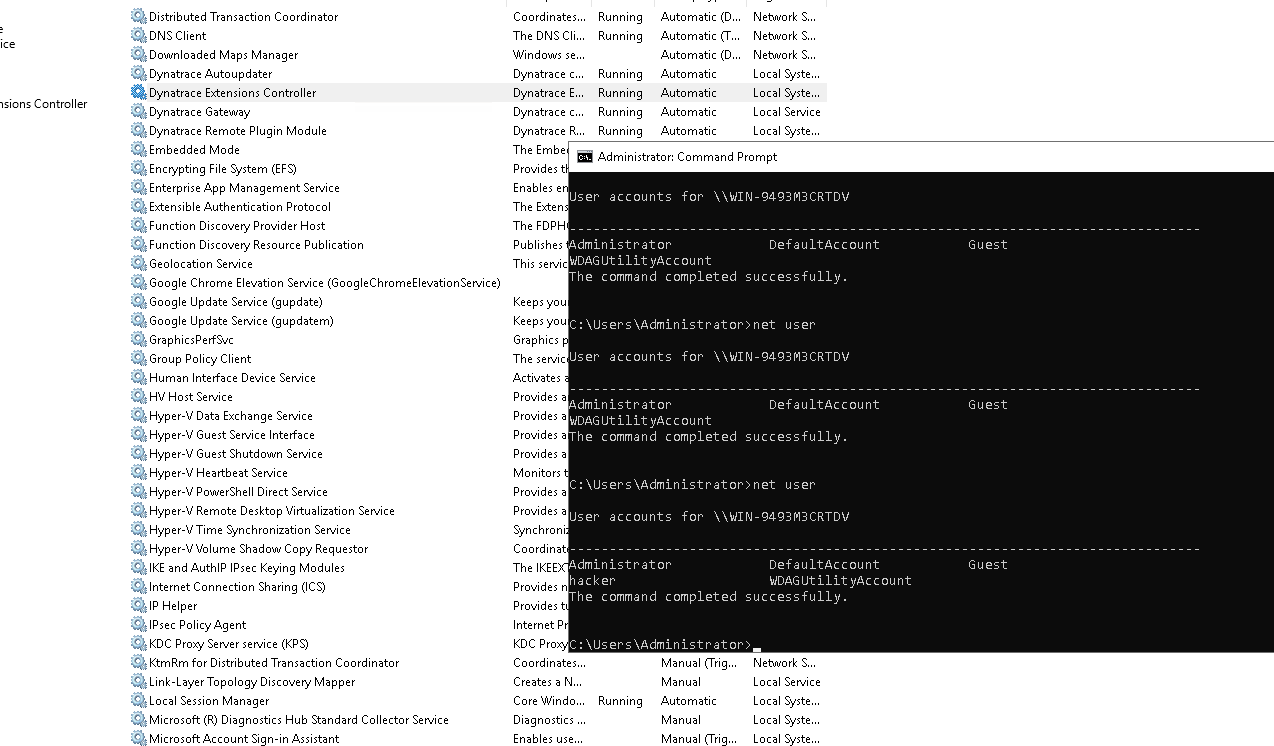 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
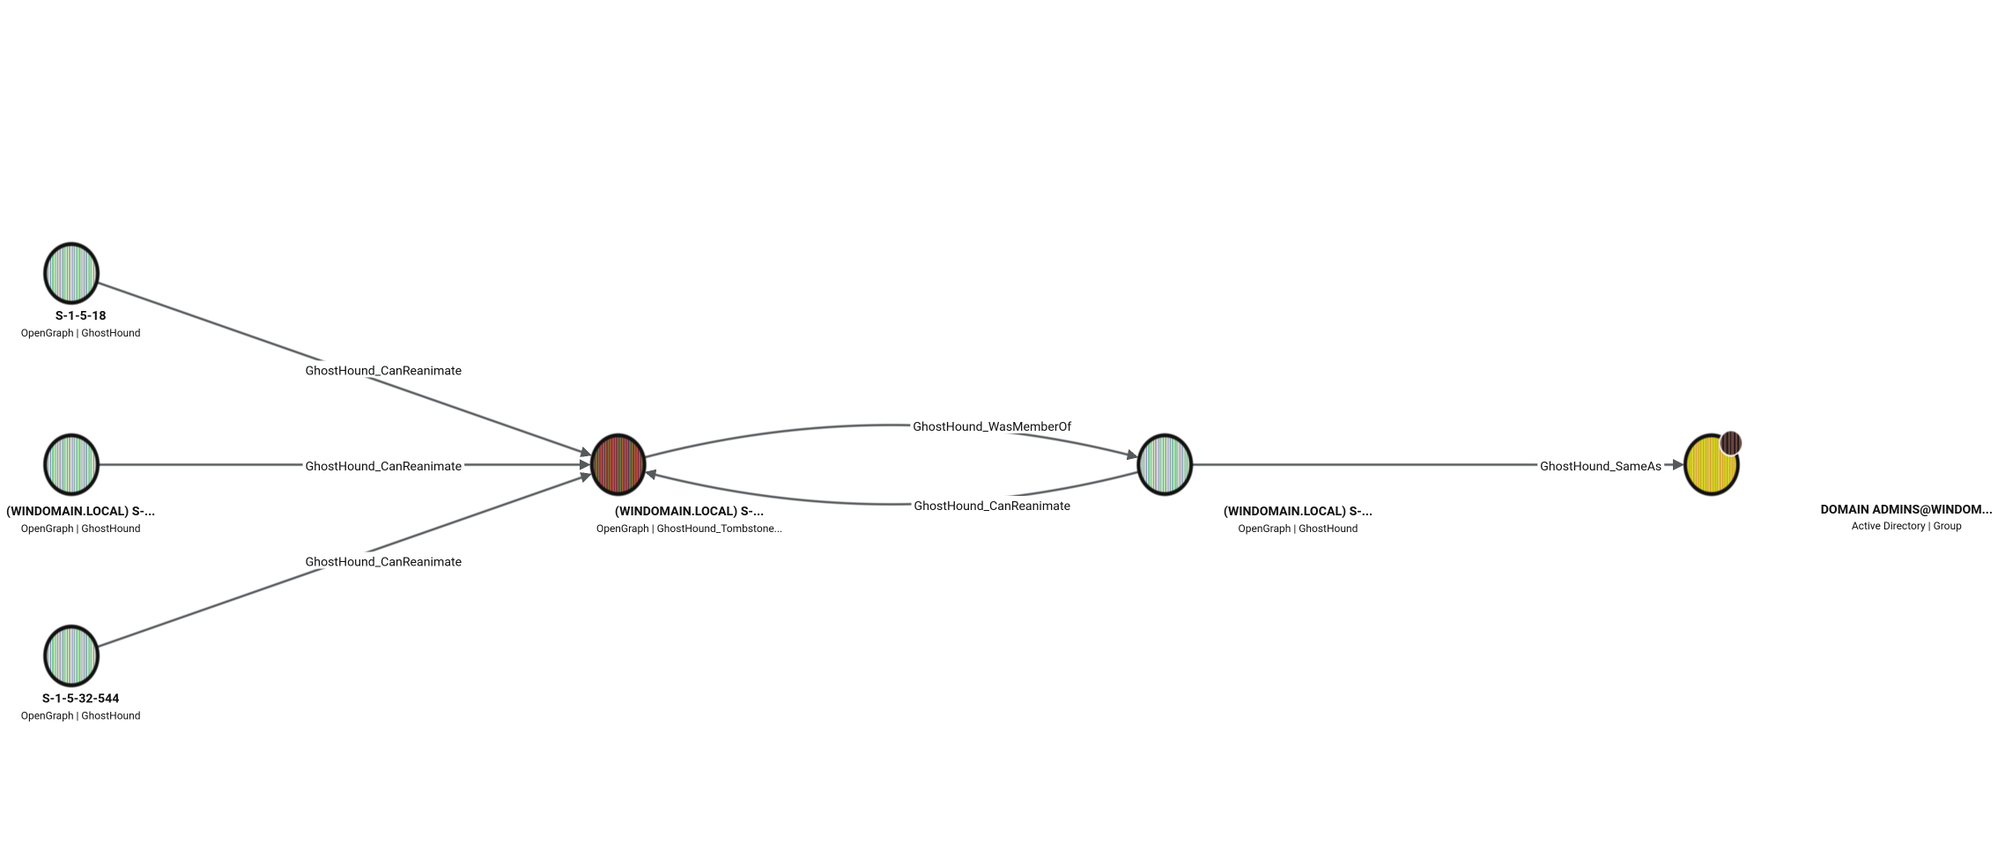 jvbotelho/ghosthound
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…