
CVE-2025-21479-FX5P
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
android-securitybinary-exploitationexploitation+6
3
diyiqiuye/cve-2025-21479-fx5pTemporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
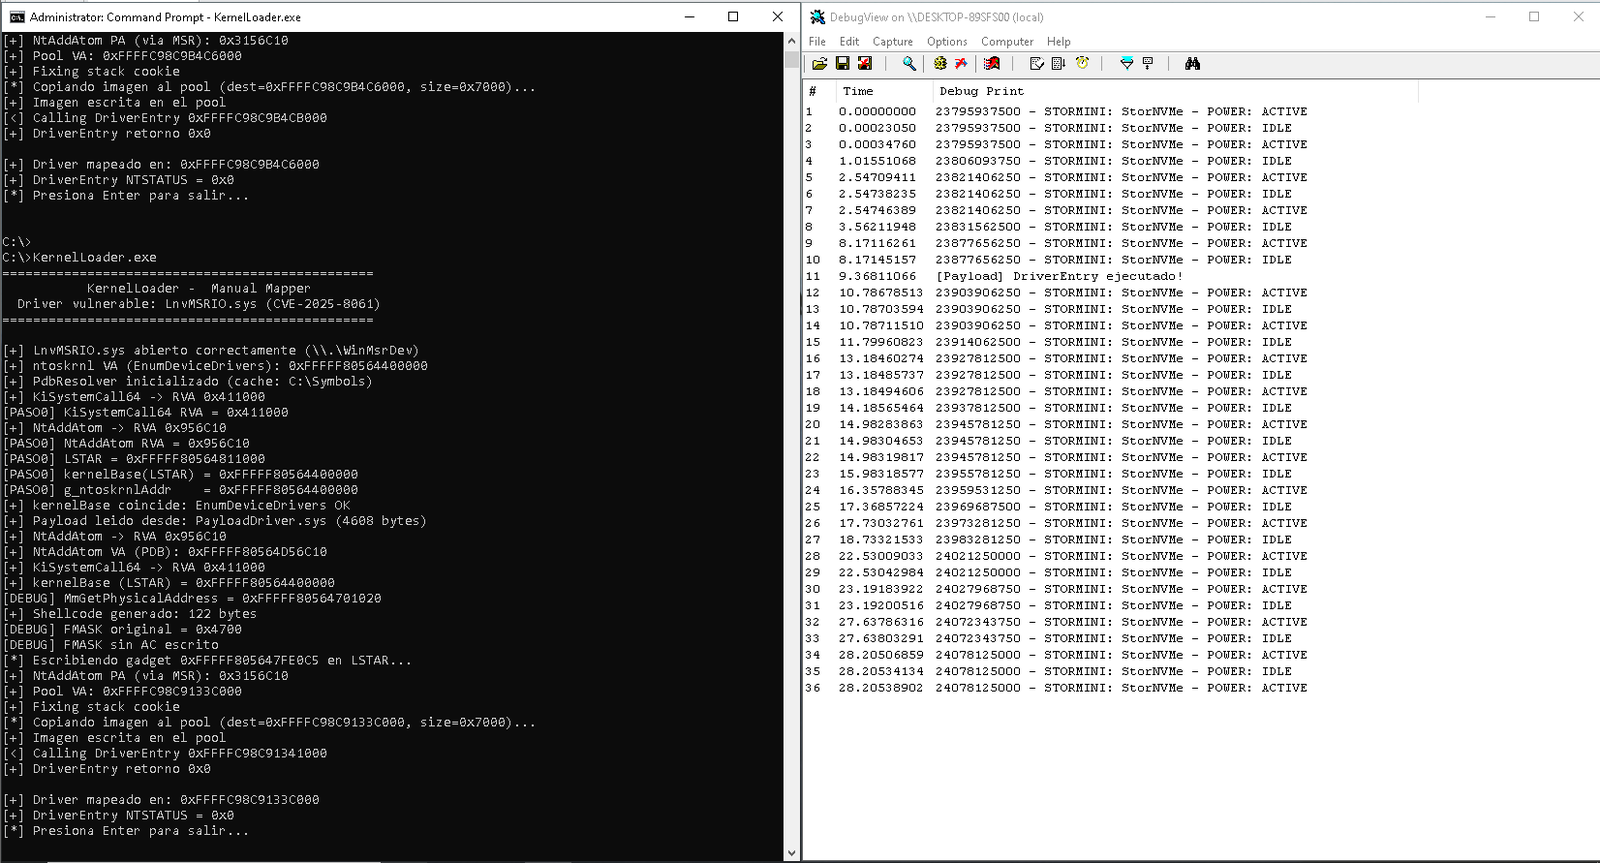 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
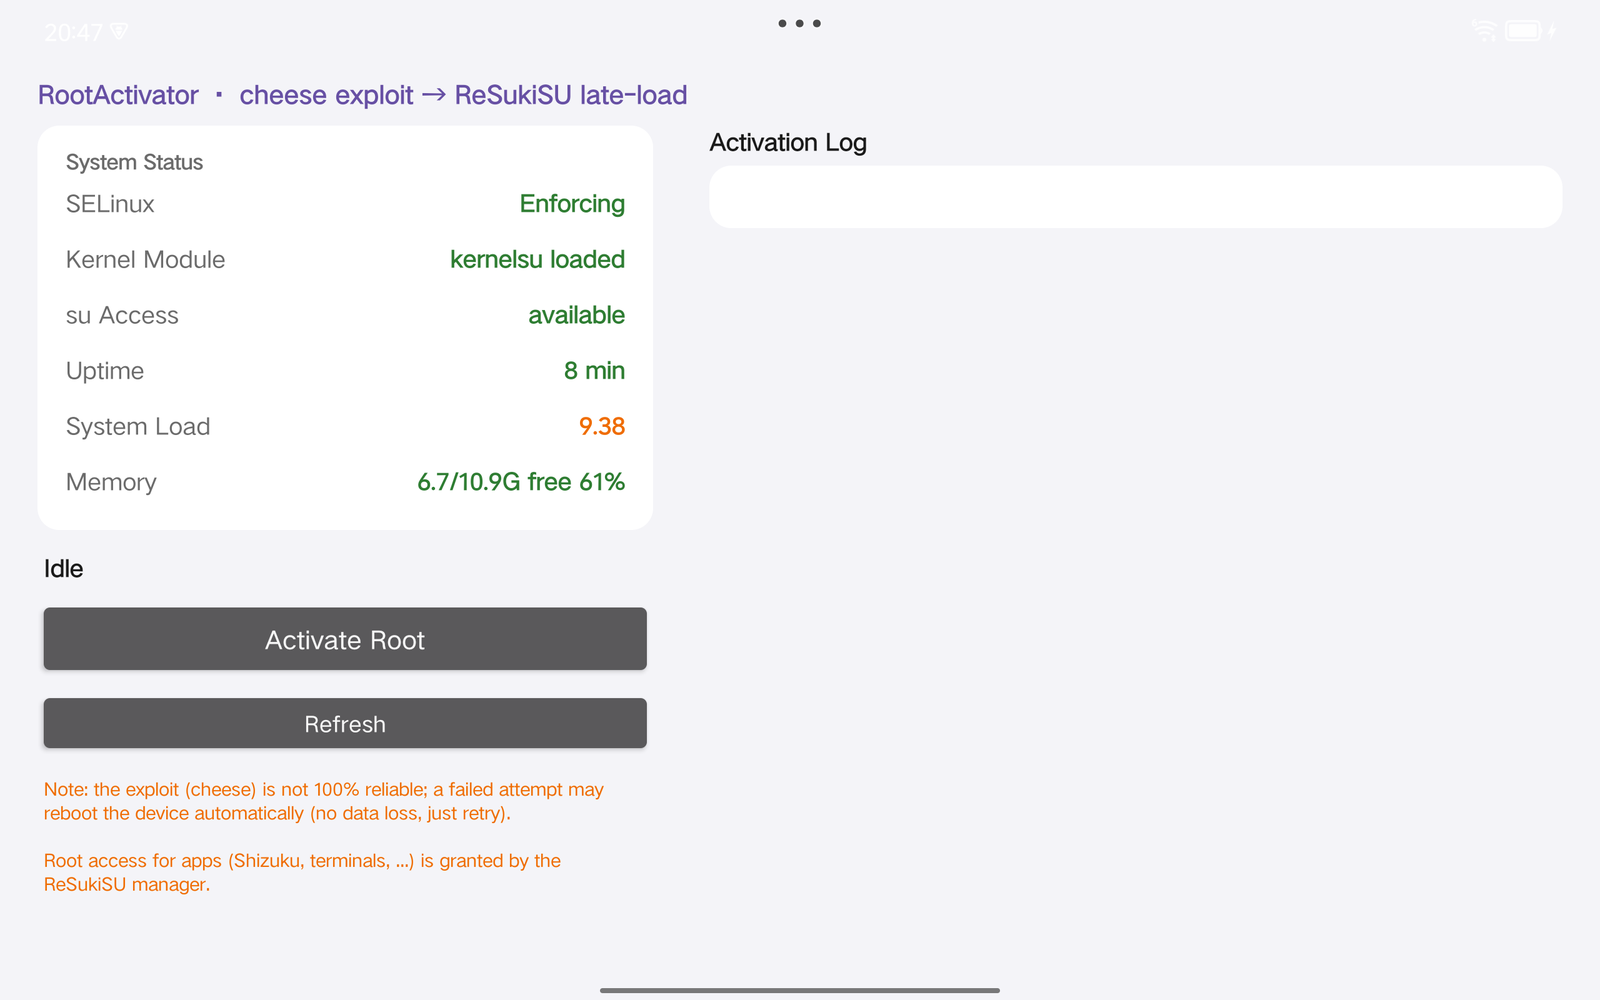 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
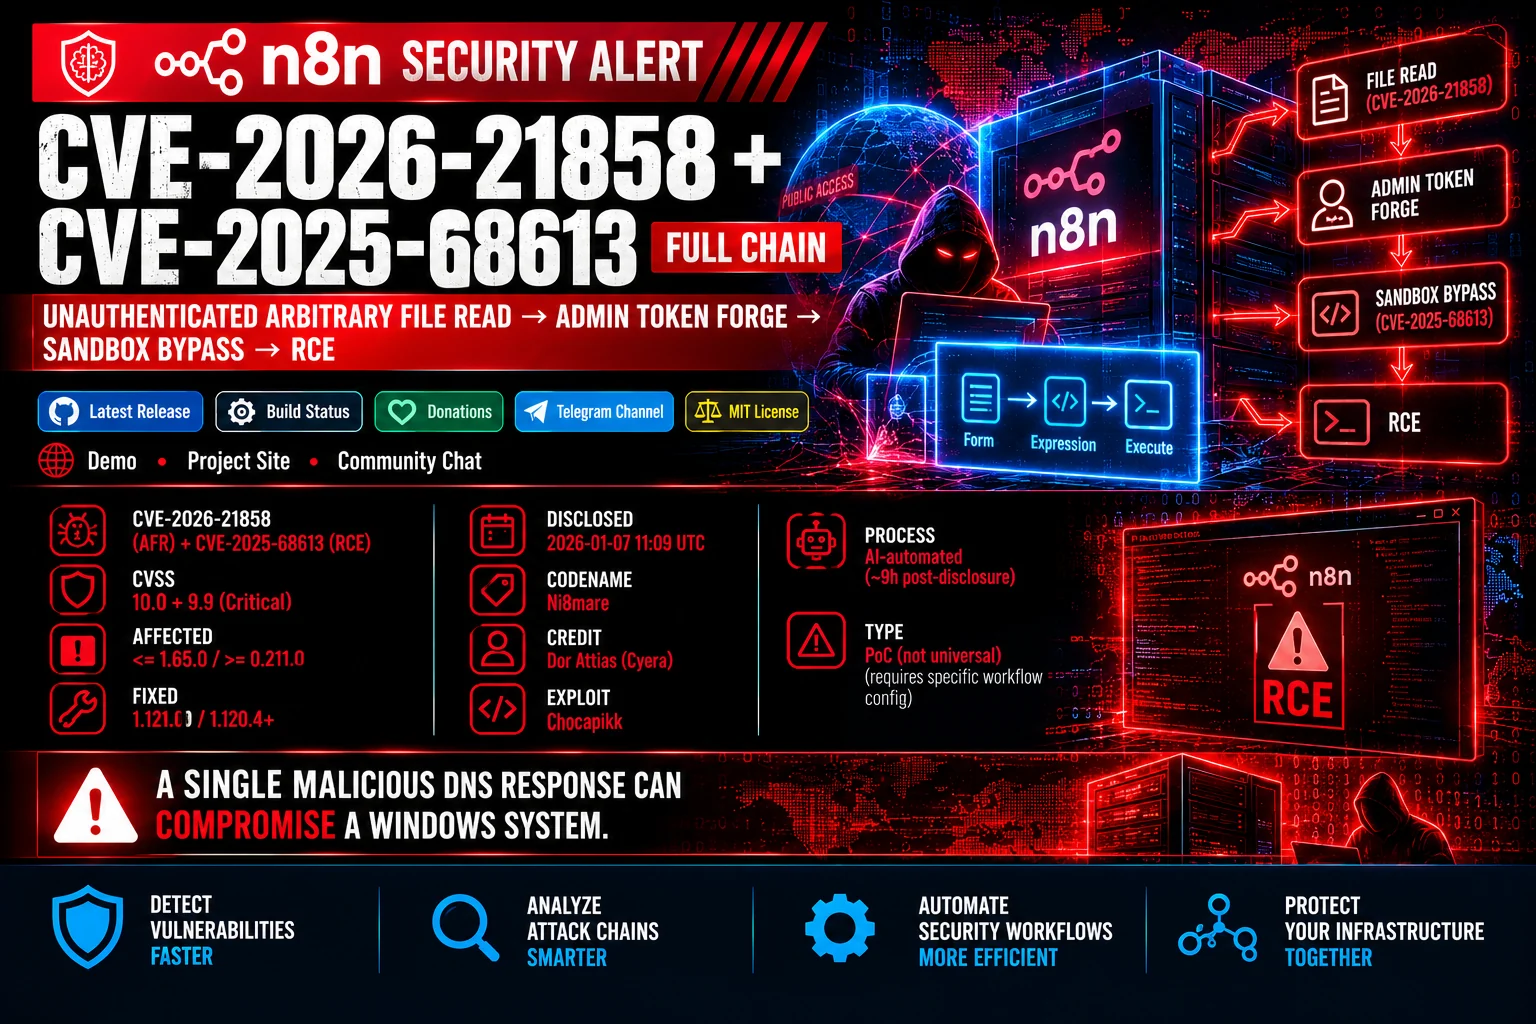 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 cybertechajju/cve-2025-32463
Privilege escalation to root using sudo chroot, NO NEED for gcc installed.
 beleknarcisse169-cmd/cve-2025-26263
Proof-of-concept demonstrating credential disclosure in GeoVision ASManager via memory dumping, enabling unauthorized access and system compromise.
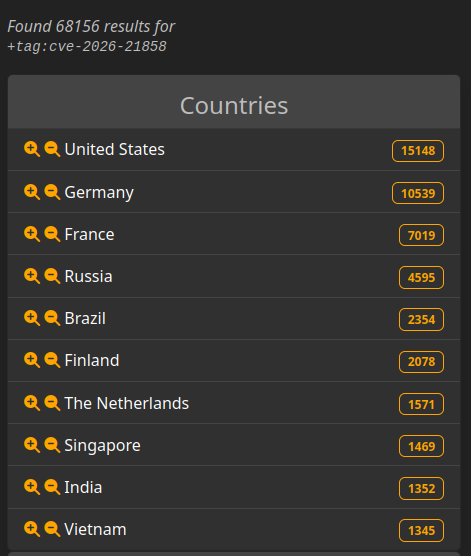 alhakim88/cve-2026-21858
Automated exploit chain for n8n combining arbitrary file read, admin token forgery, and sandbox bypass to achieve unauthenticated remote code…
 linux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
Android kernel root exploit for iQOO Neo9 (CVE-2025-21479, Adreno GPU SDS) providing arbitrary physical write, kernel cap bypass, and root daemon/su…
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 d4m0n/cve-2025-50168-pwn2own-berlin-2025
CVE-2025-50168 Exploit PoC — Pwn2Own Berlin 2025 - LPE(Windows 11) winning bug.
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 oilseller2001/poc-for-cve-2025-9074
Proof-of-Concept exploit for CVE-2025-9074 - Unauthenticated Docker API exposure allowing arbitrary container creation and host filesystem access.
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 mbanyamer/msc-eviltwin-local-privilege-escalation
CVE-2025-26633 (CVSS 7.8) – Zero-day MMC .msc EvilTwin LPE actively exploited by Water Gamayun APT. PoC creates local admin via malicious MSC file on…
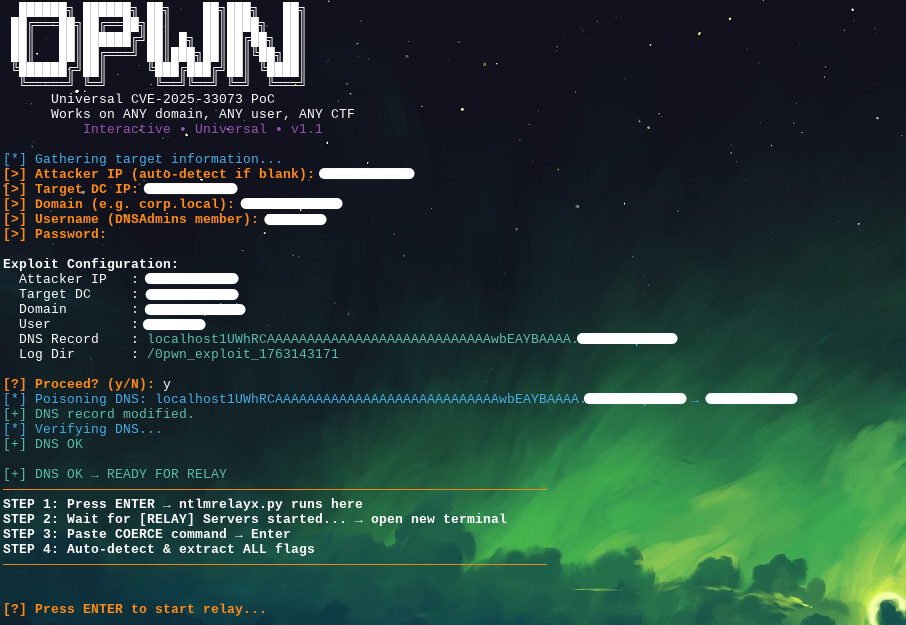 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.