Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…

Offset Independent Credential Extraction Tool

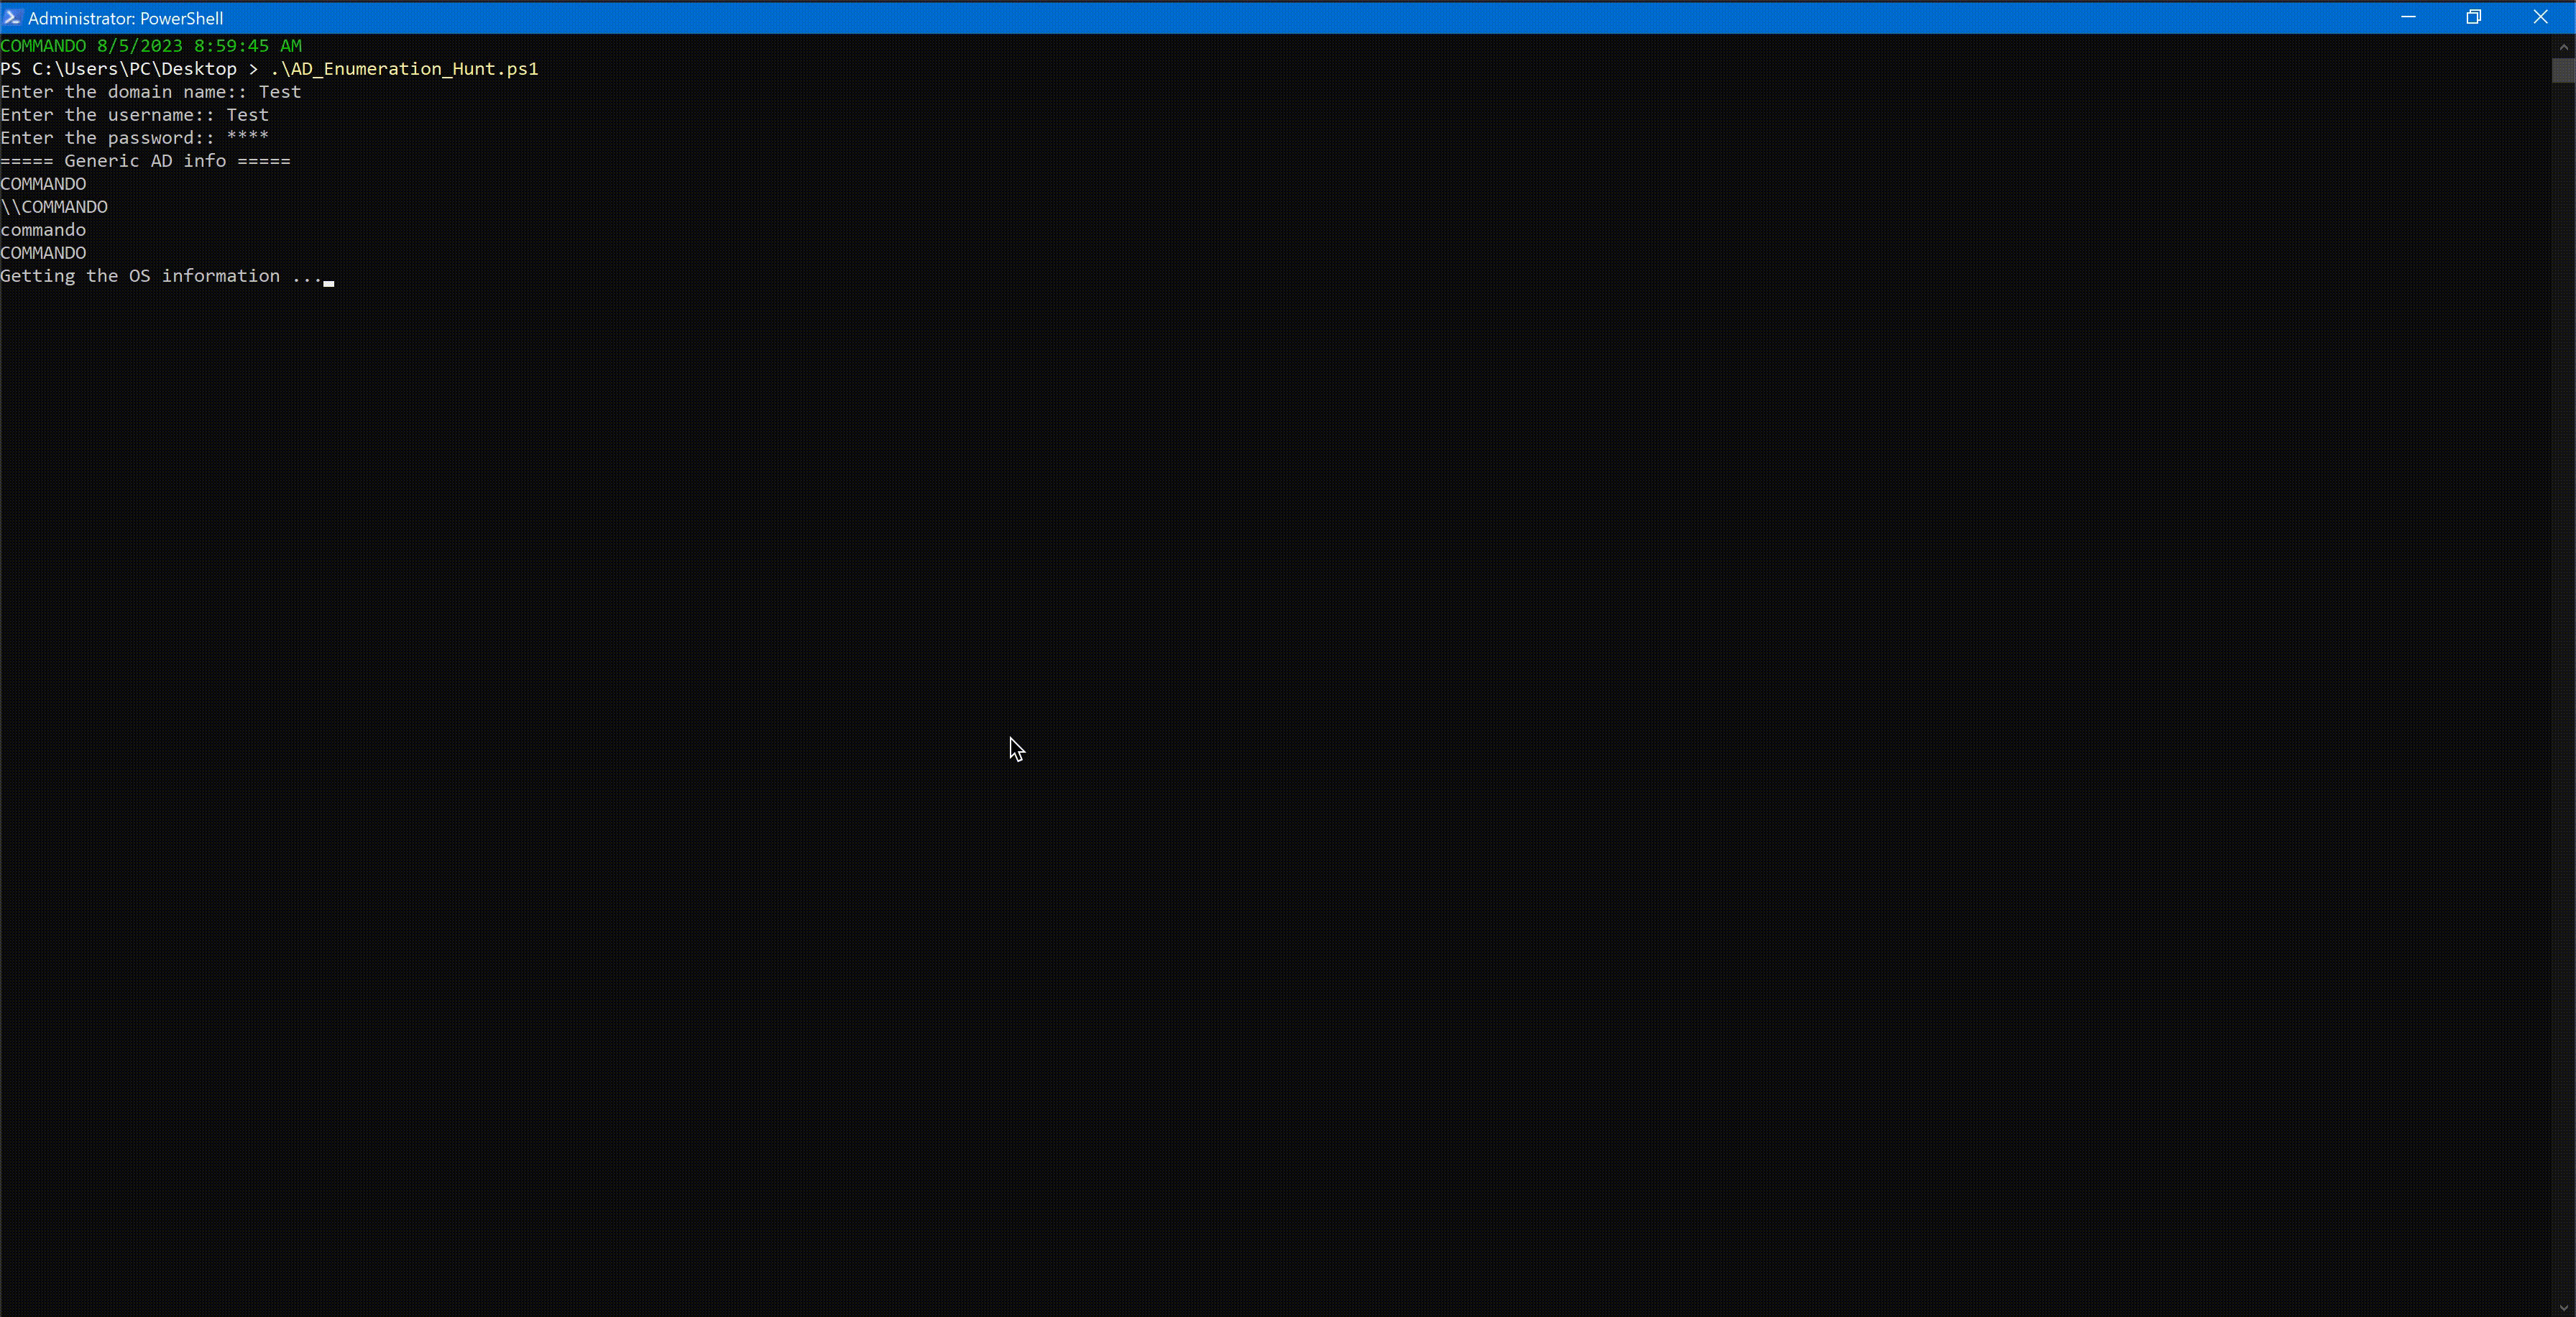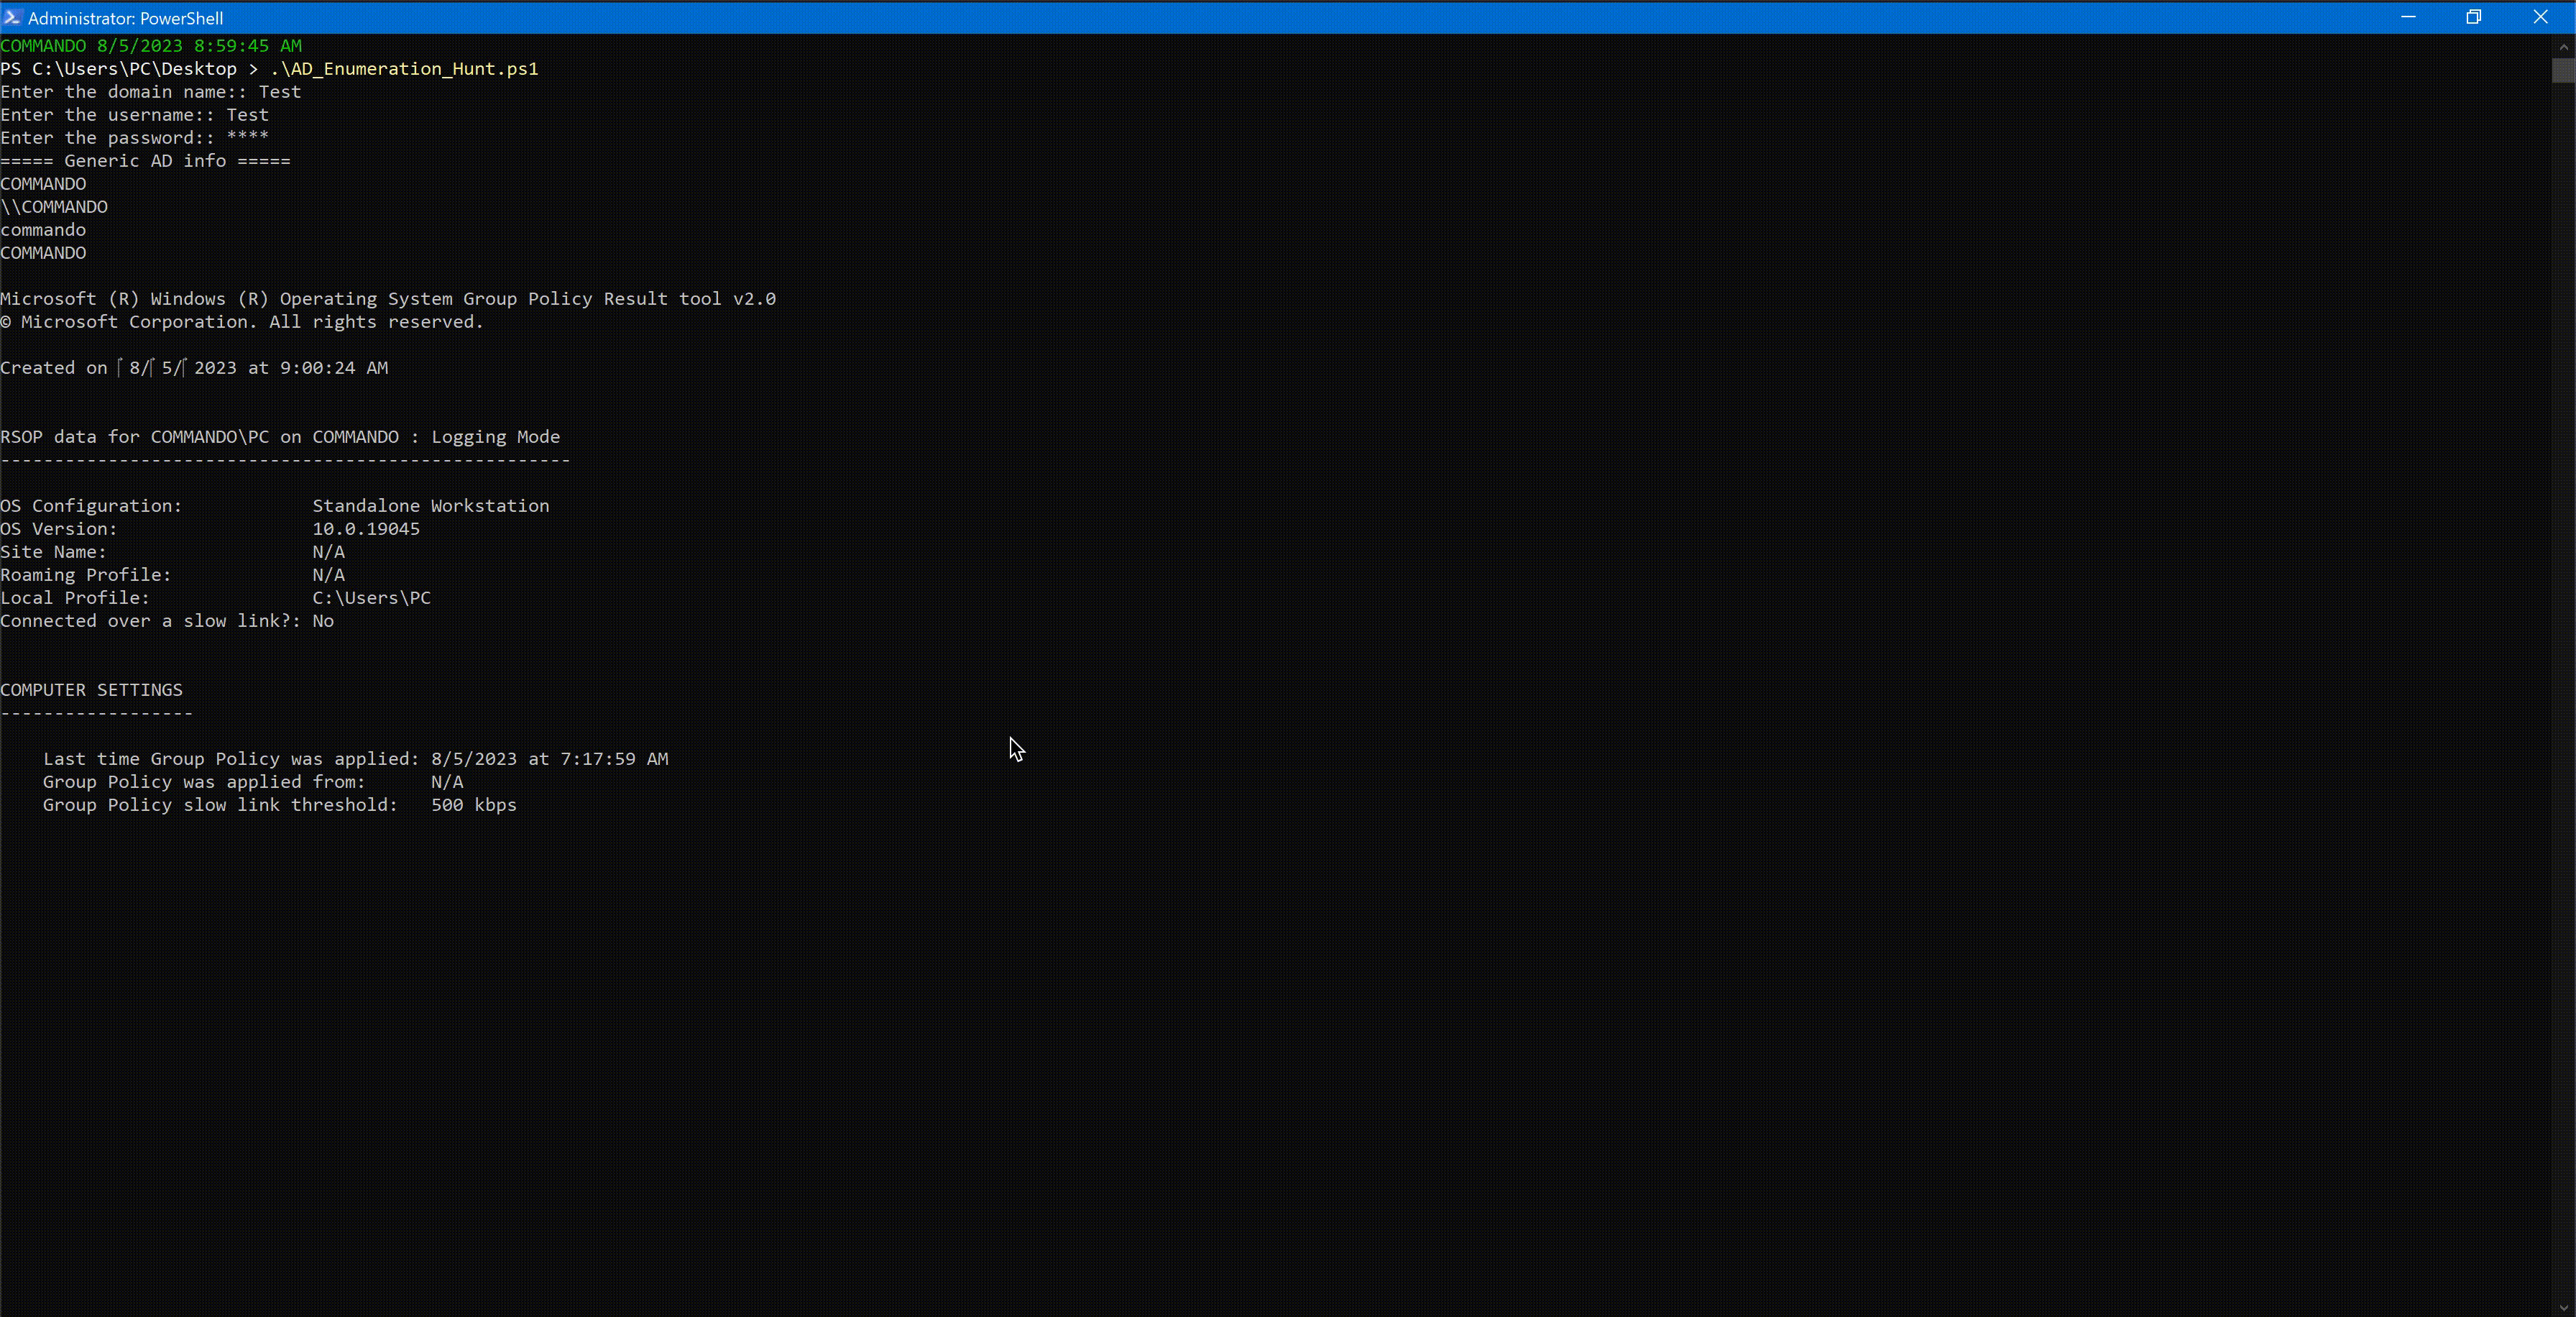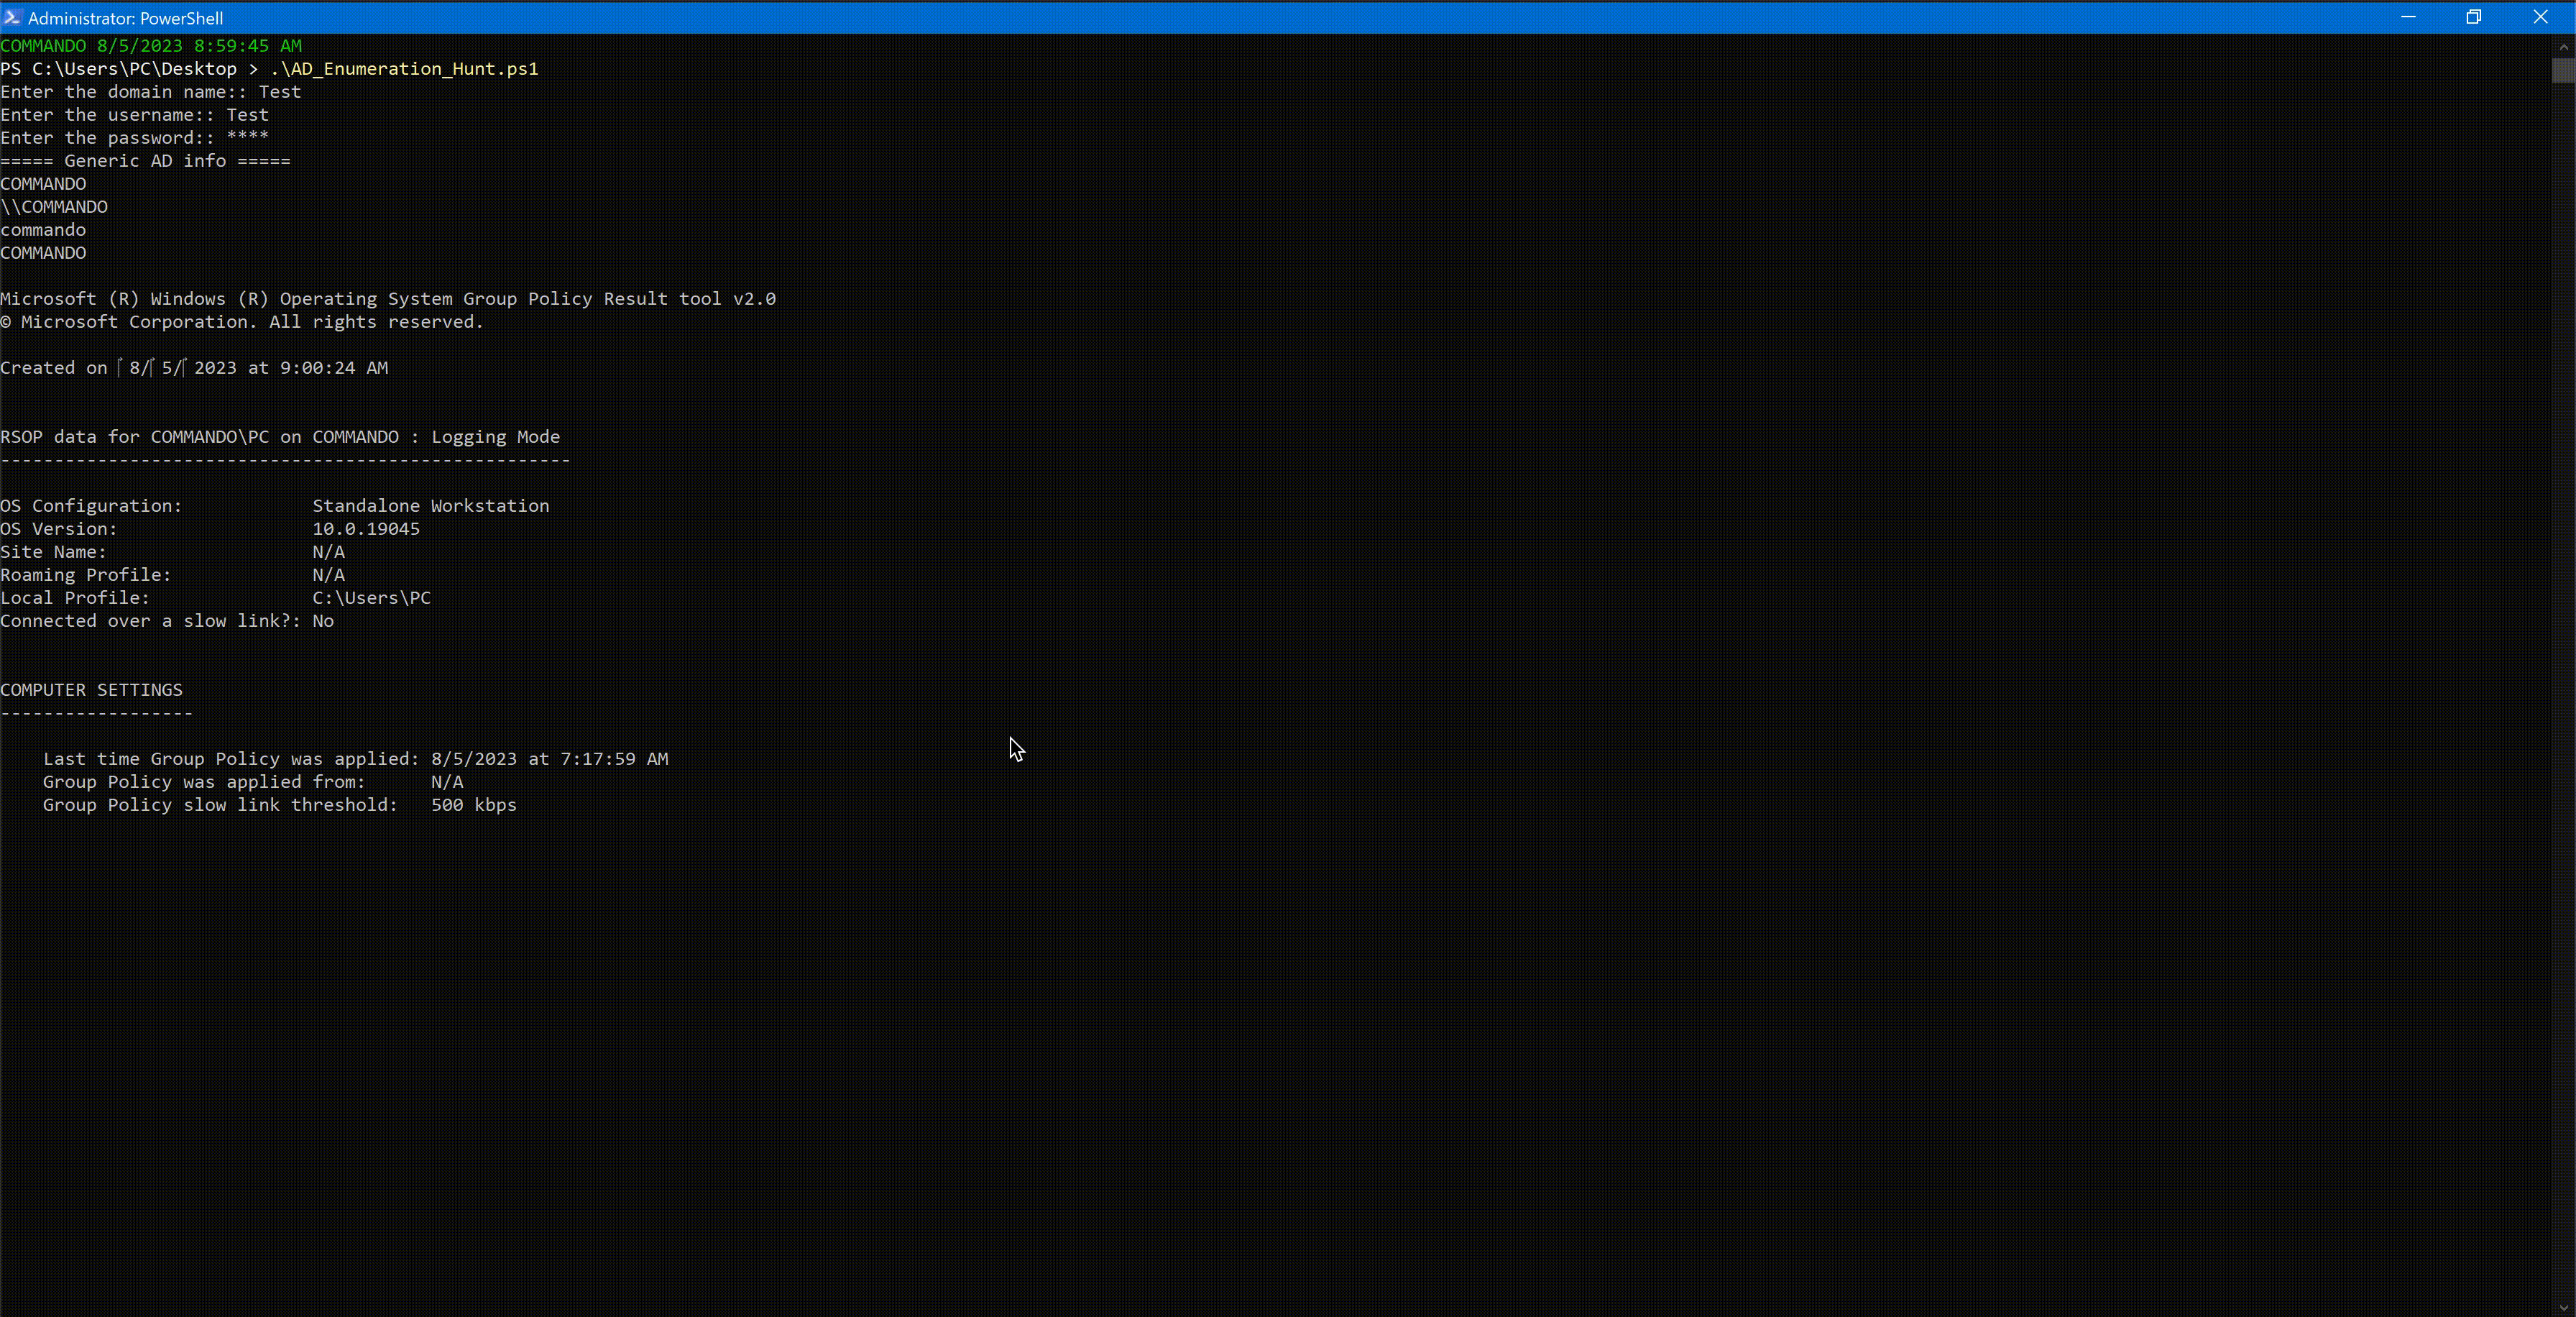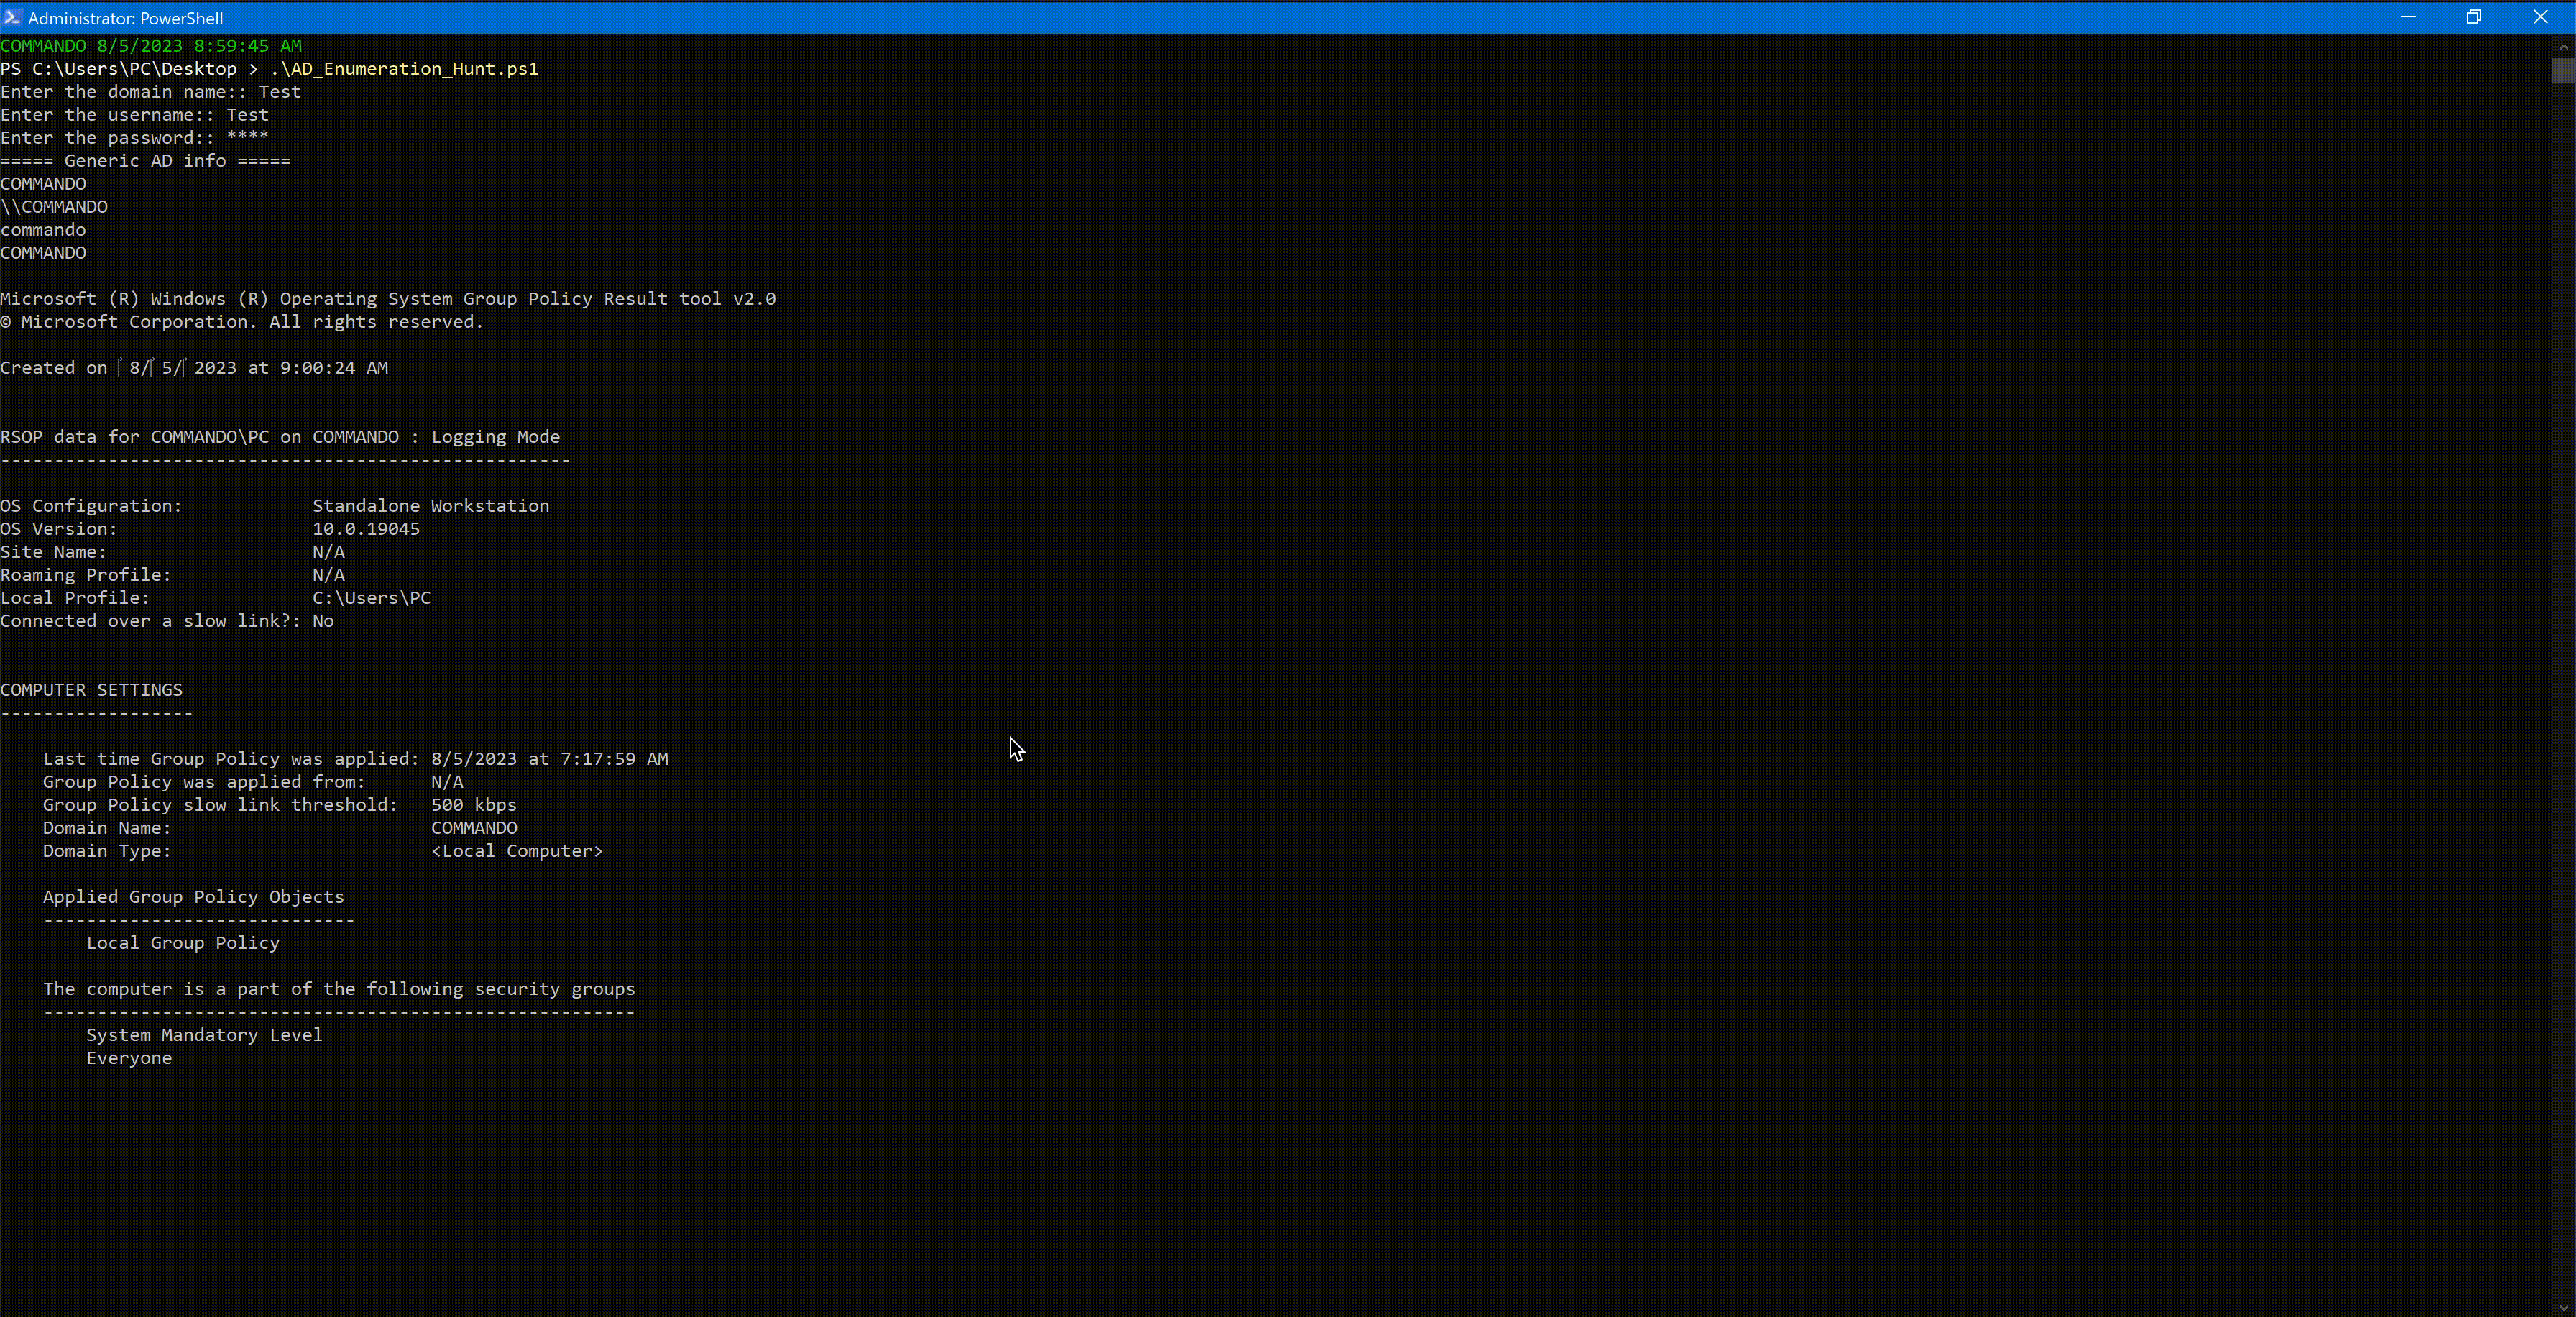
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.

Red Team K8S Adversary Emulation Based on kubectl

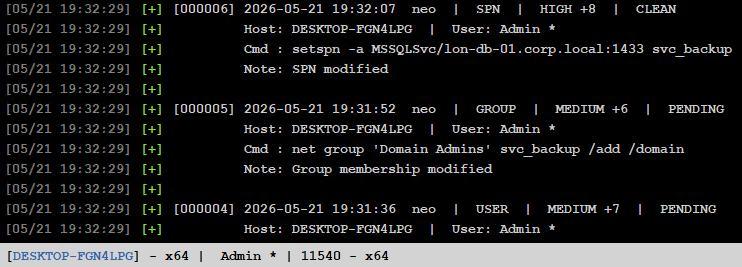
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

A collection of Windows, Linux and MySQL privilege escalation scripts and exploits.

AD CS exploitation related stuff goes here

Tools and Techniques for Red Team / Penetration Testing

Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…

PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.

A collection of scripts for assessing Microsoft Azure security

This repository is a collection of powershell functions every hacker should know

Offensive Lua.

Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…

Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions