
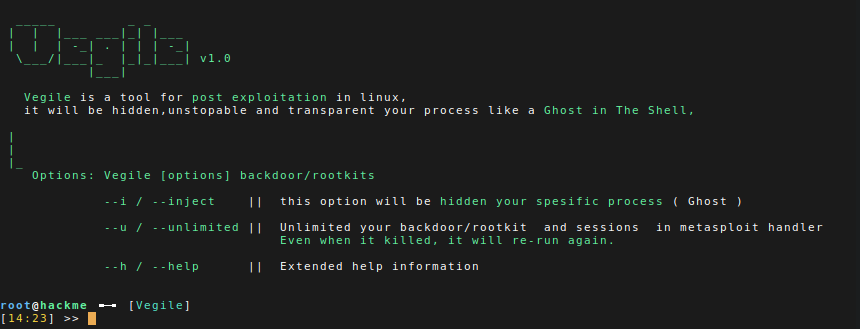
Vegile
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
exploit-frameworkslateral-movementpayload-generation+4
753
screetsec/vegileThis tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 chokepoint/azazel
Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 gmh5225/callmewin32kdriver
Load your driver like win32k.sys
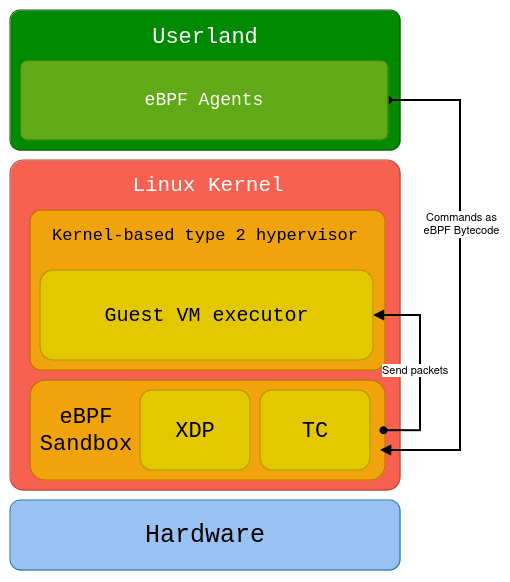 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 xaff-xaff/black-angel-rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.
 xaff-xaff/kernel-process-hollowing
Windows x64 kernel mode rootkit process hollowing POC.
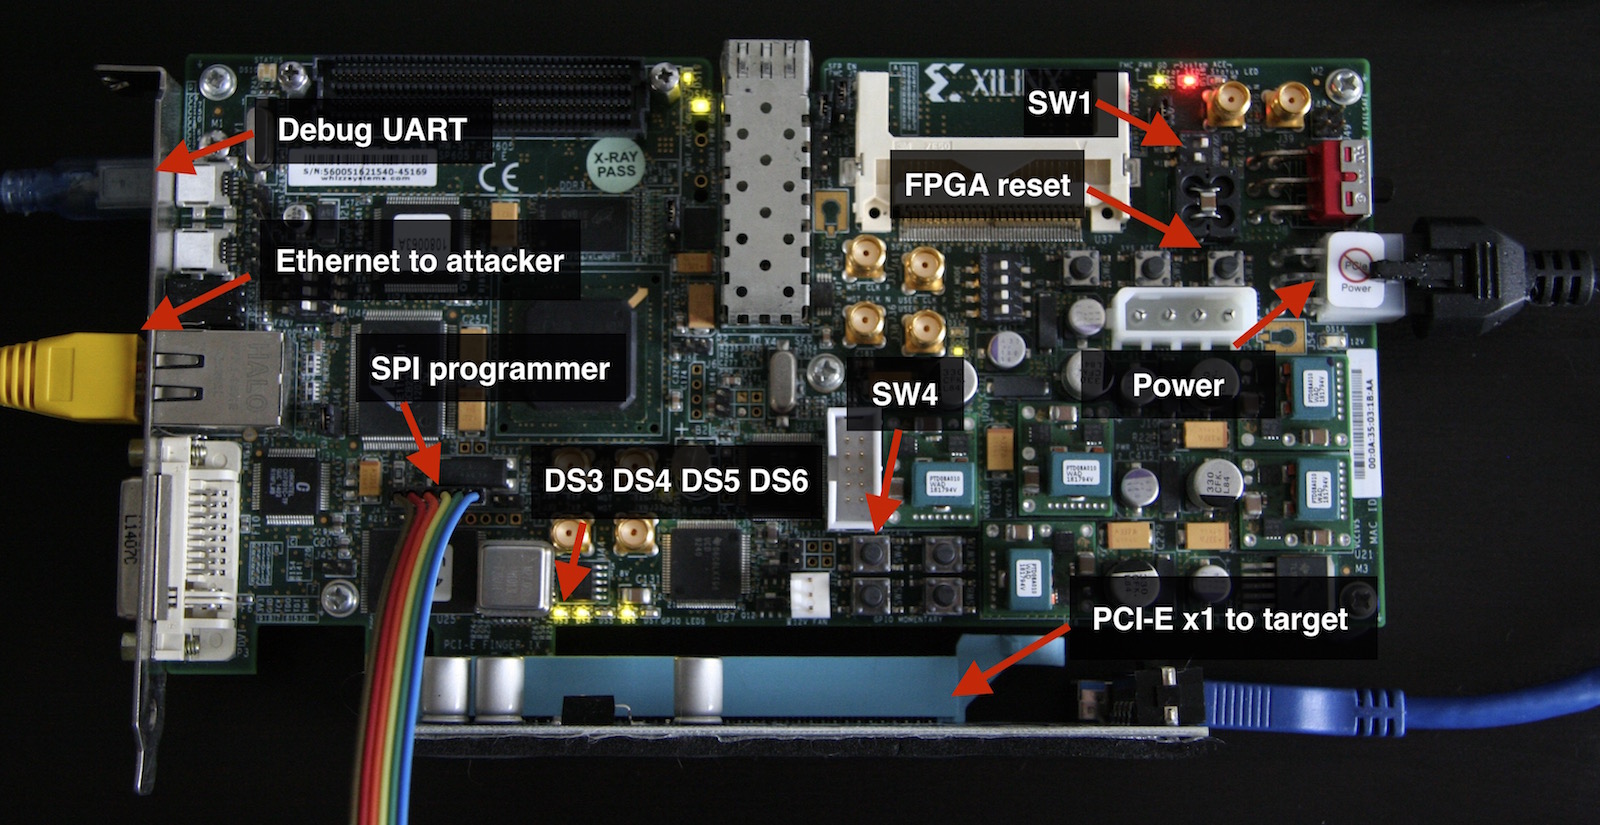 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 diego-tella/codeine
Linux LKM Rootkit
 xaff-xaff/cronos-rootkit
Cronos is Windows 10/11 x64 ring 0 rootkit. Cronos is able to hide processes, protect and elevate them with token manipulation.
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK