

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
81 results
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
evilrdp preview

evilrdp

GitHubskelsec/evilrdp

RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…

command-and-controllateral-movementpenetration-testing+3
3101 year ago
NimSyscallPacker preview

NimSyscallPacker

GitHubs3cur3th1ssh1t/nimsyscallpacker

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

binary-exploitationexploitationlateral-movement+7
22024 days ago
AI-FILE preview

AI-FILE

GitHubkyle41111/ai-file

A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
ai-securitycommand-and-controldata-exfiltration+7
133 days ago
MoveEdr preview

MoveEdr

GitHubduhirsch/moveedr

Permanently disable EDRs as local admin

anti-botdefensive-toolsids-ips-evasion+5
1329 months ago
Rusty-Playground preview

Rusty-Playground

GitHubblacksnufkin/rusty-playground

Some Rust program I wrote while learning Malware Development

binary-analysisexploitationmalware-analysis+6
1621 year ago
silph preview

silph

GitHubalmounah/silph

Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall

authenticationmemory-forensicspassword-cracking+3
1679 months ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
CS-Remote-OPs-BOF preview

CS-Remote-OPs-BOF

GitHubtrustedsec/cs-remote-ops-bof

Remote operations commands implemented using Beacon Object Files
authenticationencryption-decryption-toolslateral-movement+6
1.2k11 days ago
PrivKit preview

PrivKit

GitHubmertdas/privkit

PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.

binary-analysisexploitationpenetration-testing+4
6278 months ago
Stitch preview

Stitch

GitHubnathanlopez/stitch

Python Remote Administration Tool (RAT)

educationpassword-crackingpayload-generation+2
3.7k9 years ago
TrickDump preview

TrickDump

GitHubricardojoserf/trickdump

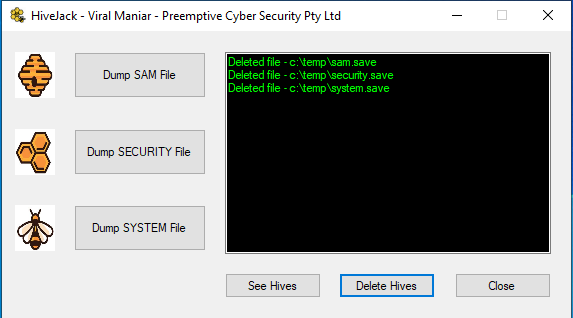
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
memory-forensicspost-exploitationred-teaming
6081 month ago
HiveJack preview

HiveJack

GitHubviralmaniar/hivejack

This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
lateral-movementpenetration-testingpost-exploitation
1126 years ago
CVE-2026-41091-PoC-Exploit preview

CVE-2026-41091-PoC-Exploit

GitHubtc4dy/cve-2026-41091-poc-exploit

CVE-2026-41091 RedSun | Microsoft Defender LPE exploit. Low-privileged users gain NT AUTHORITY\SYSTEM 🔥 via Cloud Files API + NTFS junction…
binary-exploitationeducationexploitation+4
46 days ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

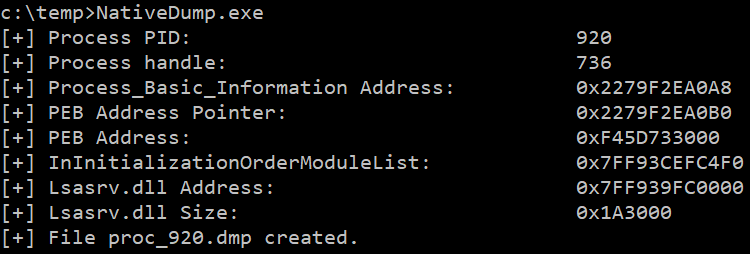
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
memory-forensicspost-exploitationred-teaming
7491 month ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
command-and-controldata-exfiltrationeducation+8
1758 months ago
PyADRecon preview

PyADRecon

GitHubl4rm4nd/pyadrecon

Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…

authenticationinformation-gatheringpenetration-testing+4
682 months ago
Previous12345Next