
edu-recon
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
educationexploitationinformation-gathering+8
yeee3642/edu-reconAuthorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
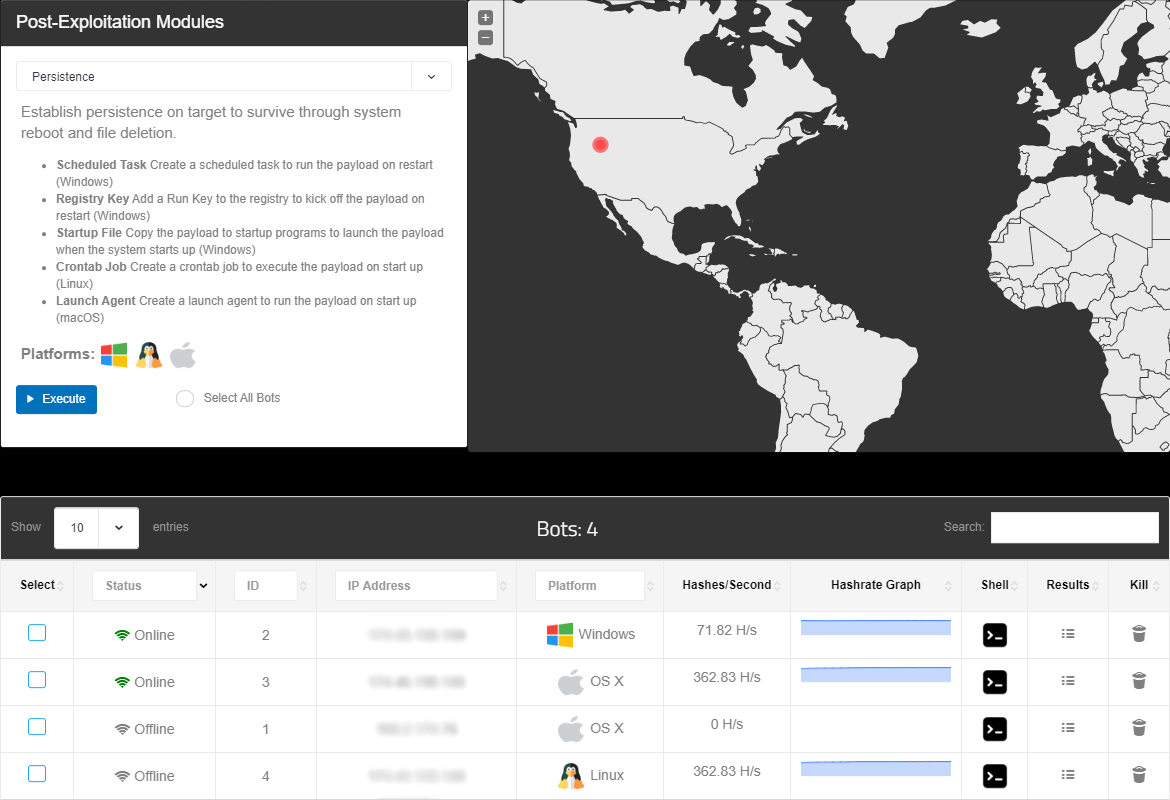 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
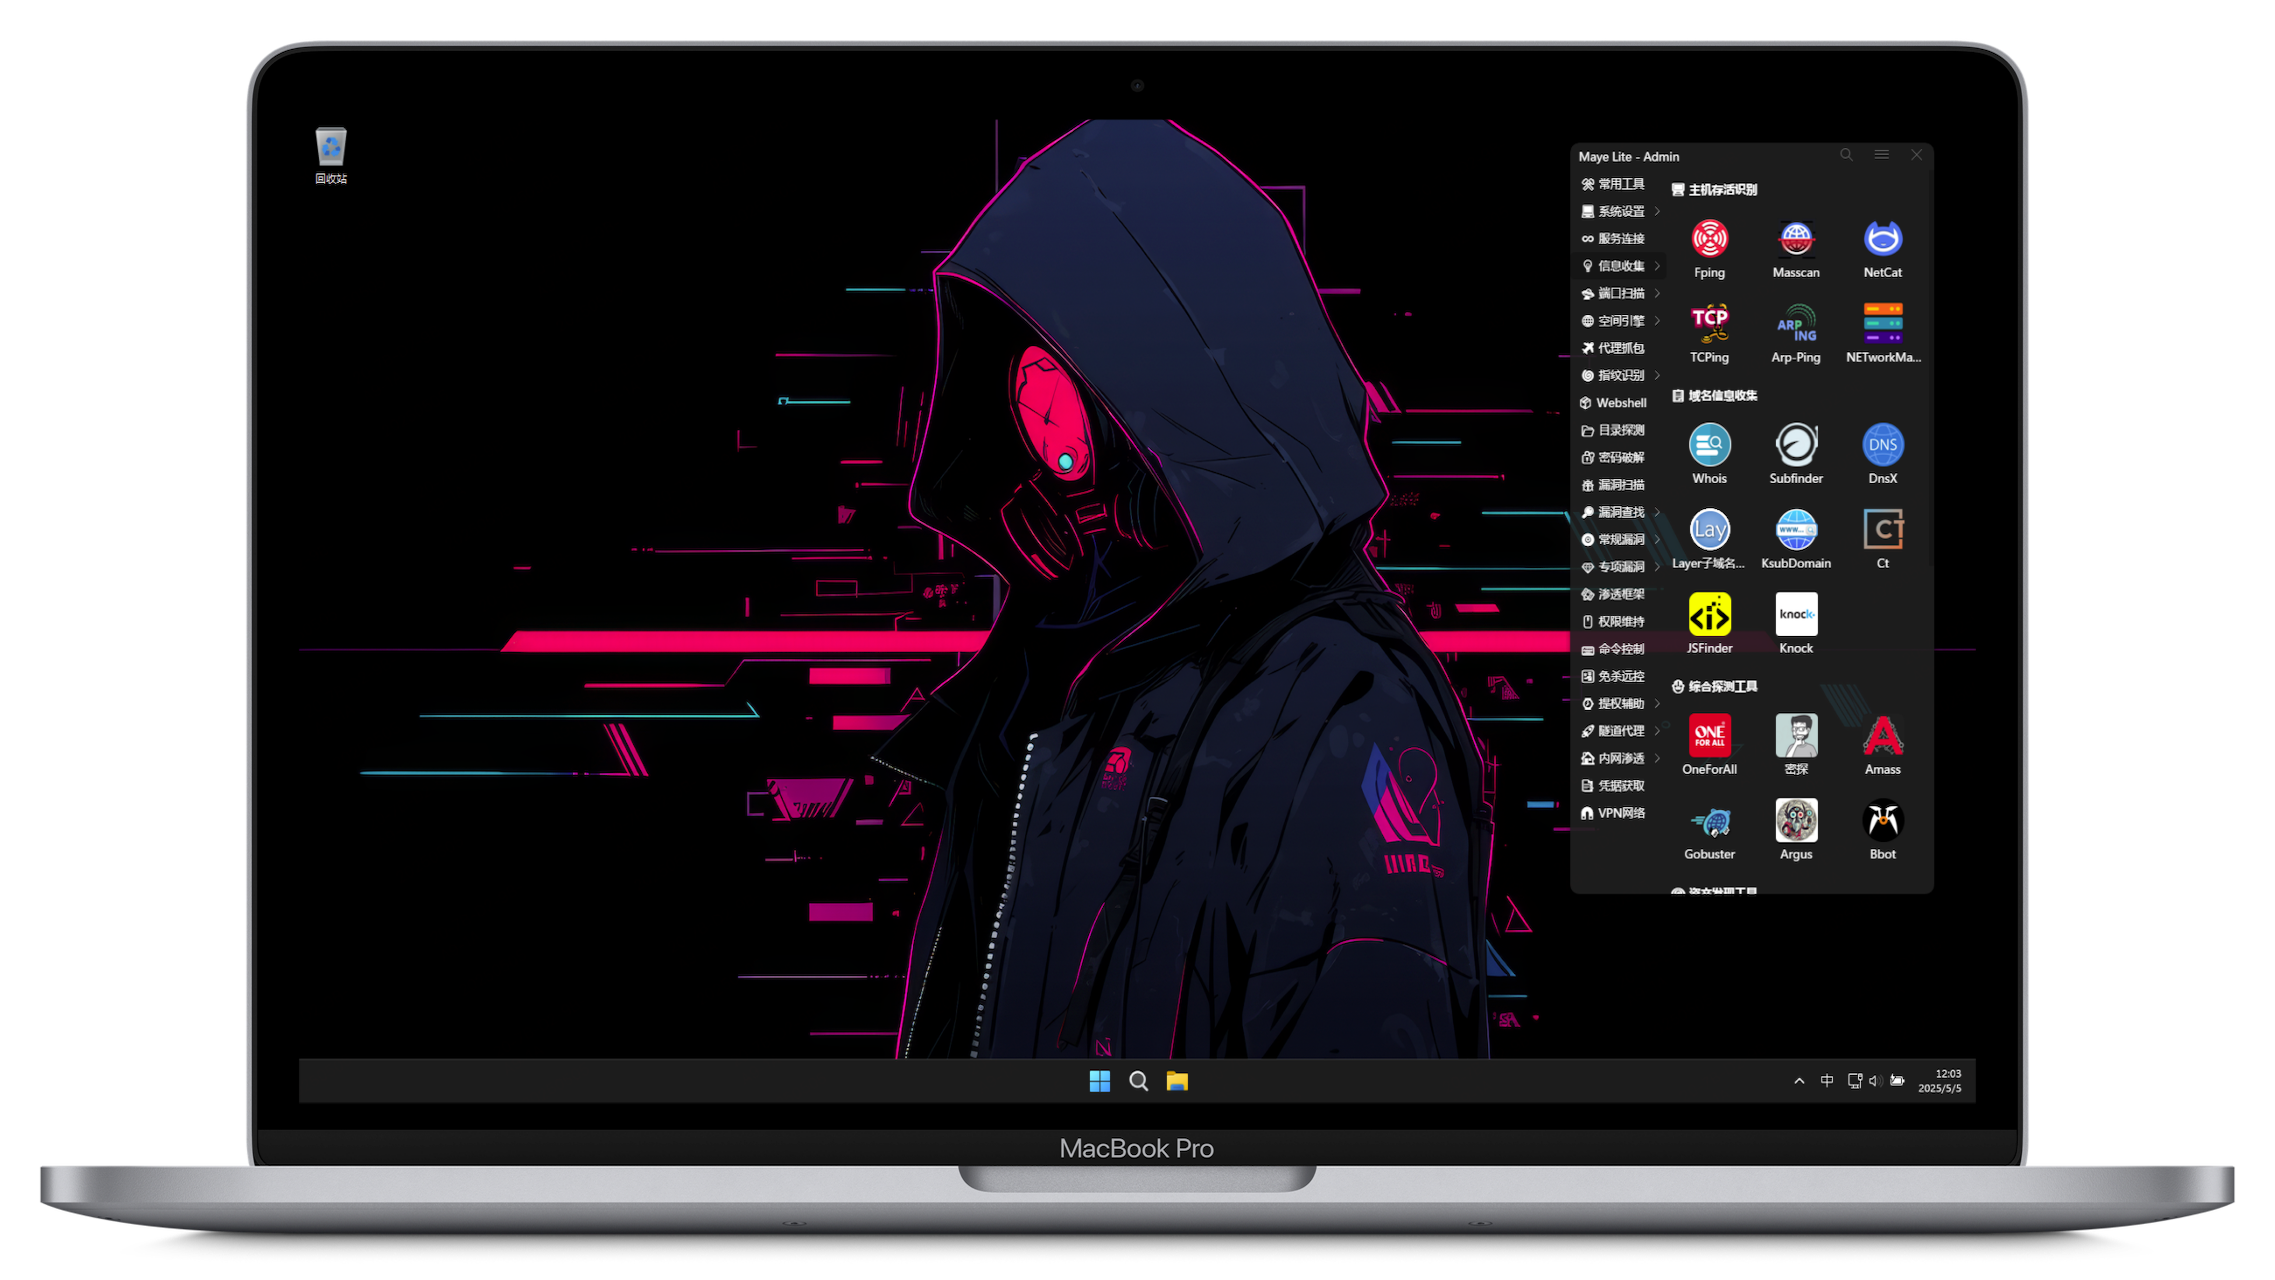 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 alechilczenko/kimi
Attack Surface Discovery tool built on a microservice approach, utilizing multi-threading for fast, internet-scale asset indexing
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
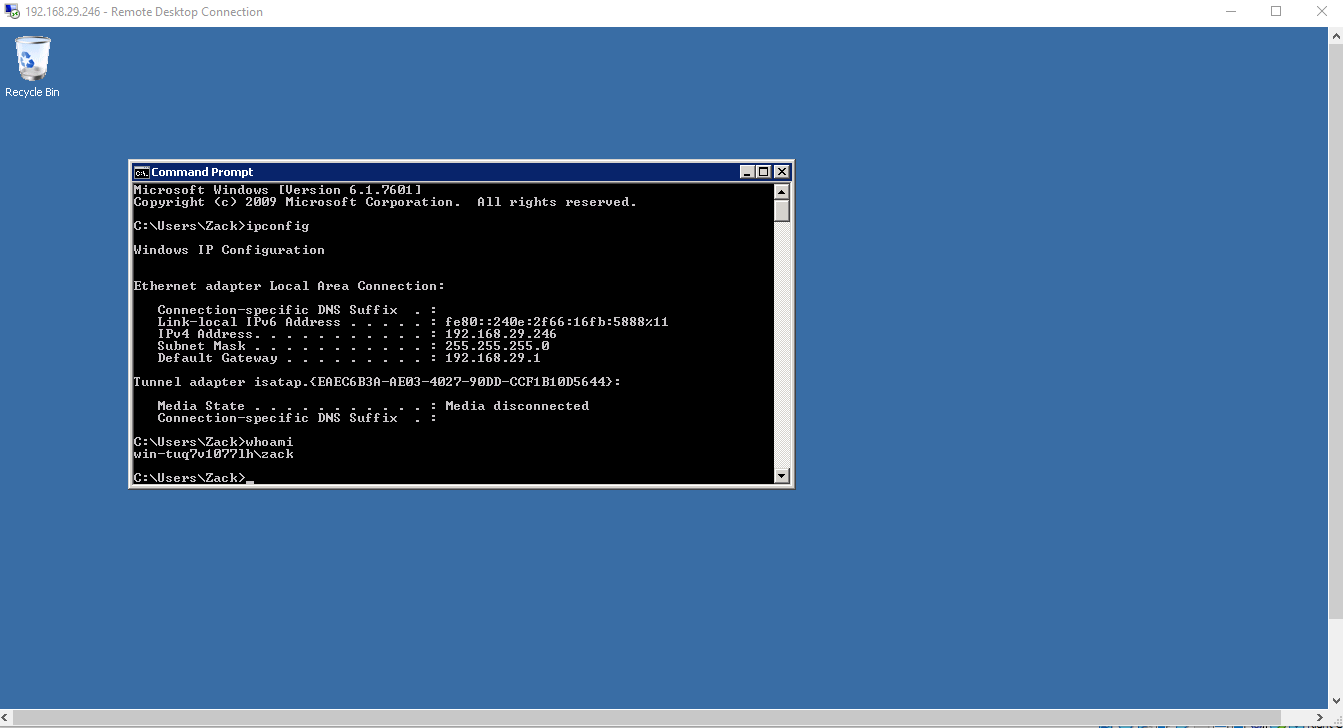 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
 nu11secur1ty/nmap-cheat-sheet
Curated cheat sheet for Nmap, covering target selection, port scanning, service/OS detection, NSE scripts, and output formats for network…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 farinap5/a-xex
This project is part of a school work focusing on network security.
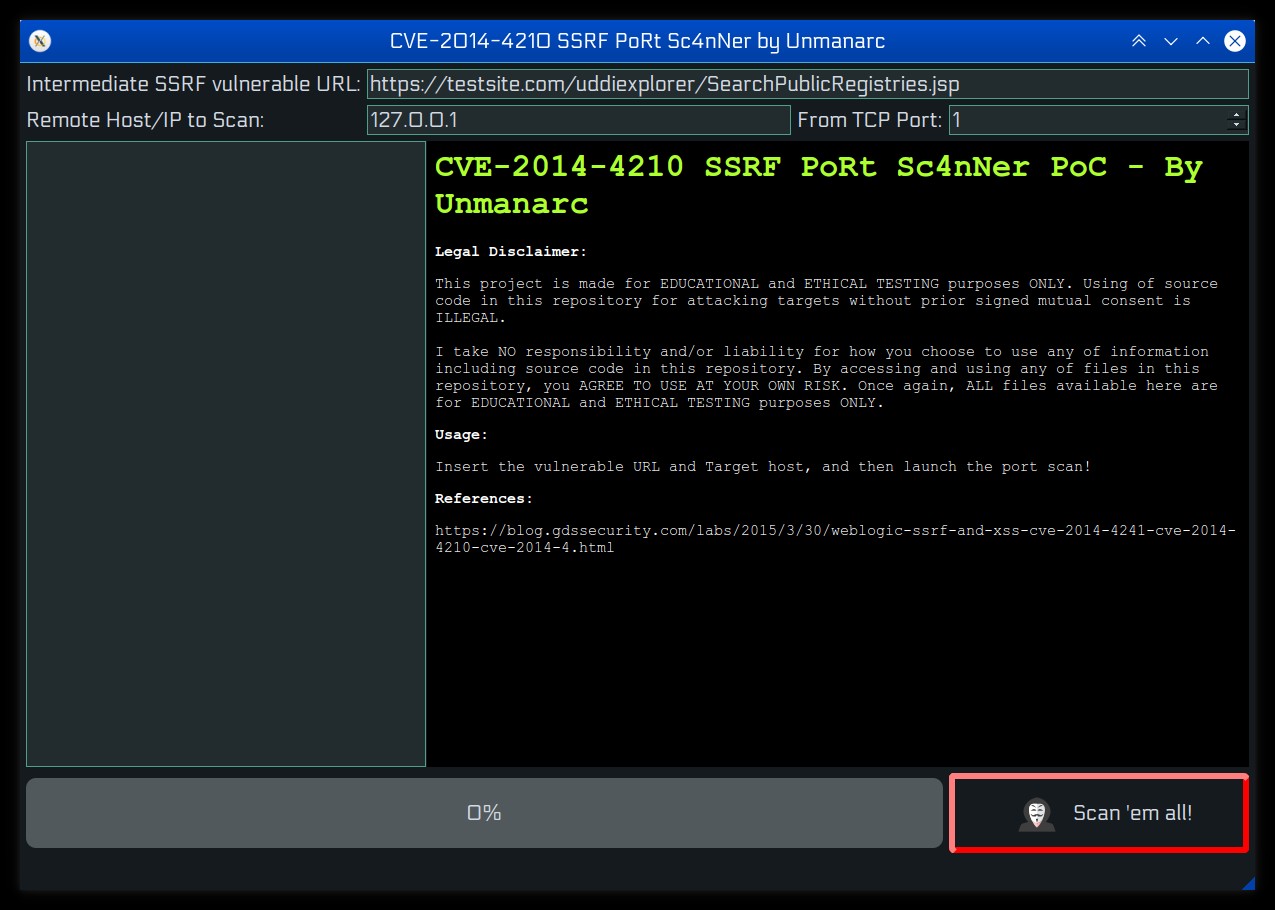 unmanarc/cve-2014-4210-ssrf-portscanner-poc
CVE-2014-4210 SSRF PORTSCANNER PoC
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 mngunibanda1-prog/jozini-network-scanner
Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.