

peeko
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
command-and-controldata-exfiltrationinformation-gathering+7
2331 year ago
b3rito/peekopeeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 mttaggart/offensivenotion
Notion as a platform for offensive operations
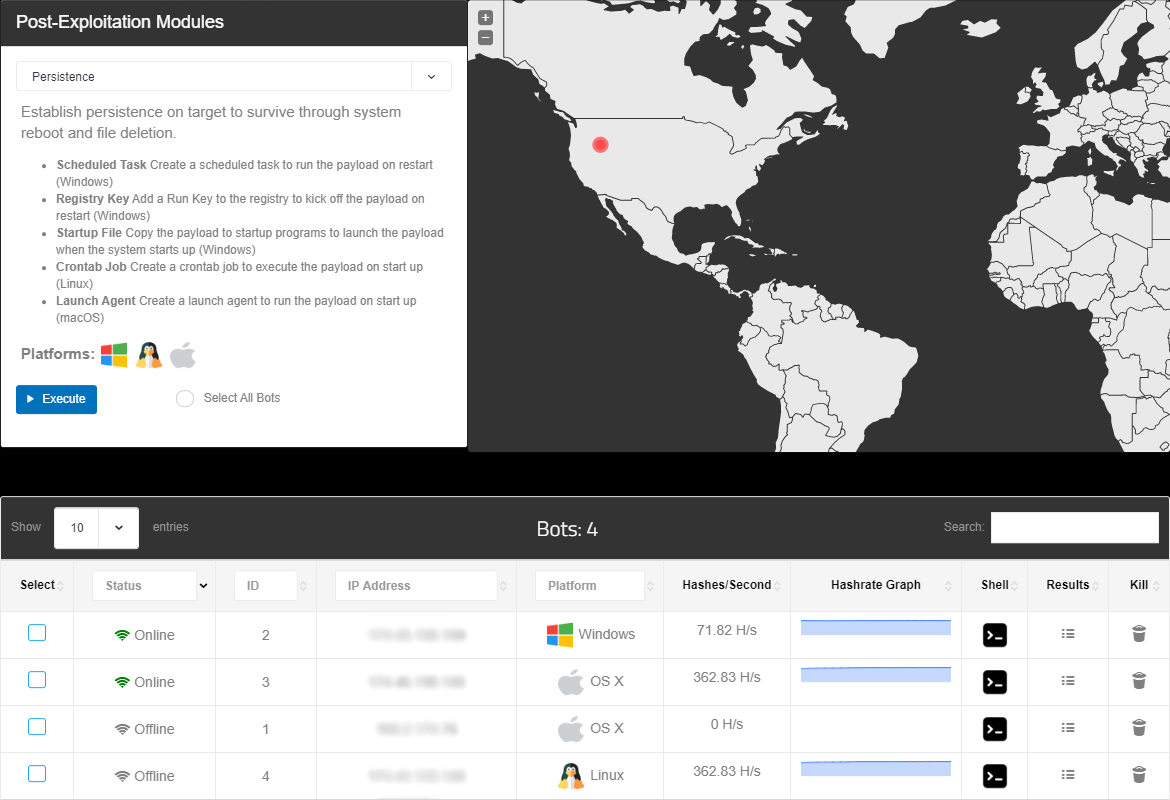 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 besimorhino/powercat
netshell features all in version 2 powershell
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs

 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 cyberdudebivash/cyberdudebivash-fortisiem-cve-2025-64155-scanner
Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…