

FinalRecon
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
crawlerdns-analysisinformation-gathering+7
2.9k
thewhiteh4t/finalreconAutomated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…

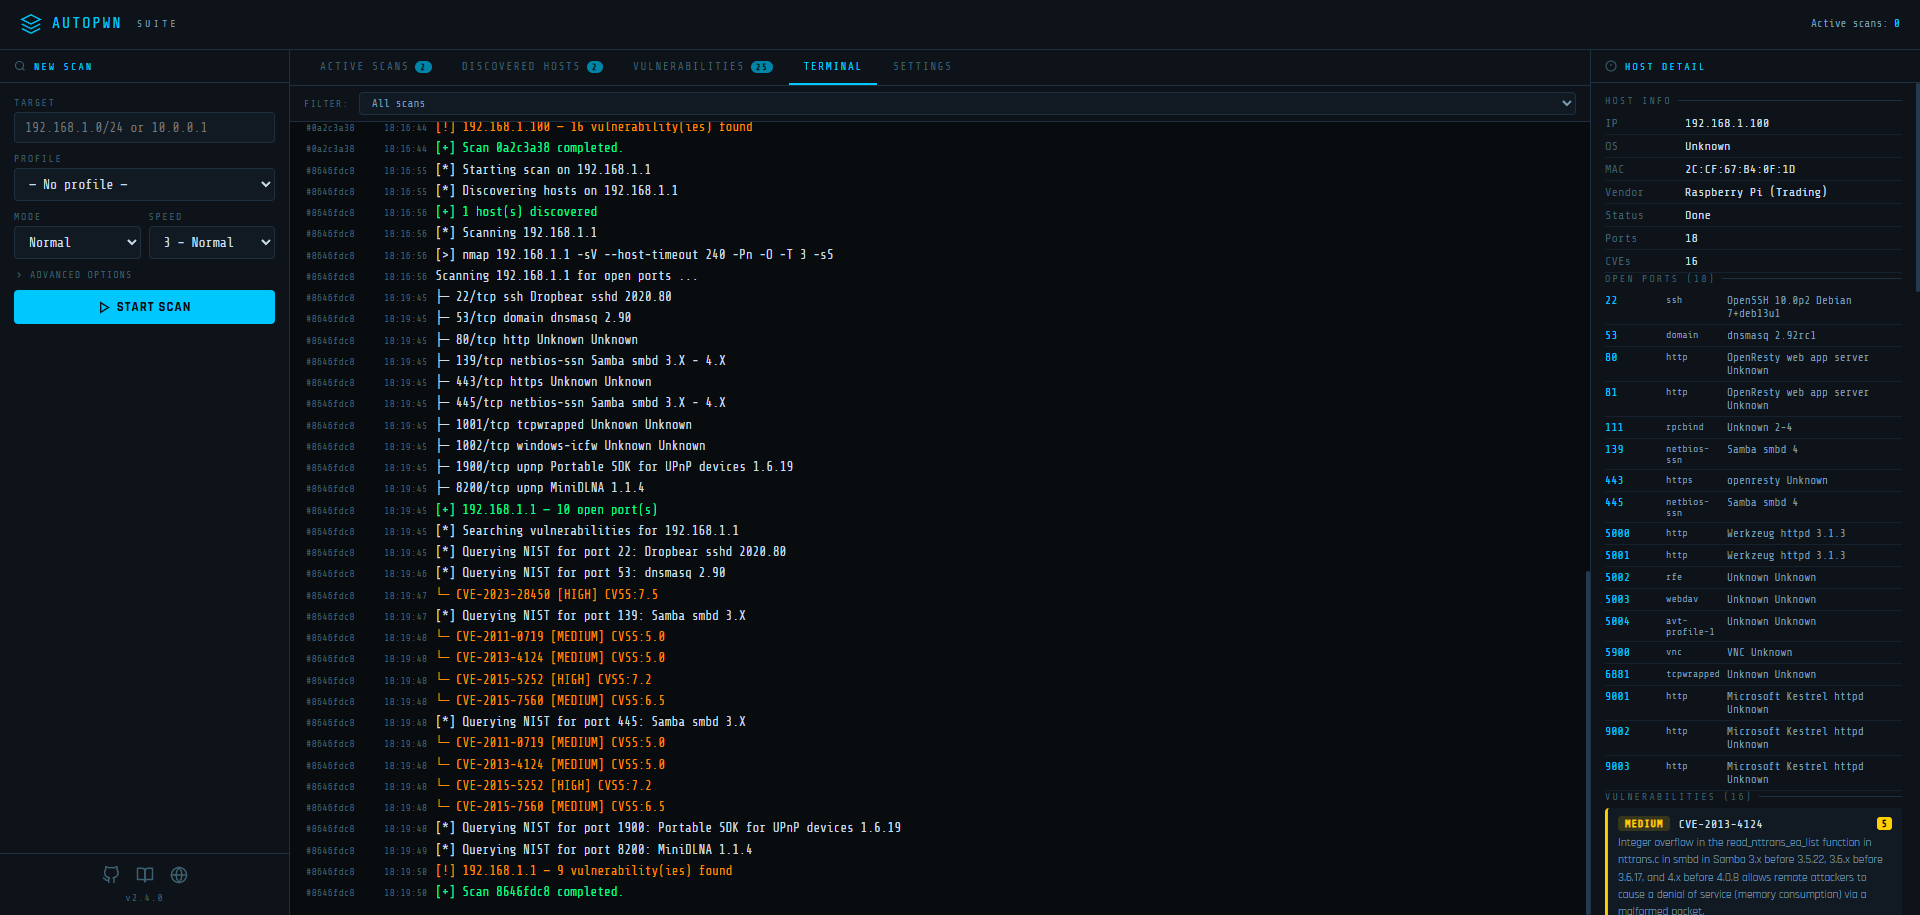 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
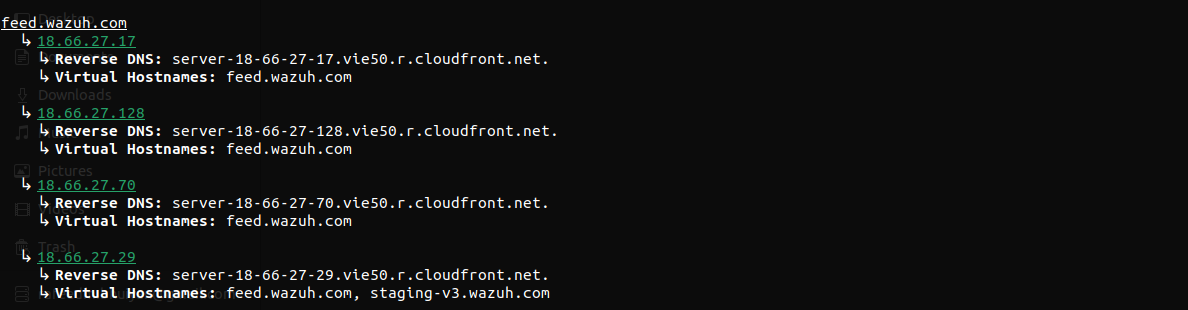 pptx704/domainim
A fast and comprehensive tool for organizational network scanning
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
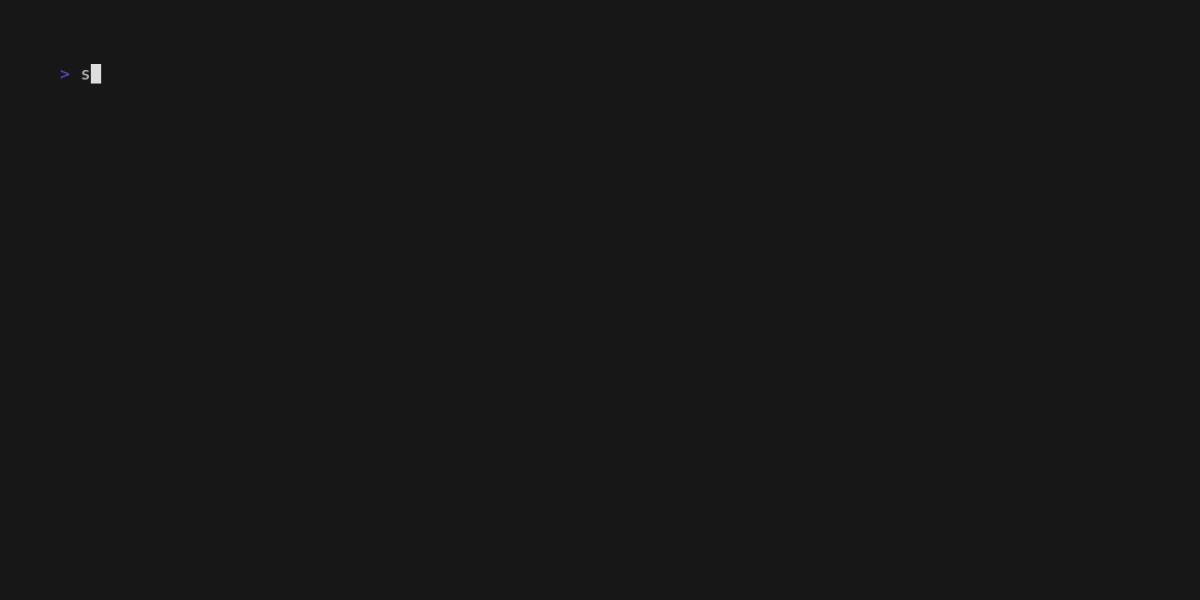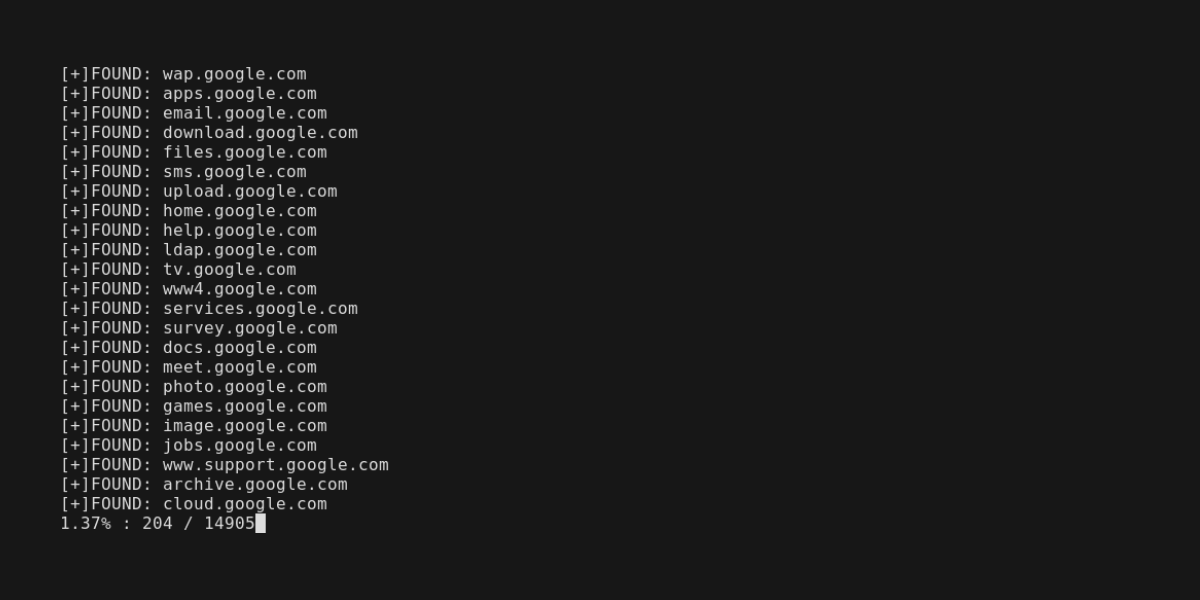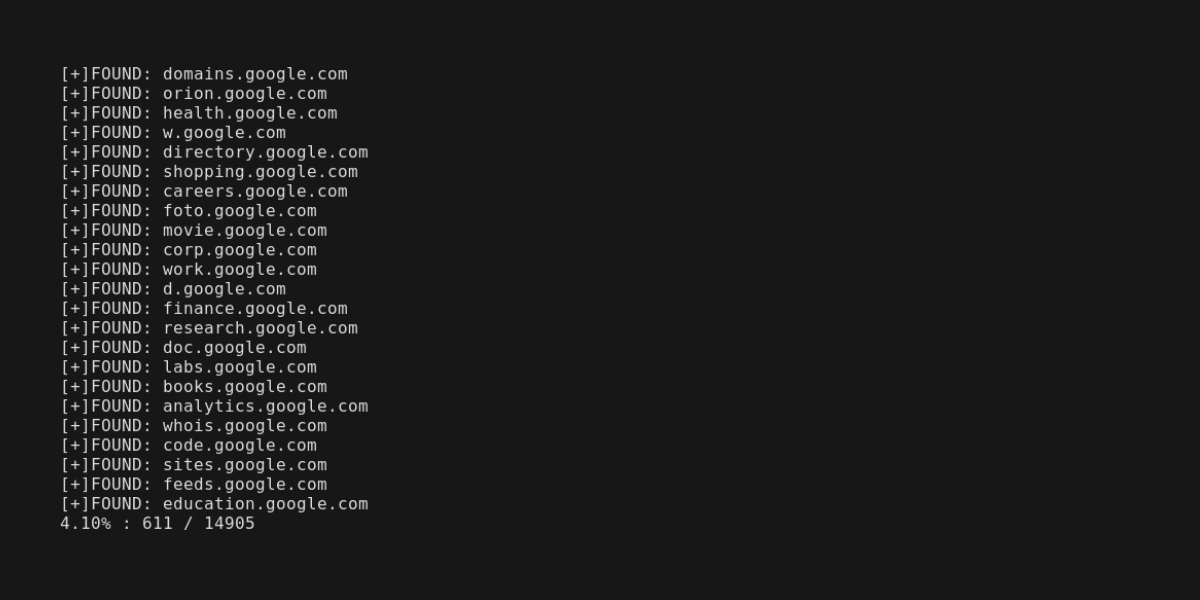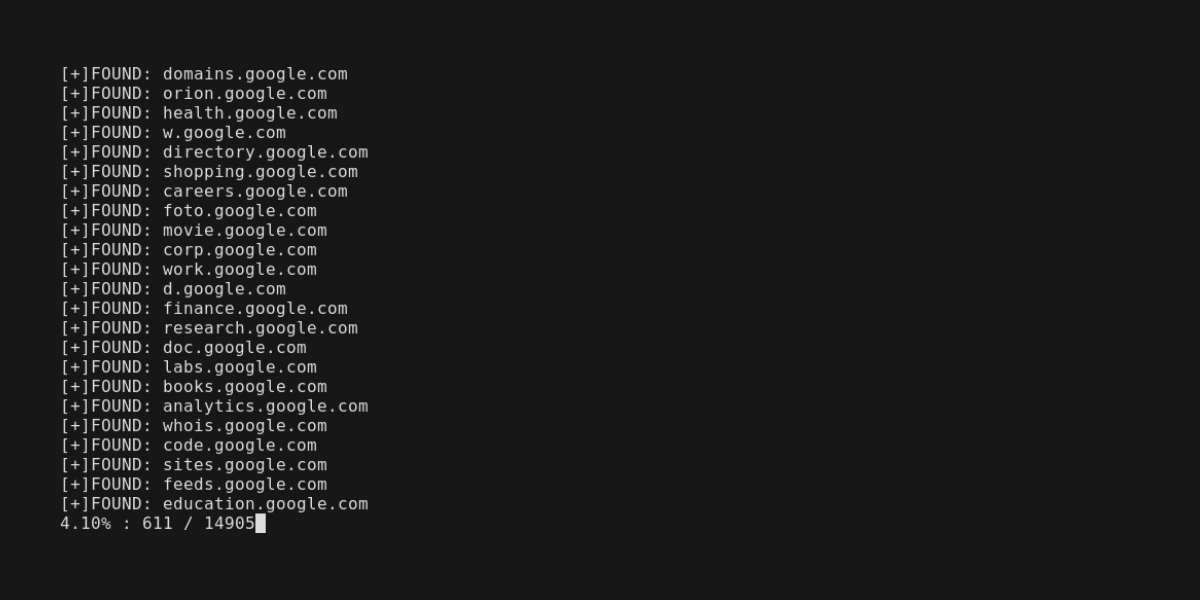 edoardottt/scilla
Information Gathering tool - DNS / Subdomains / Ports / Directories enumeration
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 bee-san/rustscan
🤖 The Modern Port Scanner 🤖
 pepelux/sippts
Set of tools to audit SIP based VoIP Systems

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…