

dddd
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
fingerprint-spoofinginformation-gatheringnetwork-mapping+9
1.9k
sleepingbag945/ddddBatch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
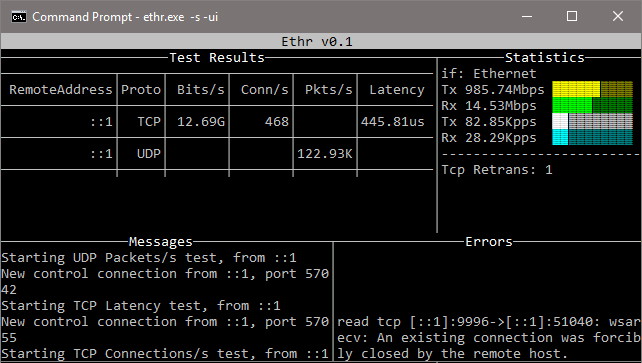 microsoft/ethr
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
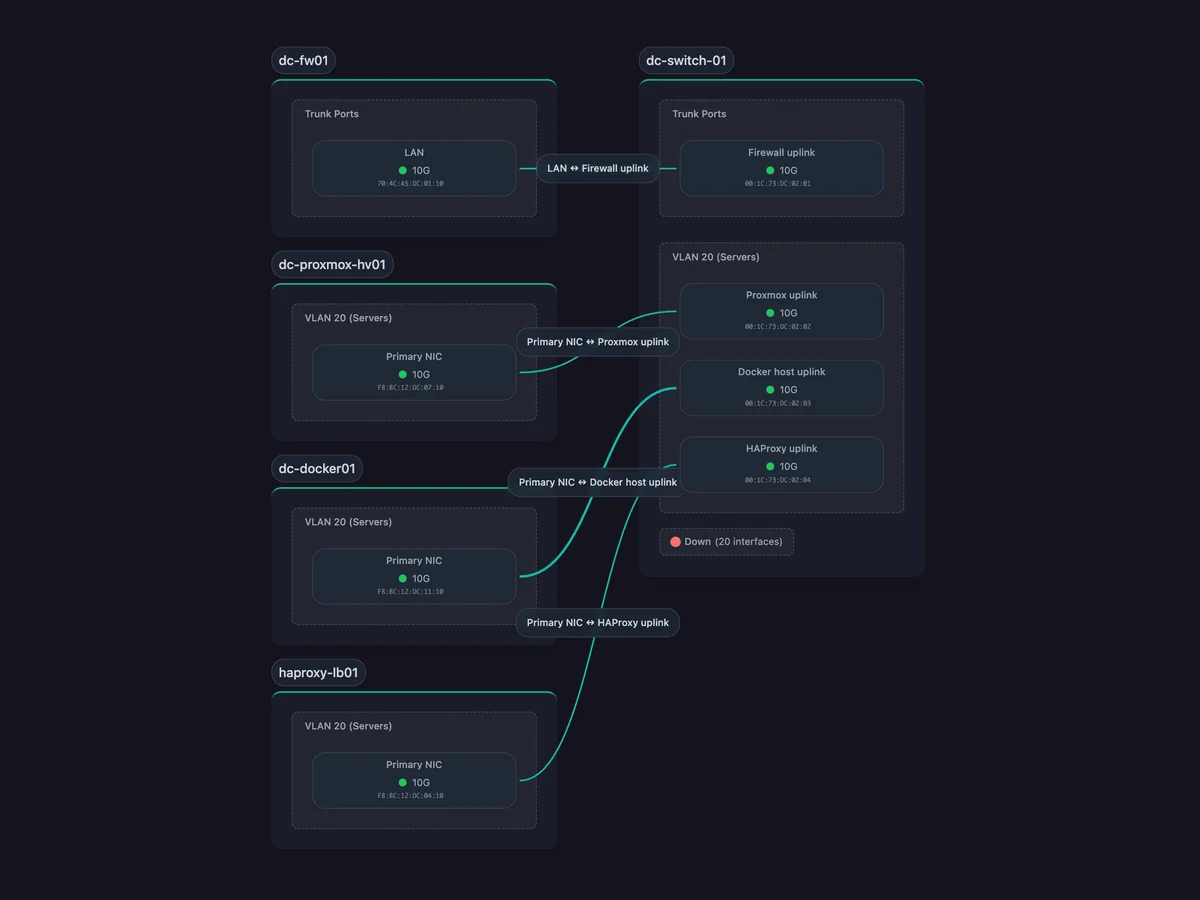 scanopy/scanopy
Network diagrams that update themselves
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
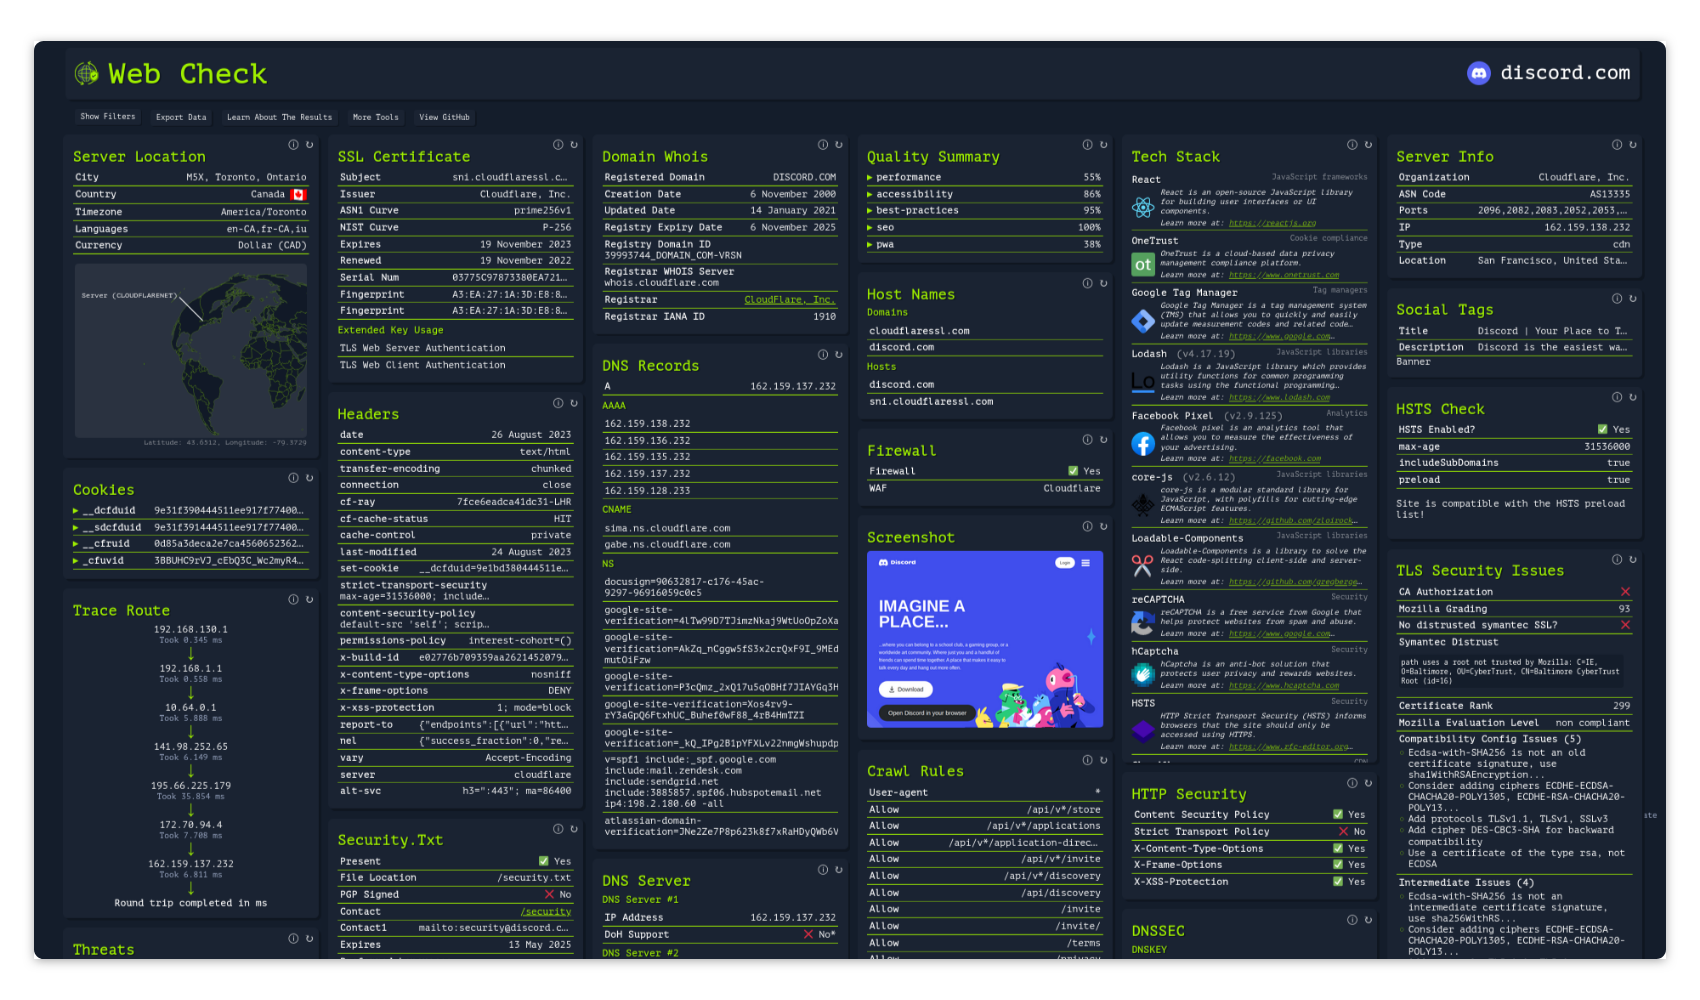 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 yunuscadirci/callstranger
Vulnerability checker for Callstranger (CVE-2020-12695)
 skr0x1c0/blind-ssrf-cve-2020-15002
https://hackerone.com/reports/865652
 cyberdudebivash/cyberdudebivash-fortisiem-cve-2025-64155-scanner
Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 sibexico/deadend
Lightweight scriptable honeypot runner
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…