

ultrasploiter
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
command-and-controlexploitationexploit-frameworks+9
vqkro/ultrasploiterA single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026
 royhills/arp-scan
Fast ARP-based network scanner for discovering and fingerprinting IPv4 hosts on local networks, with vendor lookup, adjustable scan rates, and…
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 medpaf/hawk
Network, recon and offensive-security tool for Linux.

 samh4cks/cve-2023-27163-internalprober
A tool to perform port scanning using vulnerable Request-Baskets
 r4tw1z/cve-2024-6387
This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…
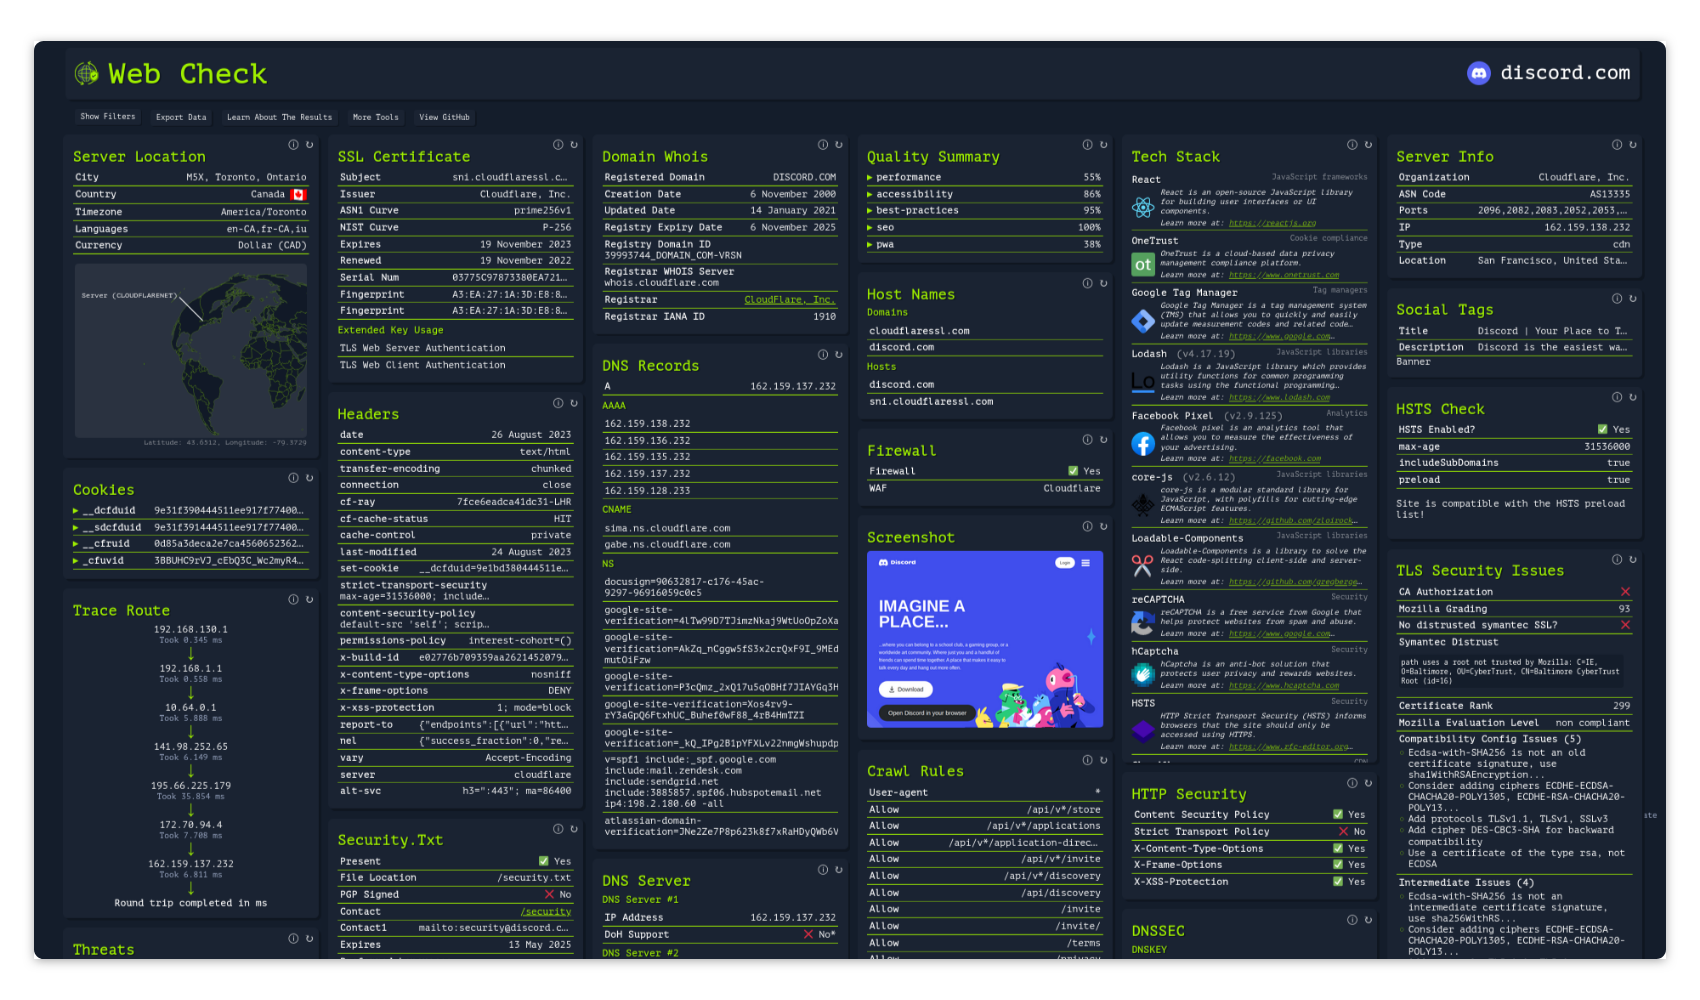 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 haishanzheng/cve-2019-0708-generate-hosts
CIDR-based host discovery tool that uses nmap to identify Windows machines with open port 3389 (RDP), reducing target IPs for CVE-2019-0708…
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 bkfish/cnvd-2020-10487-tomcat-ajp-lfi-scanner
Cnvd-2020-10487 / cve-2020-1938, scanner tool
 baimaobg/sunflower_exp
Sunflower CVE-2022-10270 vulnerability exploitation tool
 x-projetion/cve-2023-4596-openssh-multi-checker
CVE-2024-6387-checker is a tool or script designed to detect the security vulnerability known as CVE-2024-6387 OpenSSH. CVE-2024-6387 OpenSSH is an…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
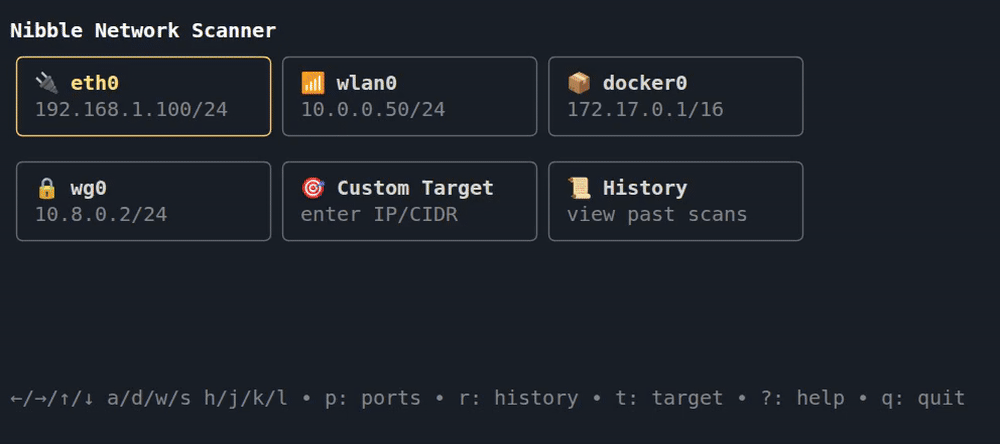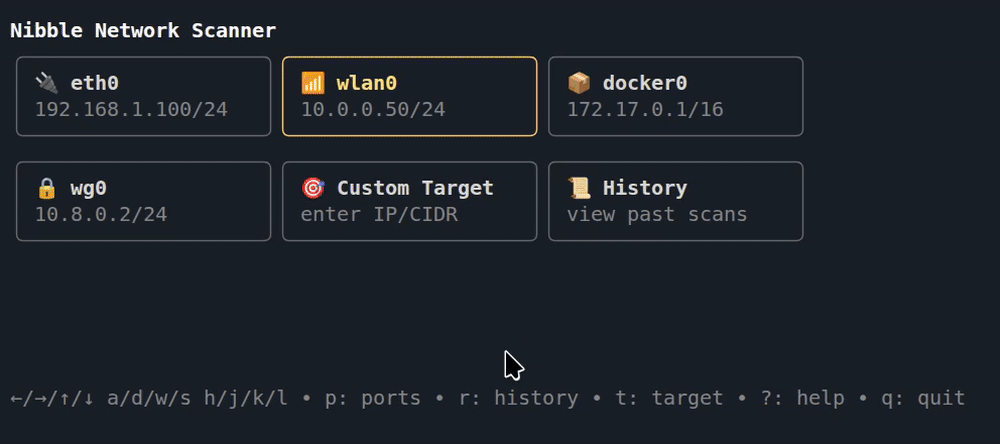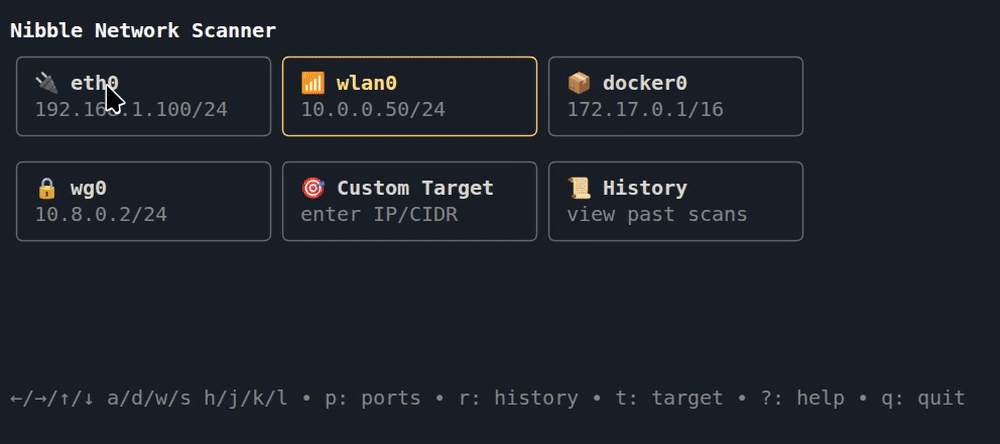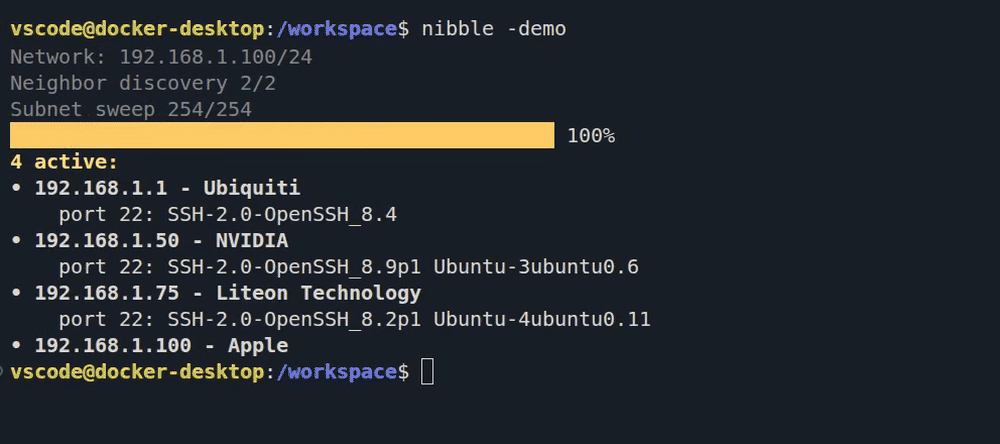 backendsystems/nibble
easy to use network scanner, with a clickable tui interface
 rickgeex/cve-2024-6387-checker
CVE-2024-6387-Check is a streamlined and efficient tool created to detect servers operating on vulnerable versions of OpenSSH.