
Argus
 divinelabio/argus
The Ultimate Information Gathering Toolkit
crawlerdns-subdomain-enumerationemail-harvesting+8
divinelabio/argusThe Ultimate Information Gathering Toolkit
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
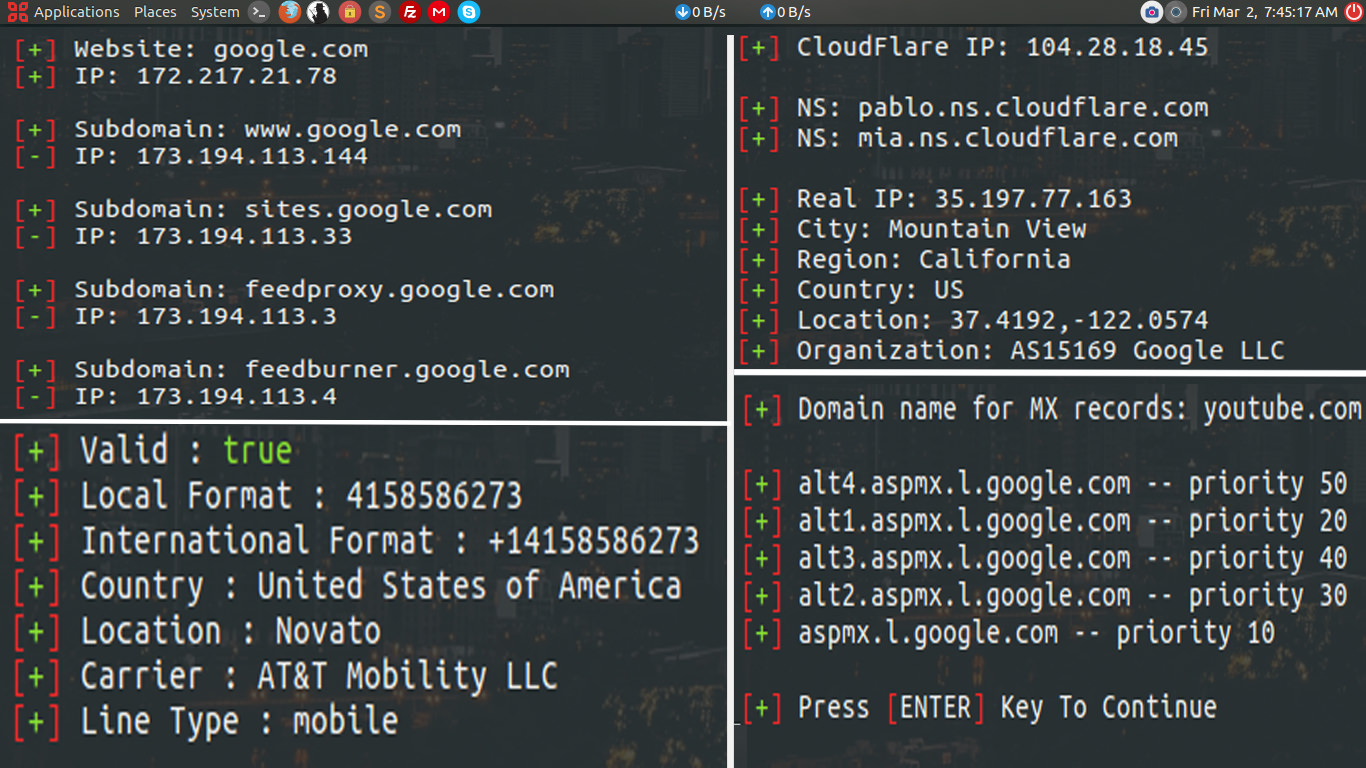 moham3driahi/th3inspector
Th3Inspector 🕵️ Best Tool For Information Gathering 🔎
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
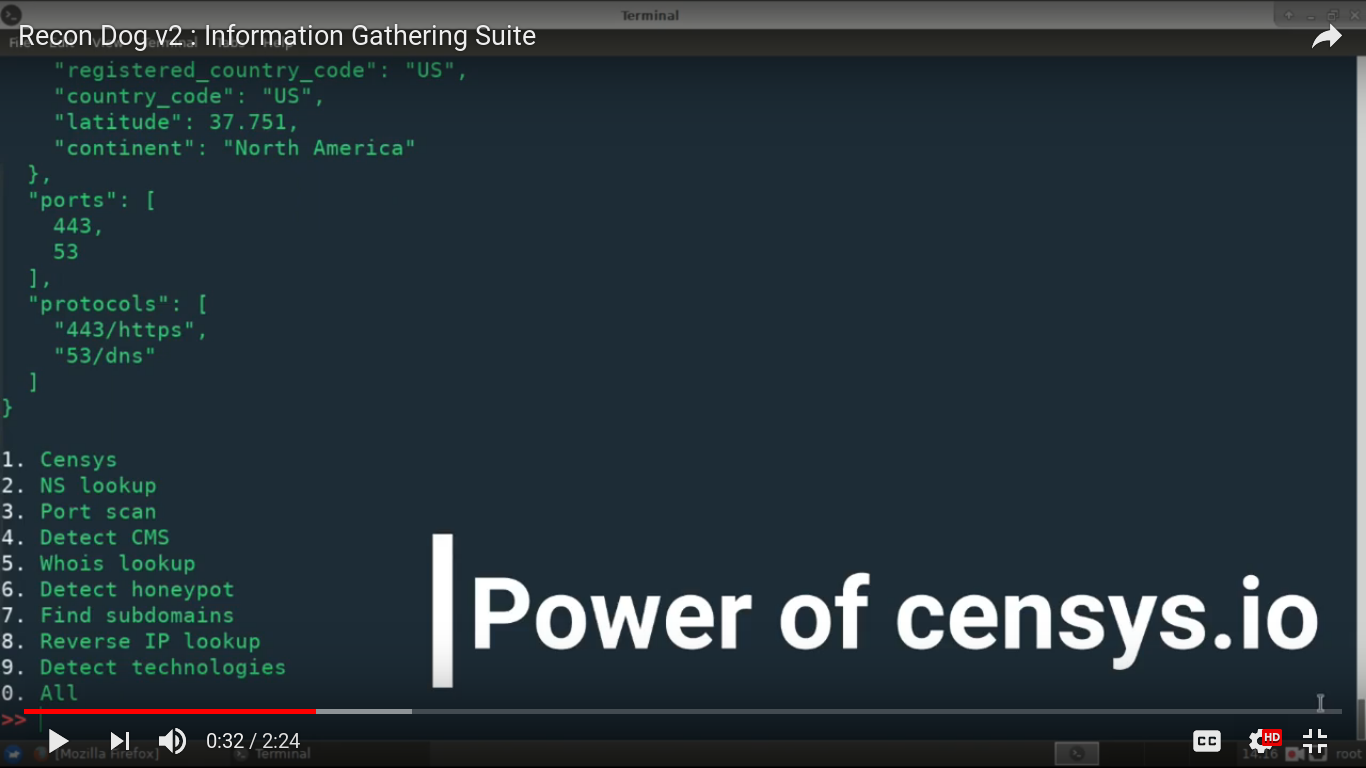
 wattocyber/cantina
OSCP-legal network recon orchestrator for port discovery, service classification, and enum-only plugin dispatch across HTTP, SMB, FTP, SNMP, SSH, and…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
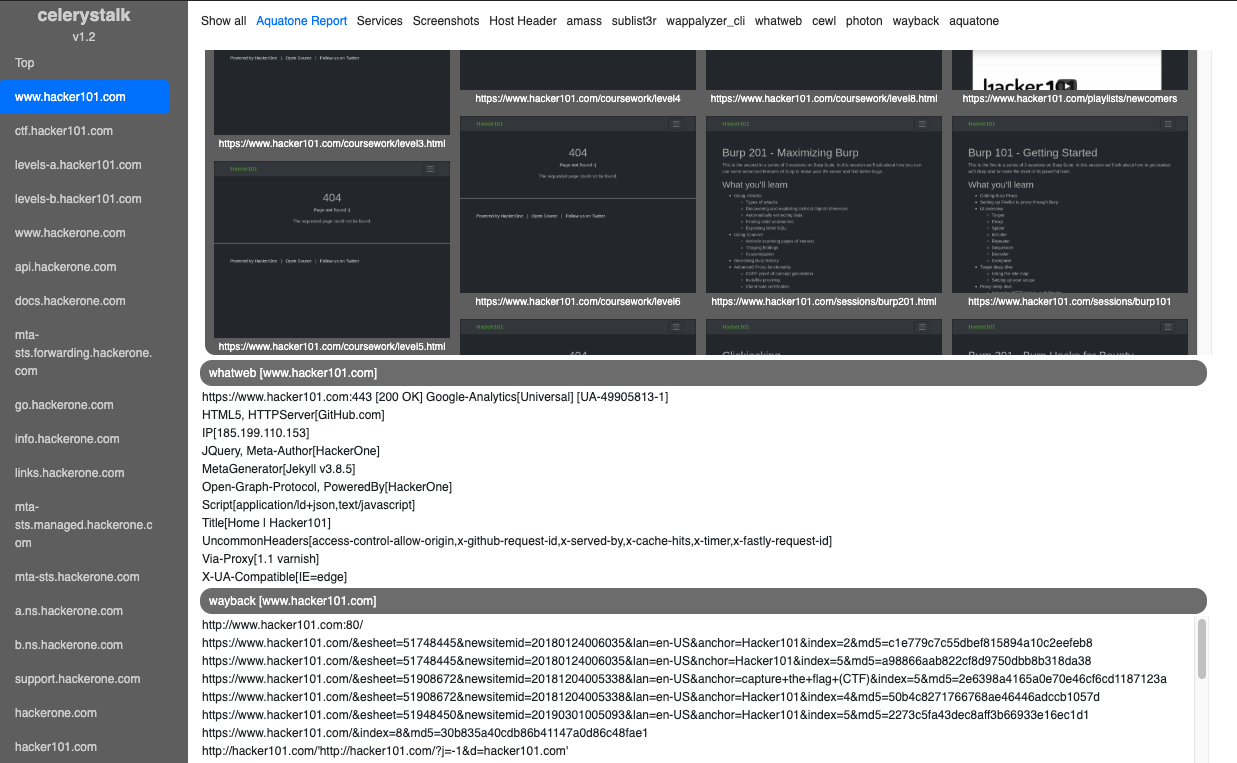 sethsec/celerystalk
An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.
 cappricio-securities/ghostrecon
gh0str3con is a All in one cloud based web Recon tool.
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 reddyyz/astsu
A network scanner tool, developed in Python 3 using scapy.
 eslam3kl/3klcon
Automation Recon tool which works with Large & Medium scopes. It performs a lot of tasks and gets back all the results in separated files.
 besimorhino/powercat
netshell features all in version 2 powershell