

httpx
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
api-securityapi-security-testingcrawler+18
10.4k
projectdiscovery/httpxFast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
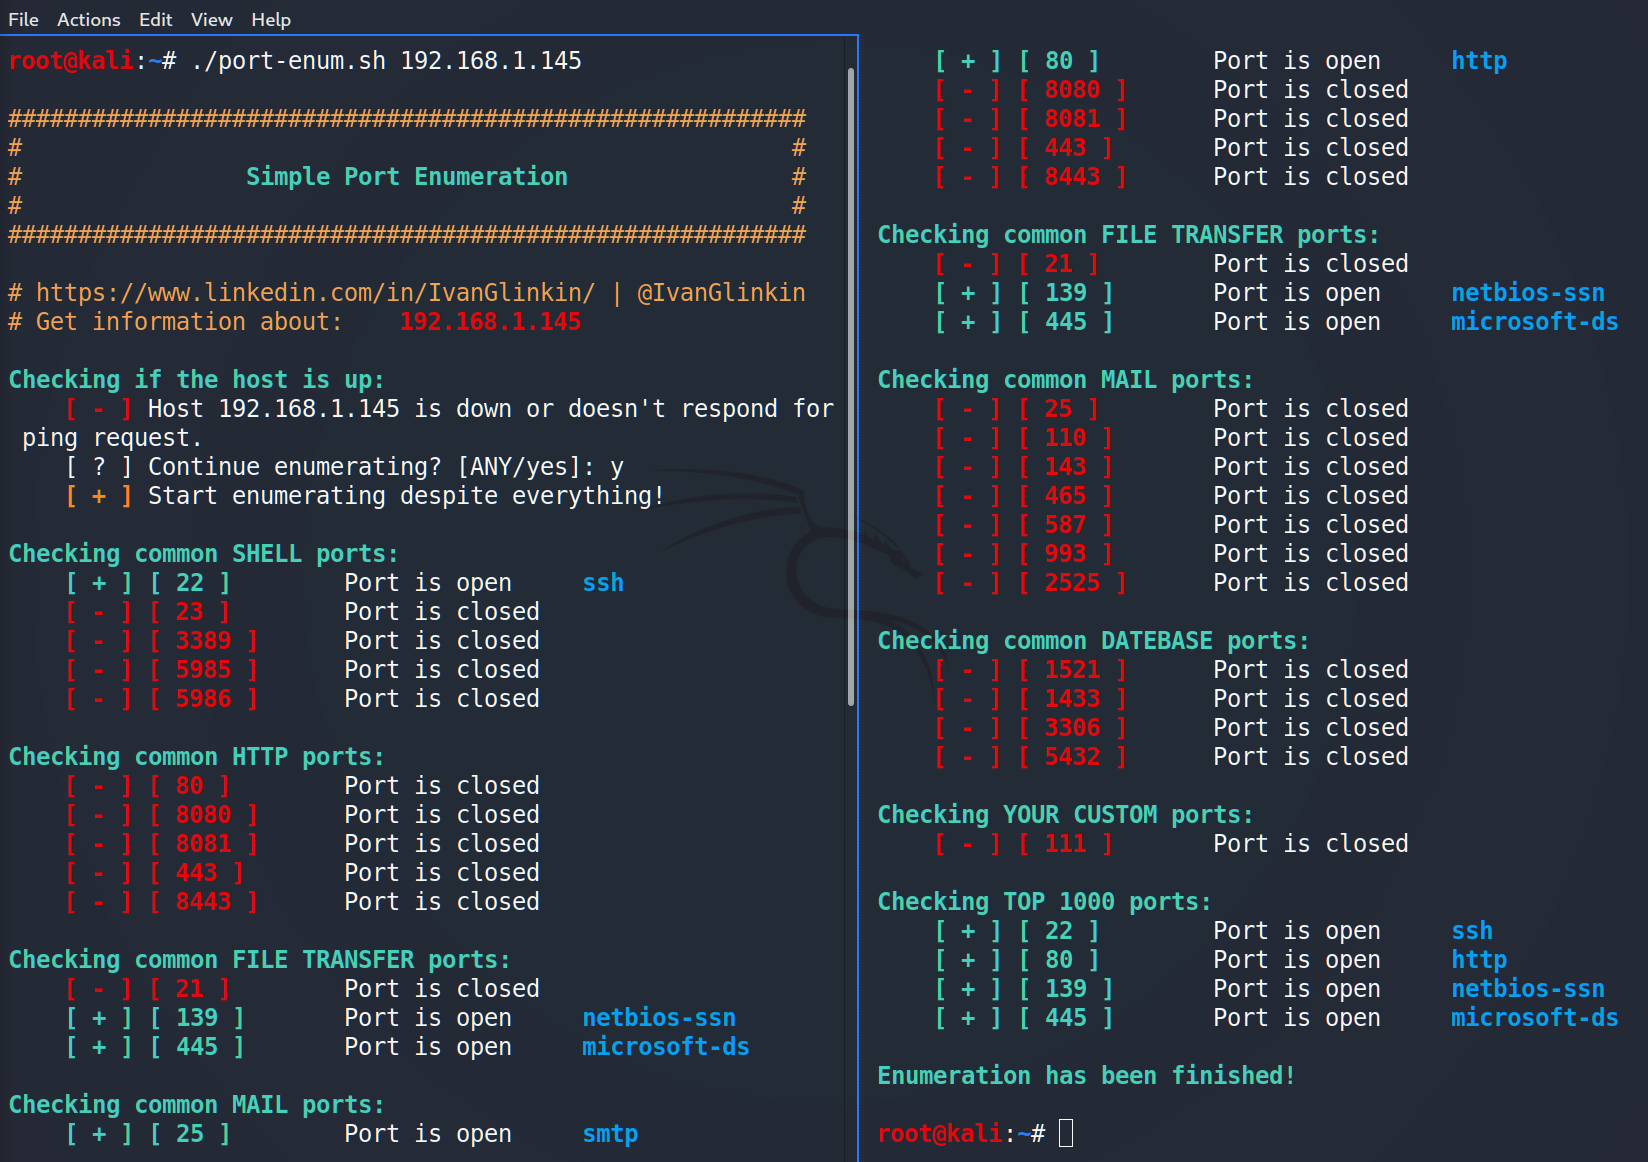 ivanglinkin/port-enumeration
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…
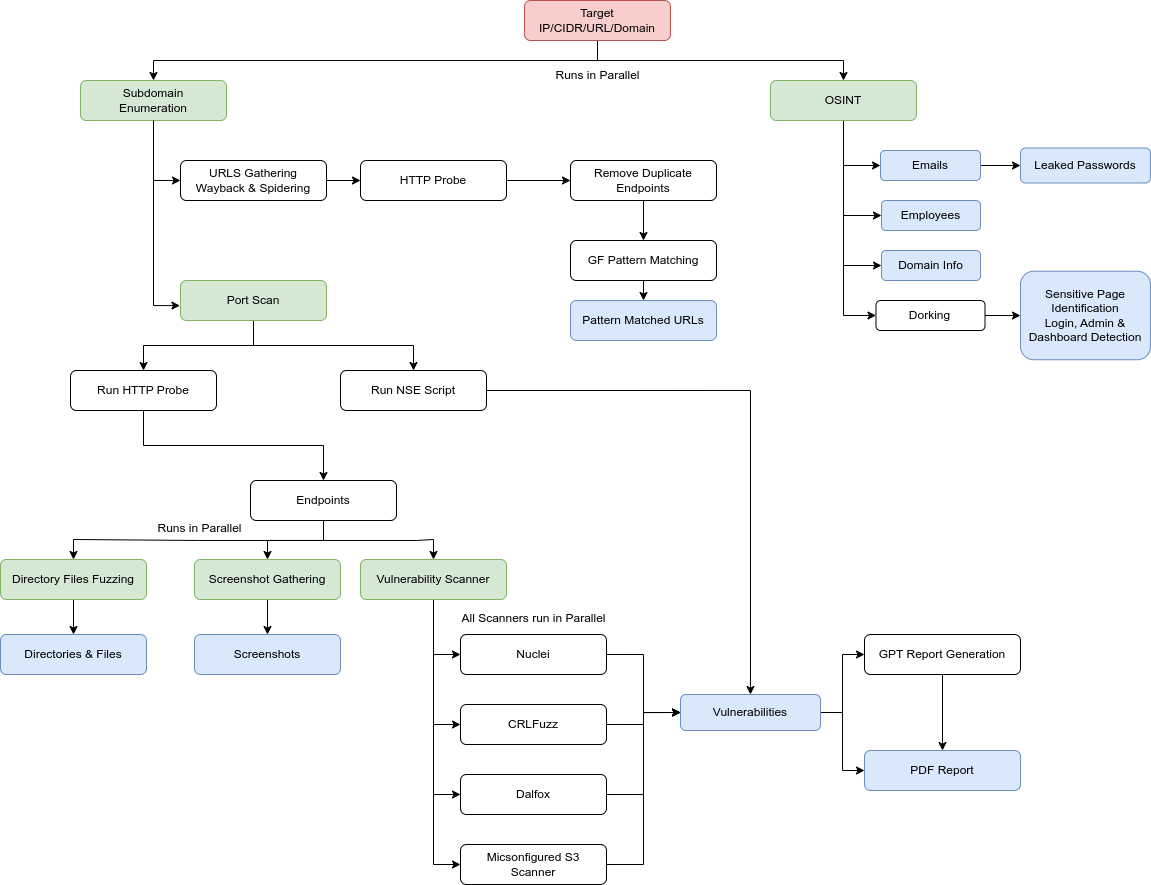 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 yashas-13/pentx-vapt-skill
Open-source AI-powered 5-phase VAPT pentest agent — recon/scan/vuln/exploit/report with PoC
 peco602/findwall
Check if your provider is blocking you!
 mad-robot/spartan
Automated reconnaissance framework integrating subdomain enumeration, live host probing, port scanning, CMS detection, and directory brute-forcing…
 hcbaker/puwr
Pivot your way deeper into computer networks with SSH compromised machines.
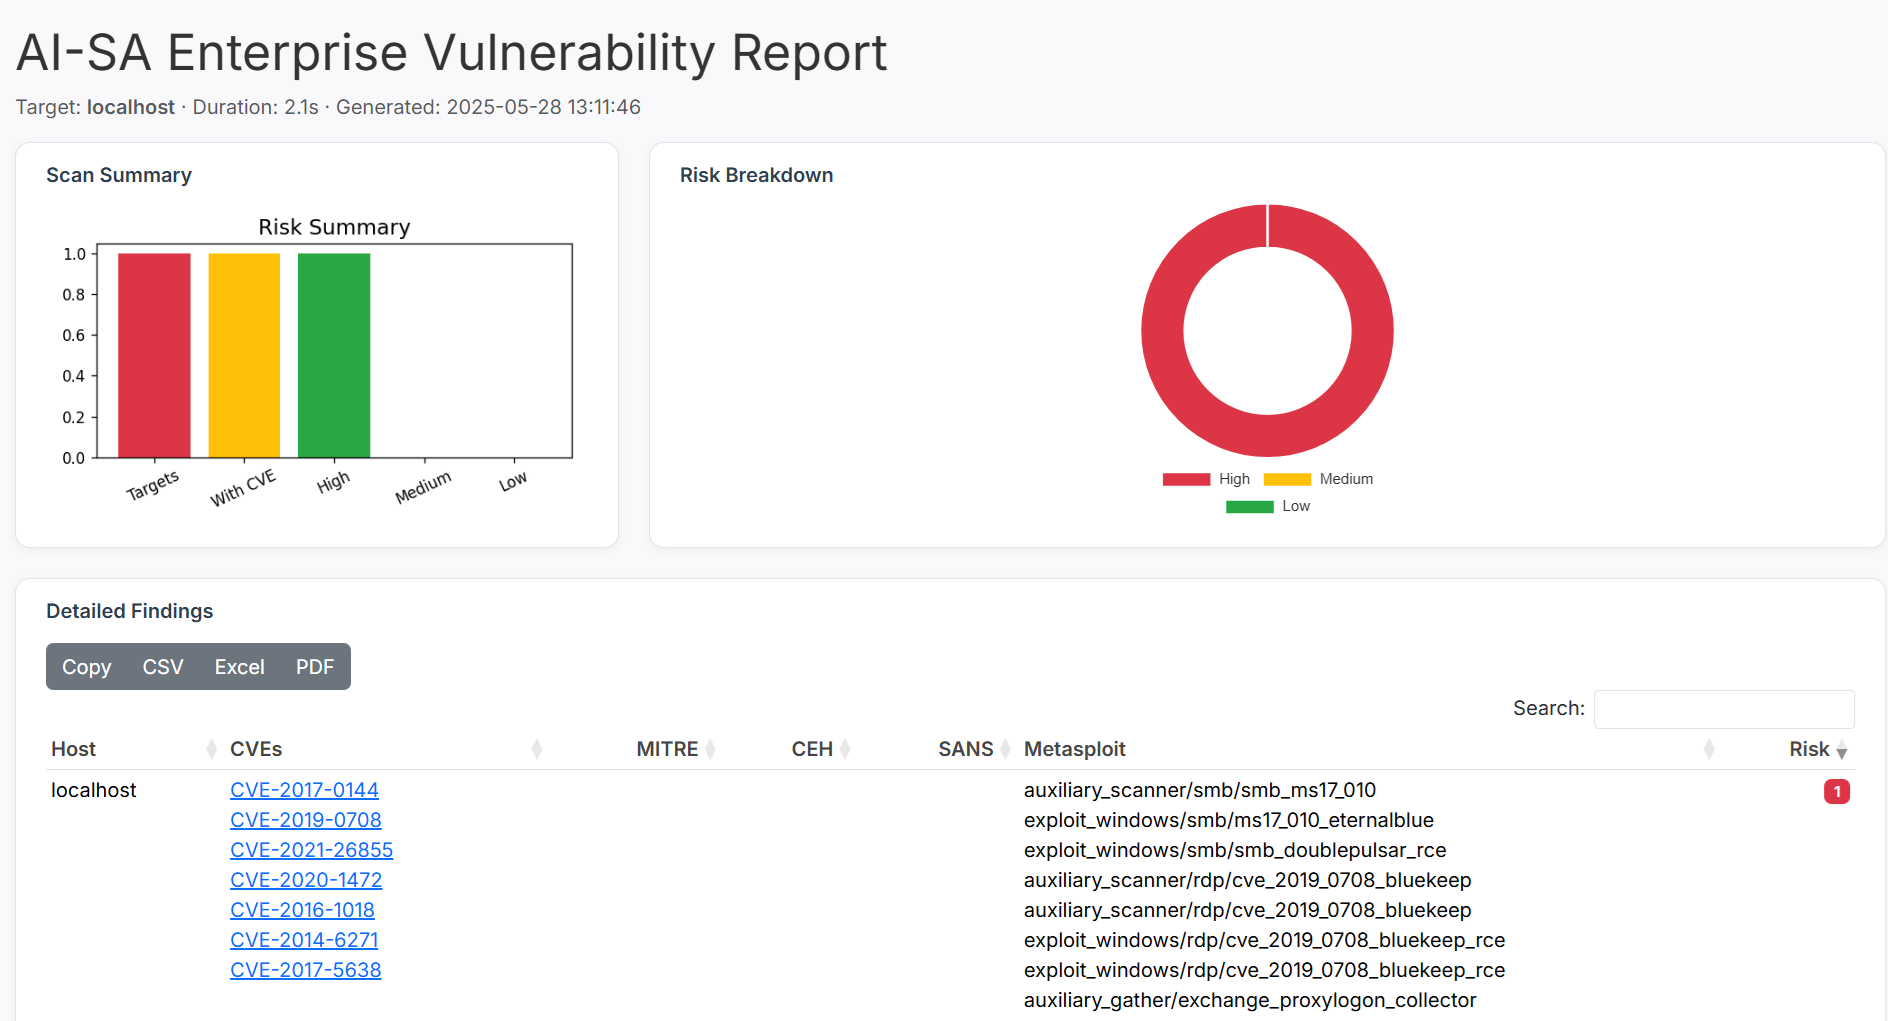 gmh5225/aisa-scanner
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
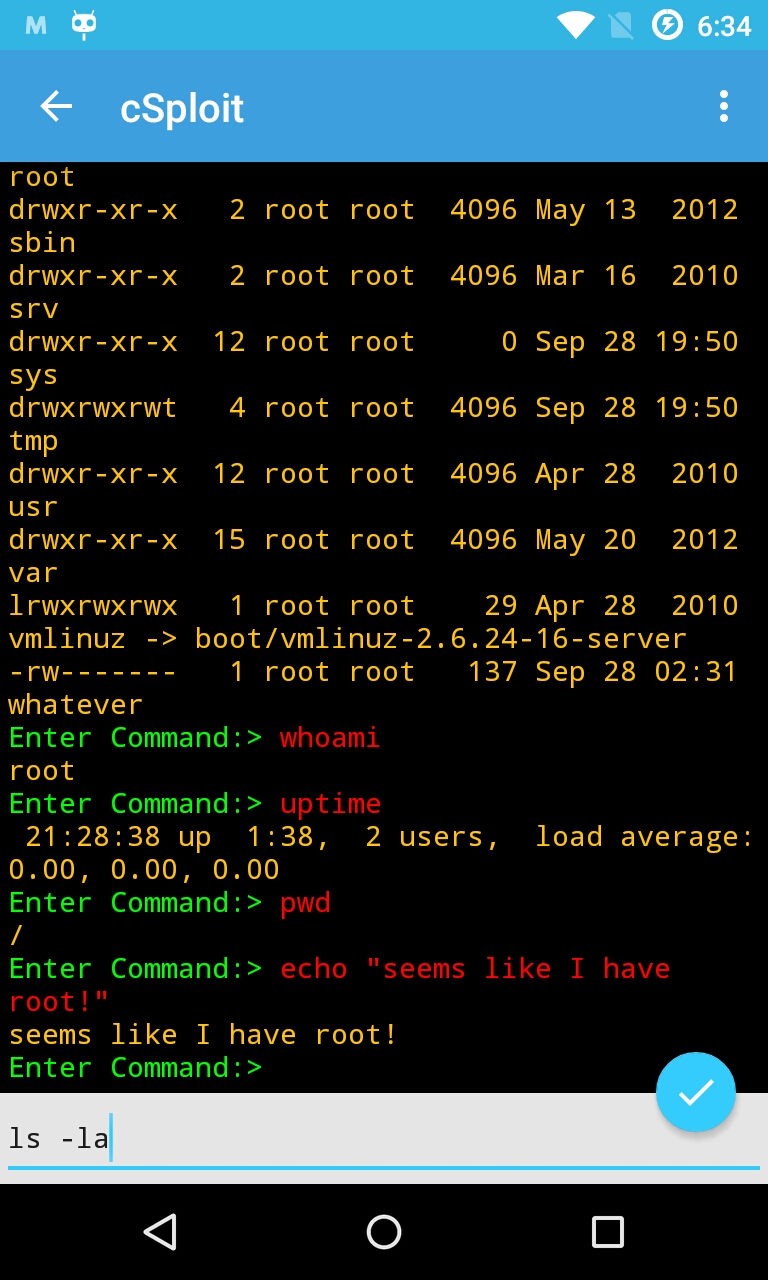 csploit/android
cSploit - The most complete and advanced IT security professional toolkit on Android.
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
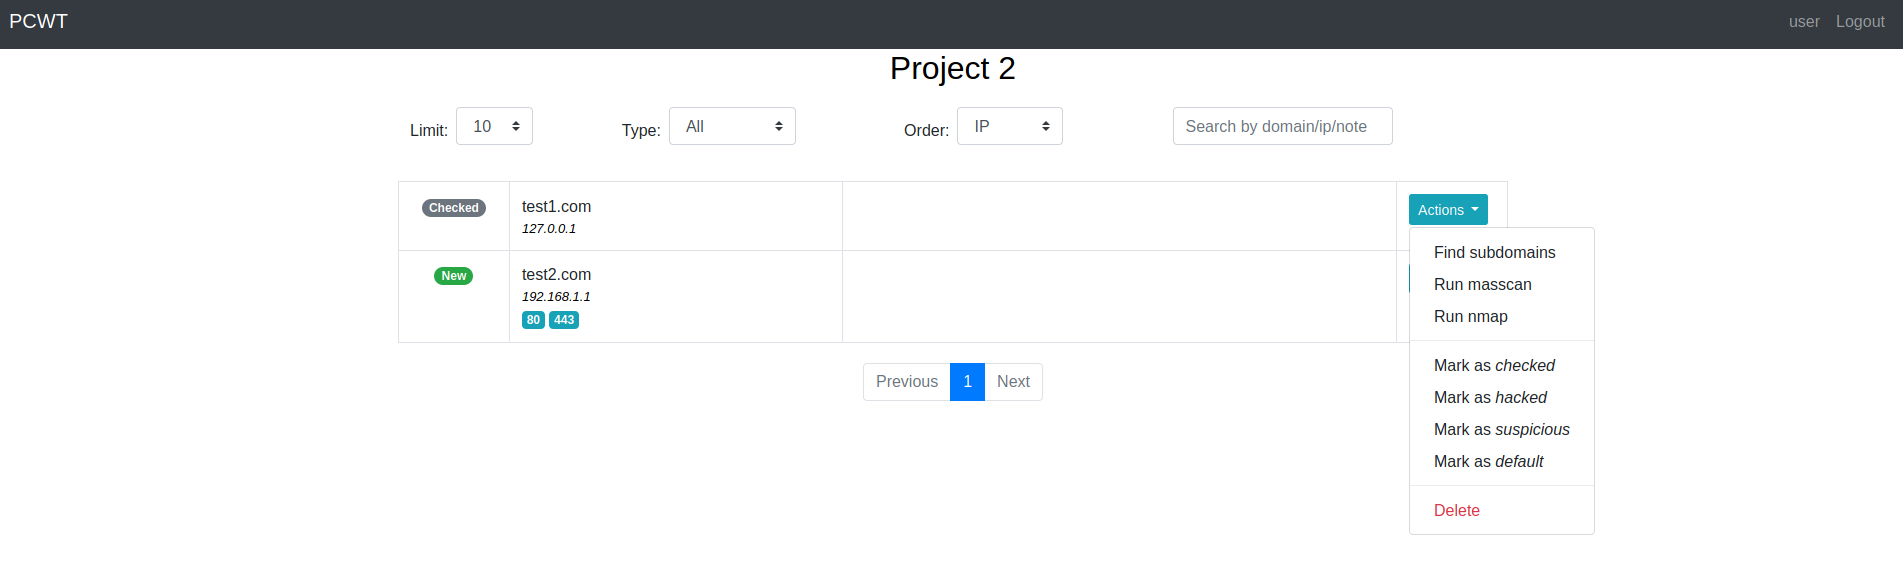 ascr0b/pcwt
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
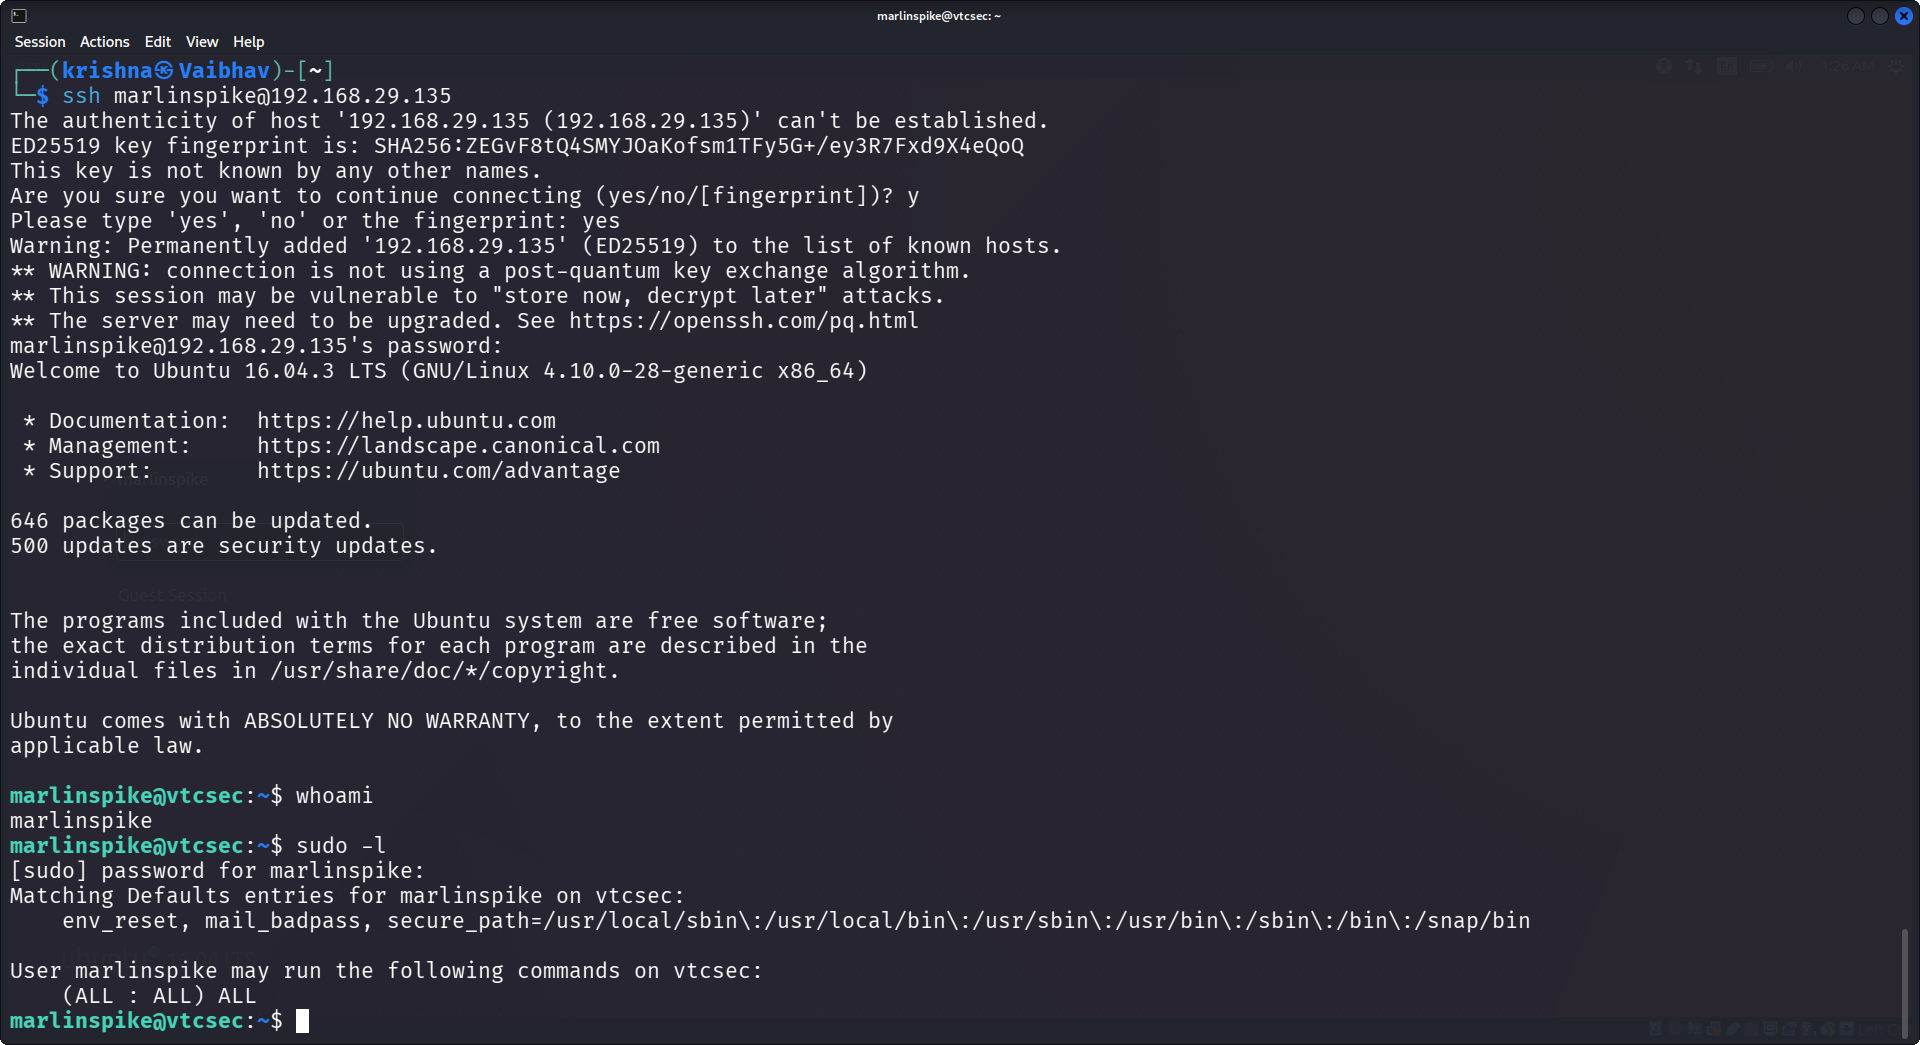 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)