
CVE-2025-1306
 nxploited/cve-2025-1306
Newscrunch <= 1.8.4 - Cross-Site Request Forgery to Arbitrary File Upload
educationexploitationpayload-generation+2
51 year ago
nxploited/cve-2025-1306Newscrunch <= 1.8.4 - Cross-Site Request Forgery to Arbitrary File Upload
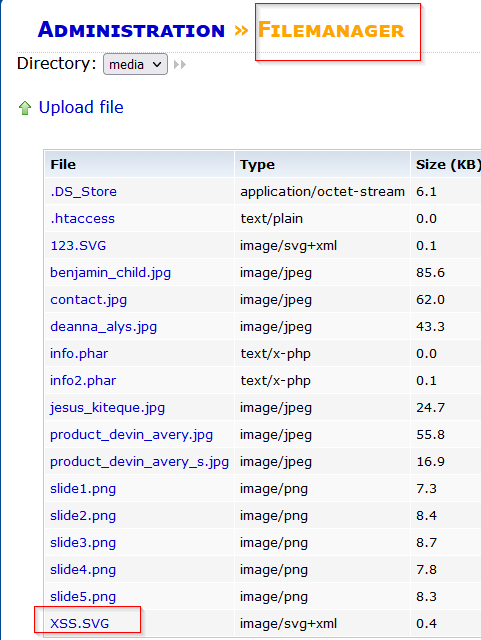 sromanhu/cve-2023-44767_ritecms-file-upload--xss---filemanager
RiteCMS 3.0 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will…
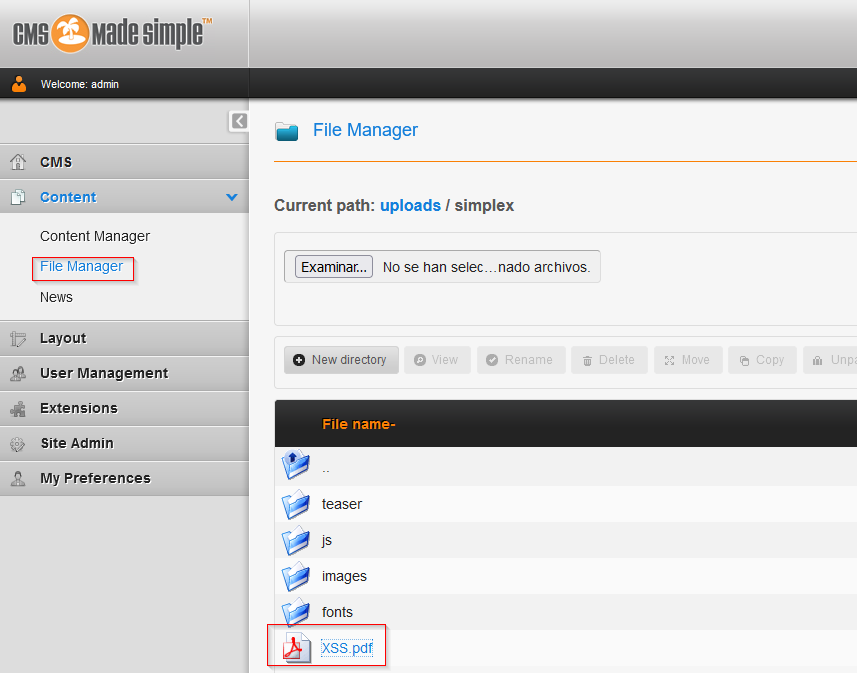 sromanhu/cve-2023-43872-cmsmadesimple-arbitrary-file-upload--xss---file-manager
CMSmadesimple 2.2.18 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed…
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
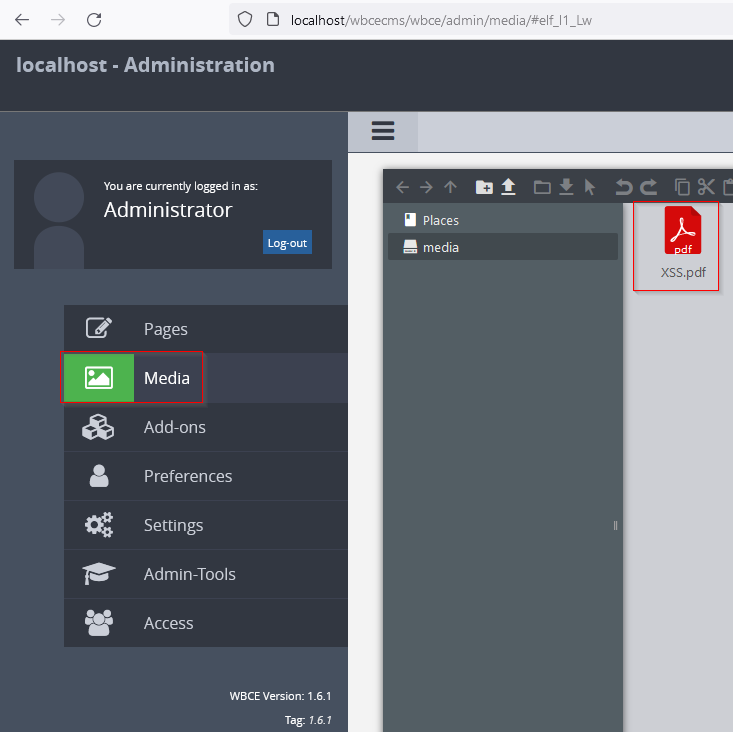 sromanhu/cve-2023-43871-wbce-arbitrary-file-upload--xss---media
WBCE 1.6.1 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will launch…
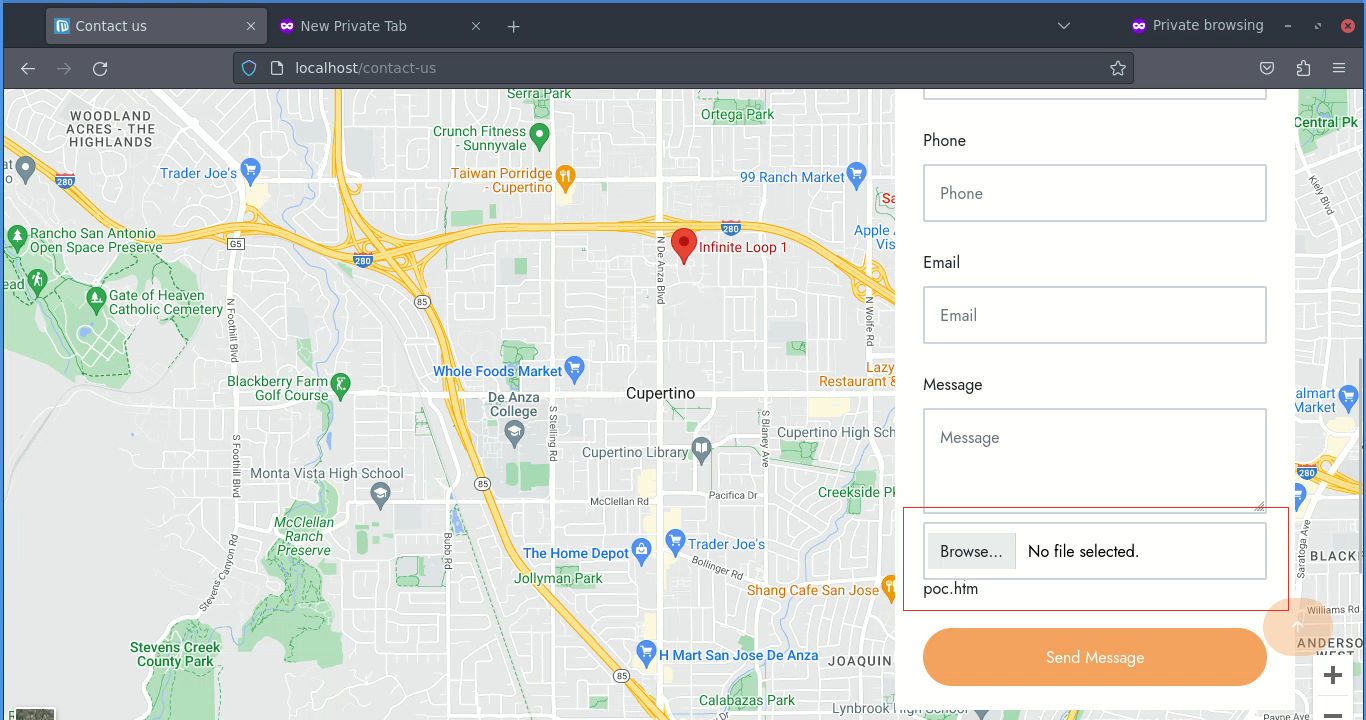 cyber-wo0dy/cve-2023-49052
Microweber version 2.0.4 vulnerable to "Uploading Malicious Files"
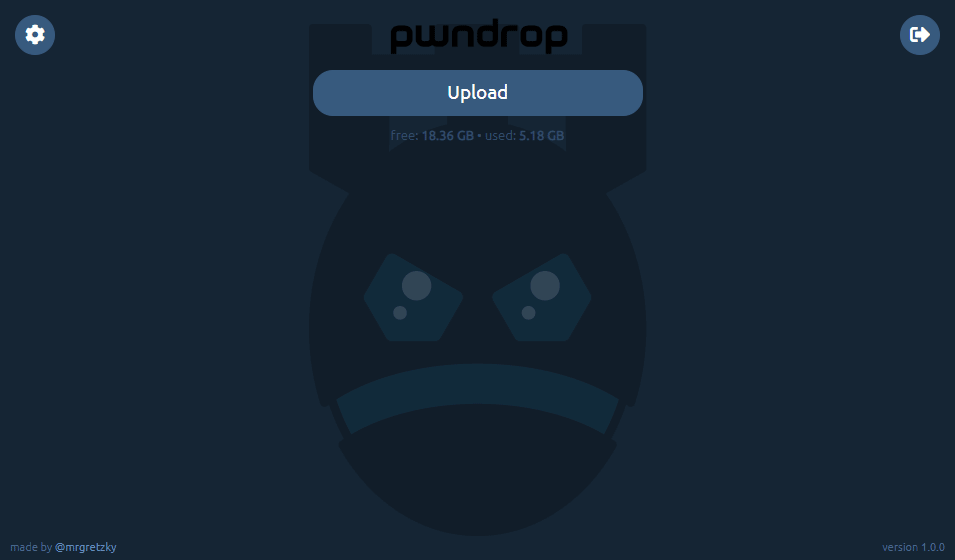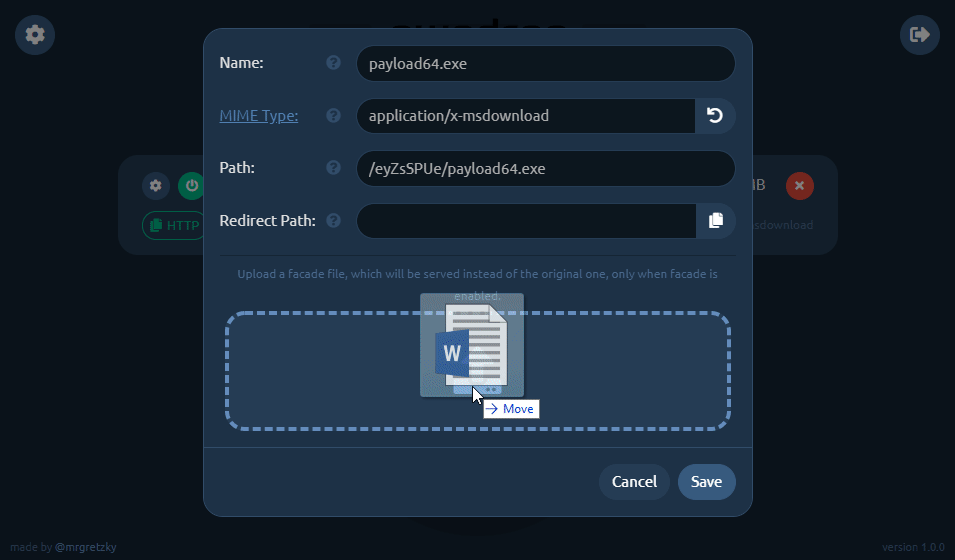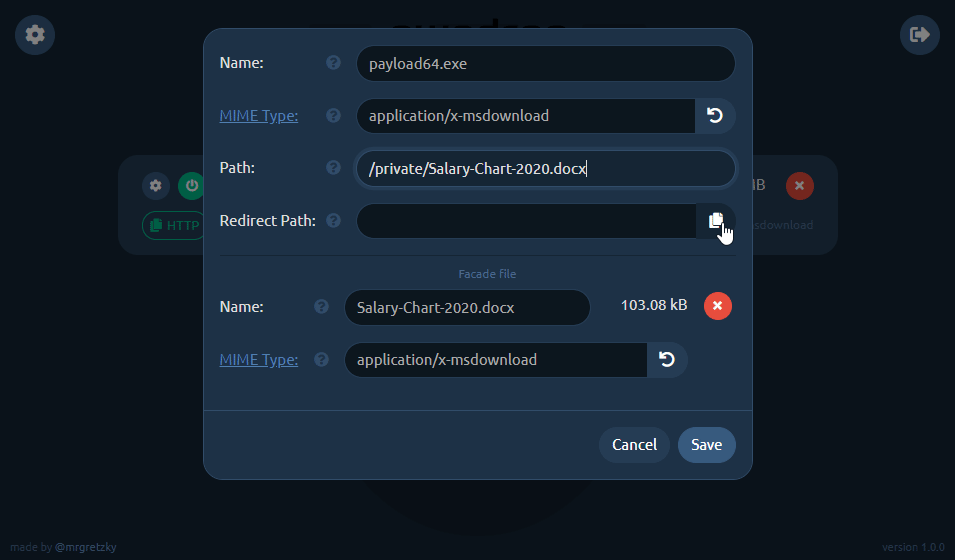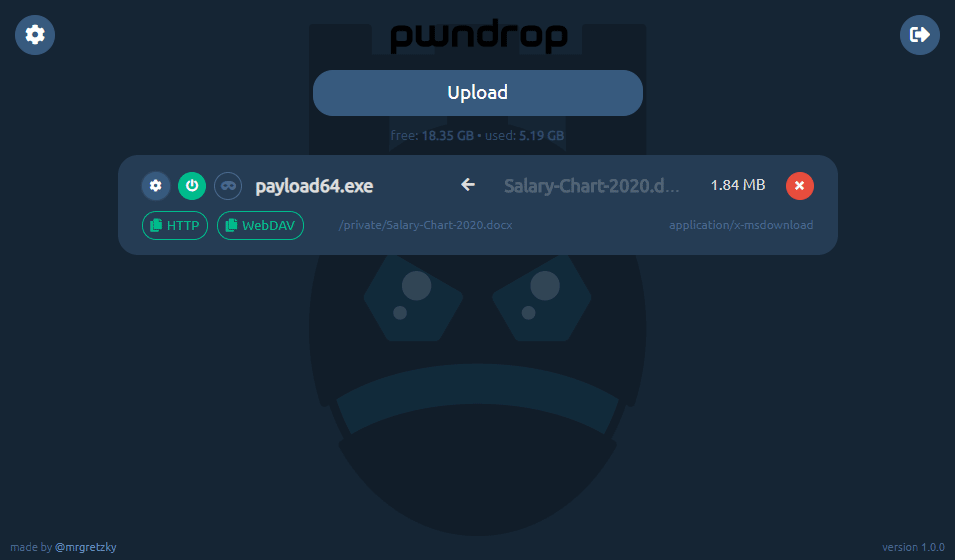 kgretzky/pwndrop
Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV.